
最新发布第566页

Appium Desktop CVE-2023-2479 命令注入漏洞
漏洞标题 Appium Desktop CVE-2023-2479 命令注入漏洞 漏洞描述 Appium Desktop CVE-2023-2479 命令注入漏洞 日期: 2024-02-07 | 影响软件: Appium Desktop | PoC代码 暂无
 2023年9月15日 07:51

浅谈红队中的外网信息收集(连载第一篇)
0x00 前言 最近在对以往所学习的有关红队的知识点进行梳理总结,这里主要参考了 ATT&CK 矩阵模型,不过对其进行了简化,同时加入了一些国内特有的情况放了进去。 大体上会按照外网信息收集...
2022年3月10日 23:32
centos6超20TB磁盘的分区格式化的示例代码_Linux
这篇文章主要介绍了centos6超20TB磁盘的分区格式化的示例代码,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编来一起学习学习吧 一、...
2023年10月17日 21:20CVE-2024-8673: Z-Downloads < 1.11.7 - Cross-Site Scripting
漏洞标题 CVE-2024-8673: Z-Downloads < 1.11.7 - Cross-Site Scripting 漏洞描述 The plugin does not properly validate uploaded files allowing for the uploading of SVGs containing m...
2024年12月16日 20:21CVE-2019-19823: TOTOLINK/Realtek Routers – Information Disclosure
漏洞标题 CVE-2019-19823: TOTOLINK/Realtek Routers - Information Disclosure 漏洞描述 A certain router administration interface using Realtek APMIB (e.g., on TOTOLINK models) allows ...
2019年5月29日 19:19Bylancer Quicklancer CVE-2024-7188 SQL注入漏洞
漏洞标题 Bylancer Quicklancer CVE-2024-7188 SQL注入漏洞 漏洞描述 Bylancer Quicklancer是Bylancer公司的一个自由职业者平台。Bylancer Quicklancer 存在SQL注入漏洞。此漏洞是由于对用户发...
2024年4月6日 13:36CVE-2019-19823: TOTOLINK/Realtek Routers – Information Disclosure
漏洞标题 CVE-2019-19823: TOTOLINK/Realtek Routers - Information Disclosure 漏洞描述 A certain router administration interface using Realtek APMIB (e.g., on TOTOLINK models) allows ...
2019年11月21日 18:23CVE-2021-29484: Ghost CMS <=4.32 - Cross-Site Scripting
漏洞标题 CVE-2021-29484: Ghost CMS <=4.32 - Cross-Site Scripting 漏洞描述 Ghost CMS 4.0.0 to 4.3.2 contains a DOM cross-site scripting vulnerability. An unused endpoint added du...
2021年2月23日 10:03CVE-2021-24278: WordPress Contact Form 7 <2.3.4 - Arbitrary Nonce Generation
漏洞标题 CVE-2021-24278: WordPress Contact Form 7 <2.3.4 - Arbitrary Nonce Generation 漏洞描述 WordPress Contact Form 7 before version 2.3.4 allows unauthenticated users to use ...
2021年11月16日 01:53CVE-2010-1955: Joomla! Component Deluxe Blog Factory 1.1.2 – Local File Inclusion
漏洞标题 CVE-2010-1955: Joomla! Component Deluxe Blog Factory 1.1.2 - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the Deluxe Blog Factory (com_blogfactory)...
2010年8月26日 23:57CVE-2025-3415: Grafana – Exposes DingDing API Keys
漏洞标题 CVE-2025-3415: Grafana - Exposes DingDing API Keys 漏洞描述 An incident occurred where the DingDing alerting integration URL was inadvertently exposed to viewers due to a ...
2025年8月24日 02:36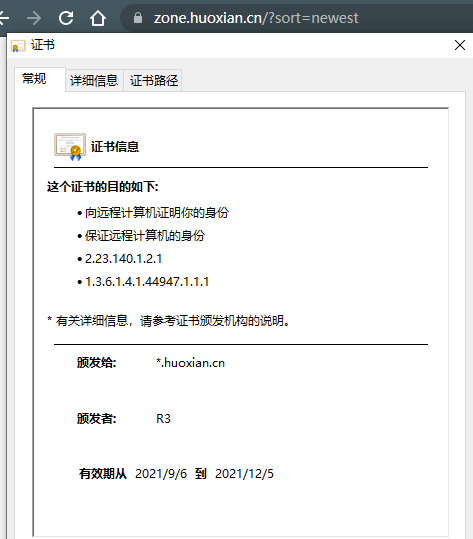
批量获取网站SSL证书里的域名
大佬们在日常刷洞过程中,或者批量扫某个POC时,总会扫到很多未知资产或者结果量太大一个个去验证资产归属太费时费力。而一些https站点的证书中能看到证书归属,一般通过证书定位的资产都比较准...
2022年3月10日 23:33CVE-2021-24219: All Thrive Themes and Plugins – Unauthenticated Option Update
漏洞标题 CVE-2021-24219: All Thrive Themes and Plugins - Unauthenticated Option Update 漏洞描述 The Thrive Optimize WordPress plugin before 1.4.13.3, Thrive Comments WordPress plug...
2021年6月16日 12:13CiscoIOSXEWLC-CVE-2025-20188-任意文件上传
漏洞标题 CiscoIOSXEWLC-CVE-2025-20188-任意文件上传 漏洞描述 用于无线局域网控制器 (WLC) 的 Cisco IOS XE 软件的带外接入点 (AP)映像下载功能中存在一个漏洞,该漏洞可能允许未经身份验...
2025年5月22日 21:18CVE-2024-40711: Veeam Backup & Replication – Unauthenticated
漏洞标题 CVE-2024-40711: Veeam Backup & Replication - Unauthenticated 漏洞描述 A deserialization of untrusted data vulnerability with a malicious payload can allow an unauthent...
2024年10月5日 02:51CVE-2019-2616: Oracle Business Intelligence/XML Publisher – XML External Entity Injection
漏洞标题 CVE-2019-2616: Oracle Business Intelligence/XML Publisher - XML External Entity Injection 漏洞描述 Oracle Business Intelligence and XML Publisher 11.1.1.9.0 / 12.2.1.3.0 /...
2019年5月12日 04:05
2026年10月20日 11:45
2026年10月19日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

