
最新发布第576页

CVE-2021-39144: XStream 1.4.18 – Remote Code Execution
漏洞标题 CVE-2021-39144: XStream 1.4.18 - Remote Code Execution 漏洞描述 XStream 1.4.18 is susceptible to remote code execution. An attacker can execute commands of the host by man...
 2021年10月17日 05:34
CVE-2024-6646: Netgear-WN604 downloadFile.php – Information Disclosure
漏洞标题 CVE-2024-6646: Netgear-WN604 downloadFile.php - Information Disclosure 漏洞描述 There is an information leakage vulnerability in the downloadFile.php interface of Netgear ...
2024年7月22日 21:36CVE-2025-1974-k8s: Ingress-Nginx Controller – Unauthenticated Remote Code Execution
漏洞标题 CVE-2025-1974-k8s: Ingress-Nginx Controller - Unauthenticated Remote Code Execution 漏洞描述 A security issue was discovered in ingress-nginx where the `auth-tls-match-cn`...
2025年11月4日 08:04CVE-2022-3908: WordPress Helloprint <1.4.7 - Cross-Site Scripting
漏洞标题 CVE-2022-3908: WordPress Helloprint <1.4.7 - Cross-Site Scripting 漏洞描述 WordPress Helloprint plugin before 1.4.7 contains a cross-site scripting vulnerability. The p...
2022年2月16日 04:09
Linux安装Python3.8.1的教程详解_Linux
这篇文章主要介绍了Linux安装Python3.8.1的教程,本文以linux安装python3.8版本为例给大家详细说明,感兴趣的朋友跟随小编一起看看吧 本例以Linux上安装Pyhton3.8版本为例进行说明 1、依赖包安...
2024年5月19日 21:16CVE-2023-1119: WP-Optimize WordPress plugin < 3.2.13 - Cross-Site Scripting
漏洞标题 CVE-2023-1119: WP-Optimize WordPress plugin < 3.2.13 - Cross-Site Scripting 漏洞描述 The WP-Optimize WordPress plugin before 3.2.13 and SrbTransLatin WordPress plugin b...
2023年5月22日 20:27CVE-2023-30194: Prestashop posstaticfooter <= 1.0.0 - SQL Injection
漏洞标题 CVE-2023-30194: Prestashop posstaticfooter <= 1.0.0 - SQL Injection 漏洞描述 Prestashop posstaticfooter <= 1.0.0 is vulnerable to SQL Injection via posstaticfooter::...
2023年10月26日 00:29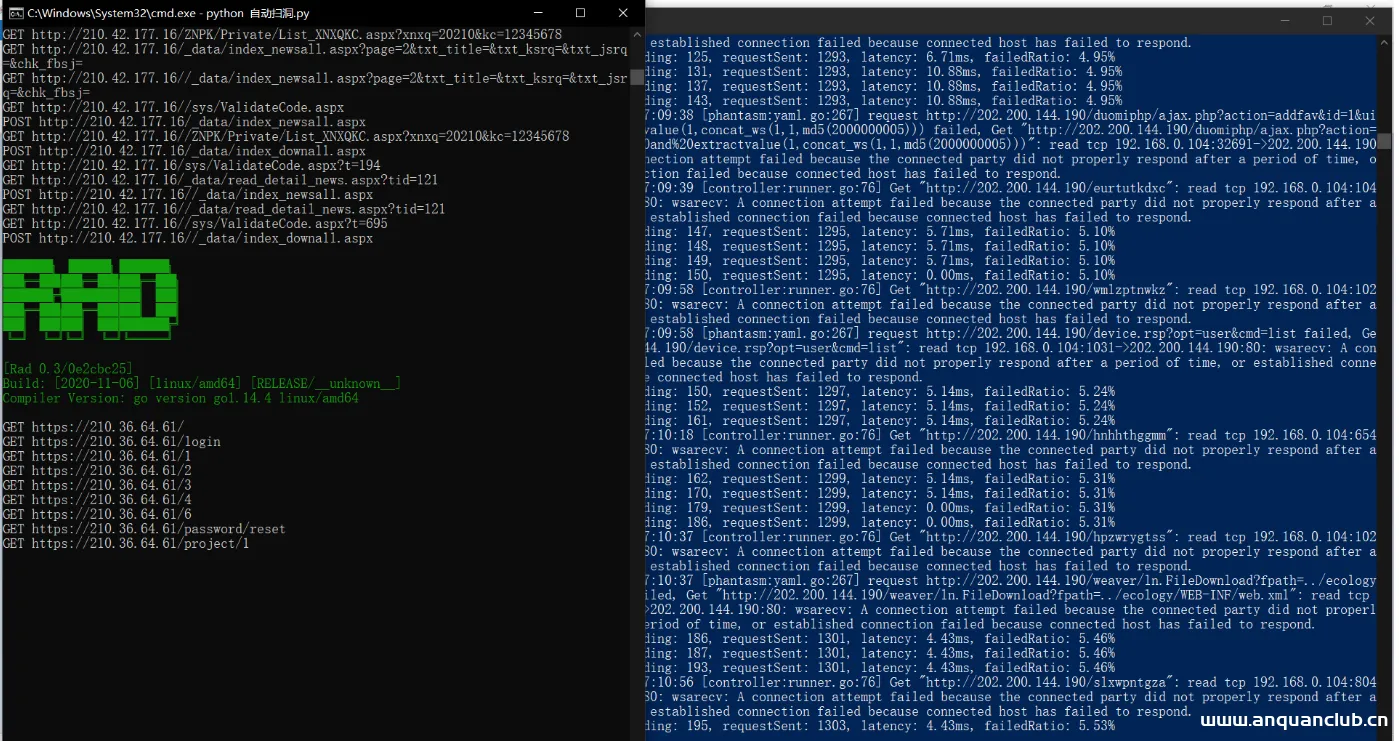
Rad爬虫——一款专为安全扫描而生的浏览器爬虫
rad,全名 Radium,名字来源于放射性元素——镭, 从一个URL开始,辐射到一整个站点空间 一款专为安全扫描而生的浏览器爬虫 下载地址 http://github.com/chaitin/rad/releases 快速使用 在...

 2023年1月13日 19:53
CVE-2021-42192: KONGA 0.14.9 – Privilege Escalation
漏洞标题 CVE-2021-42192: KONGA 0.14.9 - Privilege Escalation 漏洞描述 KONGA 0.14.9 allows attackers to set higher privilege users to full administration access. The attack vector i...
2021年12月24日 17:02CVE-2018-16979: Monstra CMS 3.0.4 – HTTP Header Injection
漏洞标题 CVE-2018-16979: Monstra CMS 3.0.4 - HTTP Header Injection 漏洞描述 Monstra CMS 3.0.4 is susceptible to HTTP header injection in the plugins/captcha/crypt/cryptographp.php ...
2018年1月29日 00:20
bugbounty技巧聚合20220112
漏洞报告 【Node.js 】通过 console.table 属性的原型污染 http://hackerone.com/reports/1431042 挖洞技巧 IDOR 漏洞 http://mukibas37.medium.com/idor-tryhackme-92823b28b1d 通过在 Web 应...
2022年3月10日 23:39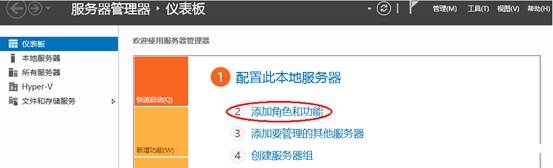
windows server 2019 服务器搭建的方法步骤(图文)_win服务器
这篇文章主要介绍了windows server 2019 服务器搭建的方法步骤(图文),文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编来一起学习学习...
2024年5月5日 20:49CVE-2017-7921: Hikvision – Authentication Bypass
漏洞标题 CVE-2017-7921: Hikvision - Authentication Bypass 漏洞描述 Hikvision DS-2CD2xx2F-I Series V5.2.0 build 140721 to V5.4.0 build 160530, DS-2CD2xx0F-I Series V5.2.0 build 1407...
2017年7月16日 14:58CVE-2024-21683: Atlassian Confluence Data Center and Server – Remote Code Execution
漏洞标题 CVE-2024-21683: Atlassian Confluence Data Center and Server - Remote Code Execution 漏洞描述 Detects a Remote Code Execution vulnerability in Confluence Data Center and Se...
2024年10月13日 04:23CVE-2024-24328: TotoLink Router setMacFilterRules – Command Injection
漏洞标题 CVE-2024-24328: TotoLink Router setMacFilterRules - Command Injection 漏洞描述 TOTOLINK A3300R V17.0.0cu.557_B20221024 was discovered to contain a command injection vulner...
2024年6月26日 14:35CVE-2022-0381: WordPress Embed Swagger <=1.0.0 - Cross-Site Scripting
漏洞标题 CVE-2022-0381: WordPress Embed Swagger <=1.0.0 - Cross-Site Scripting 漏洞描述 WordPress Embed Swagger plugin 1.0.0 and prior contains a reflected cross-site scripting ...
2022年3月8日 15:02
2026年11月9日 11:45
2026年11月8日 11:45
2026年11月7日 11:45
2026年11月6日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

