
最新发布第583页

【火线项目案例】如何挖到空白页面的高危级别未授权漏洞
在安全小天地平台的火器中看到一个资产,居然是空白页面,空白页面就没有漏洞???偏偏不信邪,上手就是干! http://xxx.target.com 打开页面啥也没有,一片空白 F12看下JS中的API接口,发现有...
 2022年3月10日 23:35

CVE-2022-37299: Shirne CMS 1.2.0 – Local File Inclusion
漏洞标题 CVE-2022-37299: Shirne CMS 1.2.0 - Local File Inclusion 漏洞描述 Shirne CMS 1.2.0 is vulnerable to local file inclusion which could cause arbitrary file read via /static/u...
2022年8月16日 21:39CVE-2023-4169: 锐捷(ruijie)RG-EW1200G路由器 未授权后台登录密码修改(谨慎使用)
漏洞标题 CVE-2023-4169: 锐捷(ruijie)RG-EW1200G路由器 未授权后台登录密码修改(谨慎使用) 漏洞描述 Ruijie Networks RG-EW1200G是中国锐捷网络(Ruijie Networks)公司的一款无线路由器。 ...
2023年7月24日 15:06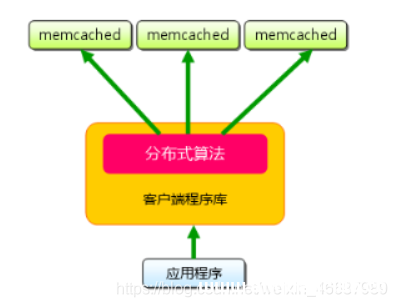
Memcached构建缓存服务器的方法_服务器其它
这篇文章主要介绍了Memcached构建缓存服务器的方法,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 前言 许多Web应用都将数据保存到关系型数据库(...
2023年4月17日 20:29CVE-2022-29303: SolarView Compact 6.00 – OS Command Injection
漏洞标题 CVE-2022-29303: SolarView Compact 6.00 - OS Command Injection 漏洞描述 SolarView Compact 6.00 was discovered to contain a command injection vulnerability via conf_mail.php...
2022年8月14日 13:11CVE-2005-3344: Horde Groupware Unauthenticated Admin Access
漏洞标题 CVE-2005-3344: Horde Groupware Unauthenticated Admin Access 漏洞描述 Horde Groupware contains an administrative account with a blank password, which allows remote attacker...
2005年1月10日 12:02CVE-2024-34351: Next.js – Server Side Request Forgery (SSRF)
漏洞标题 CVE-2024-34351: Next.js - Server Side Request Forgery (SSRF) 漏洞描述 Next.Js, inferior to version 14.1.1, have its image optimization built-in component prone to SSRF. Po...
2024年5月29日 04:46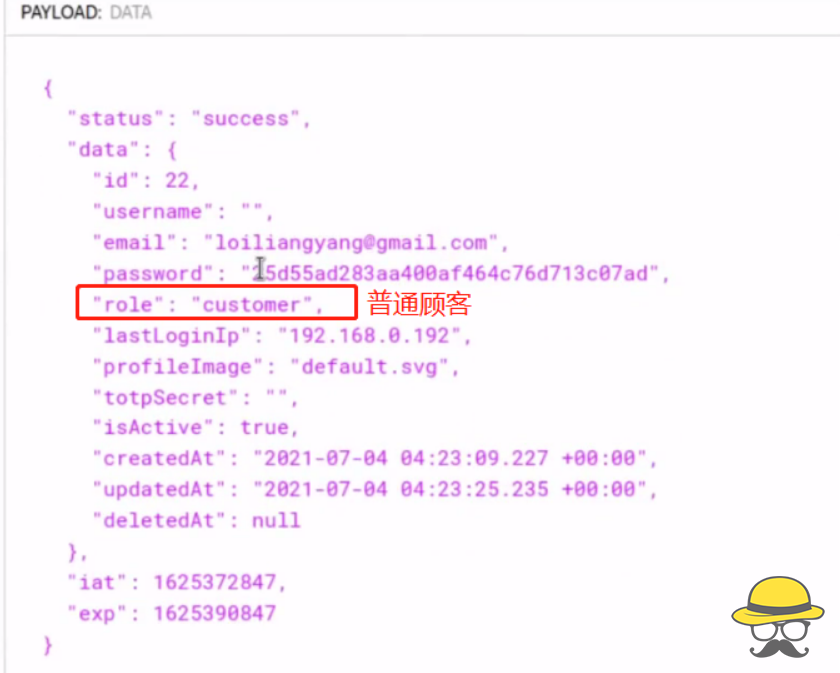
黑客如何不花一分钱获取某网站豪华会员
相关阅读 今天我们讲讲,如何通过json web token登录验证的一个漏洞来免费获取豪华会员 图文教程 我们发现用户在注册、登陆时,在payload中存在用户身份的信息,譬如非会员 再譬如豪华会员 这时...

 2022年4月1日 18:36
CVE-2022-3982: WordPress Booking Calendar <3.2.2 - Arbitrary File Upload
漏洞标题 CVE-2022-3982: WordPress Booking Calendar <3.2.2 - Arbitrary File Upload 漏洞描述 WordPress Booking Calendar plugin before 3.2.2 is susceptible to arbitrary file upload...
2022年12月15日 22:23CVE-2012-4982: Forescout CounterACT 6.3.4.1 – Open Redirect
漏洞标题 CVE-2012-4982: Forescout CounterACT 6.3.4.1 - Open Redirect 漏洞描述 Open redirect vulnerability in assets/login on the Forescout CounterACT NAC device before 7.0 allows r...
2012年10月12日 06:10CVE-2022-30073: WBCE CMS 1.5.2 – Cross-Site Scripting
漏洞标题 CVE-2022-30073: WBCE CMS 1.5.2 - Cross-Site Scripting 漏洞描述 WBCE CMS 1.5.2 contains a stored cross-site scripting vulnerability via \admin\user\save.php Display Name pa...
2022年9月14日 00:30CVE-2025-55169: WeGIA – Directory Traversal
漏洞标题 CVE-2025-55169: WeGIA - Directory Traversal 漏洞描述 WeGIA is an open source web manager with a focus on the Portuguese language and charitable institutions. Prior to vers...
2025年6月13日 17:01CVE-2021-27310: Clansphere CMS 2011.4 – Cross-Site Scripting
漏洞标题 CVE-2021-27310: Clansphere CMS 2011.4 - Cross-Site Scripting 漏洞描述 Clansphere CMS 2011.4 contains an unauthenticated reflected cross-site scripting vulnerability via th...
2021年8月27日 01:30
ubuntu20.04 LTS系统默认源sources.list文件的修改_Linux
这篇文章主要介绍了ubuntu20.04 LTS系统默认源sources.list文件的修改,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编来一起学习学...
2023年7月6日 21:27CVE-2021-42237: Sitecore Experience Platform Pre-Auth RCE
漏洞标题 CVE-2021-42237: Sitecore Experience Platform Pre-Auth RCE 漏洞描述 Sitecore XP 7.5 to Sitecore XP 8.2 Update 7 is vulnerable to an insecure deserialization attack where re...
2021年5月28日 15:02CVE-2022-1392: WordPress Videos sync PDF <=1.7.4 - Local File Inclusion
漏洞标题 CVE-2022-1392: WordPress Videos sync PDF <=1.7.4 - Local File Inclusion 漏洞描述 WordPress Videos sync PDF 1.7.4 and prior does not validate the p parameter before usin...
2022年11月29日 07:19
2026年11月9日 11:45
2026年11月8日 11:45
2026年11月7日 11:45
2026年11月6日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

