
最新发布第587页

CVE-2018-17246: Kibana – Local File Inclusion
漏洞标题 CVE-2018-17246: Kibana - Local File Inclusion 漏洞描述 Kibana versions before 6.4.3 and 5.6.13 contain an arbitrary file inclusion flaw in the Console plugin. An attacker ...
 2018年12月28日 07:13
CVE-2010-20103: ProFTPd-1.3.3c – Backdoor Command Execution
漏洞标题 CVE-2010-20103: ProFTPd-1.3.3c - Backdoor Command Execution 漏洞描述 ProFTPD 1.3.3c contains a command injection backdoor caused by a hidden FTP command trigger in the sou...
2010年8月3日 17:43CVE-2022-22897: PrestaShop AP Pagebuilder <= 2.4.4 - SQL Injection
漏洞标题 CVE-2022-22897: PrestaShop AP Pagebuilder <= 2.4.4 - SQL Injection 漏洞描述 A SQL injection vulnerability in the product_all_one_img and image_product parameters of the...
2022年7月8日 09:32CVE-2019-0230: Apache Struts <=2.5.20 - Remote Code Execution S2-059
漏洞标题 CVE-2019-0230: Apache Struts <=2.5.20 - Remote Code Execution S2-059 漏洞描述 Apache Struts 2.0.0 to 2.5.20 forced double OGNL evaluation when evaluated on raw user inp...
2019年6月4日 20:55
以隐私安全为由,苹果、谷歌反对美国国会拟议的反垄断法案
美国国会目前正在审议两项反垄断法案——《美国创新与在线选择法案(American Innovation And Choice Online Act)》和《开放应用市场法案(Open App Markets Act)》,旨在约束苹果、谷歌在内的大...
2022年3月10日 23:39CVE-2021-41291: ECOA Building Automation System – Directory Traversal Content Disclosure
漏洞标题 CVE-2021-41291: ECOA Building Automation System - Directory Traversal Content Disclosure 漏洞描述 The ECOA BAS controller suffers from a directory traversal content disclo...
2021年4月5日 07:33CVE-2021-32789: WooCommerce Blocks 2.5 to 5.5 – Unauthenticated SQL Injection
漏洞标题 CVE-2021-32789: WooCommerce Blocks 2.5 to 5.5 - Unauthenticated SQL Injection 漏洞描述 woocommerce-gutenberg-products-block is a feature plugin for WooCommerce Gutenberg B...
2021年7月26日 15:35CVE-2024-28000: WordPress LiteSpeed Cache – Unauthenticated Privilege Escalation to Admin
漏洞标题 CVE-2024-28000: WordPress LiteSpeed Cache - Unauthenticated Privilege Escalation to Admin 漏洞描述 Incorrect Privilege Assignment vulnerability in LiteSpeed Technologies L...
2024年10月6日 04:06CVE-2011-4640: WebTitan < 3.60 - Local File Inclusion
漏洞标题 CVE-2011-4640: WebTitan < 3.60 - Local File Inclusion 漏洞描述 Directory traversal vulnerability in logs-x.php in SpamTitan WebTitan before 3.60 allows remote authentic...
2011年11月12日 09:48CVE-2021-20123: Draytek VigorConnect 1.6.0-B – Local File Inclusion
漏洞标题 CVE-2021-20123: Draytek VigorConnect 1.6.0-B - Local File Inclusion 漏洞描述 Draytek VigorConnect 1.6.0-B3 is susceptible to local file inclusion in the file download func...
2021年12月9日 21:32CVE-2023-48728: WWBN AVideo 11.6 – Cross-Site Scripting
漏洞标题 CVE-2023-48728: WWBN AVideo 11.6 - Cross-Site Scripting 漏洞描述 A reflected XSS vulnerability exists in the functiongetOpenGraph videoName functionality of WWBN AVideo 11...
2023年7月17日 10:32CVE-2012-0981: phpShowtime 2.0 – Directory Traversal
漏洞标题 CVE-2012-0981: phpShowtime 2.0 - Directory Traversal 漏洞描述 A directory traversal vulnerability in phpShowtime 2.0 allows remote attackers to list arbitrary directories ...
2012年3月24日 08:22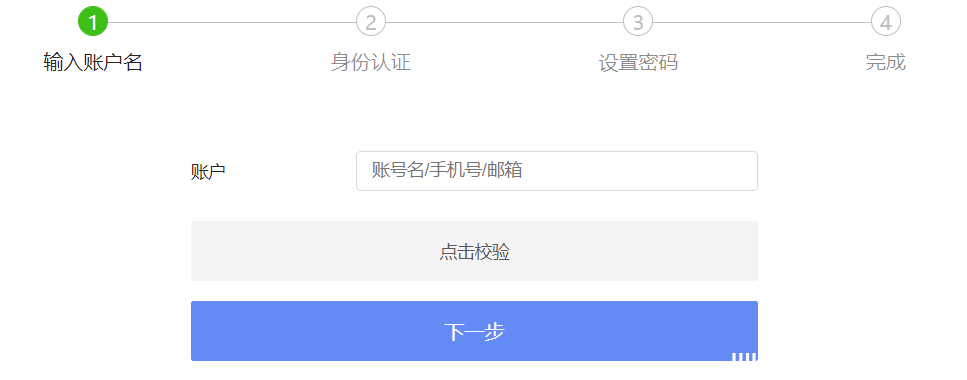
一次任意密码重置漏洞挖洞剖析
前言: 之前参加一家企业SRC挖洞,正赶上厂商搞活动,秉着有活动我就参加,有漏洞我就捡的良好心态,就去看了一下该企业的一些资产,因为活动是按漏洞危害等级给奖励,所以找一些边缘资产参加活...
2022年3月10日 23:32CVE-2023-52251: Kafka UI 0.7.1 Command Injection
漏洞标题 CVE-2023-52251: Kafka UI 0.7.1 Command Injection 漏洞描述 An issue discovered in provectus kafka-ui 0.4.0 through 0.7.1 allows remote attackers to execute arbitrary code v...
2023年5月22日 14:19CVE-2024-30188: Apache DolphinScheduler >= 3.1.0, < 3.2.2 Resource File Read And Write
漏洞标题 CVE-2024-30188: Apache DolphinScheduler >= 3.1.0, < 3.2.2 Resource File Read And Write 漏洞描述 File read and write vulnerability in Apache DolphinScheduler, authent...
2024年8月21日 10:37CVE-2012-4253: MySQLDumper 1.24.4 – Directory Traversal
漏洞标题 CVE-2012-4253: MySQLDumper 1.24.4 - Directory Traversal 漏洞描述 Multiple directory traversal vulnerabilities in MySQLDumper 1.24.4 allow remote attackers to read arbitrar...
2012年1月2日 17:42
2026年10月21日 11:45
2026年10月20日 11:45
2026年10月19日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

