
最新发布第5页

Linux下Jenkins忘记密码的操作步骤_Linux
这篇文章主要介绍了Linux下Jenkins忘记密码的操作步骤,本文给大家介绍的非常详细,具有一定的参考借鉴价值,需要的朋友可以参考下 1.Jenkins安装步骤: http://www.jb51.net/article/176615.htm...
 2026年3月15日 11:45

CVE-2012-4242: WordPress Plugin MF Gig Calendar 0.9.2 – Cross-Site Scripting
漏洞标题 CVE-2012-4242: WordPress Plugin MF Gig Calendar 0.9.2 - Cross-Site Scripting 漏洞描述 A cross-site scripting vulnerability in the MF Gig Calendar plugin 0.9.2 for WordPres...
2012年7月1日 09:15CVE-2022-23131: Zabbix – SAML SSO Authentication Bypass
漏洞标题 CVE-2022-23131: Zabbix - SAML SSO Authentication Bypass 漏洞描述 When SAML SSO authentication is enabled (non-default), session data can be modified by a malicious actor b...
2022年10月18日 15:02CVE-2010-2018: Lokomedia CMS – Local File Inclusion
漏洞标题 CVE-2010-2018: Lokomedia CMS - Local File Inclusion 漏洞描述 A Local File Inclusion (LFI) vulnerability exists in Lokomedia CMS. The application allows an attacker to incl...
2010年8月29日 22:54CVE-2022-3982: WordPress Booking Calendar <3.2.2 - Arbitrary File Upload
漏洞标题 CVE-2022-3982: WordPress Booking Calendar <3.2.2 - Arbitrary File Upload 漏洞描述 WordPress Booking Calendar plugin before 3.2.2 is susceptible to arbitrary file upload...
2022年1月16日 01:22CVE-2024-36683: PrestaShop productsalert – SQL Injection
漏洞标题 CVE-2024-36683: PrestaShop productsalert - SQL Injection 漏洞描述 In the module 'Products Alert' (productsalert) up to version 1.7.4 from Smart Modules for Prest...
2024年1月5日 20:18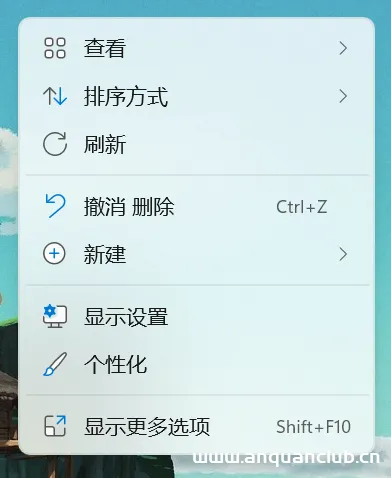
Win11桌面右键菜单栏怎么回到Win10的样子(直接命令执行便可完成,简单快捷)
很多小伙伴在用Win11的时候都有因为它的右键菜单栏所苦恼吧。 每次在解压一个文件的时候都要多点击一下 “显示更多选项” 才可以出现完整的菜单栏, 在我的电脑文件夹当中也需要点击 “显示更多...

 2022年8月17日 12:15
CVE-2019-15713: WordPress My Calendar <= 3.1.9 - Cross-Site Scripting
漏洞标题 CVE-2019-15713: WordPress My Calendar <= 3.1.9 - Cross-Site Scripting 漏洞描述 WordPress plugin My Calendar <= 3.1.9 is susceptible to reflected cross-site scripting...
2019年10月10日 01:43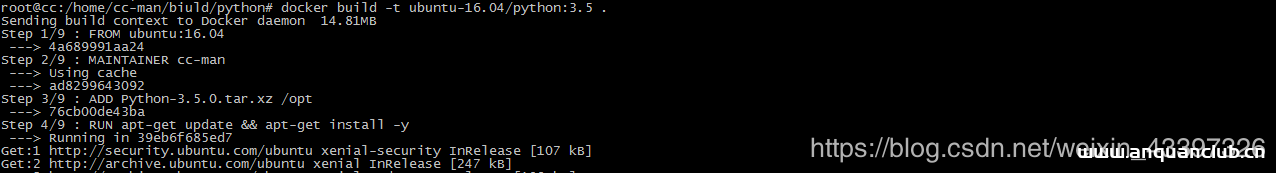
Docker制作Python运行环境基础镜像的方法步骤_docker
这篇文章主要介绍了Docker制作Python运行环境基础镜像的方法步骤,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编来一起学习学习吧 一...
2024年7月14日 20:14CVE-2022-0218: HTML Email Template Designer < 3.1 - Stored Cross-Site Scripting
漏洞标题 CVE-2022-0218: HTML Email Template Designer < 3.1 - Stored Cross-Site Scripting 漏洞描述 WordPress Email Template Designer WP HTML Mail allows stored cross-site scripti...
2022年5月22日 18:27CVE-2025-25257: Fortinet FortiWeb – SQL Injection
漏洞标题 CVE-2025-25257: Fortinet FortiWeb - SQL Injection 漏洞描述 An improper neutralization of special elements used in an SQL command ('SQL Injection') vulnerability ...
2025年9月29日 13:41CVE-2025-3605: WordPress Frontend Login and Registration Blocks Plugin 1.0.7 – Privilege Escalation
漏洞标题 CVE-2025-3605: WordPress Frontend Login and Registration Blocks Plugin 1.0.7 - Privilege Escalation 漏洞描述 Privilege escalation vulnerability exists in the Frontend Logi...
2025年3月14日 09:20CVE-2016-7834: Sony IPELA Engine IP Camera – Hardcoded Account
漏洞标题 CVE-2016-7834: Sony IPELA Engine IP Camera - Hardcoded Account 漏洞描述 Multiple SONY network cameras are vulnerable to sensitive information disclosure via hardcoded cred...
2016年2月11日 17:38
-CVE-2018-9207 jquery Upload File文件上传
本文转载于公众号:融云攻防实验室,原文地址: 漏洞复现-CVE-2018-9207 jquery Upload File文件上传 jQuery是一个快速、简洁的JavaScript框架,是继Prototype之后又一个优秀的JavaScript代码...
2023年2月10日 11:26CVE-2017-5871: Odoo <= 8.0-20160726 & 9.0 - Open Redirect
漏洞标题 CVE-2017-5871: Odoo <= 8.0-20160726 & 9.0 - Open Redirect 漏洞描述 An Open Redirect vulnerability in Odoo versions <= 8.0-20160726 and 9.0. This issue allows an ...
2017年10月1日 08:48CraftCms 代码注入漏洞(CVE-2025-32432)
漏洞标题 CraftCms 代码注入漏洞(CVE-2025-32432) 漏洞描述 攻击者可构造恶意请求利用generate-transform端点触发反序列化,执行任意代码控制服务器,未经身份验证的攻击者可以通过该漏洞在目标...
2025年1月9日 10:31
2026年9月15日 11:45
2026年9月14日 11:45
2026年9月13日 11:45
2026年9月12日 12:55
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月2日 09:46
2026年8月16日 20:18
2026年8月11日 13:39
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

