
最新发布第5页

CVE-2019-8943: WordPress Core 5.0.0 – Crop-image Shell Upload
漏洞标题 CVE-2019-8943: WordPress Core 5.0.0 - Crop-image Shell Upload 漏洞描述 WordPress through 5.0.3 allows Path Traversal in wp_crop_image(). An attacker (who has privileges to...
 2019年2月24日 14:52
CVE-2024-47533: Cobbler ‘XML-RPC’ – Authentication Bypass
漏洞标题 CVE-2024-47533: Cobbler 'XML-RPC' - Authentication Bypass 漏洞描述 Cobbler, a Linux installation server that allows for rapid setup of network installation envir...
2024年5月22日 01:16CVE-2020-24312: WordPress Plugin File Manager (wp-file-manager) Backup Disclosure
漏洞标题 CVE-2020-24312: WordPress Plugin File Manager (wp-file-manager) Backup Disclosure 漏洞描述 mndpsingh287 WP File Manager v6.4 and lower fails to restrict external access to...
2020年10月22日 13:23Altenergy Power Control Software management_model.php存在命令注入漏洞(CVE-2023-28343)
漏洞标题 Altenergy Power Control Software management_model.php存在命令注入漏洞(CVE-2023-28343) 漏洞描述 Altenergy Power System Control Software是Altenergy PowerSystem公司的微型逆变...
2023年10月31日 18:04CData Sync CVE-2024-31851 路径遍历漏洞
漏洞标题 CData Sync CVE-2024-31851 路径遍历漏洞 漏洞描述 CData sync存在路径遍历漏洞,此漏洞是由于/ui/接口对用户的请求验证不当造成的。 PoC代码 暂无
2024年10月20日 03:11CVE-2018-17431: Comodo Unified Threat Management Web Console – Remote Code Execution
漏洞标题 CVE-2018-17431: Comodo Unified Threat Management Web Console - Remote Code Execution 漏洞描述 Comodo Firewall & Central Manager (UTM) All Release before 2.7.0 & 1....
2018年1月12日 07:04CVE-2022-38295: Cuppa CMS v1.0 – Cross Site Scripting
漏洞标题 CVE-2022-38295: Cuppa CMS v1.0 - Cross Site Scripting 漏洞描述 Cuppa CMS v1.0 was discovered to contain a cross-site scripting vulnerability at /table_manager/view/cu_user...
2022年8月24日 00:45
tomcat异常解决(Invalid character found in the request target. The valid characters are defined in RFC 7230 and RFC 3986)_Tomcat
这篇文章主要介绍了tomcat 异常的解决方案,帮助大家排查错误,保持服务器的稳定,感兴趣的朋友可以了解下 1.情景展示 tomcat 日志时不时会报出如下异常信息,到底是怎么回事? java.lang.Illeg...
2023年4月2日 20:29
我有一个朋友,他被裸聊诈骗了。我只能看看能不能帮帮他
小说三要素:时间、地点、人物 时间:2021年12月份 地点:互联网 人物:我有一个朋友 我有一个朋友,当时跟我说的时候已经被骗了23w,想继续充钱10w,问我能不能继续冲,我听了来龙去脉,很明显...
2022年3月10日 23:36CVE-2021-20091: Buffalo WSR-2533DHPL2 – Configuration File Injection
漏洞标题 CVE-2021-20091: Buffalo WSR-2533DHPL2 - Configuration File Injection 漏洞描述 The web interfaces of Buffalo WSR-2533DHPL2 firmware version <= 1.02 and WSR-2533DHP3 firm...
2021年11月8日 23:35CVE-2020-8191: Citrix ADC/Gateway – Cross-Site Scripting
漏洞标题 CVE-2020-8191: Citrix ADC/Gateway - Cross-Site Scripting 漏洞描述 Citrix ADC and Citrix Gateway versions before 13.0-58.30, 12.1-57.18, 12.0-63.21, 11.1-64.14 and 10.5-70....
2020年11月3日 17:14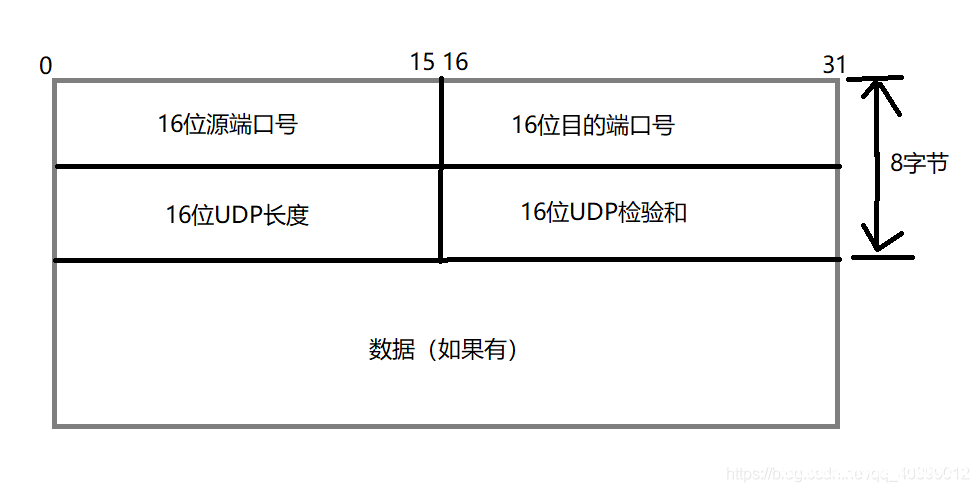
linux对于UDP的学习_Linux
本文将学习linux对于UDP的学习,UDP(用户数据报协议)没有连接的,是面向数据报的,是不可靠,点进来的小伙伴一起来学习吧 目录一、UDP、linux基础介绍二、对于各函数使用1、对于socket函数的...
2022年6月17日 10:00CVE-2023-0876: WordPress Meta SEO <= 4.5.2 - Open Redirect
漏洞标题 CVE-2023-0876: WordPress Meta SEO <= 4.5.2 - Open Redirect 漏洞描述 The WP Meta SEO WordPress plugin before 4.5.3 did not authorize several AJAX actions, which allowed ...
2023年2月2日 16:02CVE-2023-26256: STAGIL Navigation for Jira Menu & Themes <2.0.52 - Local File Inclusion
漏洞标题 CVE-2023-26256: STAGIL Navigation for Jira Menu & Themes <2.0.52 - Local File Inclusion 漏洞描述 STAGIL Navigation for Jira Menu & Themes plugin before 2.0.52 i...
2023年7月11日 05:05CVE-2021-37304: Jeecg Boot <= 2.4.5 - Information Disclosure
漏洞标题 CVE-2021-37304: Jeecg Boot <= 2.4.5 - Information Disclosure 漏洞描述 An Insecure Permissions issue in jeecg-boot 2.4.5 allows unauthenticated remote attackers to gain ...
2021年5月25日 01:21CVE-2023-2059: DedeCMS 5.7.87 – Directory Traversal
漏洞标题 CVE-2023-2059: DedeCMS 5.7.87 - Directory Traversal 漏洞描述 Directory traversal vulnerability in DedeCMS 5.7.87 allows reading sensitive files via the $activepath paramet...
2023年12月30日 19:00
2026年10月24日 11:45
2026年10月23日 11:45
2026年10月22日 11:46
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

