
最新发布第604页

Boa/0.94.13信息泄露(CVE-2021-33558)
漏洞标题 Boa/0.94.13信息泄露(CVE-2021-33558) 漏洞描述 BOA服务器是一个小巧高效的web服务器,是一个运行于unix或linux下的,支持CGI的、适合于嵌入式系统的单任务的http服务器,源代码开放、...
 2021年9月14日 09:11
CVE-2010-1352: Joomla! Component Juke Box 1.7 – Local File Inclusion
漏洞标题 CVE-2010-1352: Joomla! Component Juke Box 1.7 - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the JOOFORGE Jutebox (com_jukebox) component 1.0 and 1...
2010年5月27日 14:12CVE-2024-41107: Apache CloudStack – SAML Signature Exclusion
漏洞标题 CVE-2024-41107: Apache CloudStack - SAML Signature Exclusion 漏洞描述 The CloudStack SAML authentication (disabled by default) does not enforce signature check. In CloudSt...
2024年11月3日 12:13CVE-2012-0981: phpShowtime 2.0 – Directory Traversal
漏洞标题 CVE-2012-0981: phpShowtime 2.0 - Directory Traversal 漏洞描述 A directory traversal vulnerability in phpShowtime 2.0 allows remote attackers to list arbitrary directories ...
2012年5月25日 11:25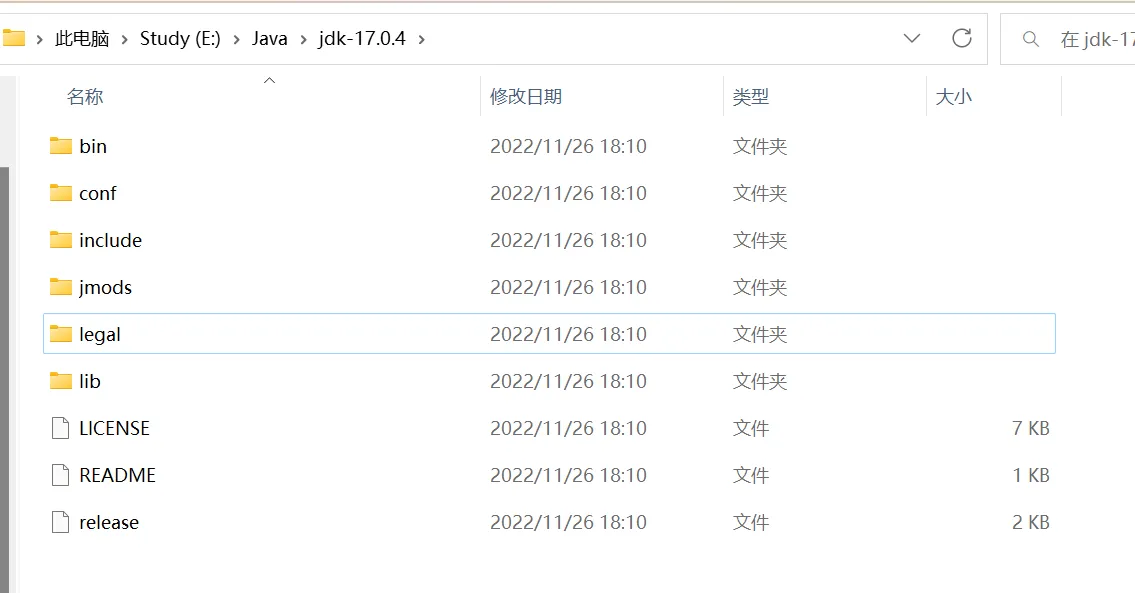
java11以上高版本没有jre文件夹 jre文件夹设置
1、安装jdk17后,发现jdk17并没有自动安装jre环境,但是很多基于java的开发工具,是需要配置jre路径的。 2.其实jdk17的安装包里是自带jre的,只不过没有自动安装,手动安装一下就可以了。 输入c...

 2023年1月13日 19:36
Apache Tomcat Ajp webapp 任意文件读取漏洞(CVE-2020-1938)
漏洞标题 Apache Tomcat Ajp webapp 任意文件读取漏洞(CVE-2020-1938) 漏洞描述 ApacheTomcat会开启AJP连接器,方便与其他Web服务器通过AJP协议进行交互。由于Tomcat本身也内含了HTTP服务器,因...
2020年12月16日 12:44CVE-2017-3528: Oracle E-Business Suite 12.1.3/12.2.x – Open Redirect
漏洞标题 CVE-2017-3528: Oracle E-Business Suite 12.1.3/12.2.x - Open Redirect 漏洞描述 The Oracle Applications Framework component of Oracle E-Business Suite (subcomponent: Popup w...
2017年9月17日 16:43CVE-2022-24260: VoipMonitor – Pre-Auth SQL Injection
漏洞标题 CVE-2022-24260: VoipMonitor - Pre-Auth SQL Injection 漏洞描述 A SQL injection vulnerability in Voipmonitor GUI before v24.96 allows attackers to escalate privileges to the...
2022年11月12日 14:32CVE-2024-45440: Drupal 11.x-dev – Full Path Disclosure
漏洞标题 CVE-2024-45440: Drupal 11.x-dev - Full Path Disclosure 漏洞描述 core/authorize.php in Drupal 11.x-dev allows Full Path Disclosure (even when error logging is None) if the ...
2024年11月29日 18:32CVE-2023-22463: KubePi JwtSigKey – Admin Authentication Bypass
漏洞标题 CVE-2023-22463: KubePi JwtSigKey - Admin Authentication Bypass 漏洞描述 KubePi is a k8s panel. The jwt authentication function of KubePi through version 1.6.2 uses hard-co...
2023年8月8日 21:48CVE-2021-41432: FlatPress 1.2.1 – Stored Cross-Site Scripting
漏洞标题 CVE-2021-41432: FlatPress 1.2.1 - Stored Cross-Site Scripting 漏洞描述 FlatPress 1.2.1 contains a stored cross-site scripting vulnerability that allows for arbitrary execu...
2021年2月14日 12:46CVE-2024-43917: WordPress TI WooCommerce Wishlist Plugin <= 2.8.2 - SQL Injection
漏洞标题 CVE-2024-43917: WordPress TI WooCommerce Wishlist Plugin <= 2.8.2 - SQL Injection 漏洞描述 In the latest version (2.8.2 as of writing the article) and below, the plugin...
2024年8月2日 11:23CVE-2021-22214: Gitlab CE/EE 10.5 – Server-Side Request Forgery
漏洞标题 CVE-2021-22214: Gitlab CE/EE 10.5 - Server-Side Request Forgery 漏洞描述 GitLab CE/EE versions starting from 10.5 are susceptible to a server-side request forgery vulnerab...
2021年4月19日 03:18CVE-2023-4112: PHPJabbers Shuttle Booking Software 1.0 – Cross Site Scripting
漏洞标题 CVE-2023-4112: PHPJabbers Shuttle Booking Software 1.0 - Cross Site Scripting 漏洞描述 The attacker can send to victim a link containing a malicious URL in an email or ins...
2023年10月10日 19:28Chamilo存在命令执行漏洞(CVE-2023-34960)
漏洞标题 Chamilo存在命令执行漏洞(CVE-2023-34960) 漏洞描述 Chamilo是一款可供用户免费下载的学习管理软件,Chamilo存在命令执行漏洞,恶意攻击者可以通过构造的xml文件任意命令,进而控制服务...
2023年4月28日 07:33CVE-2023-27637: PrestaShop `tshirtecommerce` Module – SQL Injection
漏洞标题 CVE-2023-27637: PrestaShop `tshirtecommerce` Module - SQL Injection 漏洞描述 The tshirtecommerce module for PrestaShop is vulnerable to unauthenticated SQL injection via t...
2023年10月12日 09:24
2026年11月17日 11:45
2026年11月16日 11:45
2026年11月15日 11:45
2026年11月14日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

