
最新发布第606页

CVE-2022-33901: WordPress MultiSafepay for WooCommerce <=4.13.1 - Arbitrary File Read
漏洞标题 CVE-2022-33901: WordPress MultiSafepay for WooCommerce <=4.13.1 - Arbitrary File Read 漏洞描述 WordPress MultiSafepay for WooCommerce plugin through 4.13.1 contains an ...
 2022年3月12日 11:45
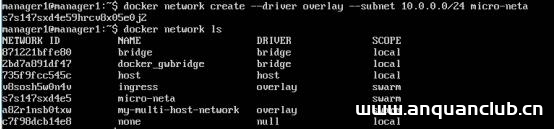
解决Docker network Create加–subnet后遇到问题_docker
这篇文章主要介绍了解决Docker network Create加--subnet后遇到问题。具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 Docker network Create加–subnet后,使用docker networ...
2023年1月7日 20:36CVE-2011-2523: VSFTPD 2.3.4 – Backdoor Command Execution
漏洞标题 CVE-2011-2523: VSFTPD 2.3.4 - Backdoor Command Execution 漏洞描述 VSFTPD v2.3.4 had a serious backdoor vulnerability allowing attackers to execute arbitrary commands on th...
2011年10月13日 08:02CVE-2022-32770: WWBN AVideo 11.6 – Cross-Site Scripting
漏洞标题 CVE-2022-32770: WWBN AVideo 11.6 - Cross-Site Scripting 漏洞描述 WWBN AVideo 11.6 contains a cross-site scripting vulnerability in the footer alerts functionality via the ...
2022年7月21日 05:10CVE-2022-2314: WordPress VR Calendar <=2.3.2 - Remote Code Execution
漏洞标题 CVE-2022-2314: WordPress VR Calendar <=2.3.2 - Remote Code Execution 漏洞描述 WordPress VR Calendar plugin through 2.3.2 is susceptible to remote code execution. The pl...
2022年4月4日 11:48CVE-2021-24215: Controlled Admin Access WordPress Plugin <= 1.4.0 - Improper Access Control & Privilege Escalation
漏洞标题 CVE-2021-24215: Controlled Admin Access WordPress Plugin <= 1.4.0 - Improper Access Control & Privilege Escalation 漏洞描述 An Improper Access Control vulnerability...
2021年12月24日 17:27CVE-2024-23897: Jenkins < 2.441 - Arbitrary File Read
漏洞标题 CVE-2024-23897: Jenkins < 2.441 - Arbitrary File Read 漏洞描述 Jenkins 2.441 and earlier, LTS 2.426.2 and earlier does not disable a feature of its CLI command parser t...
2024年12月13日 20:14CVE-2021-24351: WordPress The Plus Addons for Elementor <4.1.12 - Cross-Site Scripting
漏洞标题 CVE-2021-24351: WordPress The Plus Addons for Elementor <4.1.12 - Cross-Site Scripting 漏洞描述 WordPress The Plus Addons for Elementor plugin before 4.1.12 is suscepti...
2021年6月26日 13:53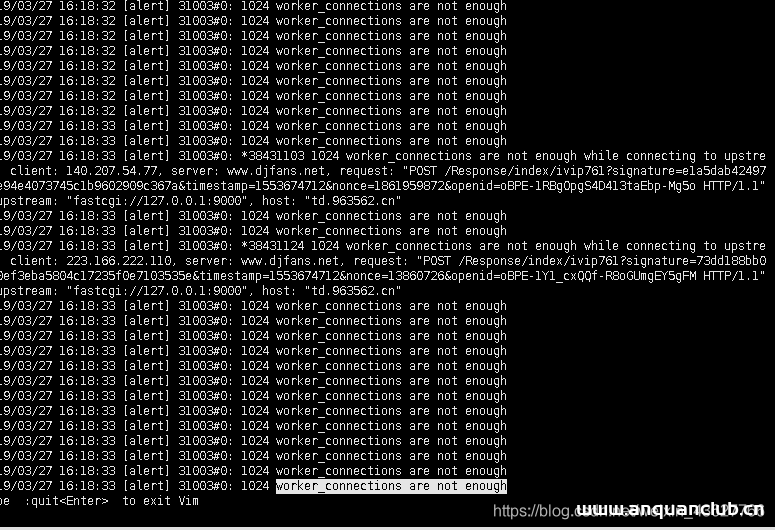
nginx服务器异常502 bad gateway原因排查_nginx
这篇文章主要介绍了nginx服务器异常502 bad gateway原因排查,本篇文章通过简要的案例,讲解了该项技术的了解与使用,以下就是详细内容,需要的朋友可以参考下 服务器进行公众号粉丝数据同步以及批...
2022年6月15日 09:45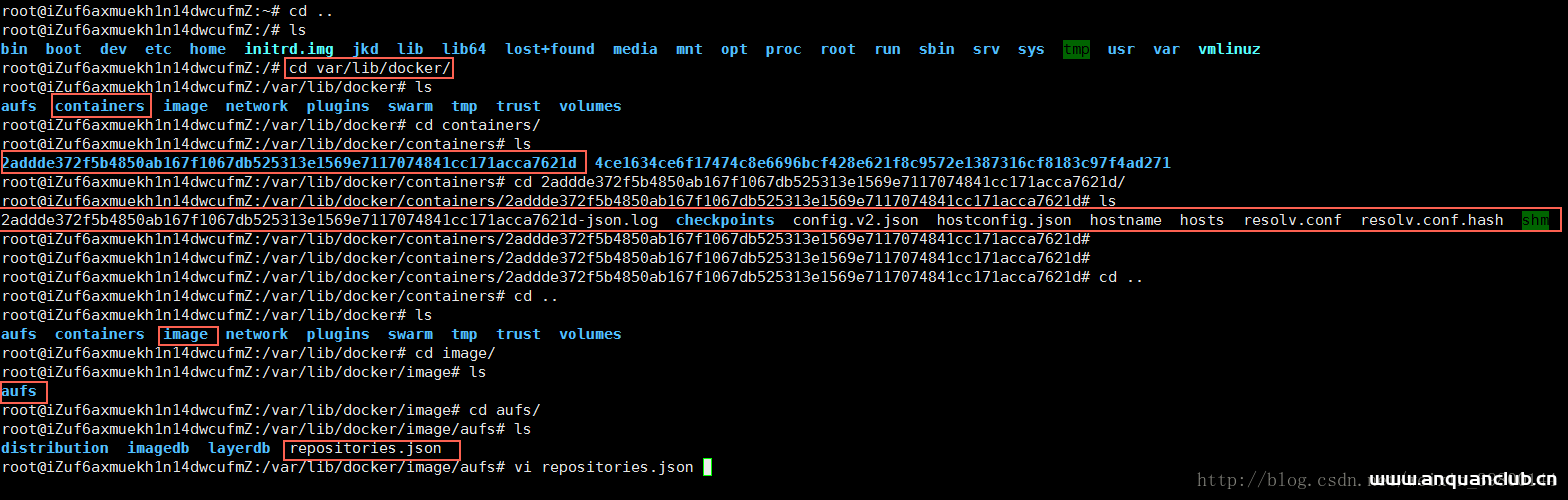
详解docker pull下来的镜像存储在哪里_docker
这篇文章主要介绍了详解docker pull下来的镜像存储在哪里,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编来一起学习学习吧 20200804...
2022年11月9日 21:34CVE-2019-5591: FortiOS – Insecure LDAP Configuration Detection
漏洞标题 CVE-2019-5591: FortiOS - Insecure LDAP Configuration Detection 漏洞描述 The FortiGate LDAP configuration was detected to be insecure due to missing ca-cert, secure LDAPS, ...
2019年2月3日 10:55CVE-2020-24391: Mongo-Express – Remote Code Execution
漏洞标题 CVE-2020-24391: Mongo-Express - Remote Code Execution 漏洞描述 Mongo-Express before 1.0.0 is susceptible to remote code execution because it uses safer-eval to validate us...
2020年6月12日 17:20CVE-2021-25065: Smash Balloon Social Post Feed < 4.1.1 - Authenticated Reflected Cross-Site Scripting
漏洞标题 CVE-2021-25065: Smash Balloon Social Post Feed < 4.1.1 - Authenticated Reflected Cross-Site Scripting 漏洞描述 The plugin was affected by a reflected XSS in custom-face...
2021年11月1日 14:28cloudpanel /file-manager/backend/makefile 任意文件上传漏洞(CVE-2023-35885)
漏洞标题 cloudpanel /file-manager/backend/makefile 任意文件上传漏洞(CVE-2023-35885) 漏洞描述 CloudPanel是CloudPanel开源的一款免费软件。用于配置和管理服务器。CloudPanel 2.3.1之前...
2023年8月7日 12:40CVE-2019-16931: WordPress Visualizer <3.3.1 - Cross-Site Scripting
漏洞标题 CVE-2019-16931: WordPress Visualizer <3.3.1 - Cross-Site Scripting 漏洞描述 WordPress Visualizer plugin before 3.3.1 contains a stored cross-site scripting vulnerabilit...
2019年10月8日 23:35
白帽训练营-如何学习web安全
学习的本质是模仿,创造的精髓在洞察。 1、如何学习web安全? 2、如何挖到第一个漏洞? 我的答案是: 1、掌握最基本的信息收集技巧 2、理解http数据包 3、使用burp进行http流量的截断和重放 4、...
2022年3月10日 23:35
2026年10月19日 11:45
2026年10月18日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

