
最新发布第618页

CVE-2024-24328: TotoLink Router setMacFilterRules – Command Injection
漏洞标题 CVE-2024-24328: TotoLink Router setMacFilterRules - Command Injection 漏洞描述 TOTOLINK A3300R V17.0.0cu.557_B20221024 was discovered to contain a command injection vulner...
 2024年7月10日 17:17
通过时间信息定位恶意进程和样本
Linux 在已知恶意域名/IP的情况下,可以通过边界设备查询首次域名解析、IP通联的时间,基于时间信息往往就可以定位到恶意进程及文件位置。 例如首次域名/IP出现的时间为2024年7月2日,可以查询2...

 2026年3月1日 15:46

CVE-2023-26255: STAGIL Navigation for Jira Menu & Themes <2.0.52 - Local File Inclusion
漏洞标题 CVE-2023-26255: STAGIL Navigation for Jira Menu & Themes <2.0.52 - Local File Inclusion 漏洞描述 STAGIL Navigation for Jira Menu & Themes plugin before 2.0.52 i...
2023年8月18日 15:48CVE-2024-21644: pyLoad Flask Config – Access Control
漏洞标题 CVE-2024-21644: pyLoad Flask Config - Access Control 漏洞描述 pyLoad is the free and open-source Download Manager written in pure Python. Any unauthenticated user can brow...
2024年1月16日 18:03运行wpscan报错Could not find ‘nokogiri’ (~> 1.8.0)
/usr/local/lib/site_ruby/2.7.0/rubygems/dependency.rb:313:in `to_specs': Could not find 'nokogiri' (~> 1.8.0) - did find: [nokogiri-1.10.9] (Gem::MissingSpecVersionError) Checked i...
2022年3月24日 16:27CVE-2016-1000127: WordPress AJAX Random Post <=2.00 - Cross-Site Scripting
漏洞标题 CVE-2016-1000127: WordPress AJAX Random Post <=2.00 - Cross-Site Scripting 漏洞描述 WordPress AJAX Random Post 2.00 is vulnerable to reflected cross-site scripting. PoC...
2016年3月10日 19:45CVE-2021-3110: PrestaShop 1.7.7.0 – SQL Injection
漏洞标题 CVE-2021-3110: PrestaShop 1.7.7.0 - SQL Injection 漏洞描述 PrestaShop 1.7.7.0 contains a SQL injection vulnerability via the store system. It allows time-based boolean SQL...
2021年11月20日 01:13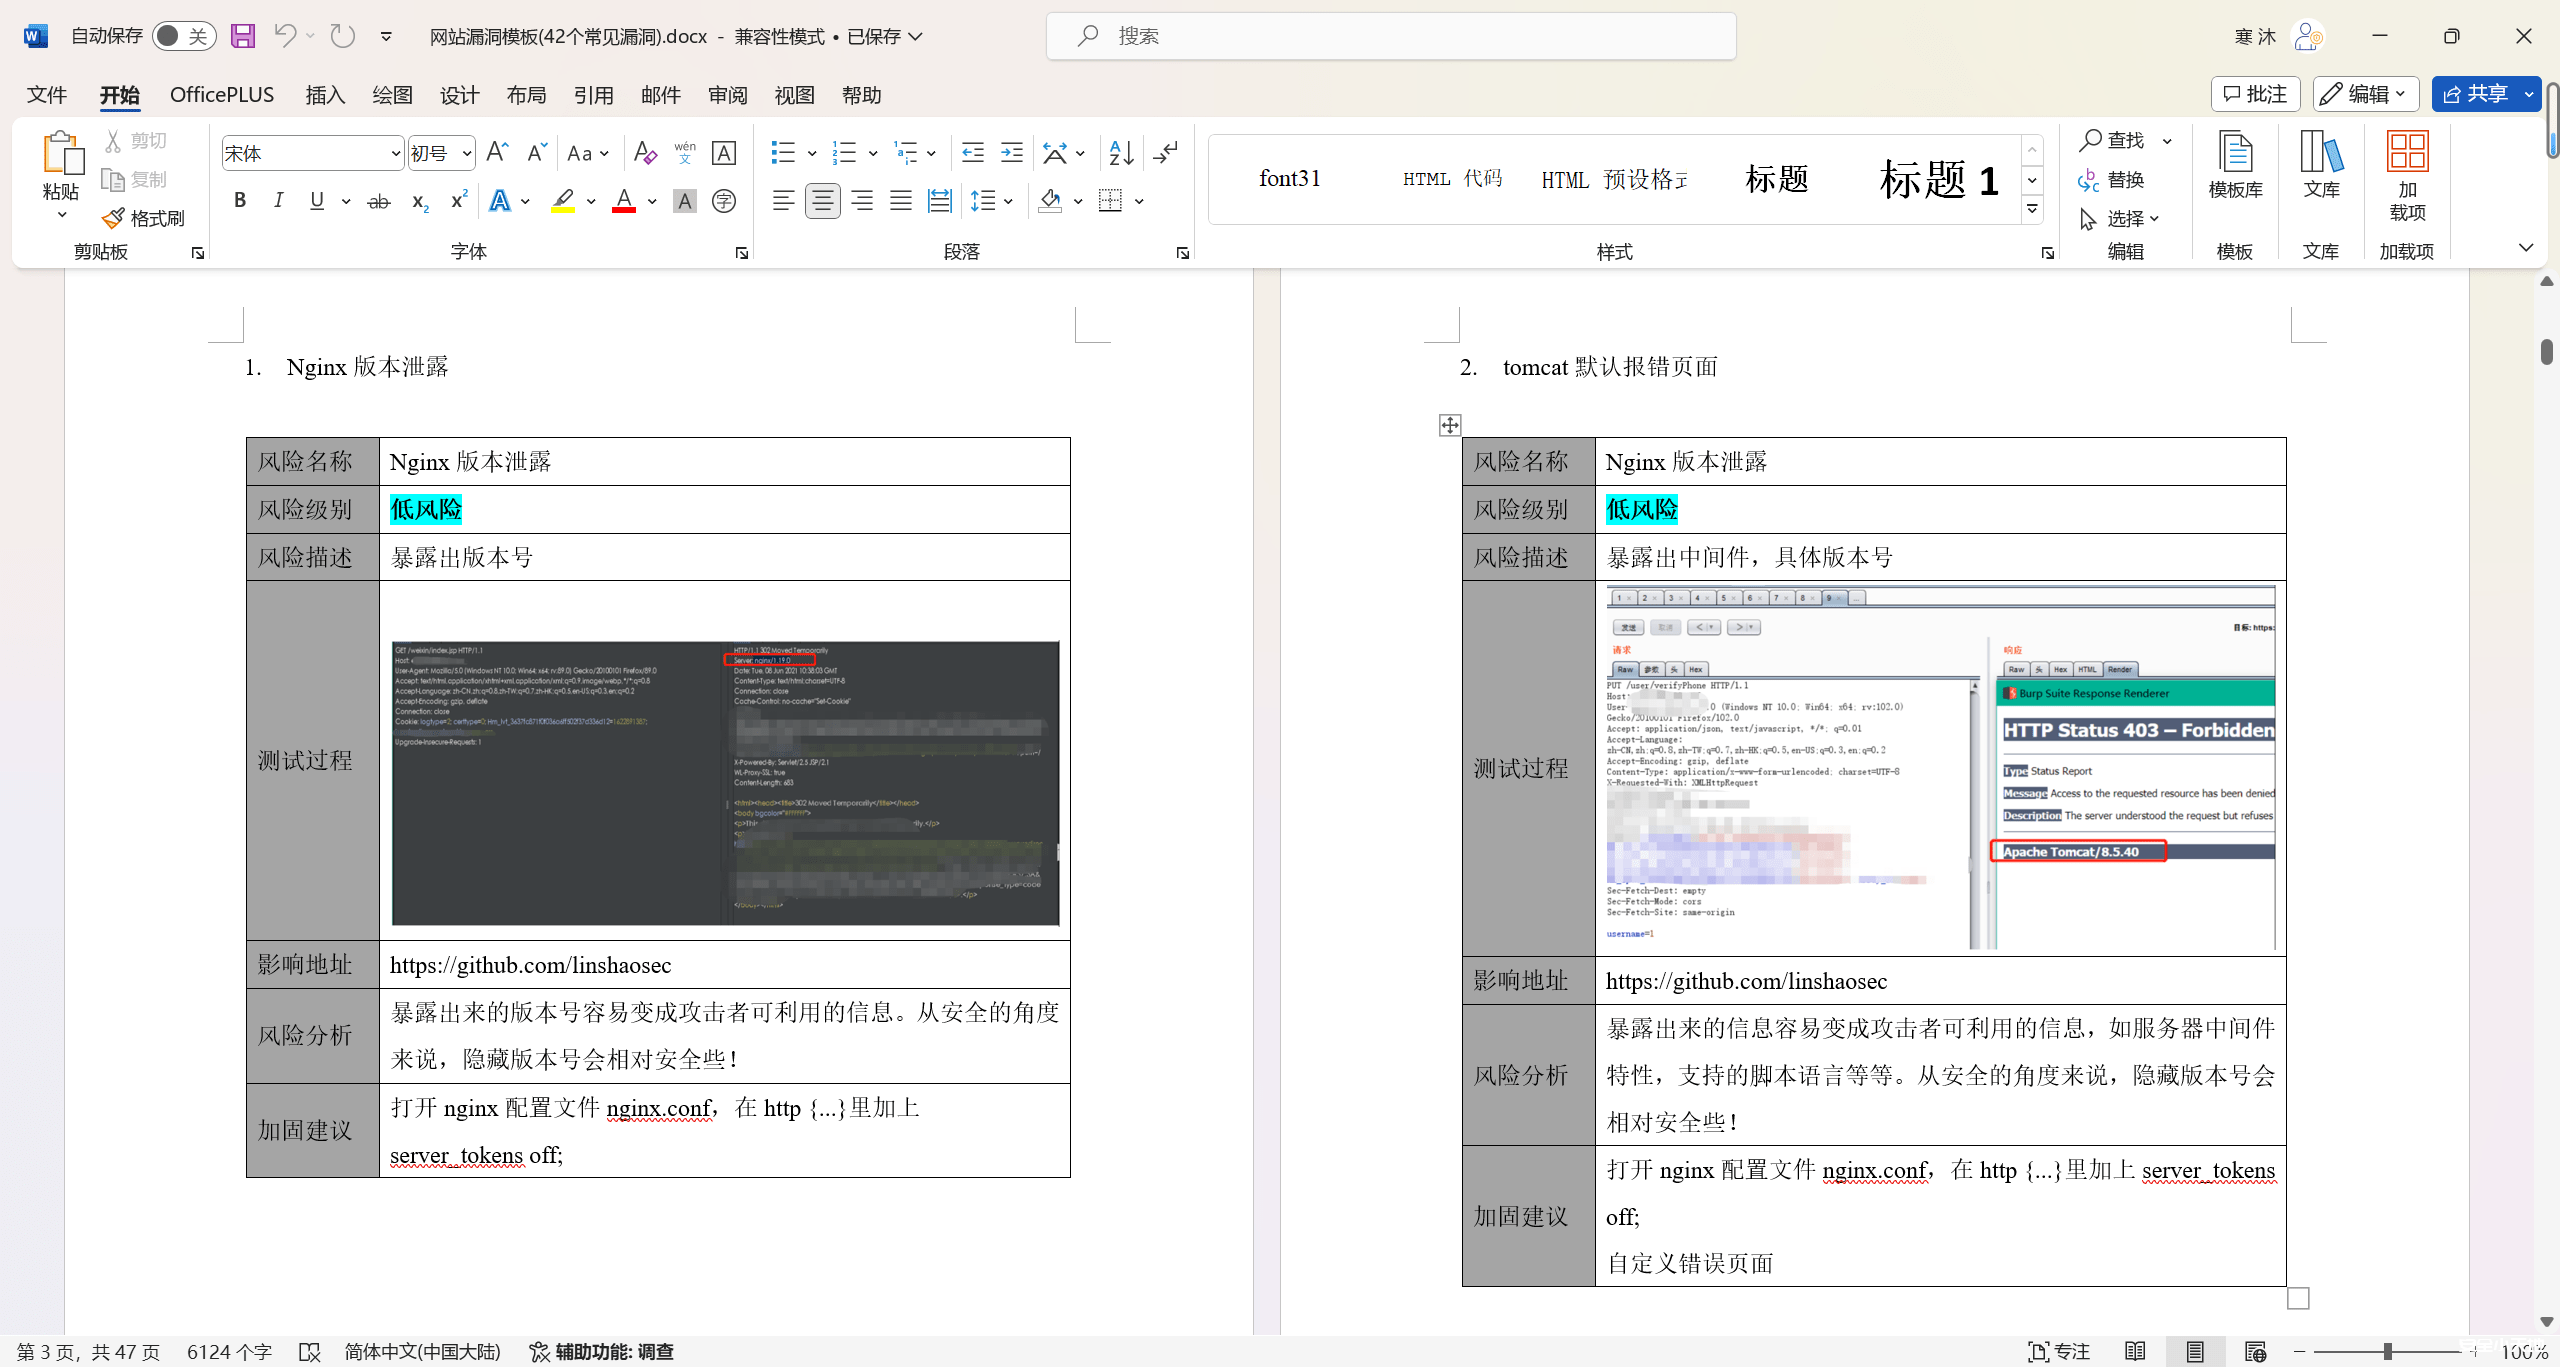
WaterExp:一款面向安服仔的扫描报告模板 和 碰瓷工具
项目名称 WaterExp 打工人新时代的摸鱼解决方案,安抚仔挖不到洞的最后一丝欢颜! http://github.com/linshaoSec/WaterExp 项目简介 (不产生实际攻击) (不会getshell) (面向水报告) 什么...
2023年12月29日 15:54bugbounty技巧聚合20210811
漏洞报告 HackerOne #1256371 PII data Leakage through hackerone reports #1145563 Tab nabbing in Hackerone inbox. Basecamp #1288898 Password reset link not expiring after changing pa...
2022年4月1日 18:36CVE-2019-6703: Total Donations Plugin for WordPress < 2.0.6 - Arbitrary Options Update
漏洞标题 CVE-2019-6703: Total Donations Plugin for WordPress < 2.0.6 - Arbitrary Options Update 漏洞描述 Incorrect access control in migla_ajax_functions.php in the Calmar Webme...
2019年11月7日 02:37CVE-2021-35395: RealTek Jungle SDK – Arbitrary Command Injection
漏洞标题 CVE-2021-35395: RealTek Jungle SDK - Arbitrary Command Injection 漏洞描述 There is a command injection vulnerability on the "formWsc" page of the management inte...
2021年1月13日 00:33CVE-2007-3010: Alcatel-Lucent OmniPCX – Remote Command Execution
漏洞标题 CVE-2007-3010: Alcatel-Lucent OmniPCX - Remote Command Execution 漏洞描述 The OmniPCX web interface has a script "masterCGI" with a remote command execution vuln...
2007年8月23日 23:10Nginx配置https原理及实现过程详解_nginx
这篇文章主要介绍了Nginx配置https原理及实现过程详解,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友可以参考下 使用linux实用工具certbot来生成htt...
2023年4月27日 21:10CVE-2024-0986: Issabel Authenticated – Remote Code Execution
漏洞标题 CVE-2024-0986: Issabel Authenticated - Remote Code Execution 漏洞描述 A vulnerability was found in Issabel PBX 4.0.0. It has been rated as critical. This issue affects som...
2024年9月22日 18:02CVE-2024-32739: CyberPower < v2.8.3 - SQL Injection
漏洞标题 CVE-2024-32739: CyberPower < v2.8.3 - SQL Injection 漏洞描述 A sql injection vulnerability exists in CyberPower PowerPanel Enterprise prior to v2.8.3. PoC代码
2024年7月28日 17:19
2026年9月23日 11:46
2026年9月22日 11:45
2026年9月21日 11:45
2026年9月20日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

