
最新发布第619页
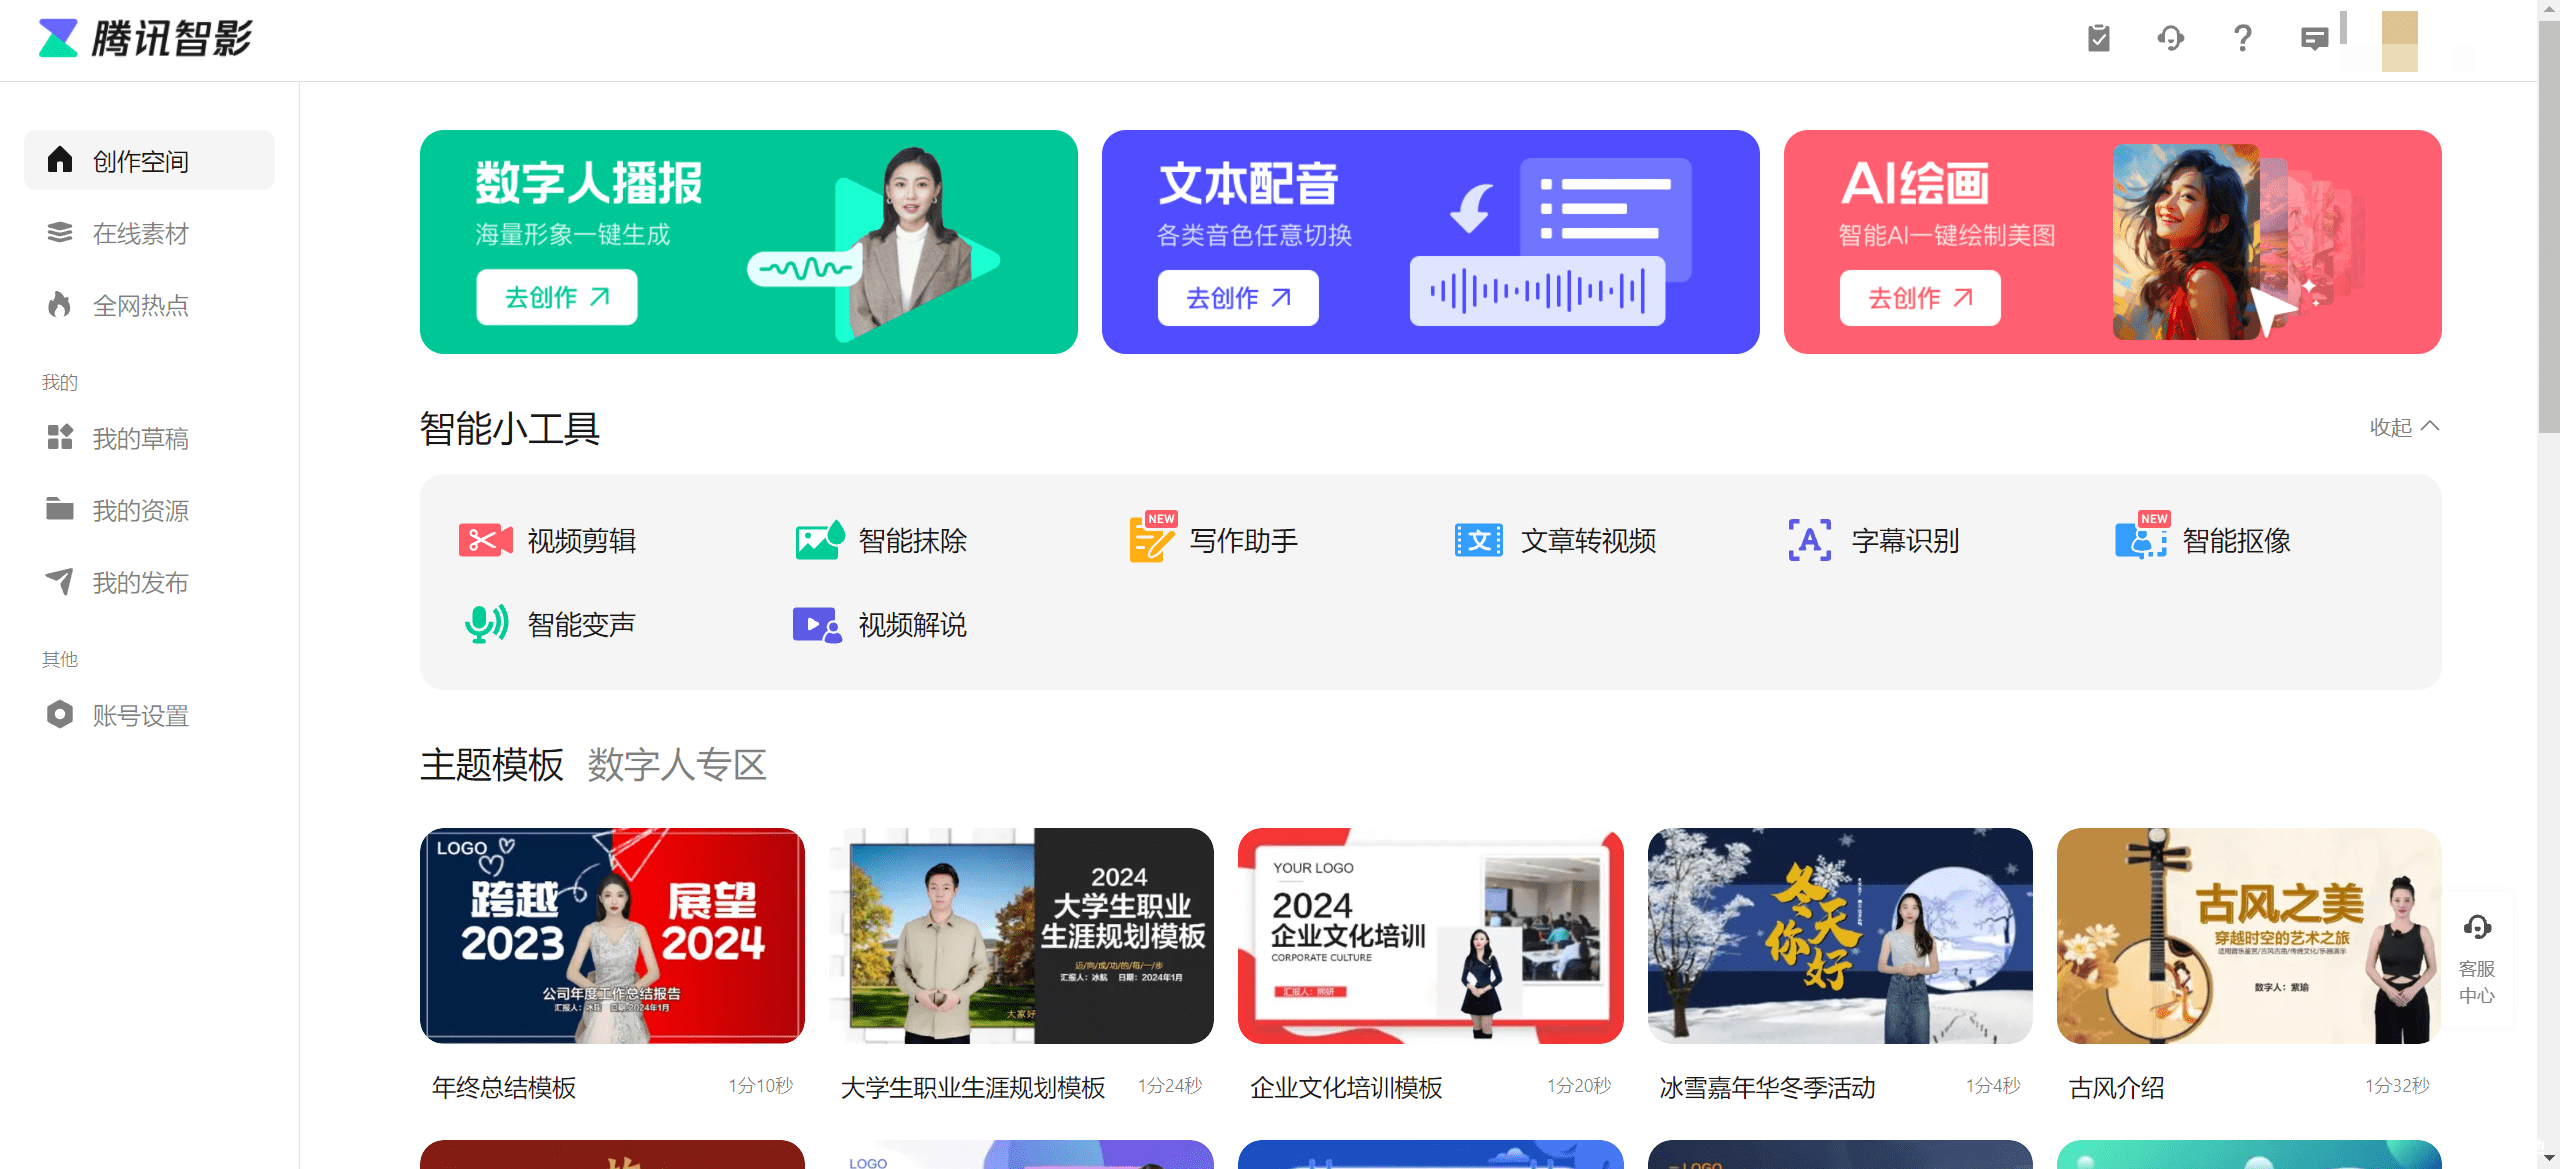
2024最新查看腾讯视频会员资源(无需看广告)
注:注意版权,需要看蓝光画质还是自己开会员吧 教程 首先打开网址:腾讯智影 http://zenvideo.mp.v.qq.com/ 注册账号,这里选择登录就可以 合作品类选自媒体,无成本无审核周期 打开在线素材库...

 2024年1月12日 15:37

CVE-2023-27179: GDidees CMS v3.9.1 – Arbitrary File Download
漏洞标题 CVE-2023-27179: GDidees CMS v3.9.1 - Arbitrary File Download 漏洞描述 GDidees CMS v3.9.1 and lower was discovered to contain an arbitrary file download vulenrability via t...
 2023年8月24日 20:23
Adobe Commerce CVE-2024-34102 XML外部实体注入漏洞
漏洞标题 Adobe Commerce CVE-2024-34102 XML外部实体注入漏洞 漏洞描述 Adobe Commerce 存在XML外部实体注入漏洞,此漏洞是由于程序未充分验证用户输入estimate-shipping-methods的数据所导致...
2024年7月13日 03:05CVE-2021-24212: WooCommerce Help Scout – Arbitrary File Upload
漏洞标题 CVE-2021-24212: WooCommerce Help Scout - Arbitrary File Upload 漏洞描述 WooCommerce Help Scout plugin before version 2.9.1 contains an unrestricted file upload vulnerabili...
2021年4月17日 10:46CVE-2022-1904: WordPress Easy Pricing Tables <3.2.1 - Cross-Site Scripting
漏洞标题 CVE-2022-1904: WordPress Easy Pricing Tables <3.2.1 - Cross-Site Scripting 漏洞描述 WordPress Easy Pricing Tables plugin before 3.2.1 contains a reflected cross-site sc...
2022年12月13日 20:48CVE-2022-23808: phpMyAdmin < 5.1.2 - Cross-Site Scripting
漏洞标题 CVE-2022-23808: phpMyAdmin < 5.1.2 - Cross-Site Scripting 漏洞描述 An issue was discovered in phpMyAdmin 5.1 before 5.1.2 that could allow an attacker to inject malicio...
2022年11月26日 22:50CVE-2019-5129: YouPHPTube Encoder 2.3 – Command Injection
漏洞标题 CVE-2019-5129: YouPHPTube Encoder 2.3 - Command Injection 漏洞描述 Exploitable unauthenticated command injections exist in YouPHPTube Encoder 2.3 a plugin for providing en...
2019年8月15日 14:58CVE-2021-22911: Rocket.Chat <=3.13 - NoSQL Injection
漏洞标题 CVE-2021-22911: Rocket.Chat <=3.13 - NoSQL Injection 漏洞描述 Rocket.Chat 3.11, 3.12 and 3.13 contains a NoSQL injection vulnerability which allows unauthenticated acce...
2021年5月16日 14:40CVE-2020-1943: Apache OFBiz <=16.11.07 - Cross-Site Scripting
漏洞标题 CVE-2020-1943: Apache OFBiz <=16.11.07 - Cross-Site Scripting 漏洞描述 Apache OFBiz 16.11.01 to 16.11.07 is vulnerable to cross-site scripting because data sent with co...
2020年3月19日 00:59CVE-2024-7029: AVTECH IP Camera – Command Injection
漏洞标题 CVE-2024-7029: AVTECH IP Camera - Command Injection 漏洞描述 The endpoint `/cgi-bin/supervisor/Factory.cgi` is vulnerable to command injection via the `action` parameter, ...
2024年7月11日 16:06CVE-2023-30150: PrestaShop leocustomajax 1.0 & 1.0.0 – SQL Injection
漏洞标题 CVE-2023-30150: PrestaShop leocustomajax 1.0 & 1.0.0 - SQL Injection 漏洞描述 PrestaShop leocustomajax 1.0 and 1.0.0 are vulnerable to SQL Injection via modules/leocus...
2023年10月10日 03:36CVE-2023-44352: Adobe Coldfusion – Cross-Site Scripting
漏洞标题 CVE-2023-44352: Adobe Coldfusion - Cross-Site Scripting 漏洞描述 Adobe ColdFusion versions 2023.5 (and earlier) and 2021.11 (and earlier) are affected by a reflected Cross...
2023年3月27日 00:31CVE-2020-14864: Oracle Fusion – Directory Traversal/Local File Inclusion
漏洞标题 CVE-2020-14864: Oracle Fusion - Directory Traversal/Local File Inclusion 漏洞描述 Oracle Business Intelligence Enterprise Edition 5.5.0.0.0, 12.2.1.3.0, and 12.2.1.4.0 are...
2020年7月26日 12:00CVE-2010-1653: Joomla! Component Graphics 1.0.6 – Local File Inclusion
漏洞标题 CVE-2010-1653: Joomla! Component Graphics 1.0.6 - Local File Inclusion 漏洞描述 A directory traversal vulnerability in graphics.php in the Graphics (com_graphics) componen...
2010年7月12日 20:52
2023最新金山wps恶意文件执行复现,附poc
0x01 漏洞描述 WPS Office for windows的内置浏览界存在逻辑漏洞,攻击者可以利用该漏洞专门构造出恶意文档,受害者打开该文档并点击文档中的URL链接或包舍了超级链接的图片时,...
2023年8月17日 18:05CVE-2022-4140: WordPress Welcart e-Commerce <2.8.5 - Arbitrary File Access
漏洞标题 CVE-2022-4140: WordPress Welcart e-Commerce <2.8.5 - Arbitrary File Access 漏洞描述 WordPress Welcart e-Commerce plugin before 2.8.5 is susceptible to arbitrary file ac...
2022年1月23日 09:20
2026年11月9日 11:45
2026年11月8日 11:45
2026年11月7日 11:45
2026年11月6日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

