
最新发布第61页

CVE-2023-4111: PHPJabbers Bus Reservation System 1.1 – Cross-Site Scripting
漏洞标题 CVE-2023-4111: PHPJabbers Bus Reservation System 1.1 - Cross-Site Scripting 漏洞描述 A vulnerability was found in PHP Jabbers Bus Reservation System 1.1 and classified as ...
 2023年1月31日 10:26
CVE-2010-1658: Joomla! Component NoticeBoard 1.3 – Local File Inclusion
漏洞标题 CVE-2010-1658: Joomla! Component NoticeBoard 1.3 - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the Code-Garage NoticeBoard (com_noticeboard) compo...
2010年7月2日 07:33CVE-2022-1392: WordPress Videos sync PDF <=1.7.4 - Local File Inclusion
漏洞标题 CVE-2022-1392: WordPress Videos sync PDF <=1.7.4 - Local File Inclusion 漏洞描述 WordPress Videos sync PDF 1.7.4 and prior does not validate the p parameter before usin...
2022年3月2日 07:14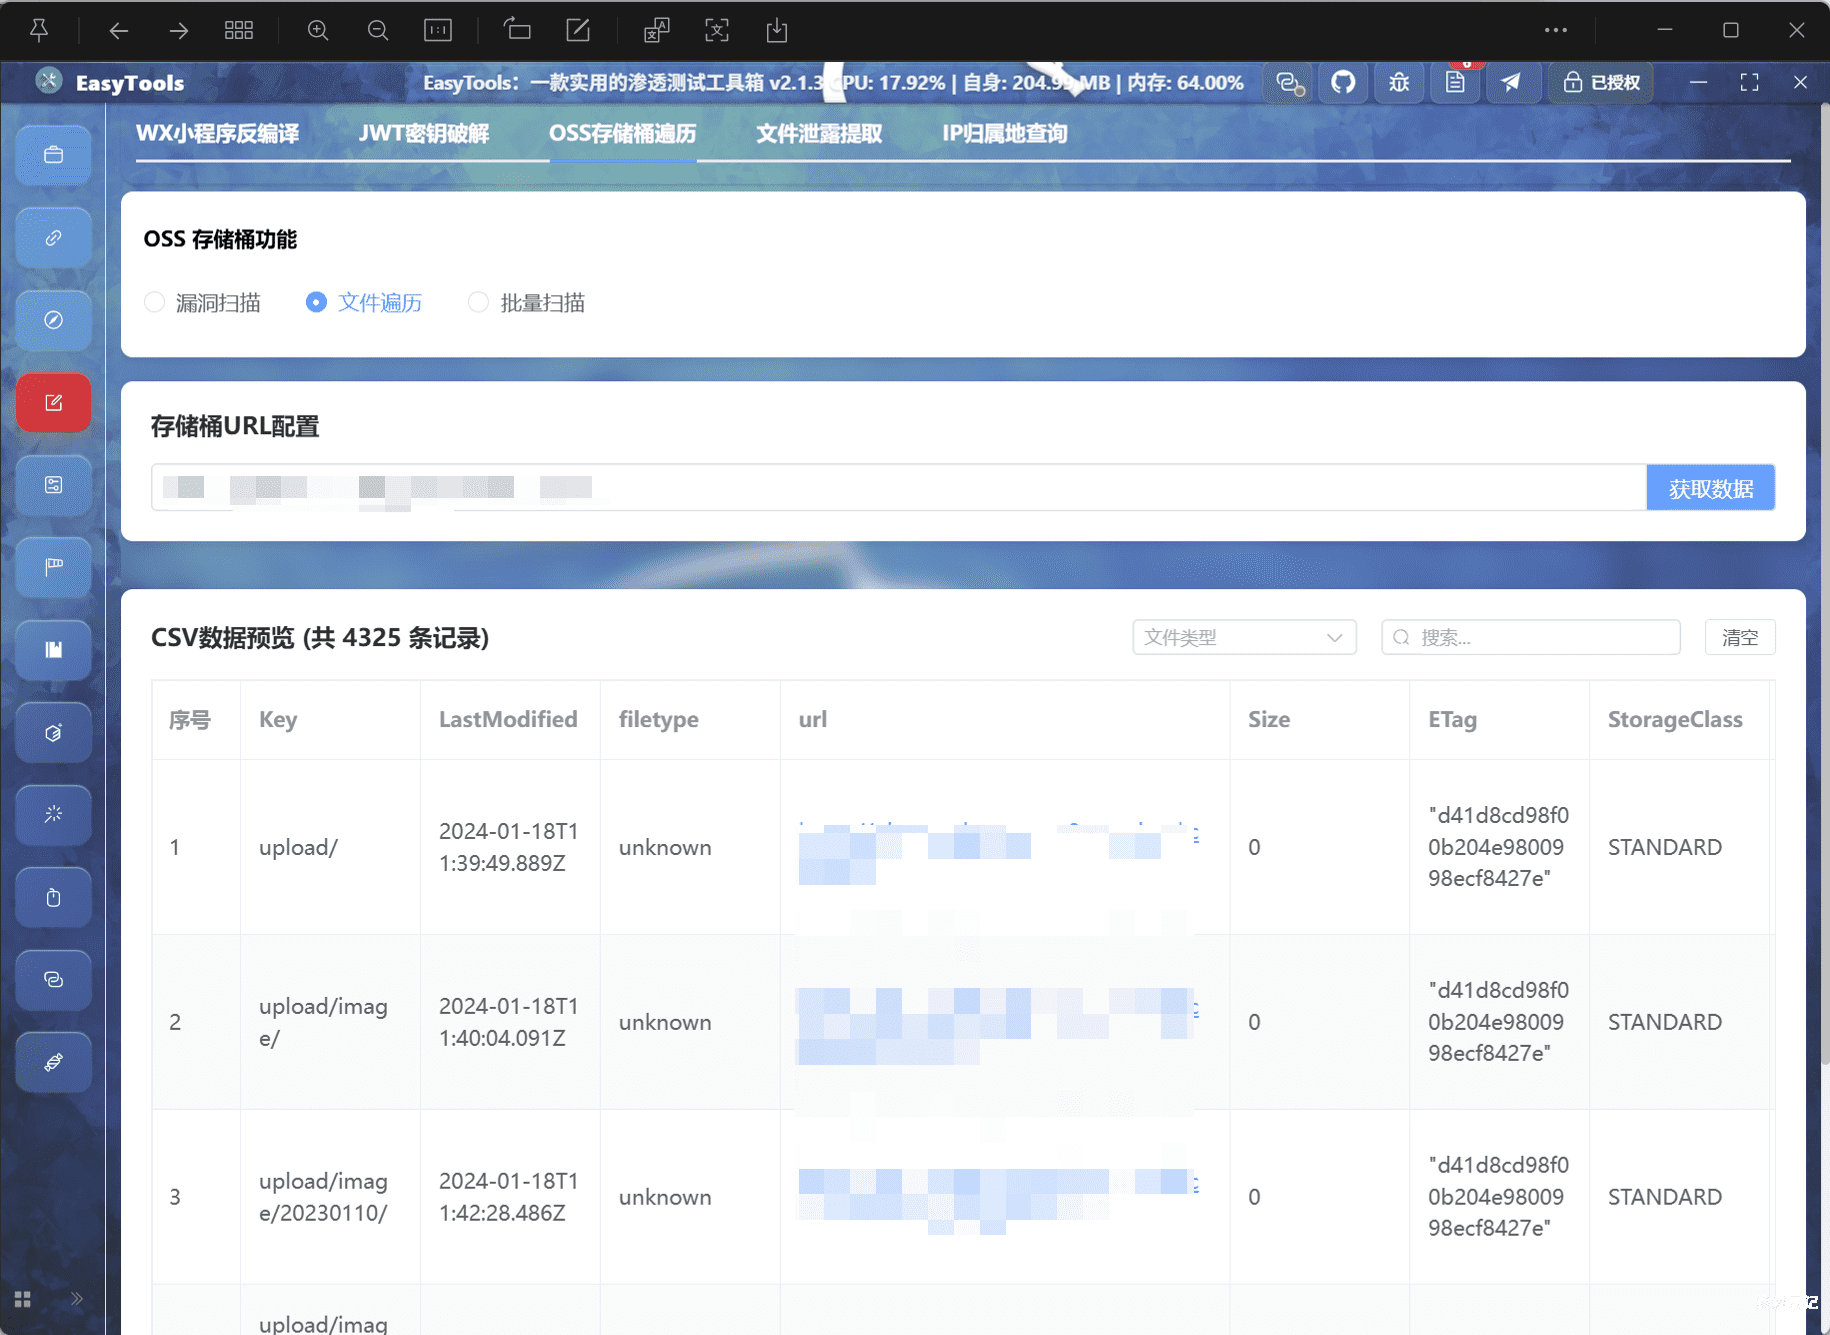
EasyTools渗透测试工具箱V2.1.4更新(优化资源桶遍历功能,支持kkfileview预览,新增空间测绘、AI版域名收集功能等诸多功能)
前言 各位看官老爷们,很久没有更新了,新的一年了在此汇报一下更新进度: 优化资源桶遍历功能,支持kkfileview预览; 重构渗透测试模块,调用httpx提高性能与准确度; 新增AI底座,方便后续功能...

 2026年3月1日 15:46
CVE-2017-17736: Kentico – Installer Privilege Escalation
漏洞标题 CVE-2017-17736: Kentico - Installer Privilege Escalation 漏洞描述 Kentico 9.0 before 9.0.51 and 10.0 before 10.0.48 are susceptible to a privilege escalation attack. An at...
2017年3月8日 09:52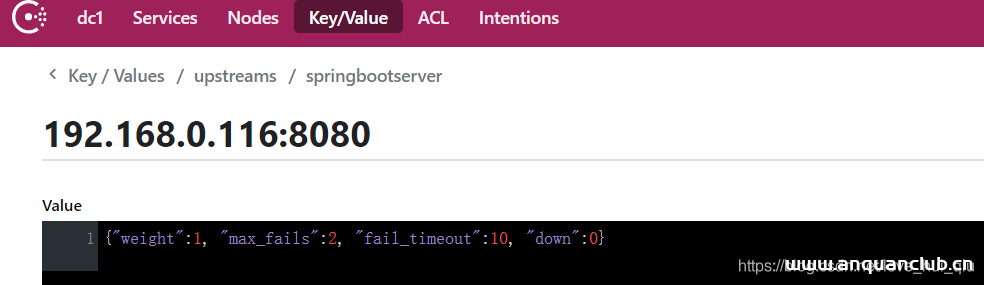
Nginx + consul + upsync 完成动态负载均衡的方法详解_nginx
这篇文章主要介绍了Nginx + consul + upsync 完成动态负载均衡,需要的朋友可以参考下 目录前置知识DNS域名解析过程 外网映射 nginx 核心知识什么是nginx应用场景名词解释Nginx + cons...
2023年3月6日 21:03CVE-2023-30777: Advanced Custom Fields < 6.1.6 - Cross-Site Scripting
漏洞标题 CVE-2023-30777: Advanced Custom Fields < 6.1.6 - Cross-Site Scripting 漏洞描述 Advanced Custom Fields beofre 6.1.6 is susceptible to cross-site scripting via the post_s...
2023年4月11日 21:42Confluence viewdefaultdecorator.action-任意文件读取(CVE-2015-8399)
漏洞标题 Confluence viewdefaultdecorator.action-任意文件读取(CVE-2015-8399) 漏洞描述 【漏洞对象】Atlassian Confluence 【涉及版本】<5.8.17 【漏洞描述】该漏洞源于spaces/viewdefaul...
2015年1月28日 06:35
bugbounty技巧聚合20211112
漏洞报告 【Judge.me 】The response shows the nginx version http://hackerone.com/reports/1395068 【Slack 250刀】Cross-site leak allows attacker to de-anonymize members of his team f...
2022年3月10日 23:39CVE-2022-29013: Razer Sila Gaming Router – Remote Code Execution
漏洞标题 CVE-2022-29013: Razer Sila Gaming Router - Remote Code Execution 漏洞描述 A command injection in the command parameter of Razer Sila Gaming Router v2.0.441_api-2.0.418 all...
2022年8月8日 03:33CVE-2025-2709: Yonyou UFIDA ERP-NC V5.0 – Cross-Site Scripting
漏洞标题 CVE-2025-2709: Yonyou UFIDA ERP-NC V5.0 - Cross-Site Scripting 漏洞描述 Yonyou UFIDA ERP-NC V5.0 is vulnerable to reflected cross-site scripting (XSS) via the key and redi...
2025年9月10日 16:47CVE-2025-34026: Versa Concerto Actuator Endpoint – Authentication Bypass
漏洞标题 CVE-2025-34026: Versa Concerto Actuator Endpoint - Authentication Bypass 漏洞描述 An authentication bypass vulnerability affected the Spring Boot Actuator endpoints in Ver...
2025年3月5日 13:40CVE-2019-10647: ZZZCMS ZZZPHP 1.6.3 – Remote PHP Code Execution (RCE)
漏洞标题 CVE-2019-10647: ZZZCMS ZZZPHP 1.6.3 – Remote PHP Code Execution (RCE) 漏洞描述 ZZZCMS zzzphp v1.6.3 contains a remote code execution caused by lack of restrictions in inc...
2019年5月15日 15:19CVE-2021-24212: WooCommerce Help Scout – Arbitrary File Upload
漏洞标题 CVE-2021-24212: WooCommerce Help Scout - Arbitrary File Upload 漏洞描述 WooCommerce Help Scout plugin before version 2.9.1 contains an unrestricted file upload vulnerabili...
2021年6月7日 10:48CVE-2024-1210: LearnDash LMS < 4.10.2 - Sensitive Information Exposure
漏洞标题 CVE-2024-1210: LearnDash LMS < 4.10.2 - Sensitive Information Exposure 漏洞描述 The LearnDash LMS plugin for WordPress is vulnerable to Sensitive Information Exposure i...
2024年10月17日 18:31CVE-2019-20224: Pandora FMS 7.0NG – Remote Command Injection
漏洞标题 CVE-2019-20224: Pandora FMS 7.0NG - Remote Command Injection 漏洞描述 Pandora FMS 7.0NG allows remote authenticated users to execute arbitrary OS commands via shell metach...
2019年8月14日 05:41
2026年10月14日 11:45
2026年10月13日 11:45
2026年10月12日 11:45
2026年10月11日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

