
最新发布第61页

CVE-2022-48197: Yahoo User Interface library (YUI2) TreeView v2.8.2 – Cross-Site Scripting
漏洞标题 CVE-2022-48197: Yahoo User Interface library (YUI2) TreeView v2.8.2 - Cross-Site Scripting 漏洞描述 Reflected cross-site scripting (XSS) exists in the TreeView of YUI2 thr...
 2022年5月14日 17:44
CVE-2022-0735: GitLab CE/EE – Information Disclosure
漏洞标题 CVE-2022-0735: GitLab CE/EE - Information Disclosure 漏洞描述 GitLab CE/EE is susceptible to information disclosure. An attacker can access runner registration tokens usin...
2022年2月18日 09:10
docker 容器自定义 hosts 网络访问操作_docker
这篇文章主要介绍了docker 容器自定义 hosts 网络访问操作,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 在 docker-compose.yml 中增加 extra_hosts 关键字就可以将数据写...
2022年8月6日 20:34CVE-2015-4455: WordPress Plugin Aviary Image Editor Addon For Gravity Forms 3.0 Beta – Arbitrary File Upload
漏洞标题 CVE-2015-4455: WordPress Plugin Aviary Image Editor Addon For Gravity Forms 3.0 Beta - Arbitrary File Upload 漏洞描述 Unrestricted file upload vulnerability in includes/up...
2015年7月16日 10:13Apache Druid 任意文件读取(CVE-2021-36749)
漏洞标题 Apache Druid 任意文件读取(CVE-2021-36749) 漏洞描述 在 Druid 摄取系统中,InputSource 用于从某个数据源读取数据。HTTP InputSource 允许经过身份验证的用户以 Druid服务器进程的权...
2021年4月24日 06:30
研究人员在Google Play商店发现新的银行木马
移动威胁检测与预防公司ThreatFabric新近发现了一种新的Android银行木马Xenomorph,该木马通过官方Google Play商店分发,目前安装量已超过50000次。该银行木马针对56家欧洲银行,目的是从其客户...
2022年3月10日 23:40CVE-2018-17153: Western Digital MyCloud NAS – Authentication Bypass
漏洞标题 CVE-2018-17153: Western Digital MyCloud NAS - Authentication Bypass 漏洞描述 It was discovered that the Western Digital My Cloud device before 2.30.196 is affected by an a...
2018年9月10日 14:25CVE-2025-26319: FlowiseAI Flowise <= 2.2.6 - Arbitrary File Upload
漏洞标题 CVE-2025-26319: FlowiseAI Flowise <= 2.2.6 - Arbitrary File Upload 漏洞描述 FlowiseAI Flowise version 2.2.6 and below contains an arbitrary file upload vulnerability in...
2025年6月22日 22:58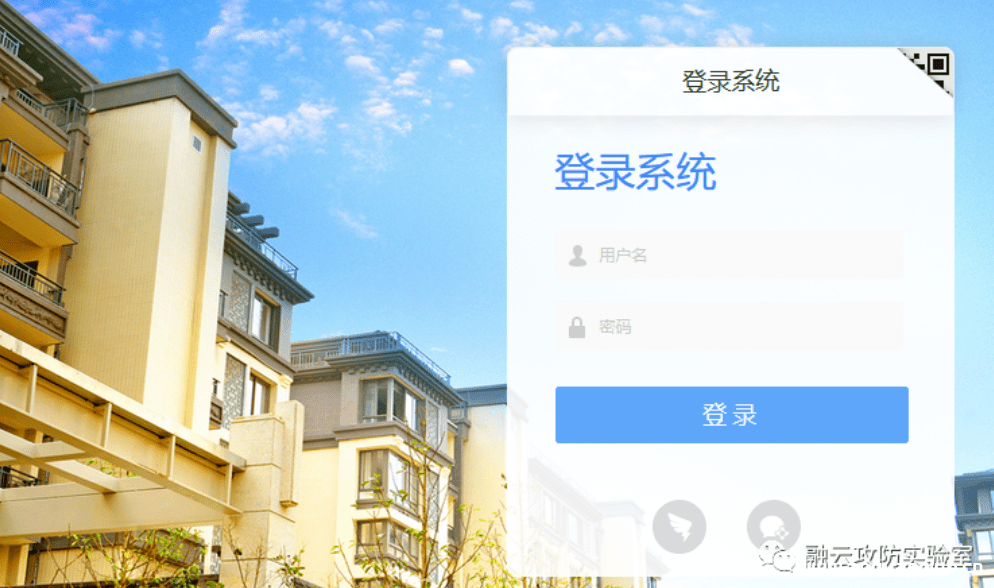
蓝凌OA custom.jsp 任意文件读取
本文转载于公众号:融云攻防实验室,原文地址: 蓝凌OA custom.jsp 任意文件读取 蓝凌是国内数字化办公专业服务商,阿里钉钉唯一投资的OA厂商,阿里云知识管理与协同领域首家战略合作伙伴。蓝凌OA...
2026年2月13日 12:53CVE-2019-15889: WordPress Download Manager <2.9.94 - Cross-Site Scripting
漏洞标题 CVE-2019-15889: WordPress Download Manager <2.9.94 - Cross-Site Scripting 漏洞描述 WordPress Download Manager plugin before 2.9.94 contains a cross-site scripting vulne...
2019年1月24日 17:56CVE-2010-2857: Joomla! Component Music Manager – Local File Inclusion
漏洞标题 CVE-2010-2857: Joomla! Component Music Manager - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the Music Manager component for Joomla! allows remote...
2010年12月12日 17:50
Linux 进程通信之FIFO的实现_Linux
这篇文章主要介绍了Linux 进程通信之FIFO的实现,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编来一起学习学习吧 FIFO通信(first i...
2024年5月11日 21:02CVE-2020-7961: Liferay Portal RCE 反序列化命令执行漏洞
漏洞标题 CVE-2020-7961: Liferay Portal RCE 反序列化命令执行漏洞 漏洞描述 Liferay Portal CE是一款用来快速构建网站的开源系统。其7.2.0 GA1及以前的版本API接口中存在一处反序列化漏洞,利...
2020年10月15日 08:05CVE-2015-4694: WordPress Zip Attachments <= 1.1.4 - Arbitrary File Retrieval
漏洞标题 CVE-2015-4694: WordPress Zip Attachments <= 1.1.4 - Arbitrary File Retrieval 漏洞描述 WordPress zip-attachments plugin allows arbitrary file retrieval as it does not ch...
2015年5月20日 17:38CVE-2023-0948: WordPress Japanized for WooCommerce <2.5.8 - Cross-Site Scripting
漏洞标题 CVE-2023-0948: WordPress Japanized for WooCommerce <2.5.8 - Cross-Site Scripting 漏洞描述 WordPress Japanized for WooCommerce plugin before 2.5.8 is susceptible to cros...
2023年7月22日 12:18CVE-2024-21645: pyload – Log Injection
漏洞标题 CVE-2024-21645: pyload - Log Injection 漏洞描述 A log injection vulnerability was identified in pyload. This vulnerability allows any unauthenticated actor to inject arbit...
2024年7月22日 04:12
2026年9月17日 18:46
2026年9月17日 11:45
2026年9月16日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月17日 18:19
2026年8月16日 20:18
2026年8月11日 13:39
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

