
最新发布第621页
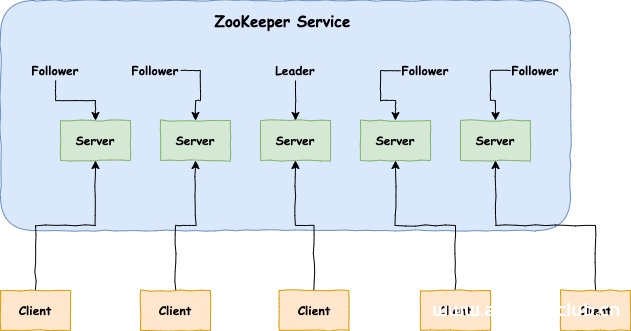
史上最便捷搭建Zookeeper服务器的方法(推荐)_zabbix
由于 ZooKeeper 便捷的使用方式、卓越的性能和良好的稳定性,被广泛地应用于诸如 Hadoop、HBase、Kafka 和 Dubbo 等大型分布式系统中。这篇文章主要介绍了史上最便捷搭建Zookeeper服务器的方法,...
 2023年12月4日 20:20

CVE-2022-39048: ServiceNow – Cross-site Scripting
漏洞标题 CVE-2022-39048: ServiceNow - Cross-site Scripting 漏洞描述 A XSS vulnerability was identified in the ServiceNow UI page assessment_redirect. To exploit this vulnerability,...
2022年8月4日 07:49CVE-2025-47423: Personal Weather Station Dashboard 12 – Directory Traversal
漏洞标题 CVE-2025-47423: Personal Weather Station Dashboard 12 - Directory Traversal 漏洞描述 Personal Weather Station Dashboard 12_lts allows unauthenticated remote attackers to r...
2025年6月10日 23:20
Linux sftp命令用法_Linux
这篇文章主要介绍了Linux sftp命令用法,小编觉得挺不错的,现在分享给大家,也给大家做个参考。一起跟随小编过来看看吧 SFTP的概念 sftp是Secure File Transfer Protocol的缩写,安全文件...
2022年6月15日 08:45CVE-2023-43654: PyTorch TorchServe SSRF
漏洞标题 CVE-2023-43654: PyTorch TorchServe SSRF 漏洞描述 TorchServe is a tool for serving and scaling PyTorch models in production. TorchServe default configuration lacks proper i...
2023年6月2日 20:12CVE-2025-5961: WordPress WPvivid Backup & Migration Plugin <= 0.9.116 - Authenticated Arbitrary File Upload
漏洞标题 CVE-2025-5961: WordPress WPvivid Backup & Migration Plugin <= 0.9.116 - Authenticated Arbitrary File Upload 漏洞描述 The Migration, Backup, Staging – WPvivid Backu...
2025年5月6日 10:27CVE-2021-44077: Zoho ManageEngine ServiceDesk Plus – Remote Code Execution
漏洞标题 CVE-2021-44077: Zoho ManageEngine ServiceDesk Plus - Remote Code Execution 漏洞描述 Zoho ManageEngine ServiceDesk Plus before 11306, ServiceDesk Plus MSP before 10530, and...
2021年5月28日 07:54
$bugbounty技巧聚合20210830$
漏洞报告 Microsoft Azure 【40000刀】ChaosDB: Unauthorized Privileged Access to Microsoft Azure Cosmos DB ChaosDB: How we hacked thousands of Azure customers’ databases | Wiz Blog ...
2022年3月10日 23:34CVE-2021-24762: WordPress Perfect Survey <1.5.2 - SQL Injection
漏洞标题 CVE-2021-24762: WordPress Perfect Survey <1.5.2 - SQL Injection 漏洞描述 Perfect Survey WordPress plugin before 1.5.2 does not validate and escape the question_id GET p...
2021年2月14日 20:52CVE-2025-46822: Java-springboot-codebase 1.1 – Arbitrary File Read
漏洞标题 CVE-2025-46822: Java-springboot-codebase 1.1 - Arbitrary File Read 漏洞描述 OsamaTaher/Java-springboot-codebase is a collection of Java and Spring Boot code snippets, appl...
2025年6月8日 01:17CVE-2023-41266: Qlik Sense Enterprise – Path Traversal
漏洞标题 CVE-2023-41266: Qlik Sense Enterprise - Path Traversal 漏洞描述 A path traversal vulnerability found in Qlik Sense Enterprise for Windows for versions May 2023 Patch 3 and...
2023年1月17日 00:46CVE-2018-18608: DedeCMS 5.7 SP2 – Cross-Site Scripting
漏洞标题 CVE-2018-18608: DedeCMS 5.7 SP2 - Cross-Site Scripting 漏洞描述 DedeCMS 5.7 SP2 is vulnerable to cross-site scripting via the function named GetPageList defined in the inc...
2018年3月25日 09:32CVE-2023-43662: ShokoServer System – Local File Inclusion (LFI)
漏洞标题 CVE-2023-43662: ShokoServer System - Local File Inclusion (LFI) 漏洞描述 ShokoServer is a media server which specializes in organizing anime. In affected versions the `/ap...
2023年3月2日 03:52CVE-2023-39121: Emlog 2.1.9 – SQL Injection
漏洞标题 CVE-2023-39121: Emlog 2.1.9 - SQL Injection 漏洞描述 emlog v2.1.9 contains a SQL injection caused by unsanitized input in the data backup/restore functionality, allowing a...
2023年9月4日 15:29CVE-2020-12478: TeamPass 2.1.27.36 – Improper Authentication
漏洞标题 CVE-2020-12478: TeamPass 2.1.27.36 - Improper Authentication 漏洞描述 TeamPass 2.1.27.36 is susceptible to improper authentication. An attacker can retrieve files from the...
2020年4月12日 16:08CVE-2020-36708: WordPress Epsilon Framework Themes <=2.4.8 - Remote Code Execution
漏洞标题 CVE-2020-36708: WordPress Epsilon Framework Themes <=2.4.8 - Remote Code Execution 漏洞描述 WordPress themes including Shapely <= 1.2.7, NewsMag <= 2.4.1, Activel...
2020年5月3日 21:52
2026年9月21日 11:45
2026年9月20日 11:45
2026年9月19日 11:45
2026年9月18日 11:46
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

