
最新发布第621页

CVE-2021-24347: WordPress SP Project & Document Manager <4.22 - Authenticated Shell Upload
漏洞标题 CVE-2021-24347: WordPress SP Project & Document Manager <4.22 - Authenticated Shell Upload 漏洞描述 WordPress SP Project & Document Manager plugin before 4.22 i...
 2021年7月19日 03:31
CVE-2022-1007: WordPress Advanced Booking Calendar <1.7.1 - Cross-Site Scripting
漏洞标题 CVE-2022-1007: WordPress Advanced Booking Calendar <1.7.1 - Cross-Site Scripting 漏洞描述 WordPress Advanced Booking Calendar plugin before 1.7.1 contains a cross-site ...
2022年12月18日 11:37CVE-2023-37679: NextGen Mirth Connect – Remote Code Execution
漏洞标题 CVE-2023-37679: NextGen Mirth Connect - Remote Code Execution 漏洞描述 Mirth Connect, by NextGen HealthCare, is an open source data integration platform widely used by hea...
2023年3月19日 18:47CVE-2023-43187: NodeBB XML-RPC Request xmlrpc.php – XML Injection
漏洞标题 CVE-2023-43187: NodeBB XML-RPC Request xmlrpc.php - XML Injection 漏洞描述 A remote code execution (RCE) vulnerability in the xmlrpc.php endpoint of NodeBB Inc NodeBB foru...
2023年8月14日 17:36CVE-2017-18492: Contact Form to DB by BestWebSoft < 1.5.7 - Cross-Site Scripting
漏洞标题 CVE-2017-18492: Contact Form to DB by BestWebSoft < 1.5.7 - Cross-Site Scripting 漏洞描述 The contact-form-to-db plugin before 1.5.7 for WordPress has multiple XSS issu...
2017年2月11日 20:01
记一次修改前端时间导致的未授权
发现之前 在前段时间看到了好像是一个支付宝的漏洞那个人修改了电脑的时间然后可以提前秒杀抢购商品,于是这个洞在弟弟我的心里深深的记住了,于是就有了后面的发现 发现过程 在刚刚加入火线某...
2022年3月10日 23:29CVE-2022-1952: WordPress eaSYNC Booking <1.1.16 - Arbitrary File Upload
漏洞标题 CVE-2022-1952: WordPress eaSYNC Booking <1.1.16 - Arbitrary File Upload 漏洞描述 WordPress eaSync Booking plugin bundle for hotel, restaurant and car rental before 1.1....
2022年6月16日 00:16CVE-2020-15568: TerraMaster TOS v4.1.24 RCE
漏洞标题 CVE-2020-15568: TerraMaster TOS v4.1.24 RCE 漏洞描述 TerraMaster TOS before 4.1.29 has Invalid Parameter Checking that leads to code injection as root. This is a dynamic c...
2020年9月3日 15:52CVE-2020-10189: ManageEngine Desktop Central Java Deserialization
漏洞标题 CVE-2020-10189: ManageEngine Desktop Central Java Deserialization 漏洞描述 Zoho ManageEngine Desktop Central before 10.0.474 is vulnerable to a deserialization of untruste...
2020年7月12日 06:00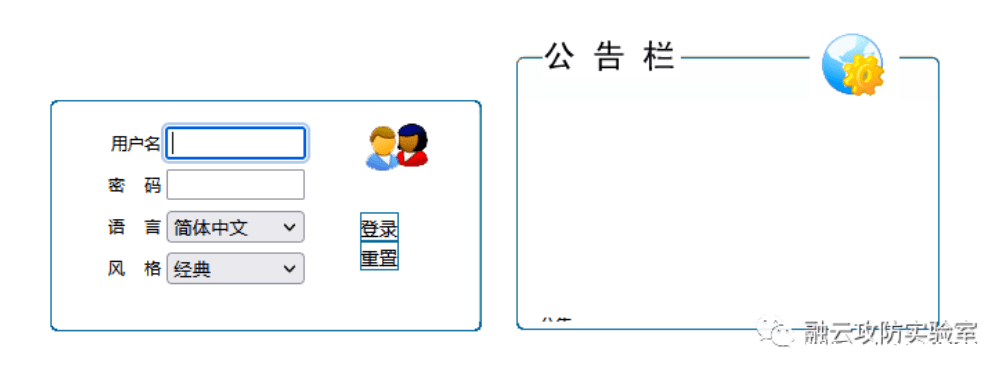
科迈 RAS系统 Cookie验证越权漏洞
本文转载于公众号:融云攻防实验室,原文地址: 漏洞复现 科迈 RAS系统 Cookie验证越权漏洞 科迈 RAS(Remote Application Solution)是中国首创远程快速应用接入方案,它结合TS终端技术,在提供...
2026年2月13日 12:53CVE-2023-37645: EyouCms v1.6.3 – Information Disclosure
漏洞标题 CVE-2023-37645: EyouCms v1.6.3 - Information Disclosure 漏洞描述 EyouCms v1.6.3 was discovered to contain an information disclosure vulnerability via the component /custom...
2023年6月16日 22:07CVE-2021-44139: Alibaba Sentinel – Server-side request forgery (SSRF)
漏洞标题 CVE-2021-44139: Alibaba Sentinel - Server-side request forgery (SSRF) 漏洞描述 There is a Pre-Auth SSRF vulnerability in Alibaba Sentinel version 1.8.2, which allows remot...
2021年10月20日 17:08CVE-2025-47423: Personal Weather Station Dashboard 12 – Directory Traversal
漏洞标题 CVE-2025-47423: Personal Weather Station Dashboard 12 - Directory Traversal 漏洞描述 Personal Weather Station Dashboard 12_lts allows unauthenticated remote attackers to r...
2025年5月2日 00:31CVE-2017-9506: Atlassian Jira IconURIServlet – Cross-Site Scripting/Server-Side Request Forgery
漏洞标题 CVE-2017-9506: Atlassian Jira IconURIServlet - Cross-Site Scripting/Server-Side Request Forgery 漏洞描述 The Atlassian Jira IconUriServlet of the OAuth Plugin from version...
2017年6月20日 13:50CVE-2019-10758: mongo-express Remote Code Execution
漏洞标题 CVE-2019-10758: mongo-express Remote Code Execution 漏洞描述 mongo-express before 0.54.0 is vulnerable to remote code execution via endpoints that uses the `toBSON` method...
2019年9月24日 07:15CVE-2024-21645: pyload – Log Injection
漏洞标题 CVE-2024-21645: pyload - Log Injection 漏洞描述 A log injection vulnerability was identified in pyload. This vulnerability allows any unauthenticated actor to inject arbit...
2024年9月13日 04:18
2026年11月9日 11:45
2026年11月8日 11:45
2026年11月7日 11:45
2026年11月6日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

