
最新发布第622页

CVE-2024-5082: Nexus Repository 2 – Remote Code Execution
漏洞标题 CVE-2024-5082: Nexus Repository 2 - Remote Code Execution 漏洞描述 A Remote Code Execution vulnerability has been discovered in Sonatype Nexus Repository 2.This issue affe...
 2024年3月15日 01:20
CVE-2023-35885: Cloudpanel 2 < 2.3.1 - Remote Code Execution
漏洞标题 CVE-2023-35885: Cloudpanel 2 < 2.3.1 - Remote Code Execution 漏洞描述 CloudPanel 2 before 2.3.1 has insecure file-manager cookie authentication. PoC代码
2023年3月1日 20:58CVE-2024-4956: Sonatype Nexus Repository Manager 3 – Local File Inclusion
漏洞标题 CVE-2024-4956: Sonatype Nexus Repository Manager 3 - Local File Inclusion 漏洞描述 Path Traversal in Sonatype Nexus Repository 3 allows an unauthenticated attacker to read...
2024年5月18日 01:37CVE-2023-0777: modoboa 2.0.4 – Admin TakeOver
漏洞标题 CVE-2023-0777: modoboa 2.0.4 - Admin TakeOver 漏洞描述 Authentication Bypass by Primary Weakness in GitHub repository modoboa/modoboa prior to 2.0.4. PoC代码
2023年11月30日 02:34CVE-2018-3810: Oturia WordPress Smart Google Code Inserter <3.5 - Authentication Bypass
漏洞标题 CVE-2018-3810: Oturia WordPress Smart Google Code Inserter <3.5 - Authentication Bypass 漏洞描述 Oturia Smart Google Code Inserter plugin before 3.5 for WordPress allow...
2018年4月29日 17:11CVE-2022-35914: GLPI <=10.0.2 - Remote Command Execution
漏洞标题 CVE-2022-35914: GLPI <=10.0.2 - Remote Command Execution 漏洞描述 GLPI through 10.0.2 is susceptible to remote command execution injection in /vendor/htmlawed/htmlawed/...
2022年10月31日 04:03CVE-2023-41265: Qlik Sense Enterprise – HTTP Request Smuggling
漏洞标题 CVE-2023-41265: Qlik Sense Enterprise - HTTP Request Smuggling 漏洞描述 An HTTP Request Tunneling vulnerability found in Qlik Sense Enterprise for Windows for versions May...
2023年2月15日 05:11CVE-2019-9193: PostgreSQL 9.3-12.3 Authenticated Remote Code Execution
漏洞标题 CVE-2019-9193: PostgreSQL 9.3-12.3 Authenticated Remote Code Execution 漏洞描述 In PostgreSQL 9.3 through 11.2, the "COPY TO/FROM PROGRAM" function allows superu...
2019年8月17日 16:08
西方最大轮胎制造商普利司通遭勒索软件攻击,攻击者自称无政治立场
普利司通是世界最知名的轮胎制造商之一,在美洲拥有50多家生产工厂和55000名员工。近日,该公司确认遭到Lockbit勒索软件攻击,重要数据遭窃。Lockbit勒索软件团伙威胁普利司通在2022年3月15日23...
2022年3月16日 09:16CVE-2025-34032: Moodle LMS Jmol Plugin <= 6.1 - Cross-Site Scripting
漏洞标题 CVE-2025-34032: Moodle LMS Jmol Plugin <= 6.1 - Cross-Site Scripting 漏洞描述 A reflected cross-site scripting (XSS) vulnerability exists in the Moodle LMS Jmol plugin ...
2025年6月29日 05:56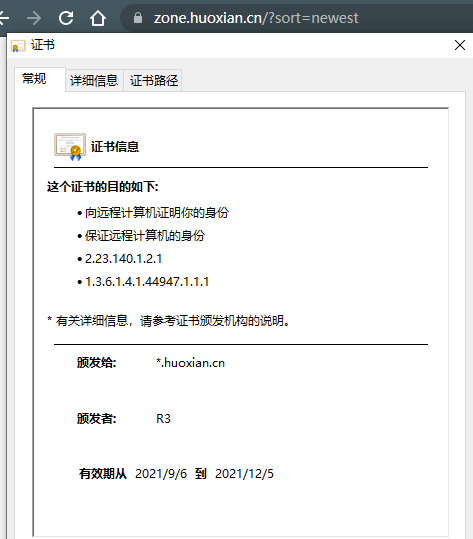
批量获取网站SSL证书里的域名
大佬们在日常刷洞过程中,或者批量扫某个POC时,总会扫到很多未知资产或者结果量太大一个个去验证资产归属太费时费力。而一些https站点的证书中能看到证书归属,一般通过证书定位的资产都比较准...
2022年3月10日 23:33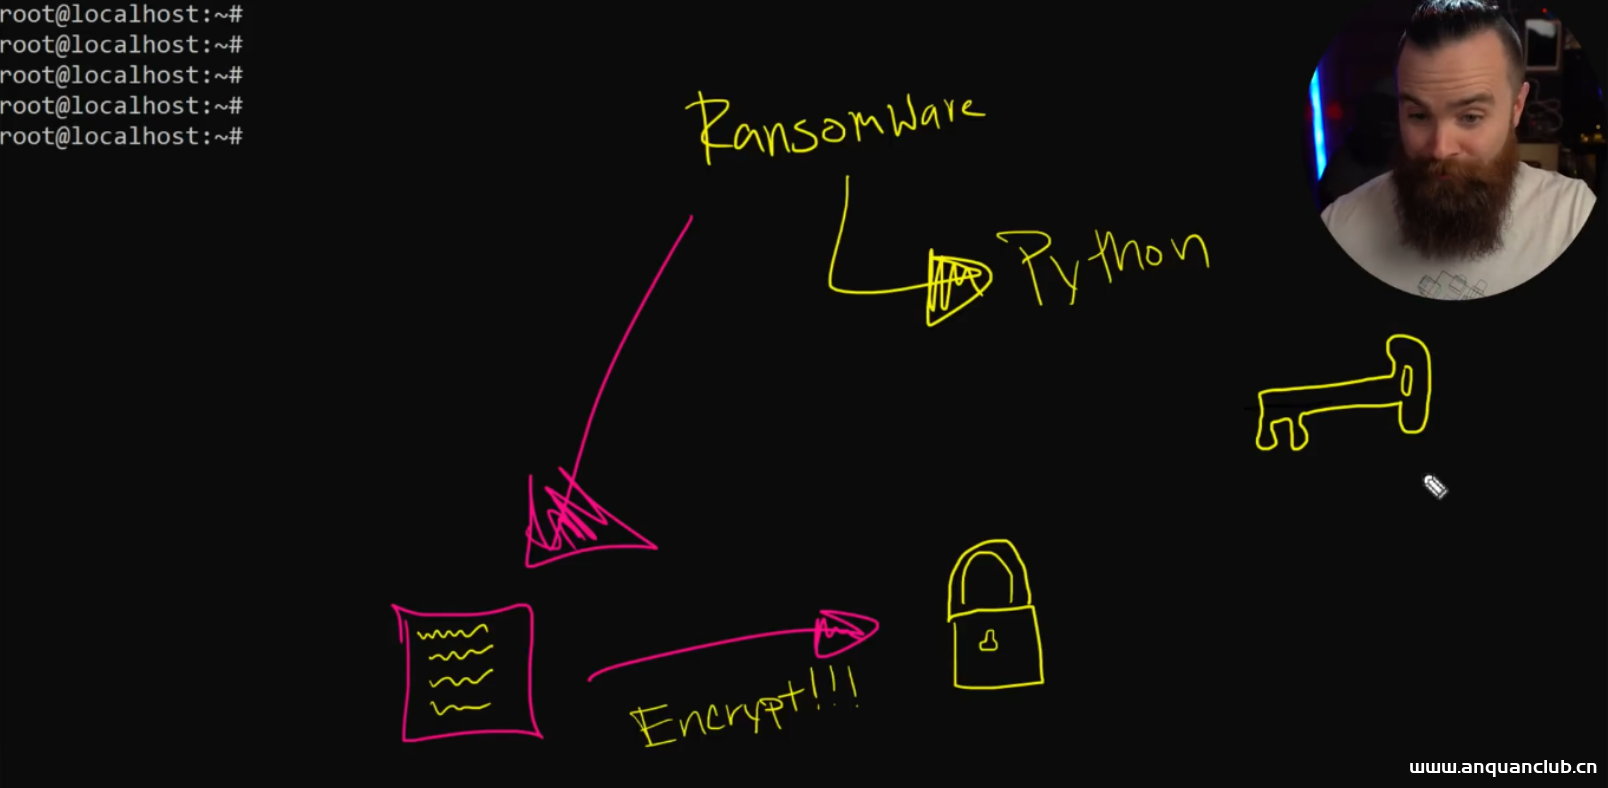
如何使用Python编写一个简单好玩的勒索程序?
相关阅读 图文讲解 原理分析 其实我们要写的脚本本质上就是一个加密程序,将文件内容通过Fernet算法进行加密,然后生成key,后面我们可以通过key在进行解密,这个过程是不是像极了勒索的场面…...

 2023年1月13日 19:56
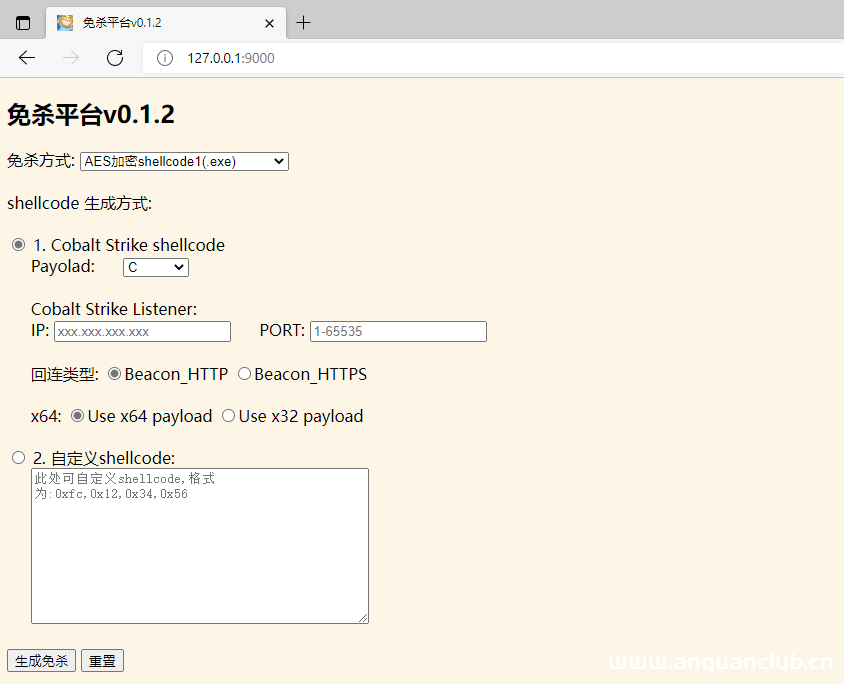
免杀基础教学
0x00 前言: 最近闲来无事搞了一个免杀平台玩儿玩儿,用于生成免杀Cobalt Strike木马和免杀加载一些其它shellcode(如msf、自定义等),这里就和大家分享一下免杀思路。 通过本篇文章你将学会: 杀...
2022年3月10日 23:36
Nginx服务器添加Systemd自定义服务过程解析_nginx
这篇文章主要介绍了Nginx服务器添加Systemd自定义服务过程解析,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友可以参考下 一、以nginx为例 使用yum命...
2023年1月19日 20:36使用Tomcat Native提升Tomcat IO效率的方法详解_Tomcat
这篇文章主要介绍了使用Tomcat Native提升Tomcat IO效率的方法,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 目录简介Tomcat的连接方式APR和Tom...
2022年12月2日 21:07Nginx 负载均衡是什么以及该如何配置_nginx
这篇文章主要介绍了Nginx 负载均衡是什么以及该如何配置,帮助大家更好的理解和使用Nginx服务器,感兴趣的朋友可以了解下 什么是负载均衡 负载均衡主要通过专门的硬件设备或者通过软件算法实现...
2022年10月7日 20:37
2026年9月20日 11:45
2026年9月19日 11:45
2026年9月18日 11:46
2026年9月17日 18:46
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

