
最新发布第635页

CVE-2017-12637: SAP NetWeaver Application Server Java 7.5 – Local File Inclusion
漏洞标题 CVE-2017-12637: SAP NetWeaver Application Server Java 7.5 - Local File Inclusion 漏洞描述 SAP NetWeaver Application Server Java 7.5 is susceptible to local file inclusion ...
 2017年6月26日 09:35

bugbounty技巧聚合20220120
漏洞报告 【 Recorded Future】Dom Xss 漏洞 http://hackerone.com/reports/1448616 【 U.S. Dept Of Defense】ADF Faces 中的错误设置导致信息泄露 http://hackerone.com/reports/1422641 【 U...
2022年3月10日 23:39CVE-2023-40779: IceWarp Mail Server Deep Castle 2 v.13.0.1.2 – Open Redirect
漏洞标题 CVE-2023-40779: IceWarp Mail Server Deep Castle 2 v.13.0.1.2 - Open Redirect 漏洞描述 An issue in IceWarp Mail Server Deep Castle 2 v.13.0.1.2 allows a remote attacker to ...
2023年6月28日 05:47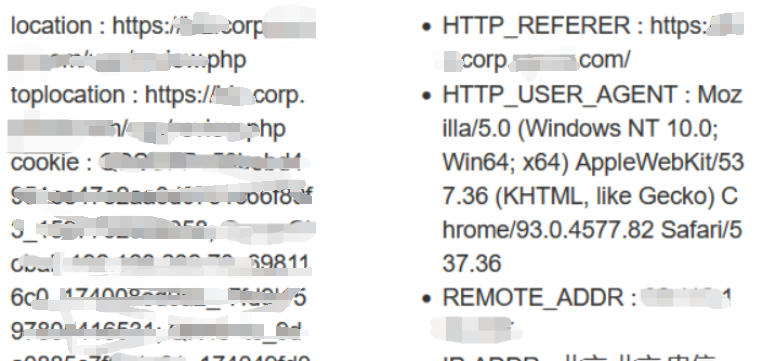
内网xss结合host碰撞到内部应用任意访问
一、引言: 某天在挖掘xss的过程中,本着见框就插的原则,不会轻易放过任何一个可以输入内容的地方。 有些内容输入之后即可显示在页面上,有些内容输入之后会输出到别的系统上,可能是一些后台...
2022年3月10日 23:30CVE-2024-53900: Mongoose < 8.8.3 - Remote Code Execution
漏洞标题 CVE-2024-53900: Mongoose < 8.8.3 - Remote Code Execution 漏洞描述 Mongoose before 8.8.3 can improperly use $where in match, leading to search injection. PoC代码
2024年11月30日 00:27Apache OFBiz CVE-2024-38856 未授权代码执行漏洞
漏洞标题 Apache OFBiz CVE-2024-38856 未授权代码执行漏洞 漏洞描述 Apache OFBiz存在未授权代码执行漏洞,该漏洞是由于ProgramExport接口对用户的权限校验不当导致的。 PoC代码 暂无
2024年3月29日 17:49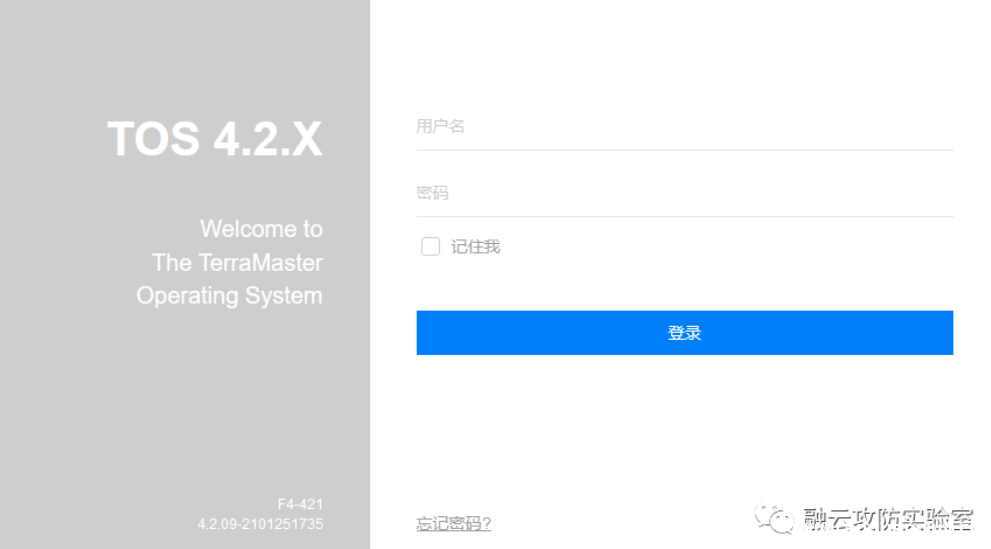
TerraMaster TOS exportUser.php 远程命令执行
本文转载于公众号:融云攻防实验室,原文地址: 漏洞复现 TerraMaster TOS exportUser.php 远程命令执行 TerramasterTOS是中国深圳市图美电子技术(Terramaster)公司的一款基于Linux平台的,专...
2026年2月13日 12:53CVE-2010-1315: Joomla! Component webERPcustomer – Local File Inclusion
漏洞标题 CVE-2010-1315: Joomla! Component webERPcustomer - Local File Inclusion 漏洞描述 A directory traversal vulnerability in weberpcustomer.php in the webERPcustomer (com_weberp...
2010年2月28日 03:20Linux执行可执行文件提示No such file or directory的解决方法_Linux
这篇文章主要介绍了Linux执行可执行文件提示No such file or directory的解决方法,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编来...
2024年1月16日 20:19CVE-2017-1000353: Jenkins CLI – Java Deserialization
漏洞标题 CVE-2017-1000353: Jenkins CLI - Java Deserialization 漏洞描述 Jenkins versions 2.56 and earlier as well as 2.46.1 LTS and earlier are vulnerable to an unauthenticated remo...
2017年12月28日 06:04CVE-2020-26919: NETGEAR ProSAFE Plus – Unauthenticated Remote Code Execution
漏洞标题 CVE-2020-26919: NETGEAR ProSAFE Plus - Unauthenticated Remote Code Execution 漏洞描述 NETGEAR ProSAFE Plus before 2.6.0.43 is susceptible to unauthenticated remote code ex...
2020年3月9日 15:42
Windows DNS服务器曝”蠕虫级”漏洞,已存在长达17年_win服务器
这篇文章主要介绍了Windows DNS服务器曝"蠕虫级"漏洞,已存在长达17年,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 漏洞介绍 SigRed...
2023年9月23日 20:43Apache Struts2(S2-061)远程代码执行漏洞(CVE-2020-17530)
漏洞标题 Apache Struts2(S2-061)远程代码执行漏洞(CVE-2020-17530) 漏洞描述 Apache Struts2框架是一个用于开发Java EE网络应用程序的Web框架。Struts2 会对某些标签属性(比如 id,其他属性有...
2020年3月21日 11:17CVE-2025-1595: EasyCVR <=2.1.2 - Information Disclosure
漏洞标题 CVE-2025-1595: EasyCVR <=2.1.2 - Information Disclosure 漏洞描述 A vulnerability has been found in Anhui Xufan Information Technology EasyCVR up to 2.7.0 and classified...
2025年4月22日 10:46CVE-2021-31195: Microsoft Exchange Server – Cross-Site Scripting
漏洞标题 CVE-2021-31195: Microsoft Exchange Server - Cross-Site Scripting 漏洞描述 Microsoft Exchange Server, or OWA, is vulnerable to a cross-site scripting vulnerability in refur...
2021年12月18日 04:42CVE-2020-2551: Oracle WebLogic Server – Remote Code Execution
漏洞标题 CVE-2020-2551: Oracle WebLogic Server - Remote Code Execution 漏洞描述 Oracle WebLogic Server (Oracle Fusion Middleware (component: WLS Core Components) is susceptible to ...
2020年7月30日 22:09
2026年11月9日 11:45
2026年11月8日 11:45
2026年11月7日 11:45
2026年11月6日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

