
最新发布第654页

CVE-2022-45037: WBCE CMS v1.5.4 – Cross Site Scripting (Stored)
漏洞标题 CVE-2022-45037: WBCE CMS v1.5.4 - Cross Site Scripting (Stored) 漏洞描述 A cross-site scripting (XSS) vulnerability in /admin/users/index.php of WBCE CMS v1.5.4 allows att...
 2022年7月26日 04:37
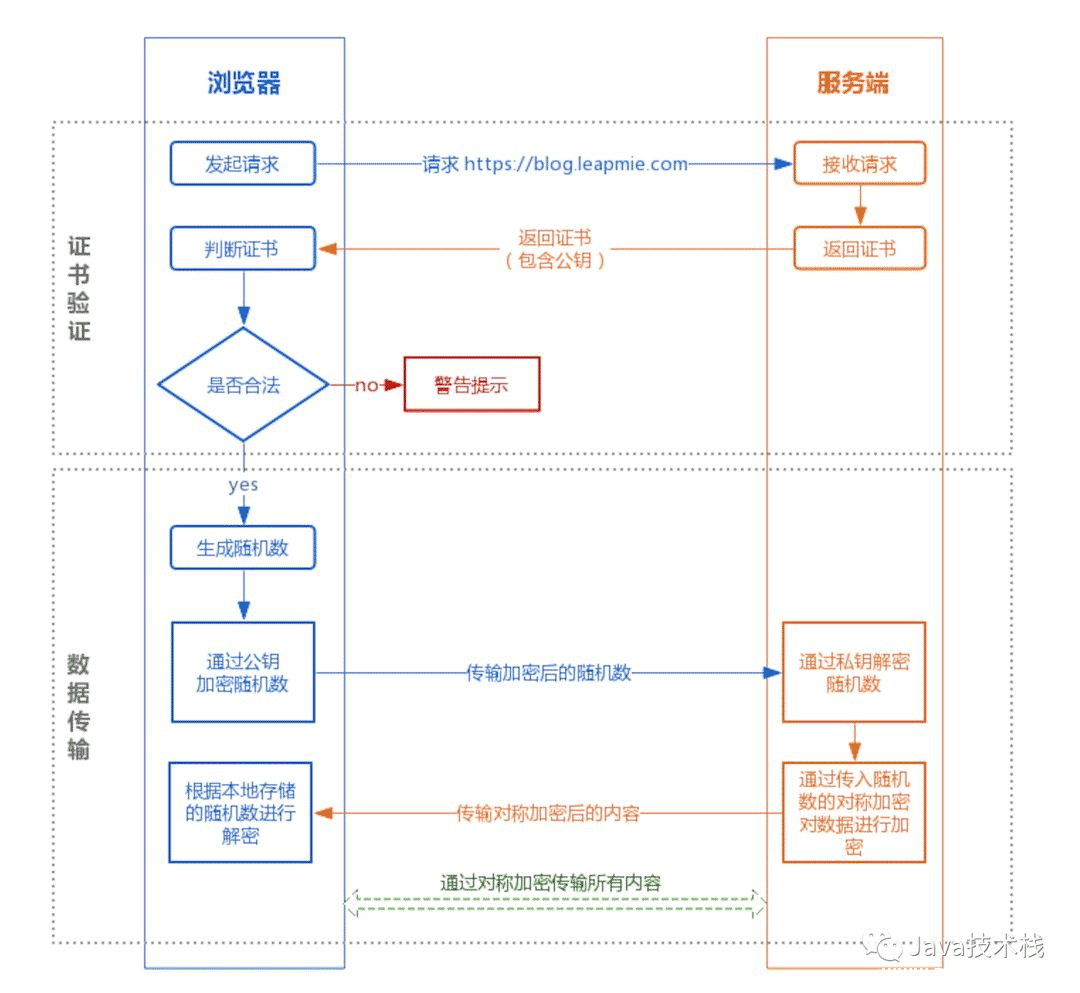
HTTPS 原理详解_服务器其它
这篇干货不错,把HTTPS的原理讲清楚了,而且容易懂,建议大家好好读一下。 随着 HTTPS 建站的成本下降,现在大部分的网站都已经开始用上 HTTPS 协议。大家都知道 HTTPS 比 HTTP 安全,也听说过...
2024年3月13日 20:44CVE-2023-24489: Citrix ShareFile StorageZones Controller – Unauthenticated Remote Code Execution
漏洞标题 CVE-2023-24489: Citrix ShareFile StorageZones Controller - Unauthenticated Remote Code Execution 漏洞描述 A vulnerability has been discovered in the customer-managed Share...
2023年1月4日 01:35CVE-2022-33901: WordPress MultiSafepay for WooCommerce <=4.13.1 - Arbitrary File Read
漏洞标题 CVE-2022-33901: WordPress MultiSafepay for WooCommerce <=4.13.1 - Arbitrary File Read 漏洞描述 WordPress MultiSafepay for WooCommerce plugin through 4.13.1 contains an ...
2022年12月7日 03:01CVE-2022-25084: TOTOLink T6 V5.9c.4085_B20190428 Command Injection
漏洞标题 CVE-2022-25084: TOTOLink T6 V5.9c.4085_B20190428 Command Injection 漏洞描述 TOTOLink 多个设备 download.cgi文件存在远程命令执行漏洞,攻击者通过构造特殊的请求可以获取服务器...
2022年1月1日 14:41
实战小tips (y4师傅传授)
实战小tips (y4师傅传授) 如非php java 写的站如何分辨例如 node.js Flask Django 如果目标机使用了nginx反代 查看js文件 doodoo.js 就是node.js 的框架 查看缓存标识符等等 本文迁移自知识星球...
2022年3月10日 23:34CVE-2021-46005: Sourcecodester Car Rental Management System 1.0 – Stored Cross-Site Scripting
漏洞标题 CVE-2021-46005: Sourcecodester Car Rental Management System 1.0 - Stored Cross-Site Scripting 漏洞描述 Sourcecodester Car Rental Management System 1.0 is vulnerable to cro...
2021年12月12日 00:57CVE-2023-1454: Jeecg Boot QuerySql sql injection
漏洞标题 CVE-2023-1454: Jeecg Boot QuerySql sql injection 漏洞描述 JeecgBoot是一款基于BPM的低代码平台!前后端分离架构 SpringBoot 2.x,SpringCloud,Ant Design&Vue,Mybatis-plus...
2023年8月7日 05:50CVE-2022-4325: WordPress Post Status Notifier Lite <1.10.1 - Cross-Site Scripting
漏洞标题 CVE-2022-4325: WordPress Post Status Notifier Lite <1.10.1 - Cross-Site Scripting 漏洞描述 WordPress Post Status Notifier Lite plugin before 1.10.1 contains a cross-sit...
2022年5月19日 10:13CVE-2020-5775: Canvas LMS v2020-07-29 – Blind Server-Side Request Forgery
漏洞标题 CVE-2020-5775: Canvas LMS v2020-07-29 - Blind Server-Side Request Forgery 漏洞描述 Canvas version 2020-07-29 is susceptible to blind server-side request forgery. An attack...
2020年9月8日 20:56CVE-2010-1307: Joomla! Component Magic Updater – Local File Inclusion
漏洞标题 CVE-2010-1307: Joomla! Component Magic Updater - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the Magic Updater (com_joomlaupdater) component for J...
2010年1月21日 23:53CVE-2025-2010: WordPress JobWP Plugin <= 2.3.9 - SQL Injection
漏洞标题 CVE-2025-2010: WordPress JobWP Plugin <= 2.3.9 - SQL Injection 漏洞描述 The JobWP - Job Board, Job Listing, Career Page and Recruitment Plugin plugin for WordPress is v...
2025年5月3日 04:37CVE-2025-57819: FreePBX – Remote Code Execution
漏洞标题 CVE-2025-57819: FreePBX - Remote Code Execution 漏洞描述 FreePBX 15, 16, and 17 contain a remote code execution caused by insufficiently sanitized user-supplied data in en...
2025年8月16日 18:31CVE-2023-22480: KubeOperator Foreground `kubeconfig` – File Download
漏洞标题 CVE-2023-22480: KubeOperator Foreground `kubeconfig` - File Download 漏洞描述 KubeOperator is an open source Kubernetes distribution focused on helping enterprises plan, d...
2023年2月19日 05:02CVE-2023-38992: Jeecg-Boot v3.5.1 – SQL Injection
漏洞标题 CVE-2023-38992: Jeecg-Boot v3.5.1 - SQL Injection 漏洞描述 SQL injection vulnerability via the title parameter at /sys/dict/loadTreeData in jeecg-boot v3.5.1. PoC代码
2023年9月1日 17:10CVE-2025-1595: EasyCVR <=2.1.2 - Information Disclosure
漏洞标题 CVE-2025-1595: EasyCVR <=2.1.2 - Information Disclosure 漏洞描述 A vulnerability has been found in Anhui Xufan Information Technology EasyCVR up to 2.7.0 and classified...
2025年12月30日 03:14
2026年9月20日 11:45
2026年9月19日 11:45
2026年9月18日 11:46
2026年9月17日 18:46
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

