
最新发布第656页

Casdoor 1.13.0-SQL注入(CVE-2022-24124)
漏洞标题 Casdoor 1.13.0-SQL注入(CVE-2022-24124) 漏洞描述 Casdoor 是一个基于 OAuth 2.0 / OIDC 的 UI 优先集中认证 / 单点登录 (SSO) 平台。该平台存在sql注入漏洞 PoC代码 暂无
 2022年6月15日 06:42
CVE-2020-26413: Gitlab CE/EE 13.4 – 13.6.2 – Information Disclosure
漏洞标题 CVE-2020-26413: Gitlab CE/EE 13.4 - 13.6.2 - Information Disclosure 漏洞描述 GitLab CE and EE 13.4 through 13.6.2 is susceptible to Information disclosure via GraphQL. Use...
2020年6月30日 05:37CVE-2024-13979: St. Joe ERP system – SQL Injection
漏洞标题 CVE-2024-13979: St. Joe ERP system - SQL Injection 漏洞描述 A SQL injection vulnerability exists in the St. Joe ERP system ("圣乔ERP系统") that allows unauthenti...
2024年2月29日 11:56CVE-2019-12988: Citrix SD-WAN Center – Remote Command Injection
漏洞标题 CVE-2019-12988: Citrix SD-WAN Center - Remote Command Injection 漏洞描述 Citrix SD-WAN Center is susceptible to remote command injection via the addModifyZTDProxy function...
2019年12月19日 07:29CVE-2021-41277 Metabase 信息泄露漏洞
漏洞标题 CVE-2021-41277 Metabase 信息泄露漏洞 漏洞描述 CVE-2021-41277 Metabase 信息泄露漏洞 PoC代码 暂无
2021年11月20日 05:33Apache Tomcat Ajp webapp 任意文件读取漏洞(CVE-2020-1938)
漏洞标题 Apache Tomcat Ajp webapp 任意文件读取漏洞(CVE-2020-1938) 漏洞描述 ApacheTomcat会开启AJP连接器,方便与其他Web服务器通过AJP协议进行交互。由于Tomcat本身也内含了HTTP服务器,因...
2020年9月13日 17:14CVE-2022-33198: WordPress Accordions – Unauthenticated Settings Update
漏洞标题 CVE-2022-33198: WordPress Accordions - Unauthenticated Settings Update 漏洞描述 Unauthenticated WordPress Options Change vulnerability in Biplob Adhikari's Accordions...
2022年10月31日 07:19
Docker容器不识别宋体等字体的解决方案_docker
这篇文章主要介绍了Docker容器不识别宋体等字体的解决方案,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 问题背景: 在使用docker部署项目的时候,由于项目中调用打印控件...
2022年7月12日 21:14CVE-2024-1210: LearnDash LMS < 4.10.2 - Sensitive Information Exposure
漏洞标题 CVE-2024-1210: LearnDash LMS < 4.10.2 - Sensitive Information Exposure 漏洞描述 The LearnDash LMS plugin for WordPress is vulnerable to Sensitive Information Exposure i...
2024年2月6日 12:40CVE-2018-19207: WP GDPR Compliance < 1.4.3 - Unauthenticated Call Any Action or Update Any Option
漏洞标题 CVE-2018-19207: WP GDPR Compliance < 1.4.3 - Unauthenticated Call Any Action or Update Any Option 漏洞描述 The WP GDPR Compliance plugin allows unauthenticated users to...
2018年3月1日 17:45
删除docker images中为none的镜像操作_docker
这篇文章主要介绍了删除docker images中为none的镜像操作,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 由于平时一直使用docker build 命令才生成一个镜像,有时候由于代...
2022年8月4日 20:36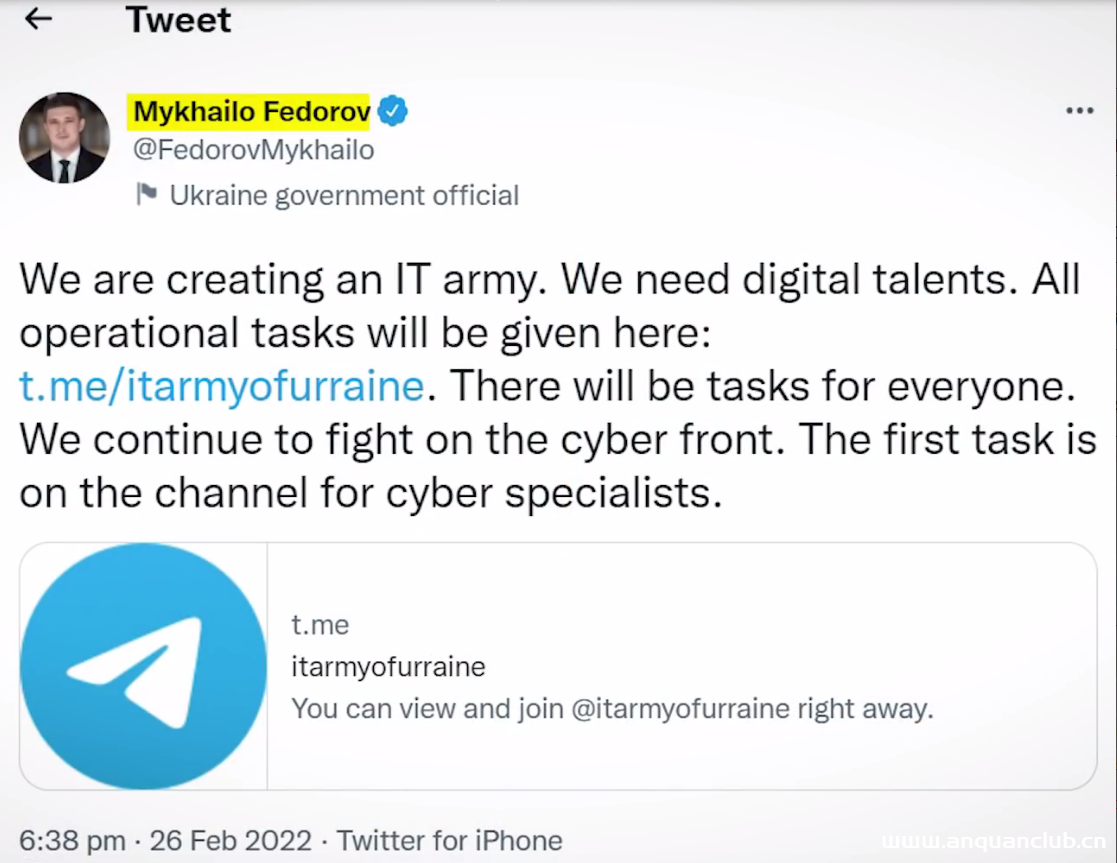
乌克兰网军使用的DDoS工具
相关阅读 图文讲解 在今天的网络安全技术新闻的探讨中,我们将主要讲解乌克兰的IT网军、他们使用的DDoS工具以及很多犯罪分子借助人们捐助制作虚假的DDoS工具盗取个人数据。 首先,我们这里先要...

 2023年1月13日 20:07
CVE-2021-3239: E-Learning System v1.0 SQL注入基于时间盲注漏洞
漏洞标题 CVE-2021-3239: E-Learning System v1.0 SQL注入基于时间盲注漏洞 漏洞描述 user_email 参数似乎容易受到基于时间的盲注的 SQL 注入攻击。 在 user_email 参数中提交了单引号,并返回...
2021年2月3日 11:21CVE-2015-7245: D-Link DVG-N5402SP – Local File Inclusion
漏洞标题 CVE-2015-7245: D-Link DVG-N5402SP - Local File Inclusion 漏洞描述 D-Link DVG-N5402SP is susceptible to local file inclusion in products with firmware W1000CN-00, W1000CN-0...
2015年1月5日 23:12CVE-2010-4769: Joomla! Component Jimtawl 1.0.2 – Local File Inclusion
漏洞标题 CVE-2010-4769: Joomla! Component Jimtawl 1.0.2 - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the Jimtawl (com_jimtawl) component 1.0.2 Joomla! all...
2010年7月4日 20:25CVE-2010-1469: Joomla! Component JProject Manager 1.0 – Local File Inclusion
漏洞标题 CVE-2010-1469: Joomla! Component JProject Manager 1.0 - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the Ternaria Informatica JProject Manager (com...
2010年11月28日 06:20
2026年11月8日 11:45
2026年11月7日 11:45
2026年11月6日 11:45
2026年11月5日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

