
最新发布第659页

CVE-2024-36991: Splunk Enterprise – Local File Inclusion
漏洞标题 CVE-2024-36991: Splunk Enterprise - Local File Inclusion 漏洞描述 In Splunk Enterprise on Windows versions below 9.2.2, 9.1.5, and 9.0.10, an attacker could perform a path...
 2024年7月14日 14:07
CVE-2019-25213: WordPress Advanced Access Manager – Path Traversal
漏洞标题 CVE-2019-25213: WordPress Advanced Access Manager - Path Traversal 漏洞描述 The Advanced Access Manager plugin for WordPress is vulnerable to Unauthenticated Arbitrary Fil...
2019年6月10日 14:17CVE-2019-1003000: Jenkins Script Security Plugin <=1.49 - Sandbox Bypass
漏洞标题 CVE-2019-1003000: Jenkins Script Security Plugin <=1.49 - Sandbox Bypass 漏洞描述 A sandbox bypass vulnerability exists in the Jenkins Script Security Plugin (versions ...
2019年5月13日 02:14CVE-2020-7961: Liferay Portal Unauthenticated < 7.2.1 CE GA2 - Remote Code Execution
漏洞标题 CVE-2020-7961: Liferay Portal Unauthenticated < 7.2.1 CE GA2 - Remote Code Execution 漏洞描述 Liferay Portal prior to 7.2.1 CE GA2 allows remote attackers to execute ar...
2020年8月5日 03:52CVE-2019-17671: WordPress <= 5.2.4 - Unauthenticated View Private/Draft Posts
漏洞标题 CVE-2019-17671: WordPress <= 5.2.4 - Unauthenticated View Private/Draft Posts 漏洞描述 WordPress before 5.2.4 contains an information disclosure caused by mishandling o...
2019年3月7日 23:11
隐患自查 – 关键信息基础设施安全保护 – hvv面试题
护网前防守方的准备工作: 护网前期自查工作清单: 互联网暴露自查: 护网保障资产梳理: 全面基础安全自查: 业务系统风险缝隙: 内部账号安全审计: 安全能力缺陷补充: 资产表的重要性及其作...

 2022年6月29日 17:53
【】-webmin CVE-2020-35606
0x01 webmin描述 Webmin是Webmin社区的一套基于Web的用于类Unix操作系统中的系统管理工具。Webmin 1.962版本及之前版本存在安全漏洞,该漏洞允许执行任意命令。任何被授权使用Package Updates模...
2022年10月31日 11:01
docker 部署 Elasticsearch kibana及ik分词器详解_docker
这篇文章主要介绍了docker 部署 Elasticsearch kibana及ik分词器详解,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 es安装 docker pull elastic...
2022年6月15日 09:43CVE-2020-10220: rConfig 3.9 – SQL Injection
漏洞标题 CVE-2020-10220: rConfig 3.9 - SQL Injection 漏洞描述 An issue was discovered in rConfig through 3.9.4. The web interface is prone to a SQL injection via the commands.inc.p...
2020年12月15日 15:09CVE-2023-6389: WordPress Toolbar <= 2.2.6 - Open Redirect
漏洞标题 CVE-2023-6389: WordPress Toolbar <= 2.2.6 - Open Redirect 漏洞描述 The plugin redirects to any URL via the "wptbto" parameter. This makes it possible for unau...
2023年9月6日 12:09在 Linux 上使用 Multitail命令的教程_Linux
MultiTail是一个开源的ncurses的实用工具,可用于在一个窗口或单一外壳,显示实时一样的尾巴命令,该命令拆分控制台为更多子窗口的日志文件的最后几行。这篇文章主要介绍了在 Linux 上使用 Mult...
2026年5月6日 11:45CVE-2025-31489: MinIO – Incomplete Signature Validation for Unsigned-Trailer Uploads
漏洞标题 CVE-2025-31489: MinIO - Incomplete Signature Validation for Unsigned-Trailer Uploads 漏洞描述 MinIO is a High Performance Object Storage released under GNU Affero General ...
2025年1月20日 18:19CVE-2023-2982: Miniorange Social Login and Register <= 7.6.3 - Authentication Bypass
漏洞标题 CVE-2023-2982: Miniorange Social Login and Register <= 7.6.3 - Authentication Bypass 漏洞描述 The WordPress Social Login and Register (Discord, Google, Twitter, LinkedI...
2023年6月29日 23:30CVE-2021-3654: Nova noVNC – Open Redirect
漏洞标题 CVE-2021-3654: Nova noVNC - Open Redirect 漏洞描述 Nova noVNC contains an open redirect vulnerability. An attacker can redirect a user to a malicious site and possibly obt...
2021年10月22日 20:55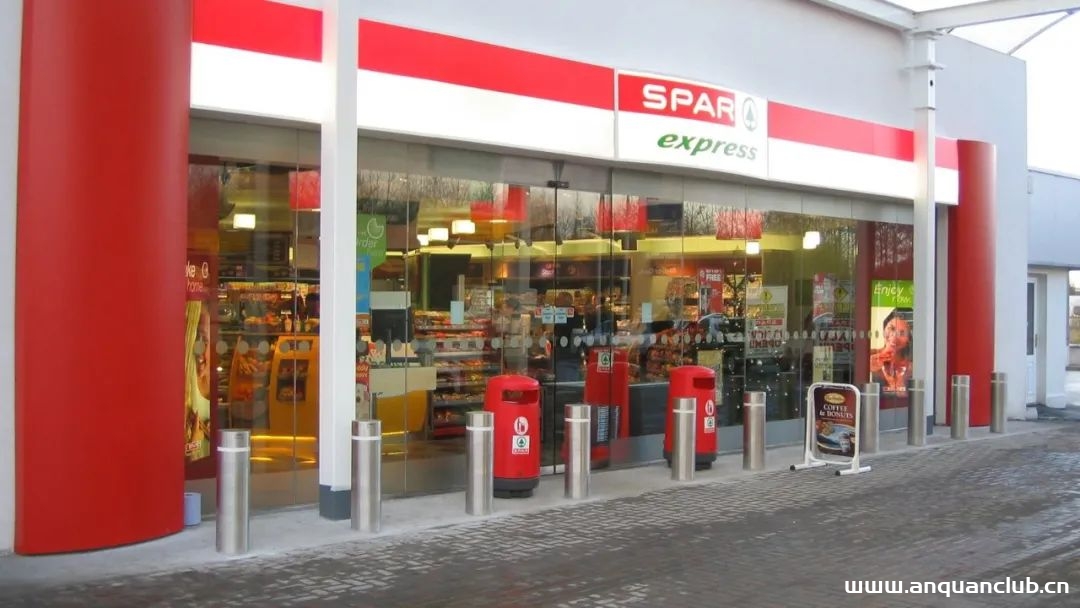
商店或关闭或只支持现金,英国北部SPAR遭遇IT中断
12月5日,英国北部的SPAR商店纷纷关闭。次日,仅有少数商店重新开门营业。但也仅支持现金支付。SPAR是总部在荷兰的国际批发零售连锁公司,在48个国家经营着13320家门店,是世界最大的自愿连锁组...
2022年3月10日 23:39Atlassian Confluence CVE-2023-22515 权限提升漏洞 (阶段1: 属性修改)
漏洞标题 Atlassian Confluence CVE-2023-22515 权限提升漏洞 (阶段1: 属性修改) 漏洞描述 Atlassian Confluence CVE-2023-22515 权限提升漏洞 (阶段1: 属性修改) 日期: 2024-02-07 | 影响软件:...
2023年5月4日 04:40
2026年11月7日 11:45
2026年11月6日 11:45
2026年11月5日 11:45
2026年11月4日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

