
最新发布第65页

CVE-2025-25291: GitLab – SAML Authentication Bypass
漏洞标题 CVE-2025-25291: GitLab - SAML Authentication Bypass 漏洞描述 ruby-saml provides security assertion markup language (SAML) single sign-on (SSO) for Ruby. An authentication ...
 2025年1月16日 22:00
CVE-2025-31125: Vite Development Server – Path Traversal
漏洞标题 CVE-2025-31125: Vite Development Server - Path Traversal 漏洞描述 Path traversal vulnerability in Vite development server's @fs endpoint allows attackers to access fi...
2025年12月30日 11:00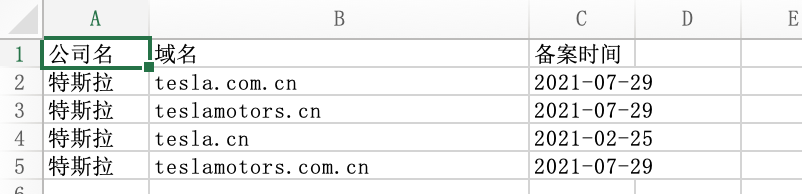
信息收集系列之自动化工具ShuiZe_0x727
0x01 前言 最近0x727团队开源了一款信息收集自动化工具-水泽。可以说是一见钟情,使用很丝滑,代码清晰适合二次开发。skr~skr~ 0x02 体验一条龙服务 以我们的老朋友tesla.cn为例子,跑一下脚...
2022年3月10日 23:34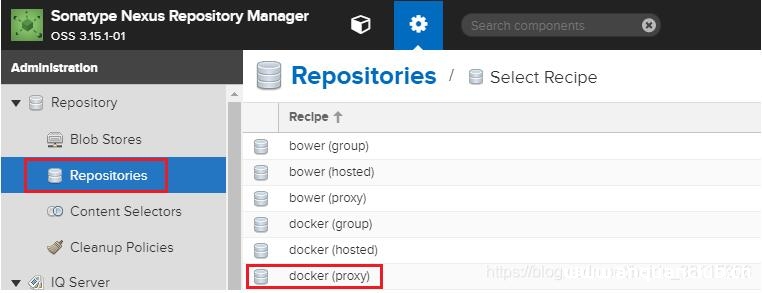
利用nexus作为私库进行代理docker,进行上传和下载镜像操作_docker
这篇文章主要介绍了利用nexus作为私库进行代理docker,进行上传和下载镜像操作,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 一、nexus的配置 1.创建docker proxy 用于从外...
2023年1月22日 21:29CVE-2023-4173: mooSocial 3.1.8 – Reflected XSS
漏洞标题 CVE-2023-4173: mooSocial 3.1.8 - Reflected XSS 漏洞描述 A vulnerability, which was classified as problematic, was found in mooSocial mooStore 3.1.6. Affected is an unknown...
2023年3月14日 08:14CVE-2022-28666: Custom Product Tabs for WooCommerce < 1.7.8 - Unauthenticated Toggle Content Setting Update
漏洞标题 CVE-2022-28666: Custom Product Tabs for WooCommerce < 1.7.8 - Unauthenticated Toggle Content Setting Update 漏洞描述 YIKES Inc. Custom Product Tabs for WooCommerce plug...
2022年10月24日 10:17CVE-2020-14750: Oracle WebLogic Server – Remote Command Execution
漏洞标题 CVE-2020-14750: Oracle WebLogic Server - Remote Command Execution 漏洞描述 Oracle WebLogic Server 10.3.6.0.0, 12.1.3.0.0, 12.2.1.3.0, 12.2.1.4.0 and 14.1.1.0.0 is suscepti...
2020年6月8日 14:32CVE-2010-1723: Joomla! Component iNetLanka Contact Us Draw Root Map 1.1 – Local File Inclusion
漏洞标题 CVE-2010-1723: Joomla! Component iNetLanka Contact Us Draw Root Map 1.1 - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the iNetLanka Contact Us Dra...
2010年2月17日 06:19CVE-2017-18565: Updater by BestWebSoft < 1.35 - Cross-Site Scripting
漏洞标题 CVE-2017-18565: Updater by BestWebSoft < 1.35 - Cross-Site Scripting 漏洞描述 The updater plugin before 1.35 for WordPress has multiple XSS issues. PoC代码
2017年4月16日 06:03
常规MD5通杀脚本
在最近的业务项目中,有一些app样本需要抓取数据包进行重放,但是因为有sign的存在,使得这一过程进行的话并不是很顺利。因此要对该sign进行解密。刚开始观察一下sign的格式,发现跟md5很相似,...
2022年3月10日 23:34CVE-2016-1000142: WordPress MW Font Changer <=4.2.5 - Cross-Site Scripting
漏洞标题 CVE-2016-1000142: WordPress MW Font Changer <=4.2.5 - Cross-Site Scripting 漏洞描述 WordPress MW Font Changer plugin 4.2.5 and before contains a cross-site scripting vu...
2016年6月28日 01:14CVE-2015-2068: Magento Server Mass Importer – Cross-Site Scripting
漏洞标题 CVE-2015-2068: Magento Server Mass Importer - Cross-Site Scripting 漏洞描述 Magento Server Mass Importer plugin contains multiple cross-site scripting vulnerabilities whic...
2015年1月11日 16:44CVE-2005-2428: Lotus Domino R5 and R6 WebMail – Information Disclosure
漏洞标题 CVE-2005-2428: Lotus Domino R5 and R6 WebMail - Information Disclosure 漏洞描述 Lotus Domino R5 and R6 WebMail with 'Generate HTML for all fields' enabled (which...
2005年11月18日 19:50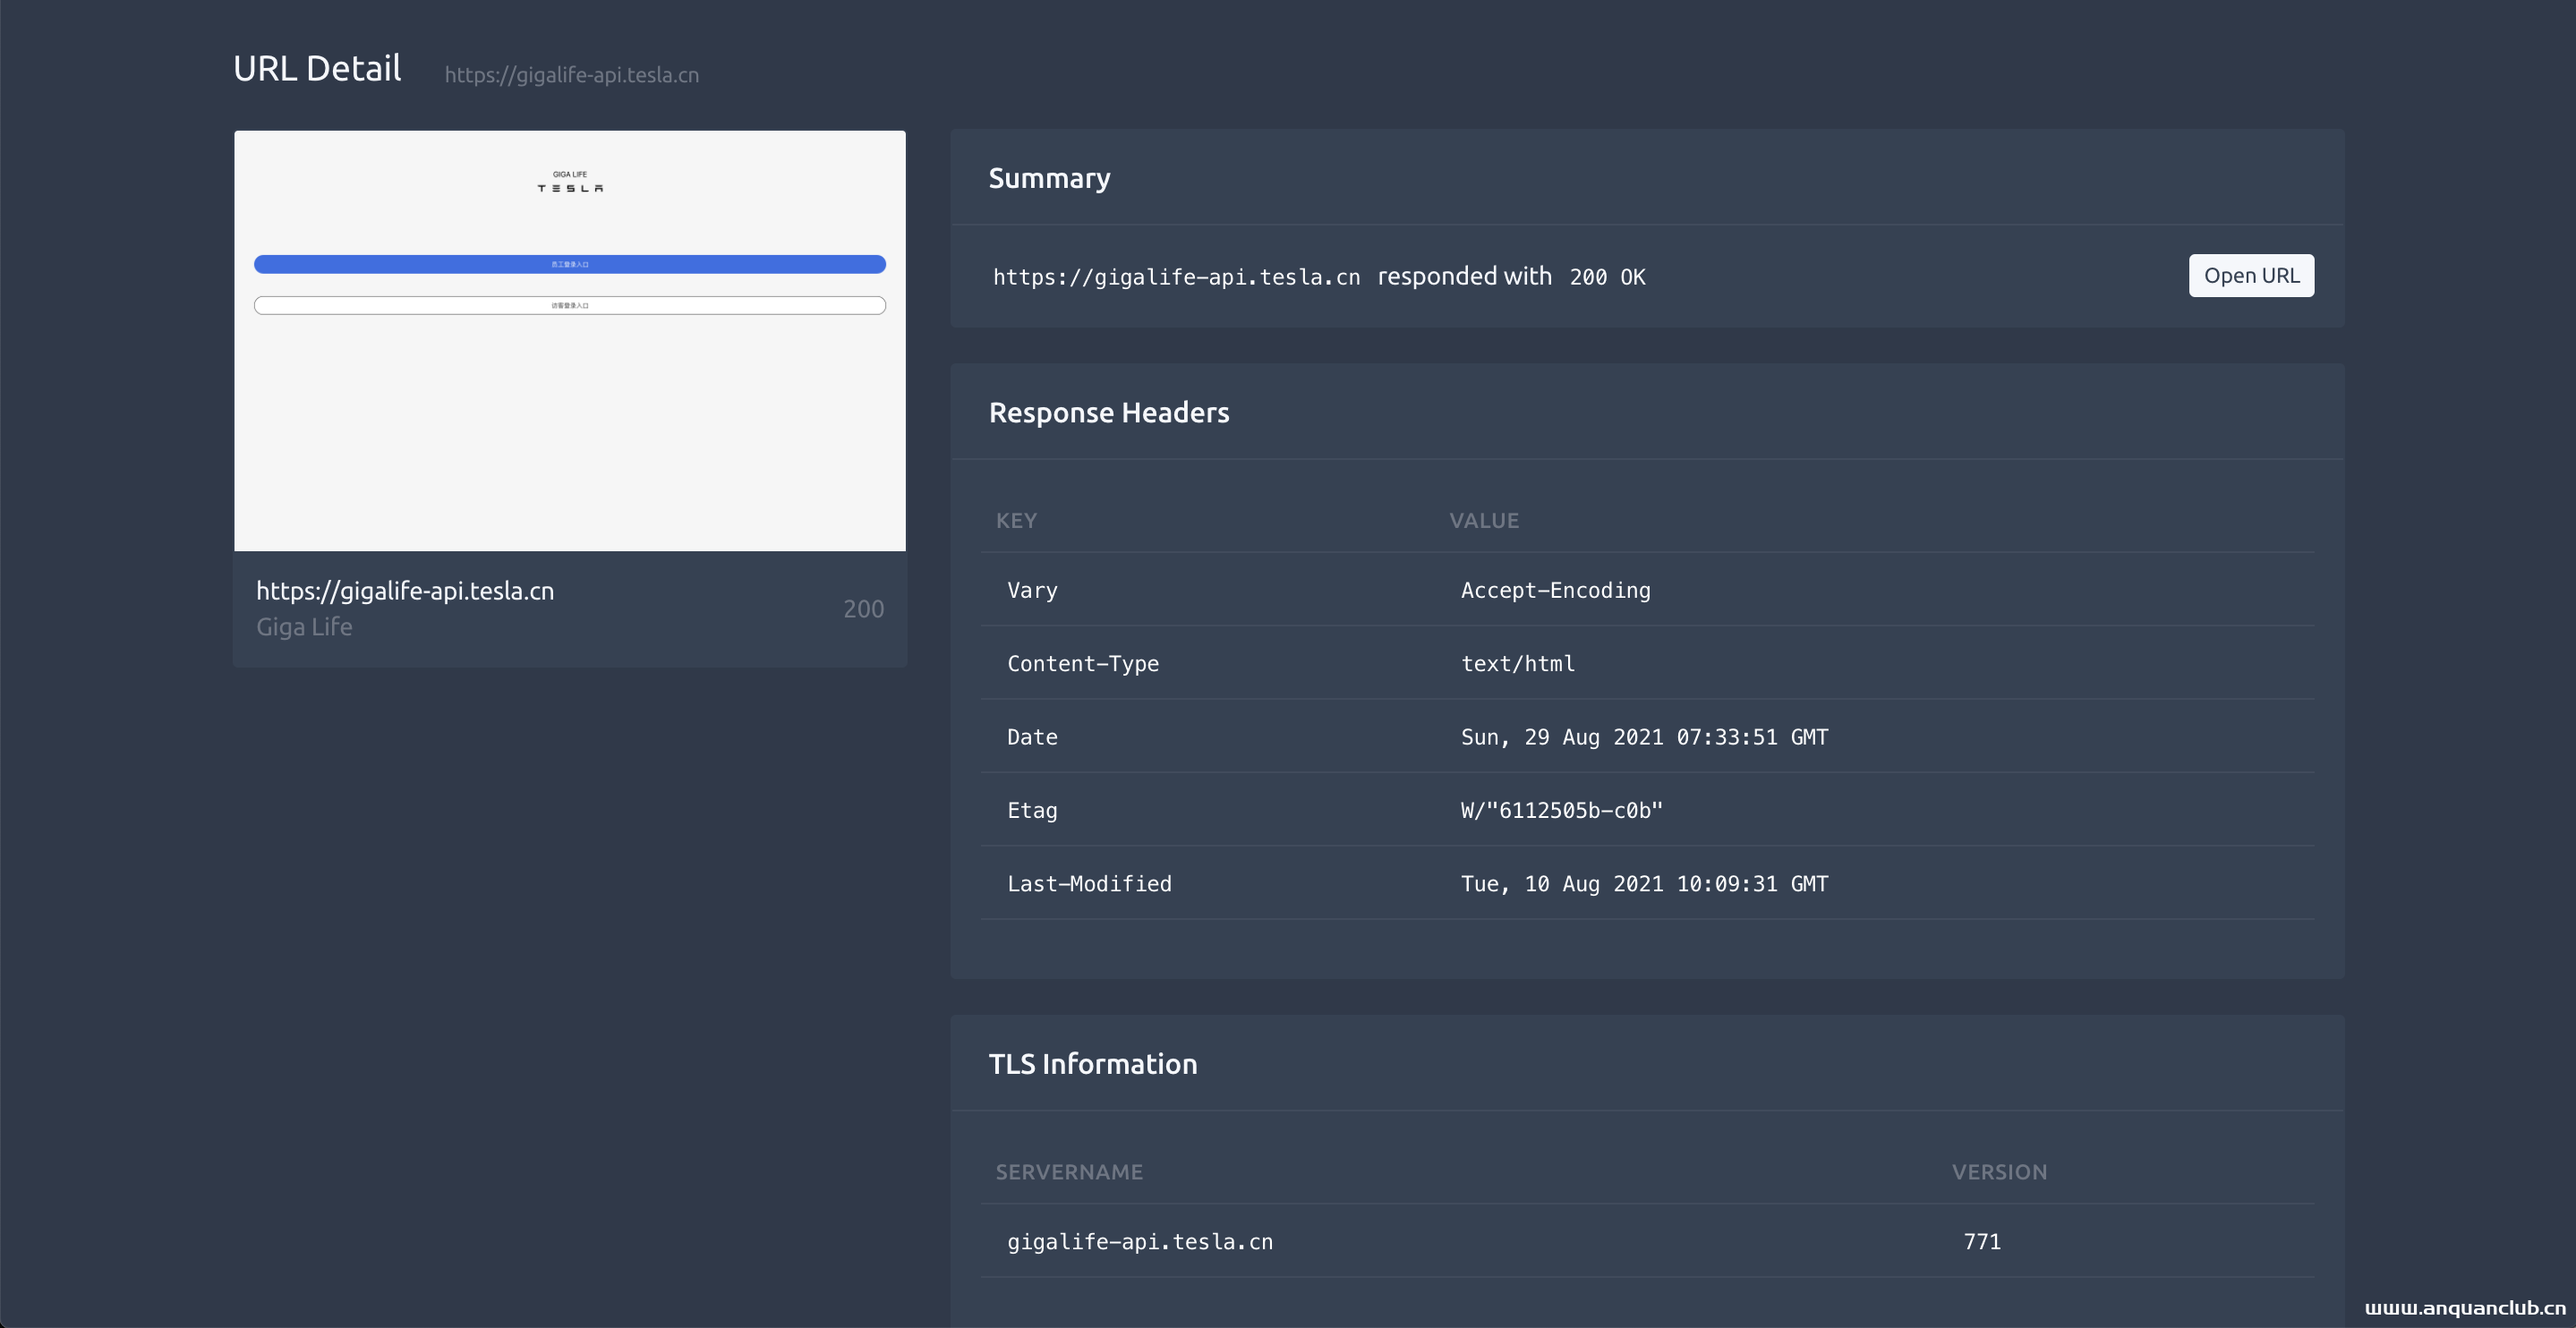
信息收集系列之网站快照
0x01 前言 似乎有20天没更新信息收集系列文章,水一篇。在我们渗透/挖洞过程中,网站快照总能帮我们快速甄别有趣的资产。 市面上也有很多工具可以对网站进行截图,例如aquatone、EyeWitness、go...
2022年3月10日 23:32CVE-2010-1307: Joomla! Component Magic Updater – Local File Inclusion
漏洞标题 CVE-2010-1307: Joomla! Component Magic Updater - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the Magic Updater (com_joomlaupdater) component for J...
2010年8月22日 03:52CVE-2024-4577: PHP CGI – Argument Injection
漏洞标题 CVE-2024-4577: PHP CGI - Argument Injection 漏洞描述 PHP CGI - Argument Injection (CVE-2024-4577) is a critical argument injection flaw in PHP. PoC代码
2024年6月29日 12:56
2026年10月24日 11:45
2026年10月23日 11:45
2026年10月22日 11:46
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

