
最新发布第662页

CVE-2025-6174: WordPress Qwizcards < 3.95 - Cross-Site Scripting (Reflected)
漏洞标题 CVE-2025-6174: WordPress Qwizcards < 3.95 - Cross-Site Scripting (Reflected) 漏洞描述 The WordPress Qwizcards plugin before version 3.95 does not sanitise and escape th...
 2025年12月19日 07:16

bugbounty技巧聚合20211027
挖洞技巧 What can I do with Open Redirect with OAuth? http://flex0geek.blogspot.com/2021/10/what-can-i-do-with-open-redirect-with.html Metacommunication and Bug Bounty Programs htt...
2022年3月10日 23:39CVE-2018-3810: Oturia WordPress Smart Google Code Inserter <3.5 - Authentication Bypass
漏洞标题 CVE-2018-3810: Oturia WordPress Smart Google Code Inserter <3.5 - Authentication Bypass 漏洞描述 Oturia Smart Google Code Inserter plugin before 3.5 for WordPress allow...
2018年4月29日 17:11CVE-2023-30777: Advanced Custom Fields < 6.1.6 - Cross-Site Scripting
漏洞标题 CVE-2023-30777: Advanced Custom Fields < 6.1.6 - Cross-Site Scripting 漏洞描述 Advanced Custom Fields beofre 6.1.6 is susceptible to cross-site scripting via the post_s...
2023年6月21日 07:18CVE-2021-21234: Spring Boot Actuator Logview Directory Traversal
漏洞标题 CVE-2021-21234: Spring Boot Actuator Logview Directory Traversal 漏洞描述 spring-boot-actuator-logview before version 0.2.13 contains a directory traversal vulnerability i...
2021年12月23日 20:03CVE-2017-9965: Schneider Electric Pelco VideoXpert Enterprise 2.0 – Path Traversal
漏洞标题 CVE-2017-9965: Schneider Electric Pelco VideoXpert Enterprise 2.0 - Path Traversal 漏洞描述 Schneider Electric Pelco VideoXpert Enterprise versions 2.0 and prior contain a...
2017年6月10日 23:18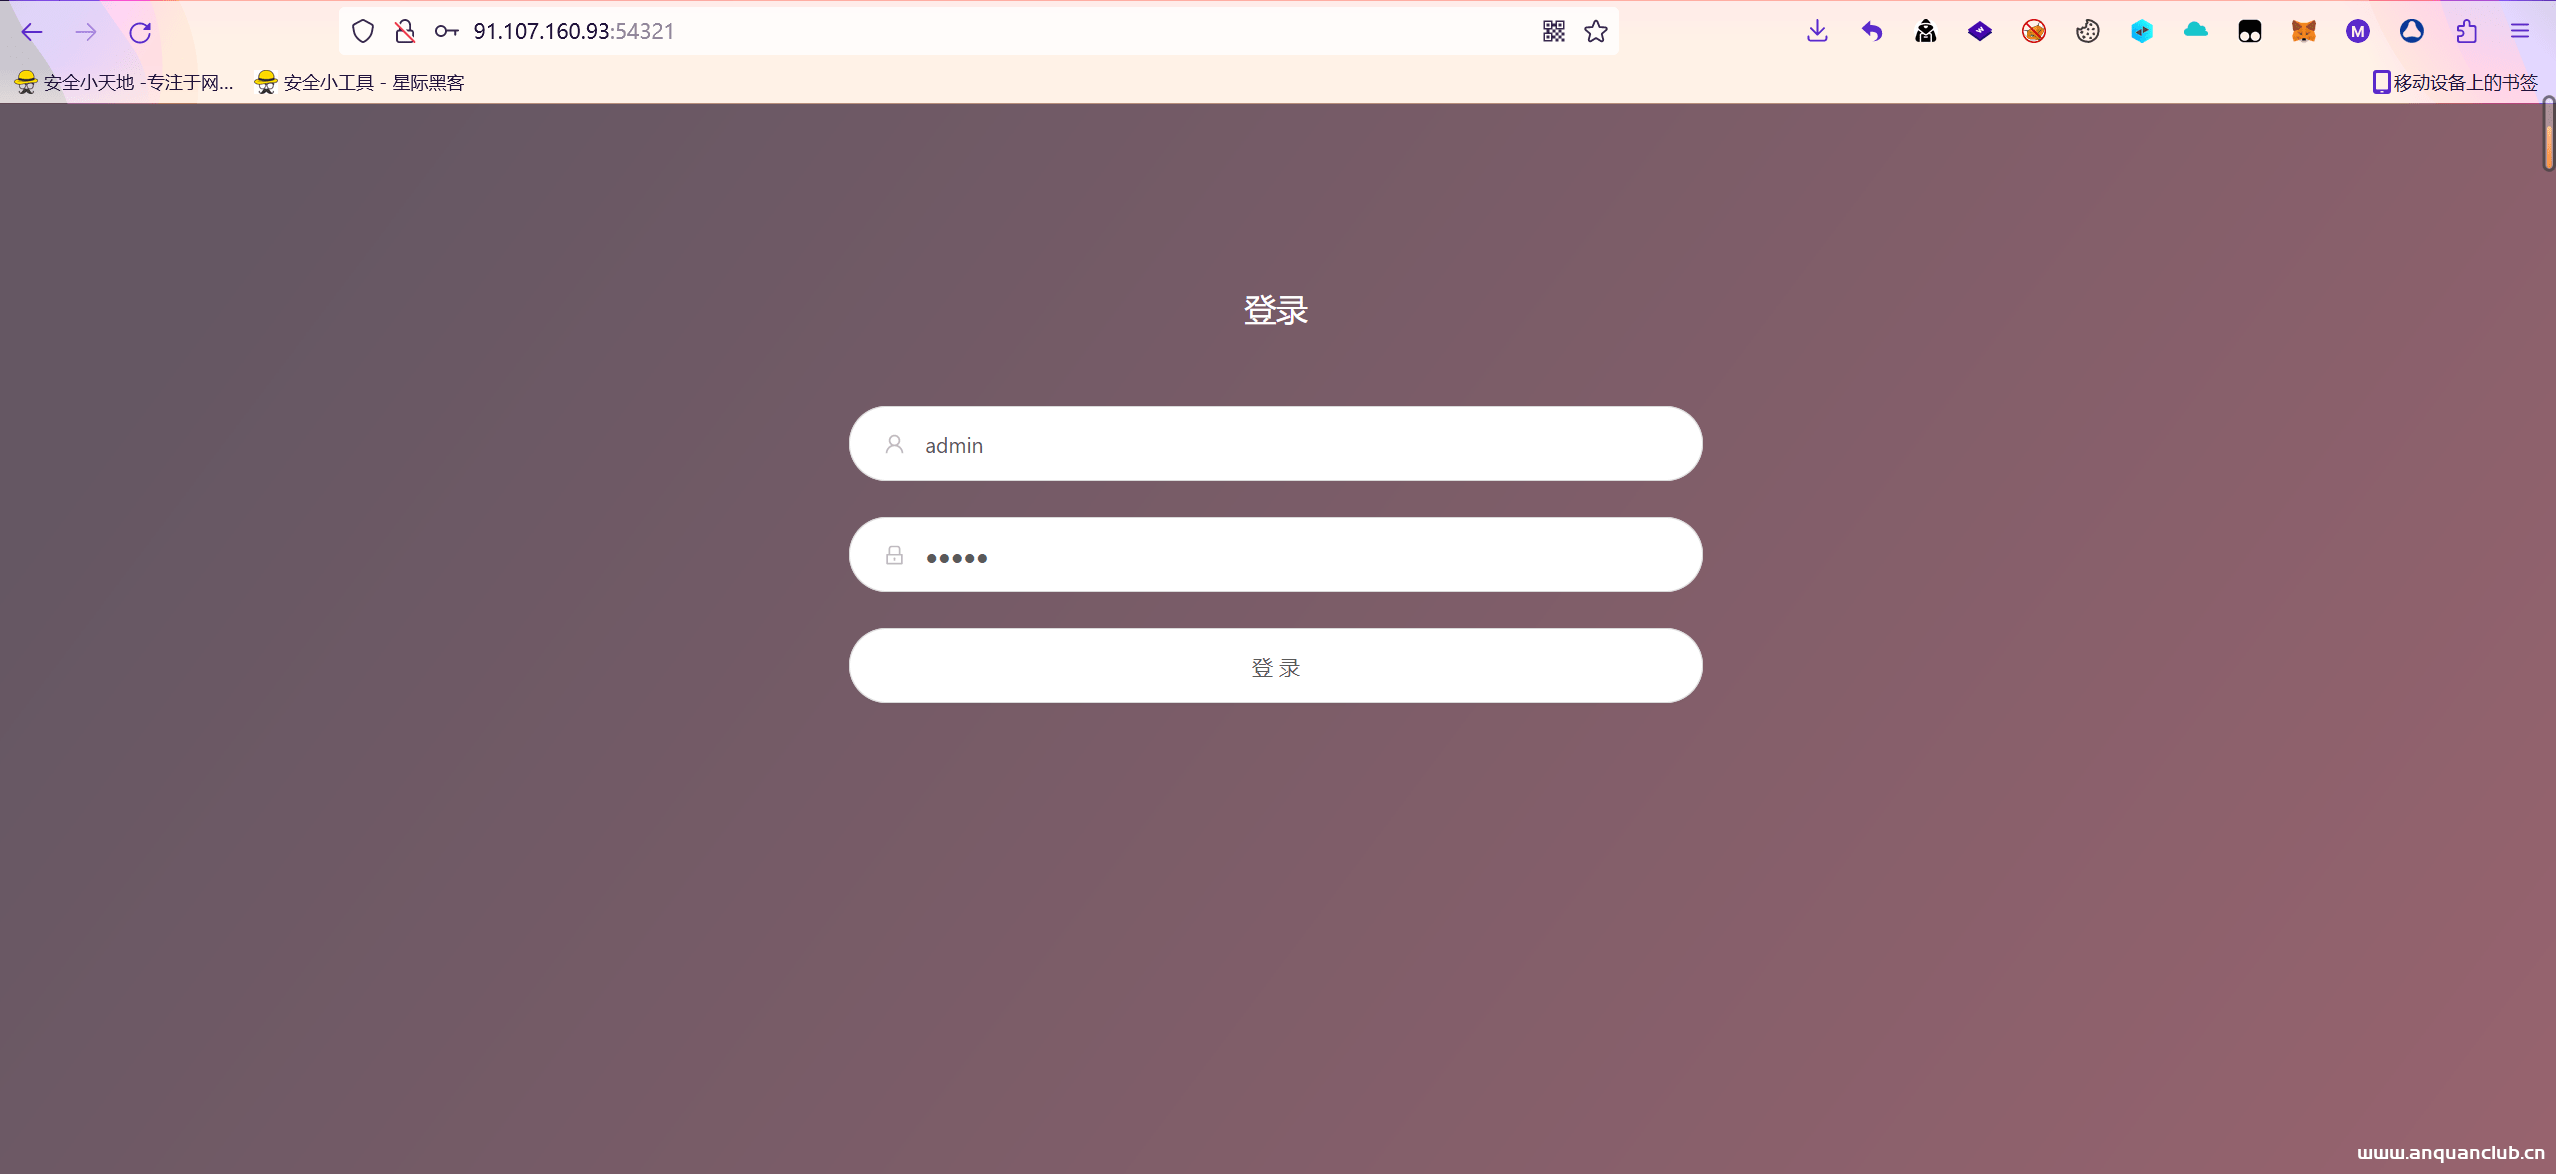
x-ui面板爬虫爬取及登陆分享
前言 最近无意间翻到了以前的一些文章,其中这个x-ui面板还蛮有意思的 首先他有固定特征,按脚本一键安装之后,默认端口就是54321,默认账号:admin,默认密码:admin 虽然后台都有地方修改,但...

 2024年6月6日 14:27
CVE-2024-9474: PAN-OS Management Web Interface – Command Injection
漏洞标题 CVE-2024-9474: PAN-OS Management Web Interface - Command Injection 漏洞描述 A privilege escalation vulnerability in Palo Alto Networks PAN-OS software allows a PAN-OS admi...
2024年3月13日 10:22CVE-2023-34048: VMware vCenter Server – Out-of-Bounds Write
漏洞标题 CVE-2023-34048: VMware vCenter Server - Out-of-Bounds Write 漏洞描述 vCenter Server contains an out-of-bounds write caused by a vulnerability in the DCERPC protocol implem...
2023年9月6日 16:41CVE-2024-43441: Apache HugeGraph-Server <1.5.0 - Authentication Bypass
漏洞标题 CVE-2024-43441: Apache HugeGraph-Server <1.5.0 - Authentication Bypass 漏洞描述 Apache HugeGraph-Server versions prior to 1.5.0 contain an authentication bypass vulnera...
2024年4月13日 19:11CVE-2025-3605: WordPress Frontend Login and Registration Blocks Plugin 1.0.7 – Privilege Escalation
漏洞标题 CVE-2025-3605: WordPress Frontend Login and Registration Blocks Plugin 1.0.7 - Privilege Escalation 漏洞描述 Privilege escalation vulnerability exists in the Frontend Logi...
2025年6月25日 14:55CVE-2022-40734: Laravel Filemanager v2.5.1 – Local File Inclusion
漏洞标题 CVE-2022-40734: Laravel Filemanager v2.5.1 - Local File Inclusion 漏洞描述 Laravel Filemanager (aka UniSharp) through version 2.5.1 is vulnerable to local file inclusion v...
2022年6月22日 17:25CVE-2023-5074: D-Link D-View 8 v2.0.1.28 – Authentication Bypass
漏洞标题 CVE-2023-5074: D-Link D-View 8 v2.0.1.28 - Authentication Bypass 漏洞描述 Use of a static key to protect a JWT token used in user authentication can allow an for an authen...
2023年8月31日 15:49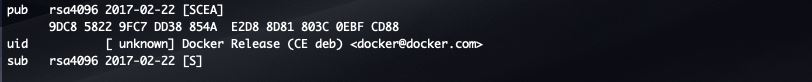
在Ubuntu18.04上安装Docker CE的方法(社区版)_docker
这篇文章主要介绍了在Ubuntu18.04上安装Docker CE的方法(社区版),文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编来一起学习学习吧 ...
2024年6月10日 21:54CVE-2018-6605: Joomla! Component Zh BaiduMap 3.0.0.1 – SQL Injection
漏洞标题 CVE-2018-6605: Joomla! Component Zh BaiduMap 3.0.0.1 - SQL Injection 漏洞描述 SQL Injection exists in the Zh BaiduMap 3.0.0.1 component for Joomla! via the id parameter in...
2018年5月21日 18:42CVE-2017-5983: JIRA Workflow Designer Plugin in Atlassian JIRA Server > 6.3.0 – Remote Code Execution (XXE)
漏洞标题 CVE-2017-5983: JIRA Workflow Designer Plugin in Atlassian JIRA Server > 6.3.0 - Remote Code Execution (XXE) 漏洞描述 The JIRA Workflow Designer Plugin in Atlassian JIRA...
2017年10月25日 19:33
2026年9月28日 11:45
2026年9月27日 11:45
2026年9月26日 11:45
2026年9月25日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

