
最新发布第685页

CVE-2024-28255: OpenMetadata – Authentication Bypass
漏洞标题 CVE-2024-28255: OpenMetadata - Authentication Bypass 漏洞描述 OpenMetadata is a unified platform for discovery, observability, and governance powered by a central metadata...
 2024年9月27日 03:17
CVE-2025-4322: Motors <= 5.6.67 - Unauthenticated Privilege Escalation via Password Update/Account Takeover
漏洞标题 CVE-2025-4322: Motors <= 5.6.67 - Unauthenticated Privilege Escalation via Password Update/Account Takeover 漏洞描述 The Motors theme for WordPress is vulnerable to pri...
2025年12月29日 16:41CVE-2019-12987: Citrix SD-WAN Center – Remote Command Injection
漏洞标题 CVE-2019-12987: Citrix SD-WAN Center - Remote Command Injection 漏洞描述 Citrix SD-WAN Center is susceptible to remote command injection via the apply action in StorageMgm...
2019年9月7日 15:54CVE-2016-10367: Opsview Monitor Pro – Local File Inclusion
漏洞标题 CVE-2016-10367: Opsview Monitor Pro - Local File Inclusion 漏洞描述 Opsview Monitor Pro prior to 5.1.0.162300841, prior to 5.0.2.27475, prior to 4.6.4.162391051, and 4.5.x...
2016年4月20日 01:47CVE-2023-23752: Joomla! Webservice – Password Disclosure
漏洞标题 CVE-2023-23752: Joomla! Webservice - Password Disclosure 漏洞描述 An issue was discovered in Joomla! 4.0.0 through 4.2.7. An improper access check allows unauthorized acce...
2023年1月28日 02:25
一个脚本让你的app自动吐出密钥信息
### 背景 安全小天地某个私密项目中涉及到一个app的测试,打开一看,证书校验--不让抓包,信息加密-无法篡改,遇到这种情况怎么,正常我这种小菜鸡都是直接放弃了,奈何厂家奖金给的高啊,我还...
2022年3月10日 23:36CVE-2021-22986: F5 BIG-IP iControl REST unauthenticated RCE
漏洞标题 CVE-2021-22986: F5 BIG-IP iControl REST unauthenticated RCE 漏洞描述 On BIG-IP versions 16.0.x before 16.0.1.1, 15.1.x before 15.1.2.1, 14.1.x before 14.1.4, 13.1.x before...
2021年8月28日 13:33CVE-2024-6396: Aimhubio Aim Server 3.19.3 – Arbitrary File Overwrite
漏洞标题 CVE-2024-6396: Aimhubio Aim Server 3.19.3 - Arbitrary File Overwrite 漏洞描述 A vulnerability in the `_backup_run` function in aimhubio/aim version 3.19.3 allows remote at...
2024年12月13日 16:30CVE-2018-9118: WordPress 99 Robots WP Background Takeover Advertisements <=4.1.4 - Local File Inclusion
漏洞标题 CVE-2018-9118: WordPress 99 Robots WP Background Takeover Advertisements <=4.1.4 - Local File Inclusion 漏洞描述 WordPress 99 Robots WP Background Takeover Advertisemen...
2018年8月20日 20:18CVE-2017-18536: WordPress Stop User Enumeration <=1.3.7 - Cross-Site Scripting
漏洞标题 CVE-2017-18536: WordPress Stop User Enumeration <=1.3.7 - Cross-Site Scripting 漏洞描述 WordPress Stop User Enumeration 1.3.7 and earlier are vulnerable to unauthentica...
2017年10月11日 12:25adminer存在服务器端请求伪造漏洞(CVE-2021-21311)
漏洞标题 adminer存在服务器端请求伪造漏洞(CVE-2021-21311) 漏洞描述 adminer是一个php开发的数据库管理的web工具,该系统存在ssrf漏洞。 PoC代码 暂无
2021年4月24日 19:34CVE-2019-9978: WordPress Social Warfare <3.5.3 - Cross-Site Scripting
漏洞标题 CVE-2019-9978: WordPress Social Warfare <3.5.3 - Cross-Site Scripting 漏洞描述 WordPress Social Warfare plugin before 3.5.3 contains a cross-site scripting vulnerabilit...
2019年11月27日 00:39CVE-2010-1304: Joomla! Component User Status – Local File Inclusion
漏洞标题 CVE-2010-1304: Joomla! Component User Status - Local File Inclusion 漏洞描述 A directory traversal vulnerability in userstatus.php in the User Status (com_userstatus) comp...
2010年11月19日 13:26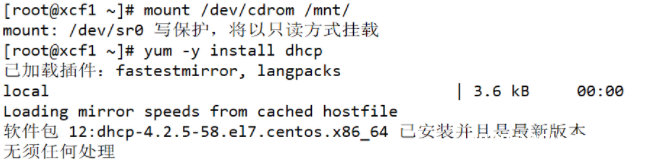
超详细讲解Linux DHCP服务_Linux
这篇文章主要介绍了Linux DHCP 服务,它可以避免IP地址冲突,提高了IP地址的利用率等优点。感兴趣的小伙伴一起来学习吧 目录一、DHCP服务(动态主机配置协议)1.背景2.概述3.优点4.DHCP报文类型...
2022年6月15日 22:46CVE-2022-31161: Roxy-WI – Remote Code Execution
漏洞标题 CVE-2022-31161: Roxy-WI - Remote Code Execution 漏洞描述 Roxy-WI before 6.1.1.0 is susceptible to remote code execution. System commands can be run remotely via the delcer...
2022年2月28日 16:45CVE-2018-10942: Prestashop AttributeWizardPro Module – Arbitrary File Upload
漏洞标题 CVE-2018-10942: Prestashop AttributeWizardPro Module - Arbitrary File Upload 漏洞描述 In the Attribute Wizard addon 1.6.9 for PrestaShop allows remote attackers to execute...
2018年5月30日 18:50
2026年11月7日 11:45
2026年11月6日 11:45
2026年11月5日 11:45
2026年11月4日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

