
最新发布第685页

CVE-2024-46938: Sitecore Experience Platform <= 10.4 - Arbitrary File Read
漏洞标题 CVE-2024-46938: Sitecore Experience Platform <= 10.4 - Arbitrary File Read 漏洞描述 An issue was discovered in Sitecore Experience Platform (XP), Experience Manager (XM...
 2024年12月24日 02:38
CVE-2020-14750: Oracle WebLogic Server – Remote Command Execution
漏洞标题 CVE-2020-14750: Oracle WebLogic Server - Remote Command Execution 漏洞描述 Oracle WebLogic Server 10.3.6.0.0, 12.1.3.0.0, 12.2.1.3.0, 12.2.1.4.0 and 14.1.1.0.0 is suscepti...
2020年10月5日 18:04CVE-2022-34093: Software Publico Brasileiro i3geo v7.0.5 – Cross-Site Scripting
漏洞标题 CVE-2022-34093: Software Publico Brasileiro i3geo v7.0.5 - Cross-Site Scripting 漏洞描述 Portal do Software Publico Brasileiro i3geo v7.0.5 was discovered to contain a cro...
2022年5月3日 16:23CVE-2025-34152: Shenzhen Aitemi M300 Wi-Fi Repeater – Unauthenticated Remote Command Execution via `time` Parameter
漏洞标题 CVE-2025-34152: Shenzhen Aitemi M300 Wi-Fi Repeater – Unauthenticated Remote Command Execution via `time` Parameter 漏洞描述 An unauthenticated OS command injection vulne...
2025年1月11日 14:13CVE-2025-2746: Kentico Xperience 13 CMS – Staging Service Authentication Bypass (WT-2025-0011)
漏洞标题 CVE-2025-2746: Kentico Xperience 13 CMS - Staging Service Authentication Bypass (WT-2025-0011) 漏洞描述 Before Kentico Xperience 13 Hotfix 173, this vulnerability can be e...
2025年8月17日 13:34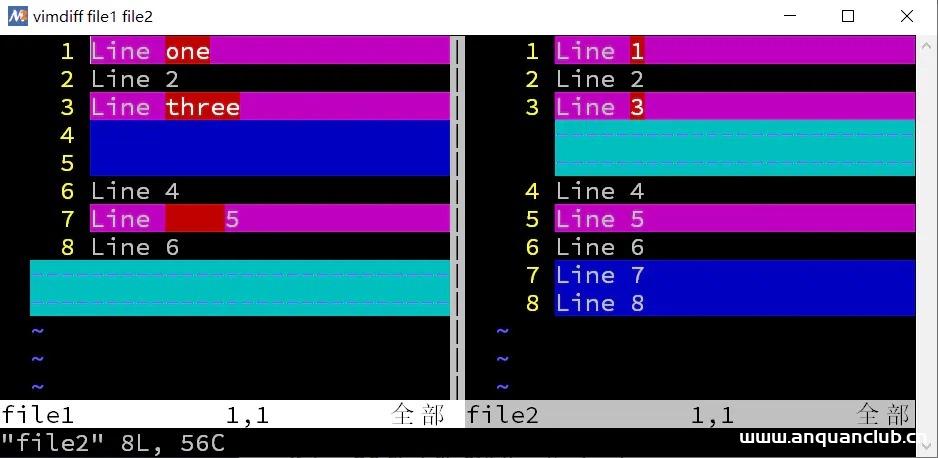
Linux下9种优秀的代码比对工具推荐小结_Linux
这篇文章主要介绍了Linux下9种优秀的代码比对工具推荐小结,不仅有命令行工具,还有 GUI 界面工具,让你轻松进行代码比对,感兴趣的可以一起来了解一下 在我们编写代码的时候,我们经常需要知道...
2023年11月1日 20:45Amcrest IP Camera Web Sha1Account1 账号密码泄漏漏洞(CVE-2017-8229)
漏洞标题 Amcrest IP Camera Web Sha1Account1 账号密码泄漏漏洞(CVE-2017-8229) 漏洞描述 Amcrest IP Camera Web是Amcrest公司的一款无线IP摄像头,设备允许未经身份验证的攻击者下载管理凭据...
2017年3月16日 21:17CVE-2021-39316: WordPress DZS Zoomsounds <=6.50 - Local File Inclusion
漏洞标题 CVE-2021-39316: WordPress DZS Zoomsounds <=6.50 - Local File Inclusion 漏洞描述 WordPress Zoomsounds plugin 6.45 and earlier allows arbitrary files, including sensitive...
2021年8月5日 21:51CVE-2025-51586: PrestaShop – Information Disclosure
漏洞标题 CVE-2025-51586: PrestaShop - Information Disclosure 漏洞描述 User enumeration vulnerability in the AdminLogin controller in PrestaShop 1.7 through 8.2.2 allows remote atta...
2025年8月2日 01:26CVE-2019-2578: Oracle Fusion Middleware WebCenter Sites 12.2.1.3.0 – Broken Access Control
漏洞标题 CVE-2019-2578: Oracle Fusion Middleware WebCenter Sites 12.2.1.3.0 - Broken Access Control 漏洞描述 Oracle Fusion Middleware WebCenter Sites 12.2.1.3.0 suffers from broken...
2019年5月22日 14:18CVE-2010-1056: Joomla! Component com_rokdownloads – Local File Inclusion
漏洞标题 CVE-2010-1056: Joomla! Component com_rokdownloads - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the RokDownloads (com_rokdownloads) component befo...
2010年10月1日 13:05
奇葩漏洞面面观
下载地址:http://i0x0fy4ibf.feishu.cn/file/boxcnP2siX6p3DN3YjKEomok3kb 简介 0x00 众里寻他千百度 0x01 精骛八极,心游万仞 0x02 天下大事,必作于细 0x03 不破楼兰终不还 0x04 工欲善其事,...
2022年3月10日 23:37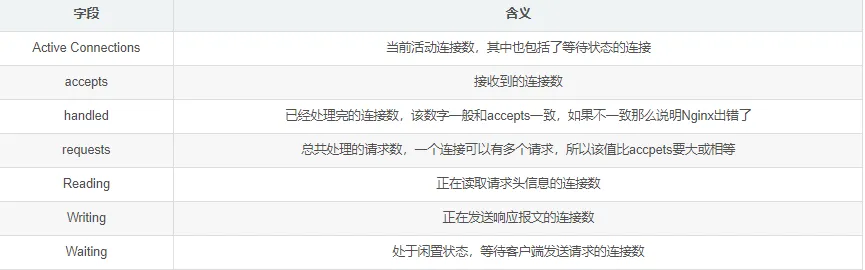
zabbix监控Nginx/Tomcat/MySQL的详细教程_zabbix
这篇文章主要介绍了zabbix监控Nginx/Tomcat/MySQL的详细教程,本文给大家介绍的非常详细,具有一定的参考借鉴价值,需要的朋友可以参考下 目录zabbix监控Nginxzabbix监控Tomcatzabbix监控MySQLza...
2026年4月19日 11:45CVE-2023-39120: Nodogsplash – Directory Traversal
漏洞标题 CVE-2023-39120: Nodogsplash - Directory Traversal 漏洞描述 Nodogsplash product was affected by a directory traversal vulnerability that also impacted the OpenWrt product. ...
2023年9月18日 22:25CVE-2022-0660: Microweber <1.2.11 - Information Disclosure
漏洞标题 CVE-2022-0660: Microweber <1.2.11 - Information Disclosure 漏洞描述 Microweber before 1.2.11 is susceptible to information disclosure. An error message is generated in ...
2022年2月9日 07:49CVE-2023-30777: Advanced Custom Fields < 6.1.6 - Cross-Site Scripting
漏洞标题 CVE-2023-30777: Advanced Custom Fields < 6.1.6 - Cross-Site Scripting 漏洞描述 Advanced Custom Fields beofre 6.1.6 is susceptible to cross-site scripting via the post_s...
2023年8月19日 16:47
2026年9月28日 11:45
2026年9月27日 11:45
2026年9月26日 11:45
2026年9月25日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

