
最新发布第689页

CVE-2024-35286: Mitel MiCollab <= 9.8.0.33 - SQL Injection
漏洞标题 CVE-2024-35286: Mitel MiCollab <= 9.8.0.33 - SQL Injection 漏洞描述 A vulnerability in NuPoint Messenger (NPM) of Mitel MiCollab through 9.8.0.33 allows an unauthentica...
 2024年1月25日 12:56
CVE-2023-34928: H3C Magic B1STV100R012 RCE
漏洞标题 CVE-2023-34928: H3C Magic B1STV100R012 RCE 漏洞描述 H3C Magic 是中国新华三(H3C)公司的一款无线路由器。 H3C Magic B1STV100R012版本存在安全漏洞。攻击者利用该漏洞可以进行命...
2023年6月14日 16:18CVE-2020-2733: JD Edwards EnterpriseOne Tools 9.2 – Information Disclosure
漏洞标题 CVE-2020-2733: JD Edwards EnterpriseOne Tools 9.2 - Information Disclosure 漏洞描述 JD Edwards EnterpriseOne Tools 9.2 is susceptible to information disclosure via the Mon...
2020年2月6日 23:11CVE-2010-2918: Joomla! Component Visites 1.1 – MosConfig_absolute_path Remote File Inclusion
漏洞标题 CVE-2010-2918: Joomla! Component Visites 1.1 - MosConfig_absolute_path Remote File Inclusion 漏洞描述 A PHP remote file inclusion vulnerability in core/include/myMailer.cl...
2010年12月7日 21:14CVE-2020-16139: Cisco Unified IP Conference Station 7937G – Denial-of-Service
漏洞标题 CVE-2020-16139: Cisco Unified IP Conference Station 7937G - Denial-of-Service 漏洞描述 Cisco Unified IP Conference Station 7937G 1-4-4-0 through 1-4-5-7 allows attackers t...
2020年12月30日 19:16CirCarLifeScada停车场自动化管理系统log-信息泄漏(CVE-2018-12634)
漏洞标题 CirCarLifeScada停车场自动化管理系统log-信息泄漏(CVE-2018-12634) 漏洞描述 【漏洞对象】Circontrol CirCarLife Scada 【漏洞描述】 Circontrol CirCarLifeScada是西班牙Circontrol...
2018年8月6日 09:36CVE-2021-35250: SolarWinds Serv-U 15.3 – Directory Traversal
漏洞标题 CVE-2021-35250: SolarWinds Serv-U 15.3 - Directory Traversal 漏洞描述 SolarWinds Serv-U 15.3 is susceptible to local file inclusion, which may allow an attacker access to ...
2021年8月23日 05:39CVE-2022-40734: UniSharp aka Laravel Filemanager v2.5.1 – Directory Traversal
漏洞标题 CVE-2022-40734: UniSharp aka Laravel Filemanager v2.5.1 - Directory Traversal 漏洞描述 UniSharp laravel-filemanager (aka Laravel Filemanager) through 2.5.1 allows download...
2022年3月17日 22:07CVE-2021-24946: WordPress Modern Events Calendar <6.1.5 - Blind SQL Injection
漏洞标题 CVE-2021-24946: WordPress Modern Events Calendar <6.1.5 - Blind SQL Injection 漏洞描述 WordPress Modern Events Calendar plugin before 6.1.5 is susceptible to blind SQL ...
2021年1月25日 11:46
欧盟数据主管命令欧洲刑警组织删除与犯罪无关的个人数据
根据欧盟数据保护监管机构EDPS于1月10日发布的新闻稿,EDPS已于一周前下令欧洲刑警组织删除与犯罪活动没有明确关联的个人的数据,以减少对公民个人权力和自由的侵犯。 此前,欧洲刑警组织...
2022年3月10日 23:39CVE-2022-0949: WordPress Stop Bad Bots <6.930 - SQL Injection
漏洞标题 CVE-2022-0949: WordPress Stop Bad Bots <6.930 - SQL Injection 漏洞描述 WordPress Stop Bad Bots plugin before 6.930 contains a SQL injection vulnerability. The plugin do...
2022年7月15日 07:22CVE-2019-9733: JFrog Artifactory 6.7.3 – Admin Login Bypass
漏洞标题 CVE-2019-9733: JFrog Artifactory 6.7.3 - Admin Login Bypass 漏洞描述 JFrog Artifactory 6.7.3 is vulnerable to an admin login bypass issue because by default the access-adm...
2019年6月9日 02:17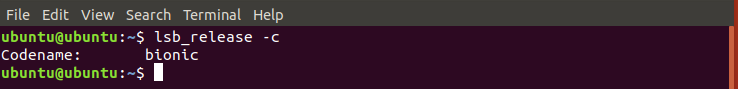
Ubuntu18.04更改apt源为阿里云源的详细过程_Linux
目录前言:Ubuntu18.04更改apt源为阿里云源ubuntu sudo update与upgrade的作用及区别总结前言: 看见Ubuntu新出了18.04版本感觉不错,装一个玩玩,虽然有很多教程可以参考,但我也给出一个不是...
2022年6月14日 23:03CVE-2017-17451: WordPress Mailster <=1.5.4 - Cross-Site Scripting
漏洞标题 CVE-2017-17451: WordPress Mailster <=1.5.4 - Cross-Site Scripting 漏洞描述 WordPress Mailster 1.5.4 and before contains a cross-site scripting vulnerability in the unsu...
2017年7月2日 22:59CVE-2020-14750: Oracle WebLogic Server – Remote Command Execution
漏洞标题 CVE-2020-14750: Oracle WebLogic Server - Remote Command Execution 漏洞描述 Oracle WebLogic Server 10.3.6.0.0, 12.1.3.0.0, 12.2.1.3.0, 12.2.1.4.0 and 14.1.1.0.0 is suscepti...
2020年3月22日 03:33CVE-2017-17731: DedeCMS 5.7 – SQL Injection
漏洞标题 CVE-2017-17731: DedeCMS 5.7 - SQL Injection 漏洞描述 DedeCMS through 5.7 has SQL Injection via the $_FILES superglobal to plus/recommend.php. PoC代码
2017年10月27日 11:33
2026年10月18日 11:45
2026年10月18日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

