
最新发布第691页

(CVE-2022-0954) Microweber 权限控制不当漏洞
漏洞标题 (CVE-2022-0954) Microweber 权限控制不当漏洞 漏洞描述 (CVE-2022-0954) Microweber 权限控制不当漏洞 PoC代码 暂无
 2022年10月10日 02:09
CVE-2021-24436: WordPress W3 Total Cache <2.1.4 - Cross-Site Scripting
漏洞标题 CVE-2021-24436: WordPress W3 Total Cache <2.1.4 - Cross-Site Scripting 漏洞描述 WordPress W3 Total Cache plugin before 2.1.4 is susceptible to cross-site scripting with...
2021年6月22日 12:33CVE-2011-3600: Apache OFBiz – XML External Entity Injection
漏洞标题 CVE-2011-3600: Apache OFBiz - XML External Entity Injection 漏洞描述 The /webtools/control/xmlrpc endpoint in OFBiz XML-RPC event handler is exposed to External Entity Inj...
2011年9月4日 20:02
如何提升Idea启动速度与Tomcat日志乱码问题_Tomcat
这篇文章主要介绍了提升Idea启动速度与Tomcat日志乱码问题,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 目录前言Idea启动速度Tomcat日志乱码前...
2022年8月20日 21:53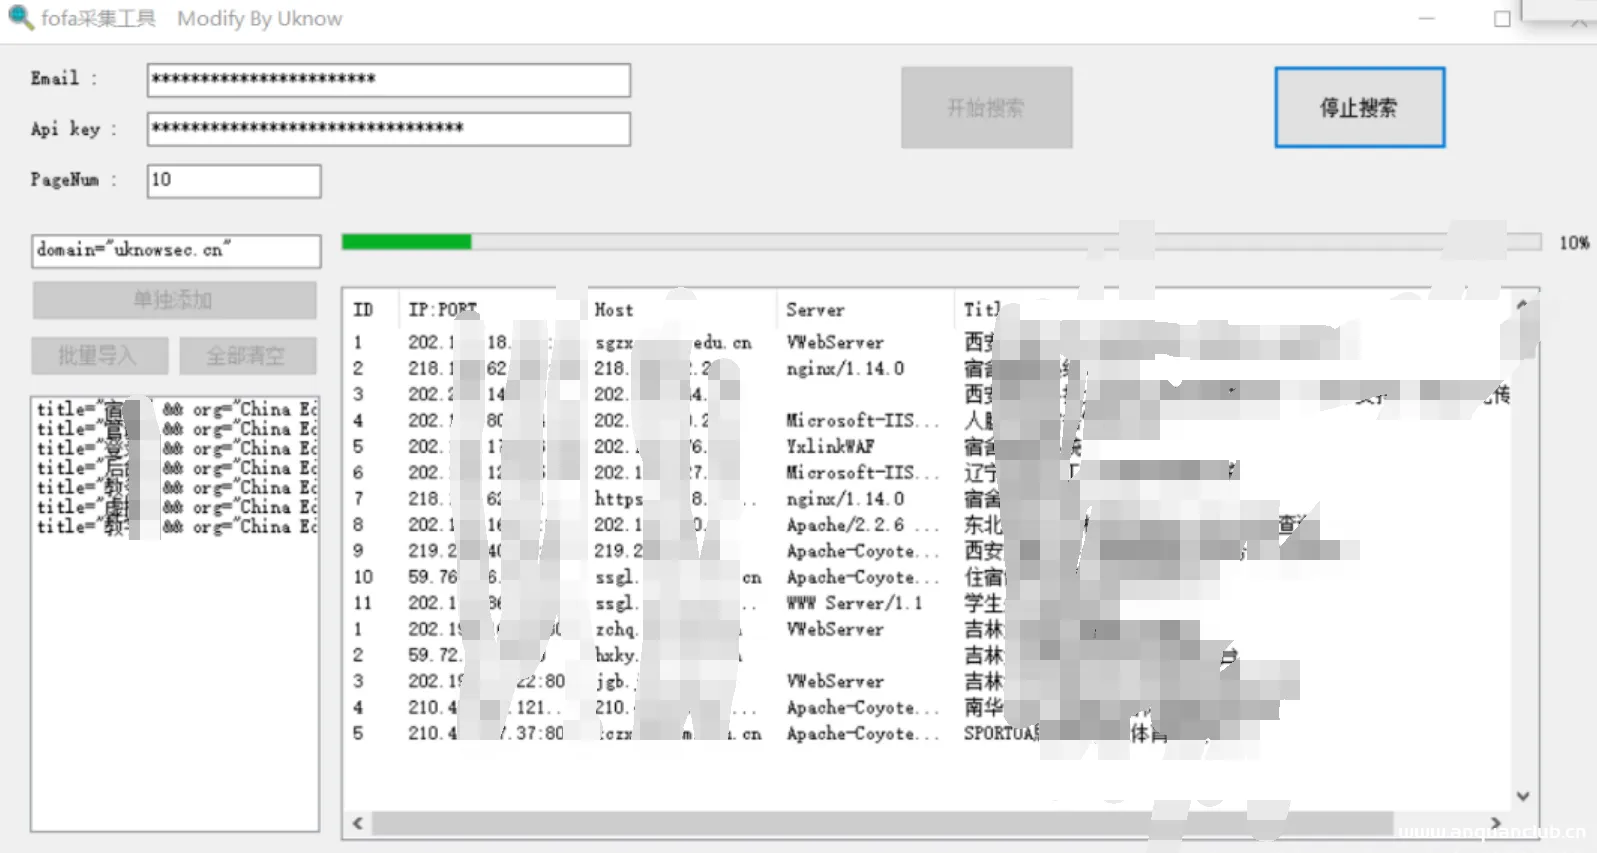
自动化批量挖掘漏洞(edu)
本文摘抄自大佬:Y7ii的优秀文章原文地址:http://blog.csdn.net/m0_46736332/article/details/118888256感谢大佬辛苦劳作,分享不易,记得打开CSDN关注Y7ii,期待大佬新作。 自动化批量挖漏洞 ...

 2023年3月29日 11:41
CVE-2017-1000029: Oracle GlassFish Server Open Source Edition 3.0.1 – Local File Inclusion
漏洞标题 CVE-2017-1000029: Oracle GlassFish Server Open Source Edition 3.0.1 - Local File Inclusion 漏洞描述 Oracle GlassFish Server Open Source Edition 3.0.1 (build 22) is vulnera...
2017年8月10日 10:17CVE-2024-25852: Linksys RE7000 – Command Injection
漏洞标题 CVE-2024-25852: Linksys RE7000 - Command Injection 漏洞描述 Linksys RE7000 v2.0.9, v2.0.11, and v2.0.15 have a command execution vulnerability in the "AccessControlLi...
2024年9月17日 09:14CVE-2016-15043: WP Mobile Detector <= 3.5 - Unrestricted File Upload
漏洞标题 CVE-2016-15043: WP Mobile Detector <= 3.5 - Unrestricted File Upload 漏洞描述 WP Mobile Detector plugin for WordPress <= 3.5 contains an unrestricted file upload vul...
2016年5月4日 07:49
越权测试小技巧
越权测试小技巧 /v2/user/1234 ---> 401 Unauthorized 绕过小技巧 大写绕过 /v2/USER/1234 ---> 200 OK 添加json后缀绕过 /v2/user/1234.json ----> 200 OK 路径穿越绕过 /v2/user/111...
2022年3月10日 23:37CVE-2022-24260: VoipMonitor – Pre-Auth SQL Injection
漏洞标题 CVE-2022-24260: VoipMonitor - Pre-Auth SQL Injection 漏洞描述 A SQL injection vulnerability in Voipmonitor GUI before v24.96 allows attackers to escalate privileges to the...
2022年10月5日 06:41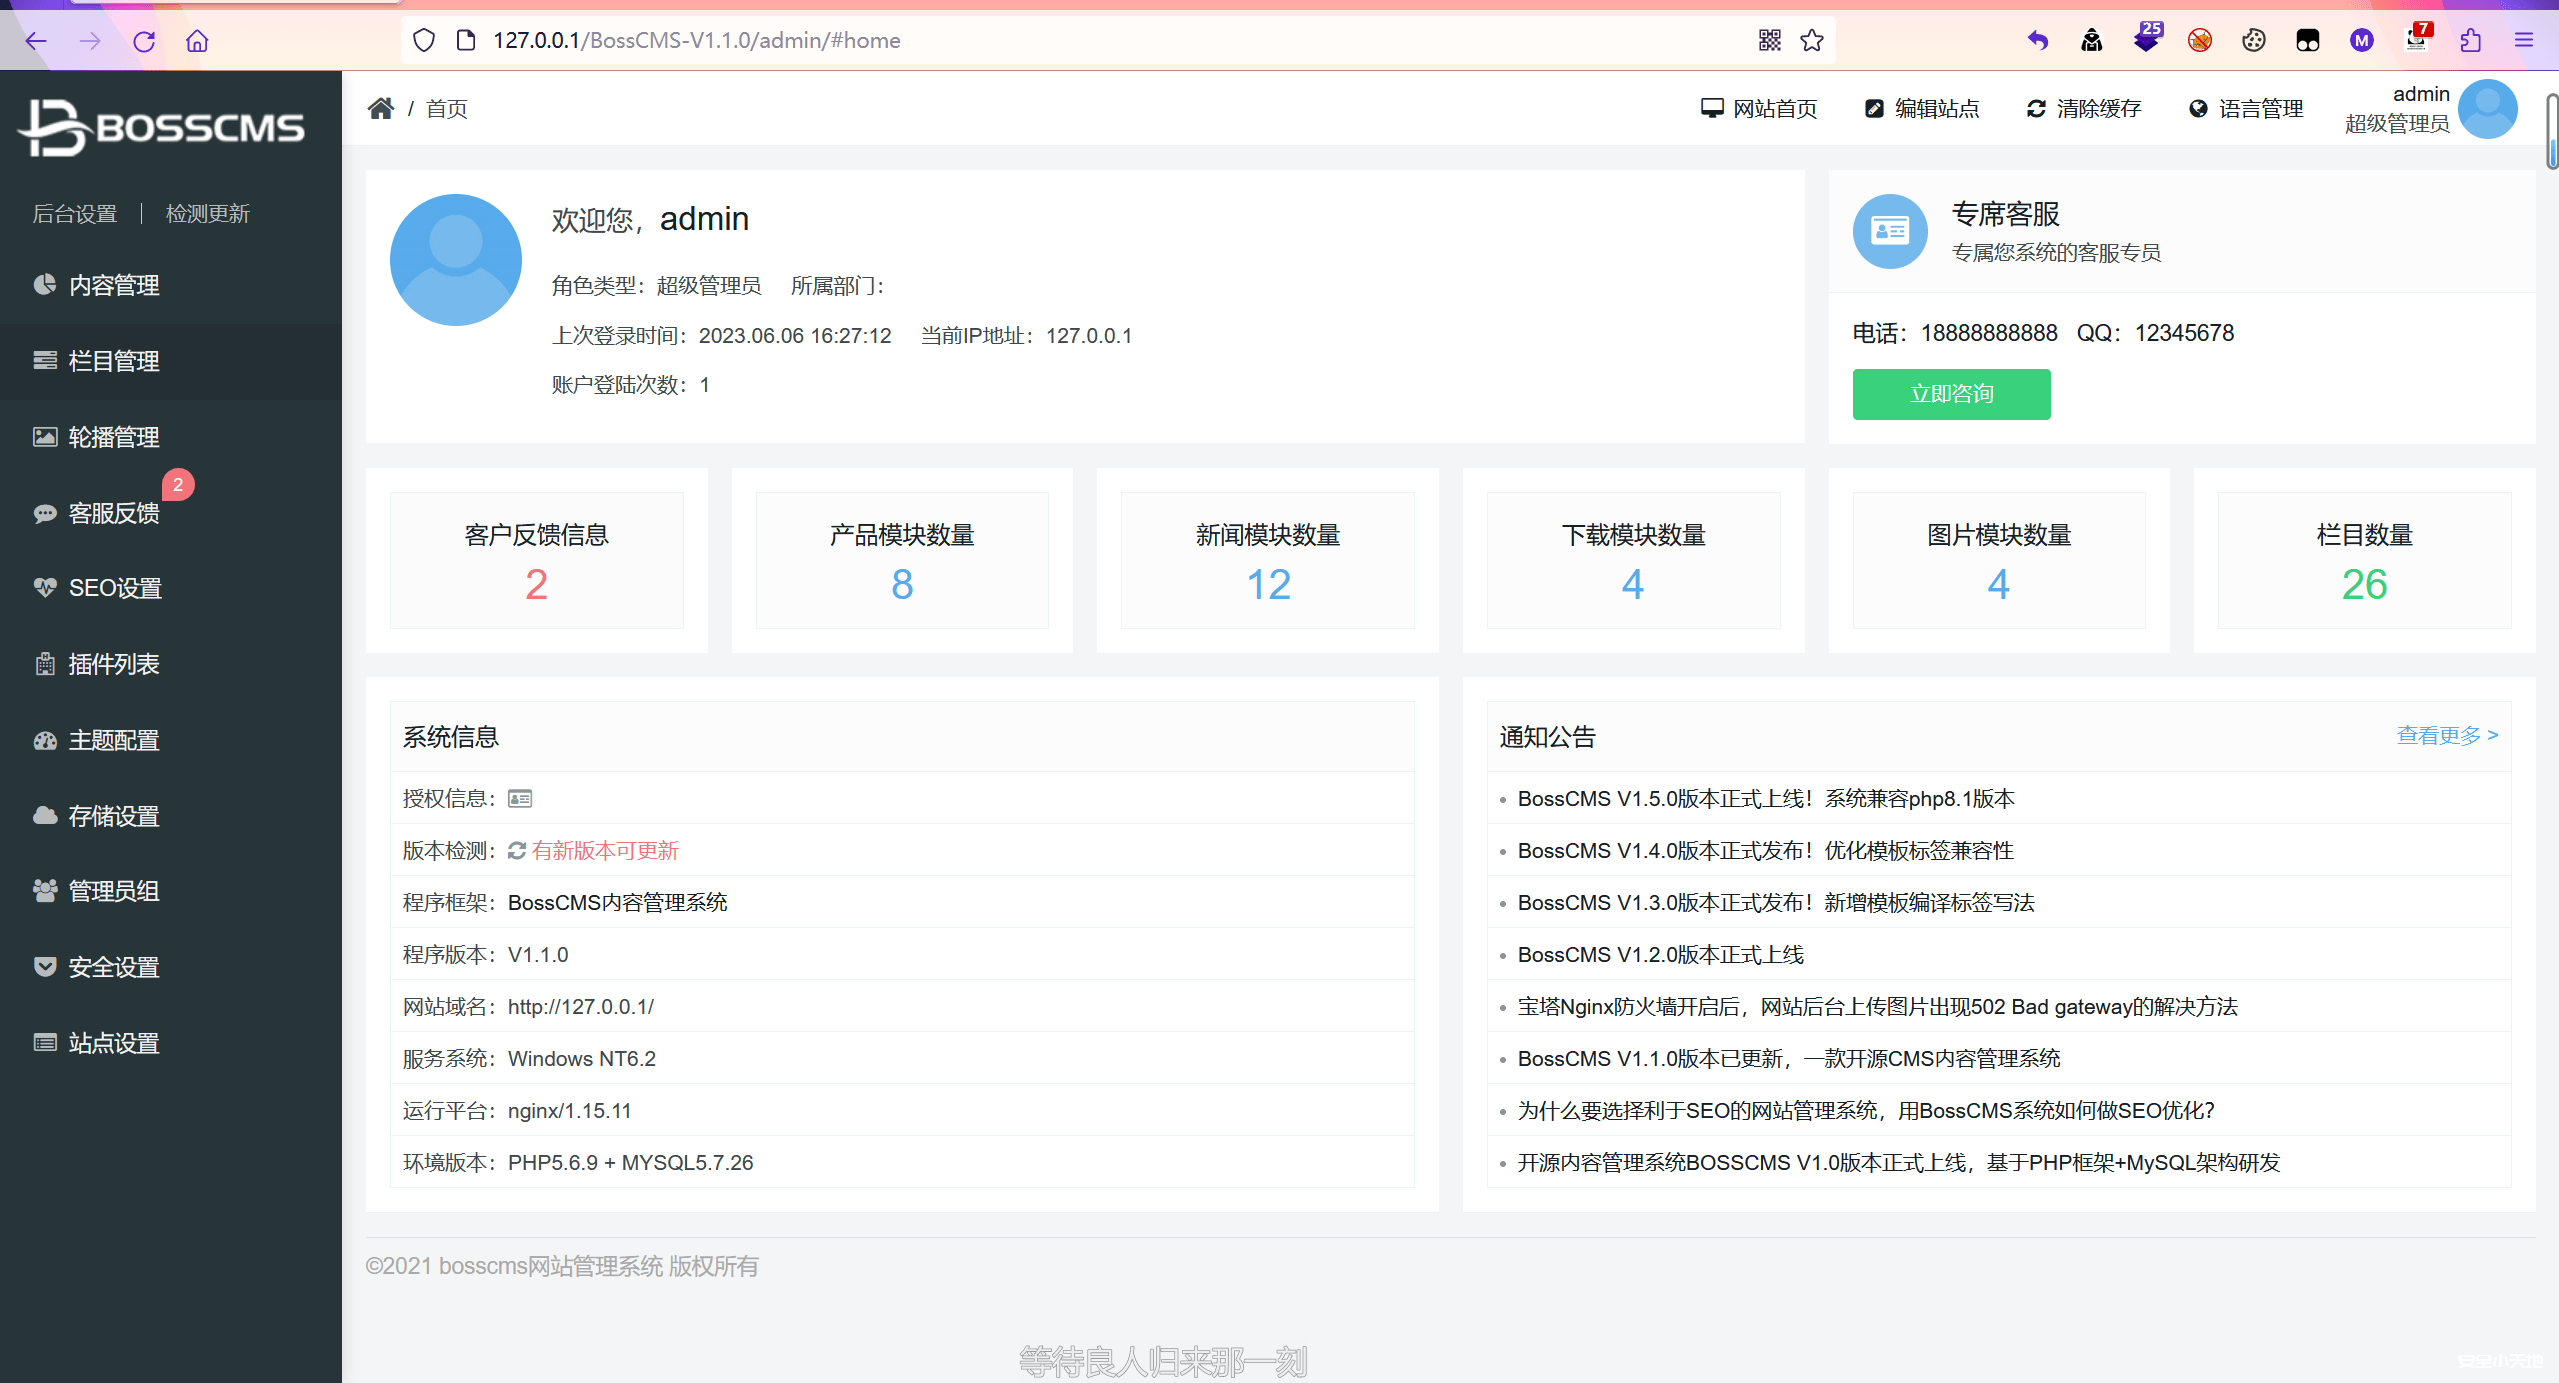
【代码审计】BossCMS1.0存在未授权访问漏洞
前言 BossCMS是温州互引信息技术有限公司开发的一款基于自主研发PHP框架MySQL架构的内容管理系统。 编号:CNVD-2022-04803 漏洞复现 下载版本1.0,安装完成如下: 根据漏洞名称我们知道,未授权...
2023年6月6日 17:20CVE-2020-9344: Jira Subversion ALM for Enterprise <8.8.2 - Cross-Site Scripting
漏洞标题 CVE-2020-9344: Jira Subversion ALM for Enterprise <8.8.2 - Cross-Site Scripting 漏洞描述 Jira Subversion ALM for Enterprise before 8.8.2 contains a cross-site scripting...
2020年11月14日 15:27Apache OFBiz CVE-2024-38856 未授权代码执行漏洞
漏洞标题 Apache OFBiz CVE-2024-38856 未授权代码执行漏洞 漏洞描述 Apache OFBiz存在未授权代码执行漏洞,该漏洞是由于ProgramExport接口对用户的权限校验不当导致的。 PoC代码 暂无
2024年10月26日 08:20CVE-2018-1000600: Jenkins GitHub Plugin <=1.29.1 - Server-Side Request Forgery
漏洞标题 CVE-2018-1000600: Jenkins GitHub Plugin <=1.29.1 - Server-Side Request Forgery 漏洞描述 Jenkins GitHub Plugin 1.29.1 and earlier is susceptible to server-side request f...
2018年2月18日 11:09CVE-2023-36844: Juniper Devices – Remote Code Execution
漏洞标题 CVE-2023-36844: Juniper Devices - Remote Code Execution 漏洞描述 Multiple cves in Juniper Network (CVE-2023-36844|CVE-2023-36845|CVE-2023-36846|CVE-2023-36847).A PHP Exter...
2023年3月3日 11:00CVE-2023-2256: WordPress Product Addons & Fields for WooCommerce < 32.0.7 - Cross-Site Scripting
漏洞标题 CVE-2023-2256: WordPress Product Addons & Fields for WooCommerce < 32.0.7 - Cross-Site Scripting 漏洞描述 The Product Addons & Fields for WooCommerce WordPress ...
2023年12月16日 22:58
2026年11月8日 11:45
2026年11月7日 11:45
2026年11月6日 11:45
2026年11月5日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

