
最新发布第691页

CVE-2021-31602: Hitachi Vantara Pentaho/Business Intelligence Server – Authentication Bypass
漏洞标题 CVE-2021-31602: Hitachi Vantara Pentaho/Business Intelligence Server - Authentication Bypass 漏洞描述 Hitachi Vantara Pentaho through 9.1 and Pentaho Business Intelligence...
 2021年6月17日 15:13
CVE-2023-4112: PHPJabbers Shuttle Booking Software 1.0 – Cross Site Scripting
漏洞标题 CVE-2023-4112: PHPJabbers Shuttle Booking Software 1.0 - Cross Site Scripting 漏洞描述 The attacker can send to victim a link containing a malicious URL in an email or ins...
2023年7月7日 00:38CVE-2017-18505: BestWebSoft’s Twitter < 2.55 - Cross-Site Scripting
漏洞标题 CVE-2017-18505: BestWebSoft's Twitter < 2.55 - Cross-Site Scripting 漏洞描述 The twitter-plugin plugin before 2.55 for WordPress has XSS. PoC代码
2017年12月12日 12:09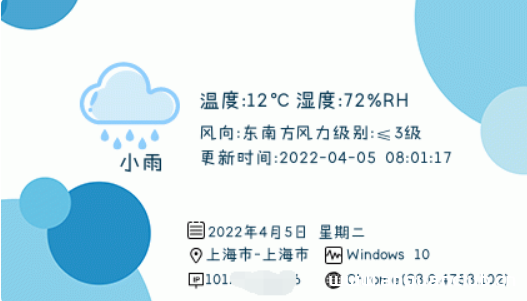
为你的网站添加一个帅气的IP签名档吧 – 教程附源码
先来看看效果吧 远程调用只需要将下面代码加到想显示的地方就行!比如网站侧栏/弹窗提醒等等... <img src='https://b.encenc.com/tools/ip_picture/' alt='' width='428' height='250' />

 2022年6月2日 18:16
Alibaba Nacos derby 未授权访问(CVE-2021-29442)
漏洞标题 Alibaba Nacos derby 未授权访问(CVE-2021-29442) 漏洞描述 Alibaba Nacos /derby端点不受保护,未经身份验证的用户可以公开访问。导致可以执行任意的select查询语句,可以查询数据库用...
2021年5月25日 09:09CVE-2023-38952: ZKTeco BioTime <= 9.0.1 - Privilege Escalation
漏洞标题 CVE-2023-38952: ZKTeco BioTime <= 9.0.1 - Privilege Escalation 漏洞描述 BioTime default employee credentials (password 123456) allow login. Sessions are not role-valida...
2023年12月15日 09:41CVE-2022-28666: Custom Product Tabs for WooCommerce < 1.7.8 - Unauthenticated Toggle Content Setting Update
漏洞标题 CVE-2022-28666: Custom Product Tabs for WooCommerce < 1.7.8 - Unauthenticated Toggle Content Setting Update 漏洞描述 YIKES Inc. Custom Product Tabs for WooCommerce plug...
2022年11月30日 20:57CVE-2023-30256: Webkul QloApps 1.5.2 – Cross-site Scripting
漏洞标题 CVE-2023-30256: Webkul QloApps 1.5.2 - Cross-site Scripting 漏洞描述 Cross Site Scripting vulnerability found in Webkil QloApps v.1.5.2 allows a remote attacker to obtain ...
2023年6月29日 15:20CVE-2025-24354: Imgproxy < 3.27.2 - Server-Side Request Forgery (SSRF)
漏洞标题 CVE-2025-24354: Imgproxy < 3.27.2 - Server-Side Request Forgery (SSRF) 漏洞描述 imgproxy contains an issue caused by not blocking the 0.0.0.0 address even when IMGPROXY...
2025年12月2日 00:20CVE-2017-7921: Hikvision – Authentication Bypass
漏洞标题 CVE-2017-7921: Hikvision - Authentication Bypass 漏洞描述 Hikvision DS-2CD2xx2F-I Series V5.2.0 build 140721 to V5.4.0 build 160530, DS-2CD2xx0F-I Series V5.2.0 build 1407...
2017年12月14日 04:57CVE-2006-2173: FileZilla FTP Server 2.2.22 – Buffer Overflow
漏洞标题 CVE-2006-2173: FileZilla FTP Server 2.2.22 - Buffer Overflow 漏洞描述 FileZilla FTP Server version 2.2.22 contains a buffer overflow vulnerability that allows remote authe...
2006年6月21日 12:33CVE-2016-3510: Oracle WebLogic Server Java Object Deserialization – Remote Code Execution
漏洞标题 CVE-2016-3510: Oracle WebLogic Server Java Object Deserialization - Remote Code Execution 漏洞描述 Unspecified vulnerability in the Oracle WebLogic Server component in Ora...
2016年8月21日 21:29CVE-2024-21644: pyLoad Flask Config – Access Control
漏洞标题 CVE-2024-21644: pyLoad Flask Config - Access Control 漏洞描述 pyLoad is the free and open-source Download Manager written in pure Python. Any unauthenticated user can brow...
2024年11月6日 03:01CVE-2019-18818: strapi CMS <3.0.0-beta.17.5 - Admin Password Reset
漏洞标题 CVE-2019-18818: strapi CMS <3.0.0-beta.17.5 - Admin Password Reset 漏洞描述 strapi CMS before 3.0.0-beta.17.5 allows admin password resets because it mishandles passwor...
2019年6月17日 08:58CVE-2021-24219: All Thrive Themes and Plugins – Unauthenticated Option Update
漏洞标题 CVE-2021-24219: All Thrive Themes and Plugins - Unauthenticated Option Update 漏洞描述 The Thrive Optimize WordPress plugin before 1.4.13.3, Thrive Comments WordPress plug...
2021年6月16日 12:13CVE-2023-5360: WordPress Royal Elementor Addons Plugin <= 1.3.78 - Arbitrary File Upload
漏洞标题 CVE-2023-5360: WordPress Royal Elementor Addons Plugin <= 1.3.78 - Arbitrary File Upload 漏洞描述 Arbitrary File Upload vulnerability in WordPress Royal Elementor Addon...
2023年12月8日 07:43
2026年11月6日 11:45
2026年11月5日 11:45
2026年11月4日 11:45
2026年11月3日 11:46
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

