
最新发布第701页
k3d入门指南之在Docker中运行K3s的详细教程_docker
在本文中,我们将简单了解k3d,这是一款可让您在安装了Docker的任何地方运行一次性Kubernetes集群的工具,此外在本文中我们还将探讨在使用k3d中可能会出现的一切问题,感兴趣的朋友跟随小编一起...
 2022年6月15日 09:45

CVE-2023-38501: CopyParty v1.8.6 – Cross Site Scripting
漏洞标题 CVE-2023-38501: CopyParty v1.8.6 - Cross Site Scripting 漏洞描述 Copyparty is a portable file server. Versions prior to 1.8.6 are subject to a reflected cross-site scripti...
2023年10月2日 11:28CVE-2019-11253: Kubernetes API Server – YAML Parsing DoS (Billion Laughs)
漏洞标题 CVE-2019-11253: Kubernetes API Server - YAML Parsing DoS (Billion Laughs) 漏洞描述 The Kubernetes API server is vulnerable to a denial of service attack via YAML/JSON pars...
2019年6月24日 00:56
Jenkins+Docker持续集成的实现_docker
Jenkins是基于Java开发的一种持续集成工具,用于监控持续重复的工作,旨在提供一个开放易用的软件平台,使软件的持续集成变成可能。本文介绍了Jenkins Docker持续集成,分享给大家 目录 一、Jen...
2022年6月15日 09:45CVE-2023-27638: tshirtecommerce PrestaShop Module – SQL Injection
漏洞标题 CVE-2023-27638: tshirtecommerce PrestaShop Module - SQL Injection 漏洞描述 The tshirtecommerce module for PrestaShop is vulnerable to unauthenticated SQL injection via the...
2023年3月6日 09:00CVE-2024-30269: DataEase <= 2.4.1 - Sensitive Information Exposure
漏洞标题 CVE-2024-30269: DataEase <= 2.4.1 - Sensitive Information Exposure 漏洞描述 DataEase, an open source data visualization and analysis tool, has a database configuration ...
2024年9月22日 09:49CVE-2022-3805: Jeg Elementor Kit < 2.5.7 - Unauthenticated Settings Update
漏洞标题 CVE-2022-3805: Jeg Elementor Kit < 2.5.7 - Unauthenticated Settings Update 漏洞描述 The Jeg Elementor Kit plugin for WordPress is vulnerable to authorization bypass in ...
2022年11月29日 21:00CVE-2013-7240: WordPress Plugin Advanced Dewplayer 1.2 – Directory Traversal
漏洞标题 CVE-2013-7240: WordPress Plugin Advanced Dewplayer 1.2 - Directory Traversal 漏洞描述 A directory traversal vulnerability in download-file.php in the Advanced Dewplayer pl...
2013年10月2日 13:31CVE-2019-20210: WordPress CTHthemes – Cross-Site Scripting
漏洞标题 CVE-2019-20210: WordPress CTHthemes - Cross-Site Scripting 漏洞描述 WordPress CTHthemes CityBook before 2.3.4, TownHub before 1.0.6, and EasyBook before 1.2.2 themes conta...
2019年4月9日 02:40CVE-2025-2712: Yonyou UFIDA ERP-NC V5.0 – Cross-Site Scripting
漏洞标题 CVE-2025-2712: Yonyou UFIDA ERP-NC V5.0 - Cross-Site Scripting 漏洞描述 Yonyou UFIDA ERP-NC V5.0 is vulnerable to reflected cross-site scripting (XSS) via the langcode par...
2025年10月18日 14:32
bugbounty技巧聚合20210811
漏洞报告 HackerOne #1256371 PII data Leakage through hackerone reports #1145563 Tab nabbing in Hackerone inbox. Basecamp #1288898 Password reset link not expiring after changing pa...
2022年4月1日 18:36CVE-2014-8799: WordPress Plugin DukaPress 2.5.2 – Directory Traversal
漏洞标题 CVE-2014-8799: WordPress Plugin DukaPress 2.5.2 - Directory Traversal 漏洞描述 A directory traversal vulnerability in the dp_img_resize function in php/dp-functions.php in...
2014年4月30日 05:18Atlassian Confluence CVE-2023-22515 权限提升漏洞 (阶段1: 属性修改)
漏洞标题 Atlassian Confluence CVE-2023-22515 权限提升漏洞 (阶段1: 属性修改) 漏洞描述 Atlassian Confluence CVE-2023-22515 权限提升漏洞 (阶段1: 属性修改) 日期: 2024-02-07 | 影响软件:...
2023年8月10日 02:36CVE-2024-23897: Jenkins < 2.441 - Arbitrary File Read
漏洞标题 CVE-2024-23897: Jenkins < 2.441 - Arbitrary File Read 漏洞描述 Jenkins 2.441 and earlier, LTS 2.426.2 and earlier does not disable a feature of its CLI command parser t...
2024年2月28日 05:55Linux crontab 命令的使用_Linux
这篇文章主要介绍了Linux crontab 命令的使用,帮助大家更好的理解和学习Linux系统,感兴趣的朋友可以了解下 1.命令简介 contab(cron table) 命令被用管理用户的需要周期性执行的任务,与 Win...
2023年6月9日 20:06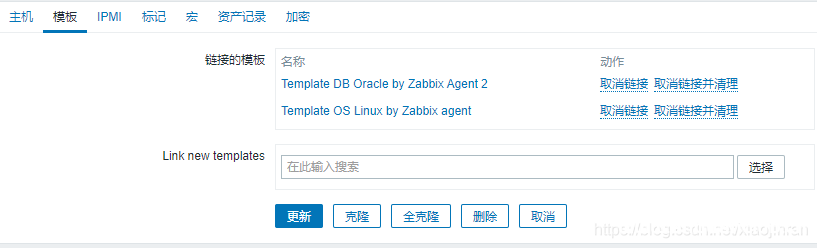
zabbix agent2 监控oracle数据库的方法_zabbix
这篇文章主要介绍了zabbix agent2 监控oracle数据库的方法,本文给大家介绍的非常详细,对大家的学习或工作具体一定的参考借鉴价值,需要的朋友可以参考下 概述 在zabbix5.0版本以上,新增了一个...
2022年6月15日 09:44
2026年10月18日 11:45
2026年10月18日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

