
最新发布第710页

CVE-2021-37538: PrestaShop SmartBlog <4.0.6 - SQL Injection
漏洞标题 CVE-2021-37538: PrestaShop SmartBlog <4.0.6 - SQL Injection 漏洞描述 PrestaShop SmartBlog by SmartDataSoft < 4.0.6 is vulnerable to a SQL injection vulnerability in ...
 2021年1月20日 06:06
CVE-2022-0434: WordPress Page Views Count <2.4.15 - SQL Injection
漏洞标题 CVE-2022-0434: WordPress Page Views Count <2.4.15 - SQL Injection 漏洞描述 WordPress Page Views Count plugin prior to 2.4.15 contains an unauthenticated SQL injection v...
2022年1月3日 02:54
一次任意密码重置漏洞挖洞剖析
前言: 之前参加一家企业SRC挖洞,正赶上厂商搞活动,秉着有活动我就参加,有漏洞我就捡的良好心态,就去看了一下该企业的一些资产,因为活动是按漏洞危害等级给奖励,所以找一些边缘资产参加活...
2022年3月10日 23:32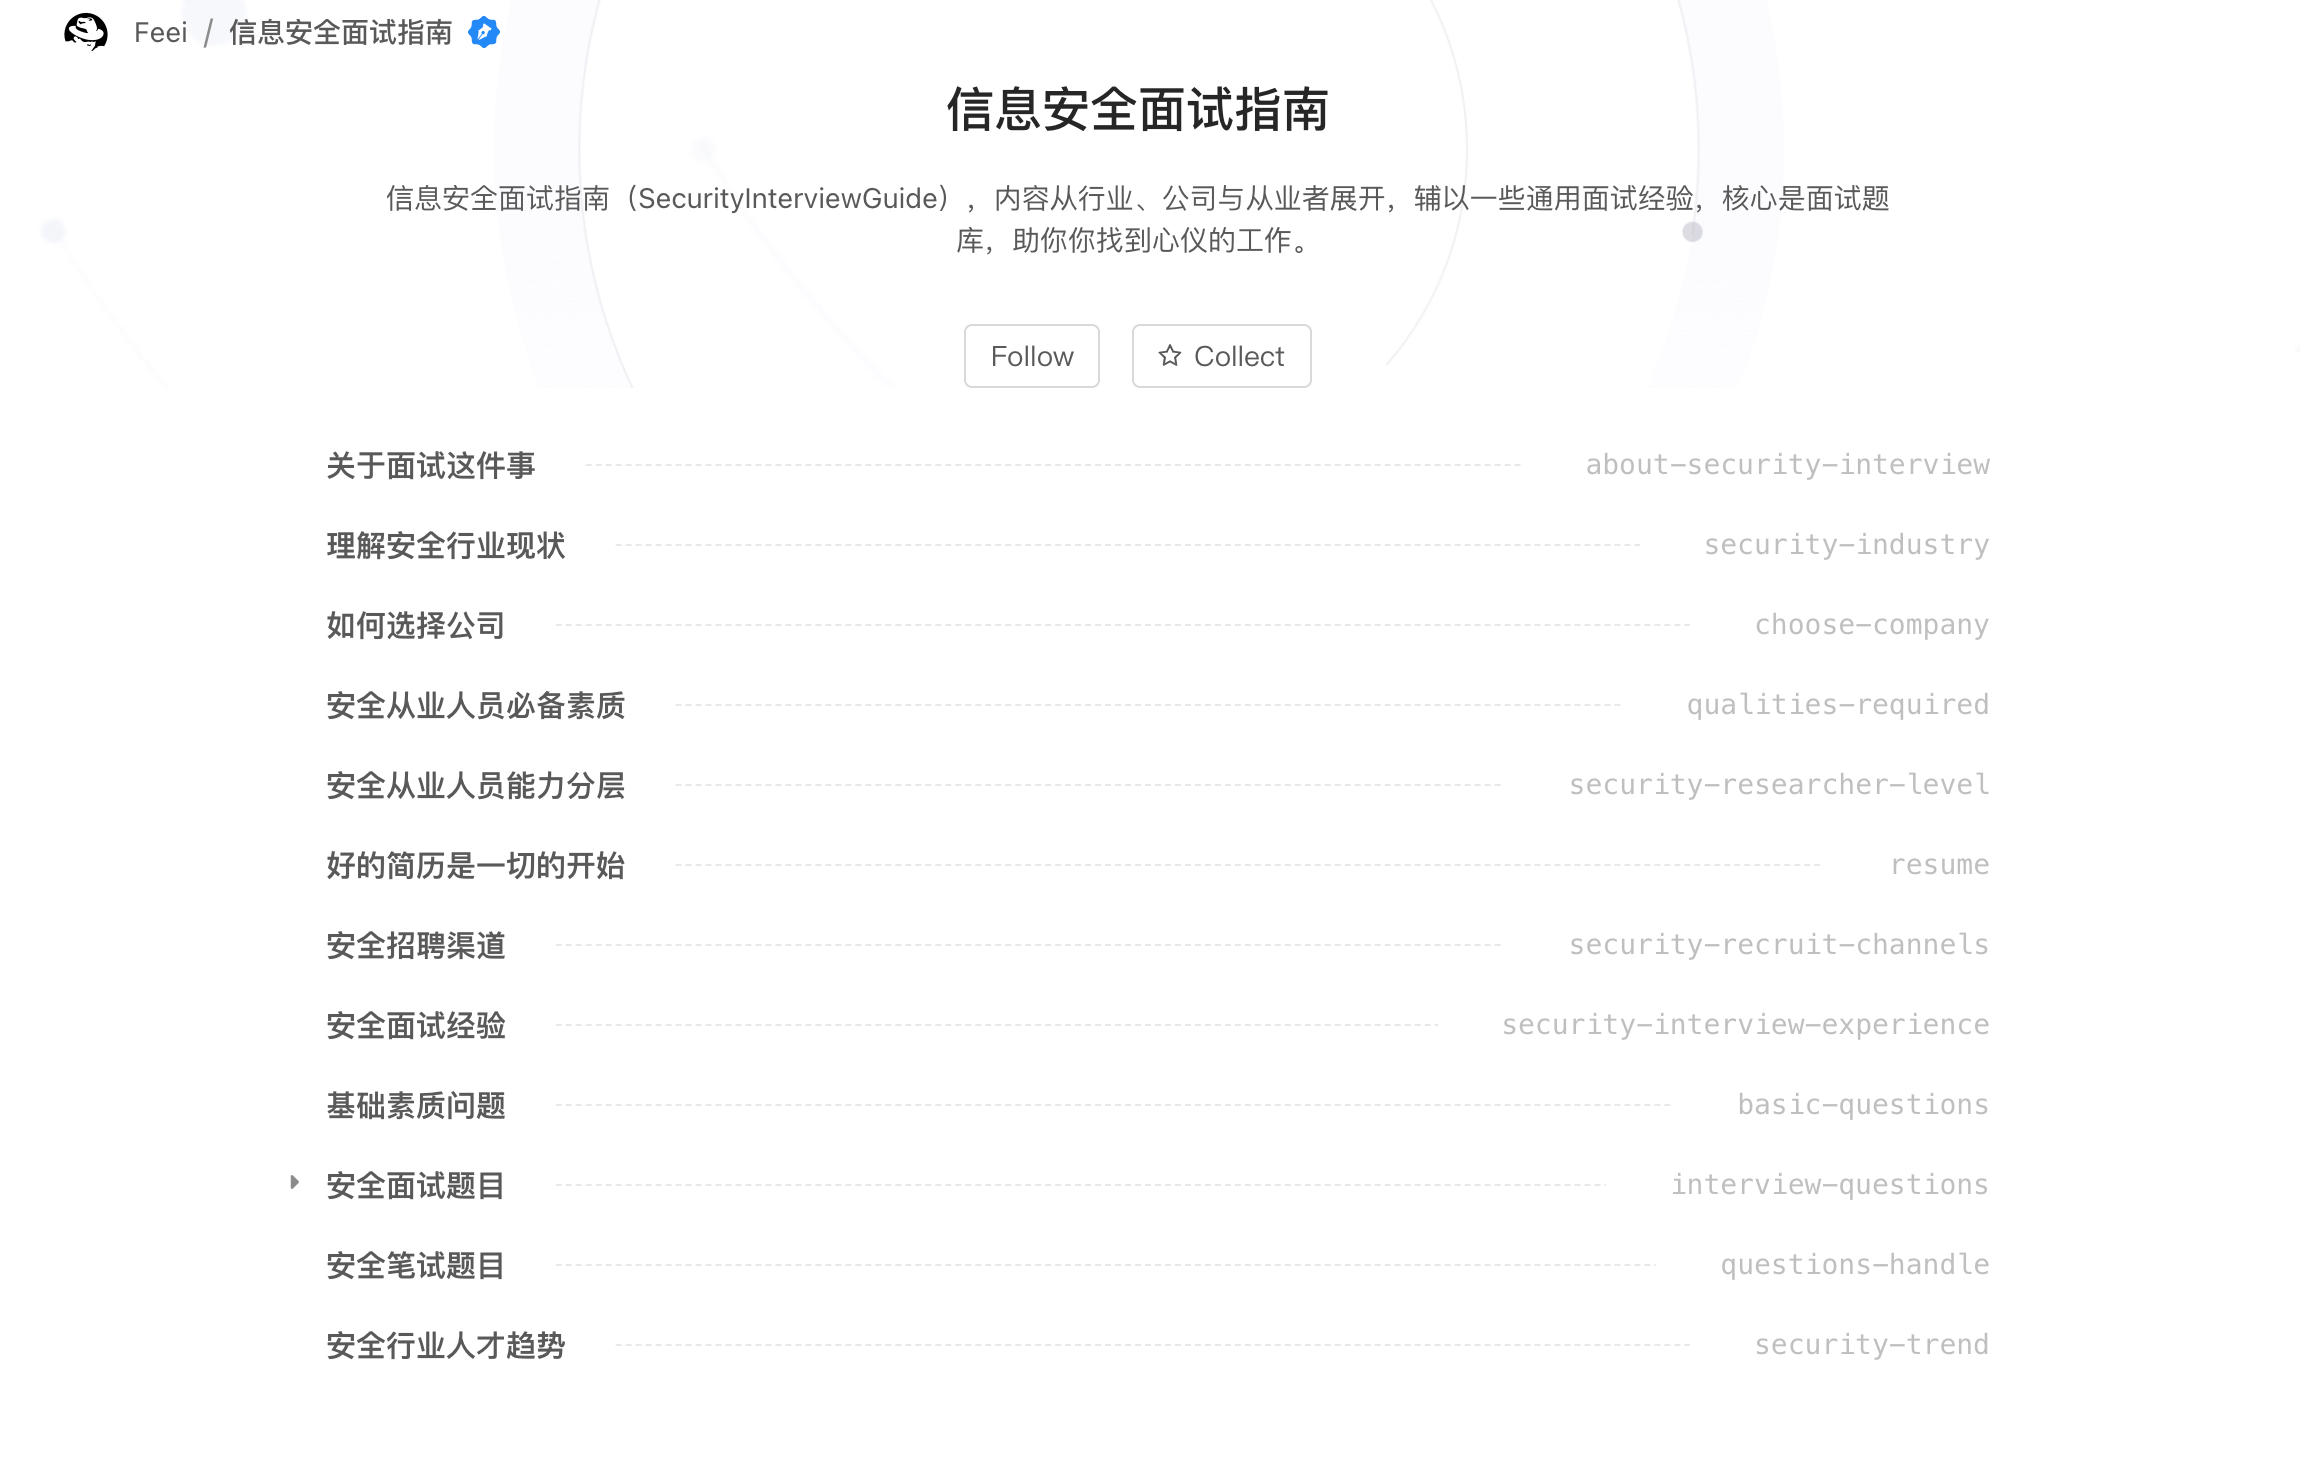
信息安全面试指南
地址: http://www.yuque.com/feei/sig 信息安全面试指南(SecurityInterviewGuide),内容从行业、公司与从业者展开,辅以一些通用面试经验,核心是面试题库,助你你找到心仪的工作。
2022年3月10日 23:38CVE-2010-5028: Joomla! Component JE Job 1.0 – Local File Inclusion
漏洞标题 CVE-2010-5028: Joomla! Component JE Job 1.0 - Local File Inclusion 漏洞描述 A SQL injection vulnerability in the JExtensions JE Job (com_jejob) component 1.0 for Joomla! a...
2010年12月20日 03:29
bugbounty技巧聚合20220107
漏洞报告 【MariaDB】Grafana LFI注入 http://hackerone.com/reports/1419213 挖洞技巧 CVE-2021-44515是 ManageEngine Desktop Central 中的身份验证绕过漏洞,可能导致远程代码执行。 http://...
2022年4月1日 18:36CVE-2022-28117: Navigate CMS 2.9.4 – Server-Side Request Forgery
漏洞标题 CVE-2022-28117: Navigate CMS 2.9.4 - Server-Side Request Forgery 漏洞描述 Navigate CMS 2.9.4 is susceptible to server-side request forgery via feed_parser class. This can ...
2022年5月1日 11:55CVE-2023-1454: Jeecg Boot QuerySql sql injection
漏洞标题 CVE-2023-1454: Jeecg Boot QuerySql sql injection 漏洞描述 JeecgBoot是一款基于BPM的低代码平台!前后端分离架构 SpringBoot 2.x,SpringCloud,Ant Design&Vue,Mybatis-plus...
2023年8月22日 14:07CVE-2021-24215: Controlled Admin Access WordPress Plugin <= 1.4.0 - Improper Access Control & Privilege Escalation
漏洞标题 CVE-2021-24215: Controlled Admin Access WordPress Plugin <= 1.4.0 - Improper Access Control & Privilege Escalation 漏洞描述 An Improper Access Control vulnerability...
2021年6月6日 16:05CVE-2019-7276: Optergy Proton/Enterprise – Unauthenticated RCE via Backdoor Console
漏洞标题 CVE-2019-7276: Optergy Proton/Enterprise - Unauthenticated RCE via Backdoor Console 漏洞描述 Optergy Proton/Enterprise devices allow Remote Root Code Execution via a Backd...
2019年6月10日 13:52CVE-2021-34622: WordPress ProfilePress <= 3.1.3 - Privilege Escalation
漏洞标题 CVE-2021-34622: WordPress ProfilePress <= 3.1.3 - Privilege Escalation 漏洞描述 ProfilePress plugin before 3.1.4 allows privilege escalation. Due to insufficient valida...
2021年1月23日 23:30CVE-2017-9805: Apache Struts2 S2-052 – Remote Code Execution
漏洞标题 CVE-2017-9805: Apache Struts2 S2-052 - Remote Code Execution 漏洞描述 The REST Plugin in Apache Struts 2.1.1 through 2.3.x before 2.3.34 and 2.5.x before 2.5.13 uses an XS...
2017年4月11日 00:12CVE-2023-45249: Acronis Cyber Infrastructure – Default Password
漏洞标题 CVE-2023-45249: Acronis Cyber Infrastructure - Default Password 漏洞描述 Acronis Cyber Infrastructure (ACI) before build 5.0.1-61, 5.1.1-71, 5.2.1-69, 5.3.1-53, and 5.4.4-...
2023年6月23日 00:31CVE-2015-8399: Atlassian Confluence configuration files read
漏洞标题 CVE-2015-8399: Atlassian Confluence configuration files read 漏洞描述 Atlassian Confluence before 5.9.1 allows remote attackers to read arbitrary files via a crafted reque...
2015年5月26日 01:31CVE-2017-3528: Oracle E-Business Suite 12.1.3/12.2.x – Open Redirect
漏洞标题 CVE-2017-3528: Oracle E-Business Suite 12.1.3/12.2.x - Open Redirect 漏洞描述 The Oracle Applications Framework component of Oracle E-Business Suite (subcomponent: Popup w...
2017年5月17日 12:28Academy LMS 6.2 CVE-2023-4974 SQL注入漏洞
漏洞标题 Academy LMS 6.2 CVE-2023-4974 SQL注入漏洞 漏洞描述 Academy LMS 6.2存在sql注入漏洞,该漏洞是由于tutor/filter接口对用户的请求验证不当导致的。 PoC代码 暂无
2023年2月23日 03:27
2026年10月18日 11:45
2026年10月18日 11:45
2026年10月17日 11:45
2026年10月16日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

