
最新发布第71页

CVE-2024-4340: sqlparse – Denial of Service
漏洞标题 CVE-2024-4340: sqlparse - Denial of Service 漏洞描述 Passing a heavily nested list to sqlparse.parse() leads to a Denial of Service due to RecursionError. PoC代码
 2024年6月23日 14:17

nginx 防盗链防爬虫配置详解_nginx
这篇文章主要介绍了nginx 防盗链防爬虫配置详解,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编来一起学习学习吧 新建配置配...
2023年4月14日 21:04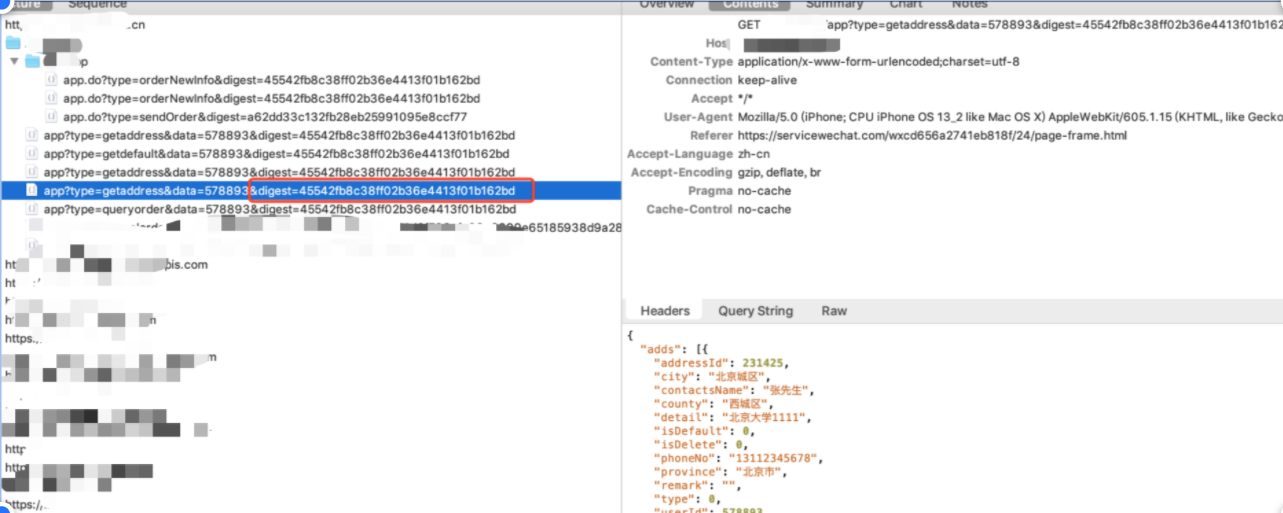
一次小程序端接口越权的分析
之前在挖一个src的时候,有一个资产是小程序 抓包如下 根据地址id查看收货地址 注意到请求里没有cookie,然后url里面这个digest字段比较奇怪,所有的接口都是根据这个参数鉴权的,一般不都应该...
2022年3月10日 23:34CVE-2010-0219: Apache Axis2 Default Login
漏洞标题 CVE-2010-0219: Apache Axis2 Default Login 漏洞描述 Apache Axis2, as used in dswsbobje.war in SAP BusinessObjects Enterprise XI 3.2, CA ARCserve D2D r15, and other products...
2010年1月23日 15:47CVE-2022-1020: WordPress WooCommerce <3.1.2 - Arbitrary Function Call
漏洞标题 CVE-2022-1020: WordPress WooCommerce <3.1.2 - Arbitrary Function Call 漏洞描述 WordPress WooCommerce plugin before 3.1.2 does not have authorisation and CSRF checks in ...
2022年4月5日 10:37CVE-2021-42887: TOTOLINK EX1200T 4.1.2cu.5215 – Authentication Bypass
漏洞标题 CVE-2021-42887: TOTOLINK EX1200T 4.1.2cu.5215 - Authentication Bypass 漏洞描述 TOTOLINK EX1200T 4.1.2cu.5215 is susceptible to authentication bypass. An attacker can bypas...
2021年12月1日 16:33CVE-2022-1057: WordPress Pricing Deals for WooCommerce <=2.0.2.02 - SQL Injection
漏洞标题 CVE-2022-1057: WordPress Pricing Deals for WooCommerce <=2.0.2.02 - SQL Injection 漏洞描述 WordPress Pricing Deals for WooCommerce plugin through 2.0.2.02 contains a SQ...
2022年1月16日 10:02CVE-2024-4841: LoLLMS WebUI – Subfolder Prediction via Path Traversal
漏洞标题 CVE-2024-4841: LoLLMS WebUI - Subfolder Prediction via Path Traversal 漏洞描述 A Path Traversal vulnerability exists in the parisneo/lollms-webui, specifically within the ...
2024年3月16日 21:23CVE-2022-26148: Grafana & Zabbix Integration – Credentials Disclosure
漏洞标题 CVE-2022-26148: Grafana & Zabbix Integration - Credentials Disclosure 漏洞描述 Grafana through 7.3.4, when integrated with Zabbix, contains a credential disclosure vul...
2022年12月16日 05:57Apache Flink 任意文件写入(CVE-2020-17518)
漏洞标题 Apache Flink 任意文件写入(CVE-2020-17518) 漏洞描述 【漏洞对象】Apache Flink 【涉及版本】Flink1.5.1-1.11.2 \【漏洞描述】ApacheFlink是一个开源的流处理框架,具有强大的流处理...
2020年5月14日 05:48Adobe ColdFusion /filemanager/iedit.cfc 未授权访问漏洞 (CVE-2023-26360)
漏洞标题 Adobe ColdFusion /filemanager/iedit.cfc 未授权访问漏洞 (CVE-2023-26360) 漏洞描述 Adobe ColdFusion是一种用于构建动态Web应用程序的服务器端编程语言和开发平台。ColdFusion的...
2023年12月4日 04:14CVE-2018-11709: WordPress wpForo Forum <= 1.4.11 - Cross-Site Scripting
漏洞标题 CVE-2018-11709: WordPress wpForo Forum <= 1.4.11 - Cross-Site Scripting 漏洞描述 WordPress wpForo Forum plugin before 1.4.12 for WordPress allows unauthenticated reflec...
2018年9月13日 12:25CVE-2024-30269: DataEase <= 2.4.1 - Sensitive Information Exposure
漏洞标题 CVE-2024-30269: DataEase <= 2.4.1 - Sensitive Information Exposure 漏洞描述 DataEase, an open source data visualization and analysis tool, has a database configuration ...
2024年11月10日 19:04CVE-2022-1580: Site Offline WP Plugin < 1.5.3 - Authorization Bypass
漏洞标题 CVE-2022-1580: Site Offline WP Plugin < 1.5.3 - Authorization Bypass 漏洞描述 The plugin prevents users from accessing a website but does not do so if the URL contained...
2022年5月9日 12:21CVE-2017-12794: Django Debug Page – Cross-Site Scripting
漏洞标题 CVE-2017-12794: Django Debug Page - Cross-Site Scripting 漏洞描述 Django 1.10.x before 1.10.8 and 1.11.x before 1.11.5 has HTML autoescaping disabled in a portion of the t...
2017年4月19日 14:14CVE-2018-7251: Anchor CMS 0.12.3 – Error Log Exposure
漏洞标题 CVE-2018-7251: Anchor CMS 0.12.3 - Error Log Exposure 漏洞描述 Anchor CMS 0.12.3 is susceptible to an error log exposure vulnerability due to an issue in config/error.php....
2018年12月10日 09:47
2026年11月12日 11:45
2026年11月11日 11:45
2026年11月10日 11:45
2026年11月9日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

