
最新发布第721页

CVE-2021-38540: Apache Airflow – Unauthenticated Variable Import
漏洞标题 CVE-2021-38540: Apache Airflow - Unauthenticated Variable Import 漏洞描述 Apache Airflow Airflow >=2.0.0 and <2.1.3 does not protect the variable import endpoint whi...
 2021年6月5日 12:26
CVE-2017-18492: Contact Form to DB by BestWebSoft < 1.5.7 - Cross-Site Scripting
漏洞标题 CVE-2017-18492: Contact Form to DB by BestWebSoft < 1.5.7 - Cross-Site Scripting 漏洞描述 The contact-form-to-db plugin before 1.5.7 for WordPress has multiple XSS issu...
2017年2月11日 20:01CVE-2018-12296: Seagate NAS OS 4.3.15.1 – Server Information Disclosure
漏洞标题 CVE-2018-12296: Seagate NAS OS 4.3.15.1 - Server Information Disclosure 漏洞描述 Seagate NAS OS version 4.3.15.1 has insufficient access control which allows attackers to ...
2018年9月11日 04:06Cuppacms 本地文件包含漏洞(CVE-2022-34121)
漏洞标题 Cuppacms 本地文件包含漏洞(CVE-2022-34121) 漏洞描述 Cuppacms 本地文件包含漏洞(CVE-2022-34121) PoC代码 暂无
2022年7月28日 09:22CVE-2019-8982: Wavemaker Studio 6.6 – Local File Inclusion/Server-Side Request Forgery
漏洞标题 CVE-2019-8982: Wavemaker Studio 6.6 - Local File Inclusion/Server-Side Request Forgery 漏洞描述 WaveMaker Studio 6.6 mishandles the studioService.download?method=getConten...
2019年8月31日 22:13CVE-2024-23692: Rejetto HTTP File Server – Template injection
漏洞标题 CVE-2024-23692: Rejetto HTTP File Server - Template injection 漏洞描述 This vulnerability allows a remote, unauthenticated attacker to execute arbitrary commands on the af...
2024年10月1日 15:56
-CVE-2020-1472 net logon RCE利用
本文转载于公众号:融云攻防实验室,原文地址: 漏洞复现-CVE-2020-1472 net logon RCE利用 2020年08月12日,Windows官方 发布了 NetLogon 特权提升漏洞 的风险通告,该漏洞编号为 CVE-202...
2023年2月1日 13:53CVE-2025-55182: React Server Components – Remote Code Execution
漏洞标题 CVE-2025-55182: React Server Components - Remote Code Execution 漏洞描述 React Server Components 19.0.0, 19.1.0, 19.1.1, and 19.2.0 including react-server-dom-parcel, reac...
2025年4月2日 08:45CVE-2021-45968: Pascom CPS – Local File Inclusion
漏洞标题 CVE-2021-45968: Pascom CPS - Local File Inclusion 漏洞描述 Pascom packaged with Cloud Phone System (CPS) versions before 7.20 contain a known local file inclusion vulnerab...
2021年10月21日 07:51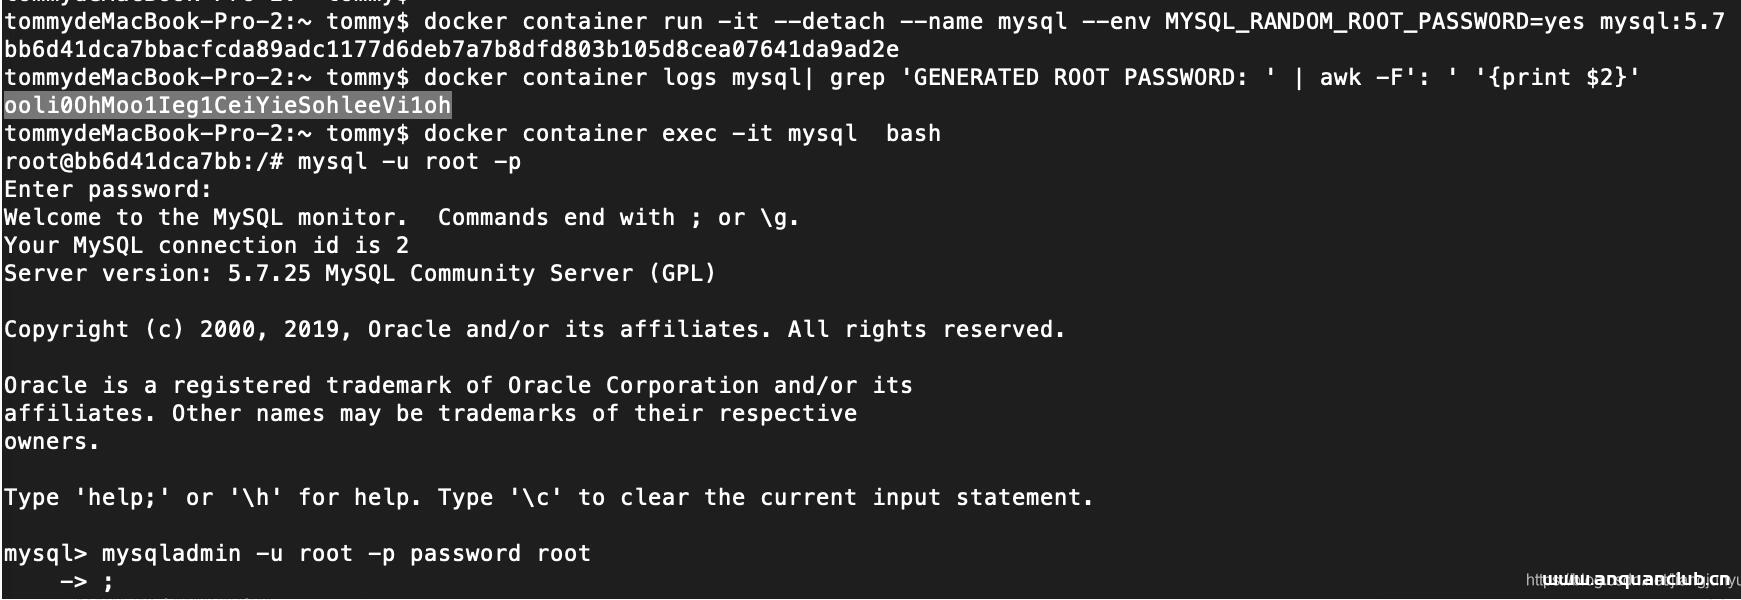
docker 免root权限登陆的解决方案_docker
这篇文章主要介绍了docker 免root权限登陆的解决方案,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 初次使用docker命令的时候会报权限问题 Got permission denied while t...
2022年6月26日 21:32
Hack Me Please靶机攻略(ubuntu_ctf)
靶机详情 靶机地址:http://www.vulnhub.com/entry/hack-me-please-1,731/。 这个靶机的目标是获得root权限。 靶机下载后安装好,选择NAT模式。 使用Kali作为此次的攻击机,同样选择NAT模式,...

 2022年4月2日 23:36
Apache Struts2(S2-061)远程代码执行漏洞(CVE-2020-17530)
漏洞标题 Apache Struts2(S2-061)远程代码执行漏洞(CVE-2020-17530) 漏洞描述 Apache Struts2框架是一个用于开发Java EE网络应用程序的Web框架。Struts2 会对某些标签属性(比如 id,其他属性有...
2020年3月21日 11:17Aspera Faspex CVE-2022-47986 远程代码执行漏洞
漏洞标题 Aspera Faspex CVE-2022-47986 远程代码执行漏洞 漏洞描述 Aspera Faspex CVE-2022-47986 远程 PoC代码 暂无
2022年12月11日 00:37CVE-2022-29298: SolarView Compact 6.00 – Local File Inclusion
漏洞标题 CVE-2022-29298: SolarView Compact 6.00 - Local File Inclusion 漏洞描述 SolarView Compact 6.00 is vulnerable to local file inclusion which could allow attackers to access s...
2022年7月3日 16:56CVE-2021-24210: WordPress PhastPress <1.111 - Open Redirect
漏洞标题 CVE-2021-24210: WordPress PhastPress <1.111 - Open Redirect 漏洞描述 WordPress PhastPress plugin before 1.111 contains an open redirect vulnerability. An attacker can r...
2021年2月5日 01:59CVE-2019-10098: Apache HTTP server v2.4.0 to v2.4.39 – Open Redirect
漏洞标题 CVE-2019-10098: Apache HTTP server v2.4.0 to v2.4.39 - Open Redirect 漏洞描述 In Apache HTTP server 2.4.0 to 2.4.39, Redirects configured with mod_rewrite that were intend...
2019年3月21日 07:34
2026年10月16日 11:45
2026年10月15日 11:45
2026年10月14日 11:45
2026年10月13日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

