
最新发布第725页
通达OA v2017 Action_upload任意文件上传漏洞
本文转载于公众号:融云攻防实验室,原文地址: 漏洞复现 通达OA v2017 Action_upload任意文件上传漏洞 通达OA(OfficeAnywhere网络智能办公系统)是由北京通达信科科技有限公司自主研发的协同...
 2026年2月13日 12:53

CVE-2008-1059: WordPress Sniplets 1.1.2 – Local File Inclusion
漏洞标题 CVE-2008-1059: WordPress Sniplets 1.1.2 - Local File Inclusion 漏洞描述 PHP remote file inclusion vulnerability in modules/syntax_highlight.php in the Sniplets 1.1.2 and 1...
2008年11月25日 00:06
Linux高并发踩过的坑及性能优化介绍_Linux
目录前言Linux应用运行过程中出现Too many open files 问题分析和解决Linux高并发下 time_wait 过多的问题分析及解决Linux更多性能优化小结前言 Linux操作系统是现在服务器的首选操作系统,在Li...
2022年6月14日 23:03CVE-2024-29269: Telesquare TLR-2005KSH – Remote Command Execution
漏洞标题 CVE-2024-29269: Telesquare TLR-2005KSH - Remote Command Execution 漏洞描述 Telesquare Tlr-2005Ksh is a Sk Telecom Lte router from South Korea's Telesquare company.Tel...
2024年7月19日 01:42CVE-2022-36883: Git Plugin up to 4.11.3 on Jenkins Build Authorization
漏洞标题 CVE-2022-36883: Git Plugin up to 4.11.3 on Jenkins Build Authorization 漏洞描述 A missing permission check in Jenkins Git Plugin 4.11.3 and earlier allows unauthenticated ...
2022年1月29日 23:25
最新版kali安装docker详细教程
1、更新源 安装好kali之后,第一件事是跟新软件源,建议设置成国内的 打开etc/apt/source.list vim /etc/apt/source.list 然后如下图所示, 注释掉kali官方的更新源: #清华大学 deb http:...

 2023年11月19日 17:05
CVE-2023-27640: PrestaShop tshirtecommerce – Directory Traversal
漏洞标题 CVE-2023-27640: PrestaShop tshirtecommerce - Directory Traversal 漏洞描述 The Custom Product Designer (tshirtecommerce) module for PrestaShop allows HTTP requests to be fo...
2023年2月1日 12:44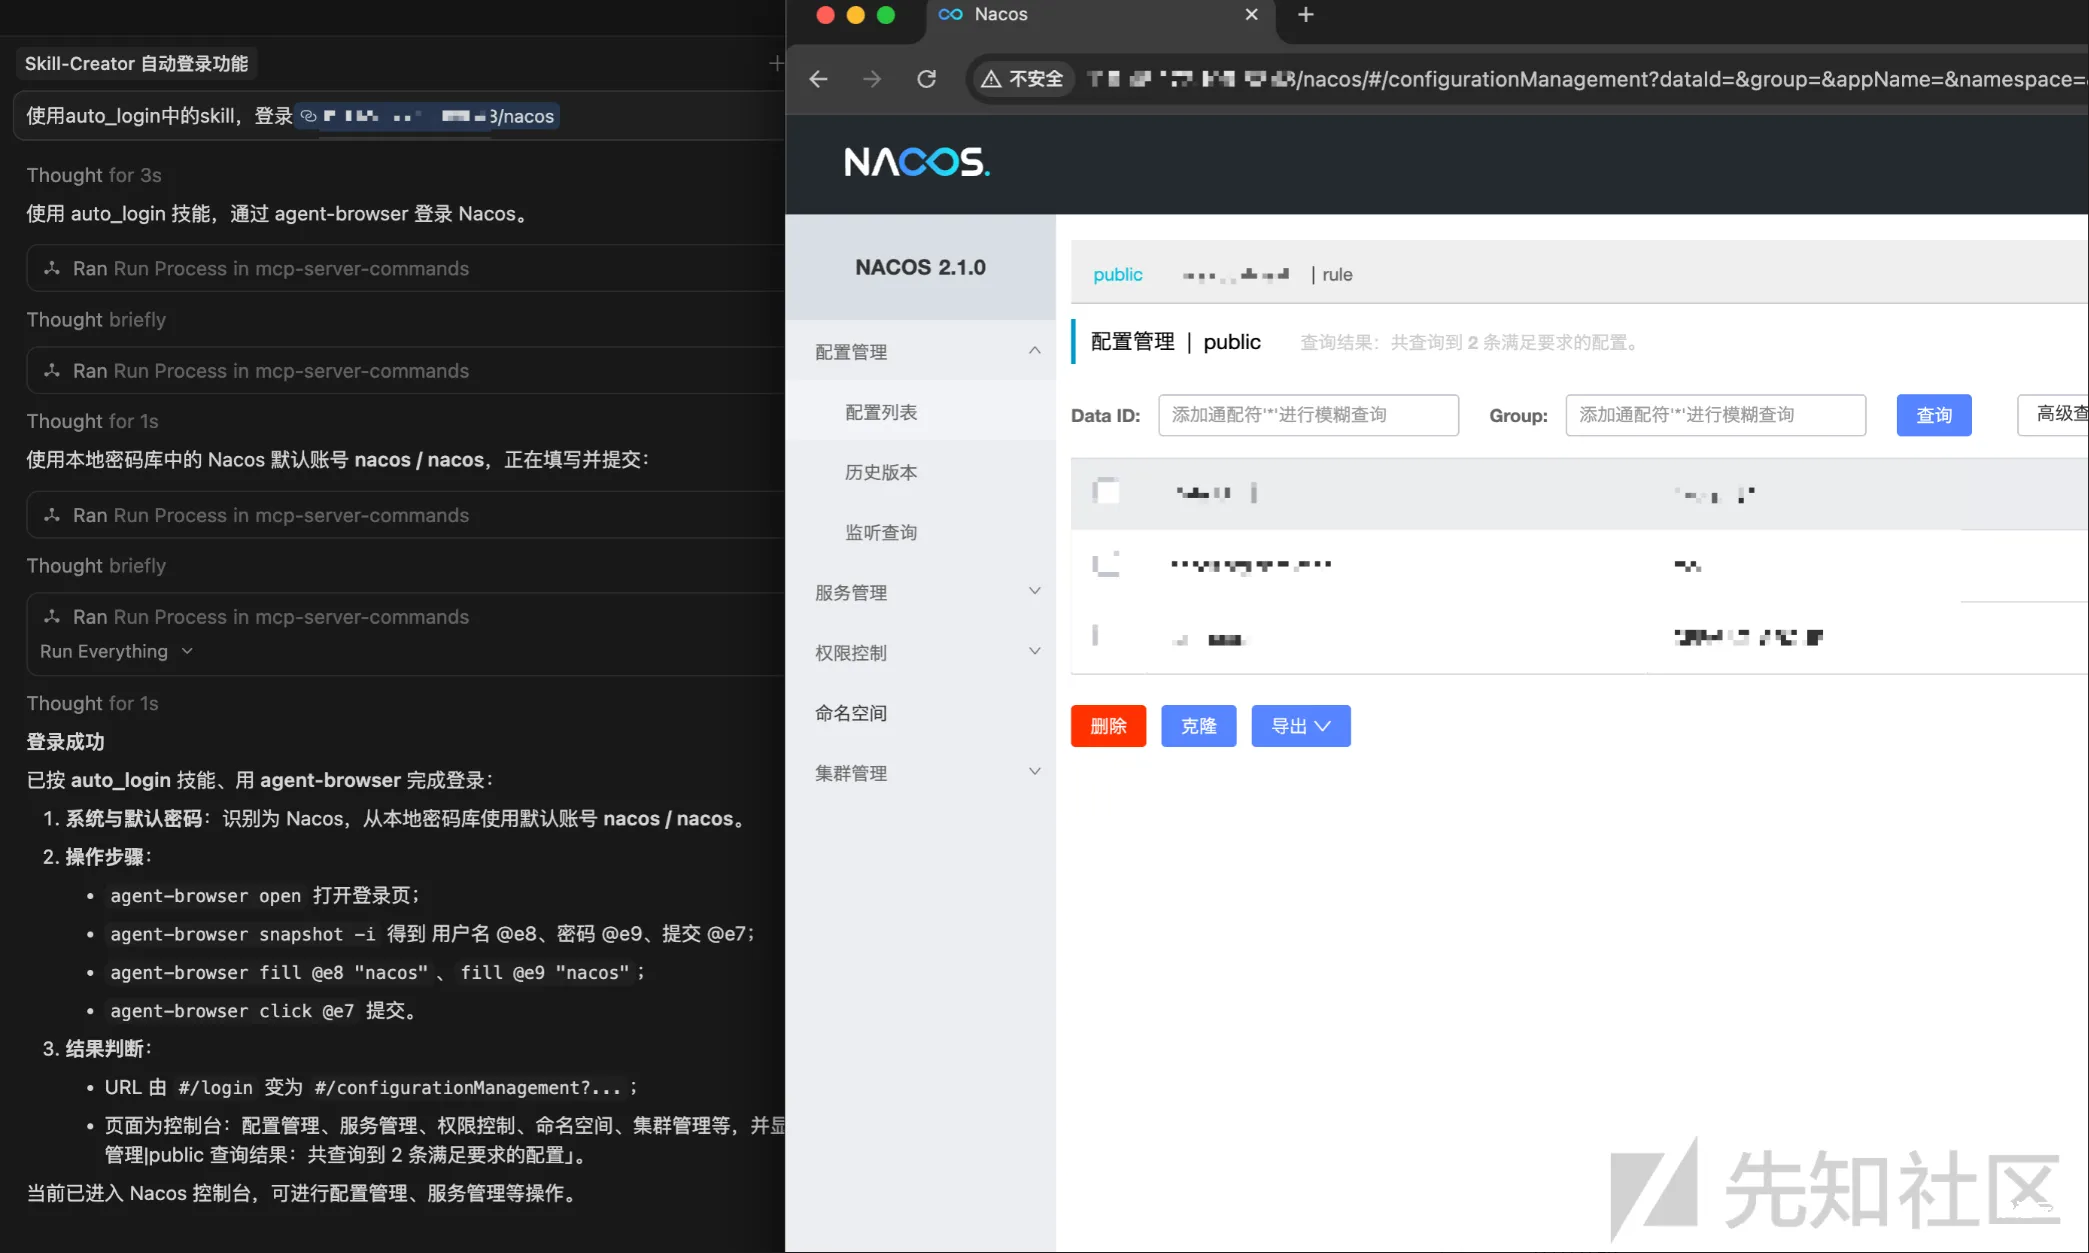
AI-Skill 自动进化的智能爆破工具(从零开始简单开发你第一个skill)
文章来源:AI-Skill 自动进化的智能爆破工具(从零开始简单开发你第一个skill)-先知社区 一、前言 在红蓝演习中,弱口令无论是出现在打点环节还是重要突破路径上,都非常常见。 但是每次在演习...
2026年3月25日 22:33CVE-2019-17232: WordPress Ultimate FAQs <= 1.8.24 – Unauthenticated Options Import and Export
漏洞标题 CVE-2019-17232: WordPress Ultimate FAQs <= 1.8.24 – Unauthenticated Options Import and Export 漏洞描述 Functions/EWD_UFAQ_Import.php in the ultimate-faqs plugin throug...
2019年4月13日 12:01CVE-2021-25298: Nagios XI 5.5.6-5.7.5 – Authenticated Remote Command Injection
漏洞标题 CVE-2021-25298: Nagios XI 5.5.6-5.7.5 - Authenticated Remote Command Injection 漏洞描述 Nagios XI 5.5.6 through 5.7.5 is susceptible to authenticated remote command inject...
2021年4月28日 13:18CVE-2013-5528: Cisco Unified Communications Manager 7/8/9 – Directory Traversal
漏洞标题 CVE-2013-5528: Cisco Unified Communications Manager 7/8/9 - Directory Traversal 漏洞描述 A directory traversal vulnerability in the Tomcat administrative web interface in ...
2013年6月15日 17:35CVE-2025-34031: Moodle Jmol Filter 6.1 – Local File Inclusion
漏洞标题 CVE-2025-34031: Moodle Jmol Filter 6.1 - Local File Inclusion 漏洞描述 Moodle Jmol Filter 6.1 is vulnerable to local file inclusion through the jsmol.php file, allowing at...
2025年6月8日 15:22CentreStack 存在反序列化漏洞(CVE-2025-30406)
漏洞标题 CentreStack 存在反序列化漏洞(CVE-2025-30406) 漏洞描述 CVE-2025-30406 是由 CentreStack 门户的硬编码 machineKey使用导致的反序列化漏洞。攻击者可以通过该漏洞获取服务器权限,...
2025年5月17日 23:41CVE-2023-30019: Imgproxy <= 3.14.0 - Server-side request forgery (SSRF)
漏洞标题 CVE-2023-30019: Imgproxy <= 3.14.0 - Server-side request forgery (SSRF) 漏洞描述 imgproxy <=3.14.0 is vulnerable to Server-Side Request Forgery (SSRF) due to a lack ...
2023年4月11日 13:40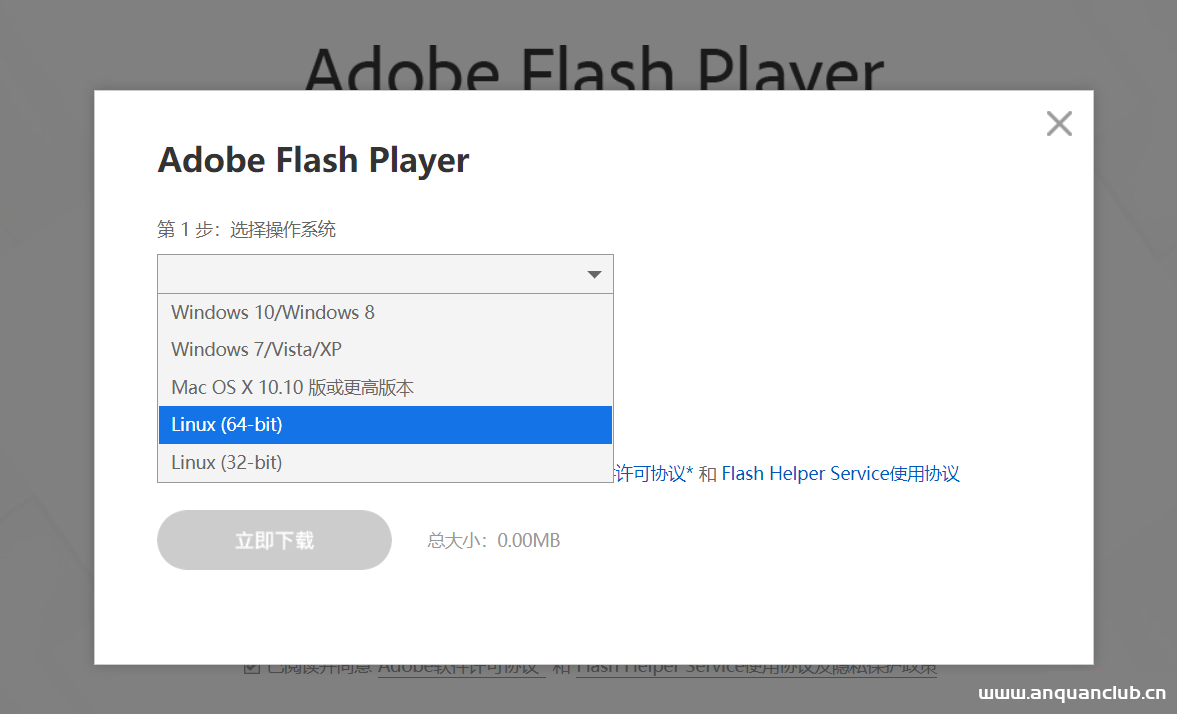
安装Linux的flash的步骤方法_Linux
在本篇文章里小编给各位分享的是关于安装Linux的flash的步骤方法,对此有需要的朋友们可以学习下。 如何安装Linux的flash 1、访问flash官网,点击下载,选择你的操作系统和flash版本 2、下载后...
2024年3月9日 20:56CVE-2016-1000132: WordPress enhanced-tooltipglossary 3.2.8 – Cross-Site Scripting
漏洞标题 CVE-2016-1000132: WordPress enhanced-tooltipglossary 3.2.8 - Cross-Site Scripting 漏洞描述 WordPress enhanced-tooltipglossary 3.2.8 contains a reflected cross-site scripti...
2016年9月20日 15:52
2026年9月19日 11:45
2026年9月18日 11:46
2026年9月17日 18:46
2026年9月17日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月17日 18:19
2026年8月16日 20:18
2026年8月11日 13:39
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

