
最新发布第728页

CVE-2021-41266: MinIO Operator Console Authentication Bypass
漏洞标题 CVE-2021-41266: MinIO Operator Console Authentication Bypass 漏洞描述 MinIO Console is a graphical user interface for the for MinIO Operator. MinIO itself is a multi-cloud...
 2021年4月2日 17:10
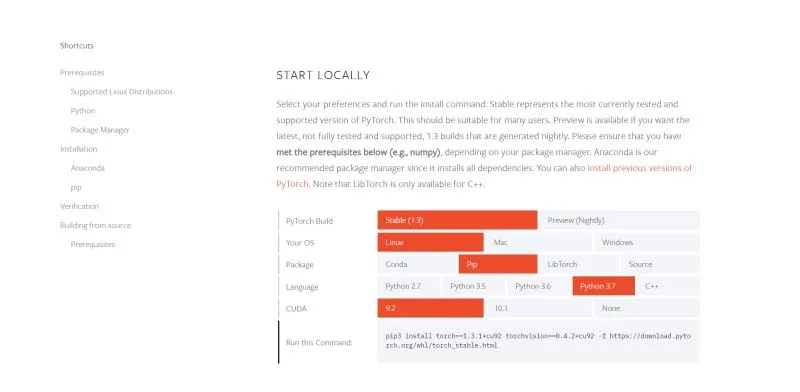
linux或windows环境下pytorch的安装与检查验证(解决runtimeerror问题)_Linux
这篇文章主要介绍了linux或windows环境下pytorch的安装与检查验证(解决runtimeerror问题),需要的朋友可以参考下 1、pytorch官网下载对应安装文件 http://pytorch.org/ 在getstarted处选择对应版...
2026年5月22日 11:45CVE-2021-37538: PrestaShop SmartBlog <4.0.6 - SQL Injection
漏洞标题 CVE-2021-37538: PrestaShop SmartBlog <4.0.6 - SQL Injection 漏洞描述 PrestaShop SmartBlog by SmartDataSoft < 4.0.6 is vulnerable to a SQL injection vulnerability in ...
2021年5月12日 19:26CVE-2017-5487: WordPress<4.7.1 Exist Username Enumeration
漏洞标题 CVE-2017-5487: Wordpress<4.7.1 Exist Username Enumeration 漏洞描述 WordPress (是一种使用PHP语言开发的博客平台)WordPress 在4.7.0版本之后将REST API插件集成到默认功能之...
2017年3月4日 10:03
红队攻击方法分析及应对之年策 – hvv面试技巧
什么是ATT&CK模型 ATT&CK背景介绍MITRE是一个由美国政府资助的研究机构,它在1958年脱离MIT,并且参与了许多商业和最高机密项目,甚至一些美国军方的威胁建模项目。2013年,MITRE推出了...

 2022年7月12日 19:38
CVE-2024-32231: Stash < 0.26.0 - SQL Injection
漏洞标题 CVE-2024-32231: Stash < 0.26.0 - SQL Injection 漏洞描述 Stash up to v0.25.1 was discovered to contain a SQL injection vulnerability via the sort parameter. PoC代码
2024年1月11日 12:08CVE-2021-31682: WebCTRL OEM <= 6.5 - Cross-Site Scripting
漏洞标题 CVE-2021-31682: WebCTRL OEM <= 6.5 - Cross-Site Scripting 漏洞描述 WebCTRL OEM 6.5 and prior is susceptible to a cross-site scripting vulnerability because the login po...
2021年12月6日 12:57CVE-2019-20224: Pandora FMS 7.0NG – Remote Command Injection
漏洞标题 CVE-2019-20224: Pandora FMS 7.0NG - Remote Command Injection 漏洞描述 Pandora FMS 7.0NG allows remote authenticated users to execute arbitrary OS commands via shell metach...
2019年9月9日 22:34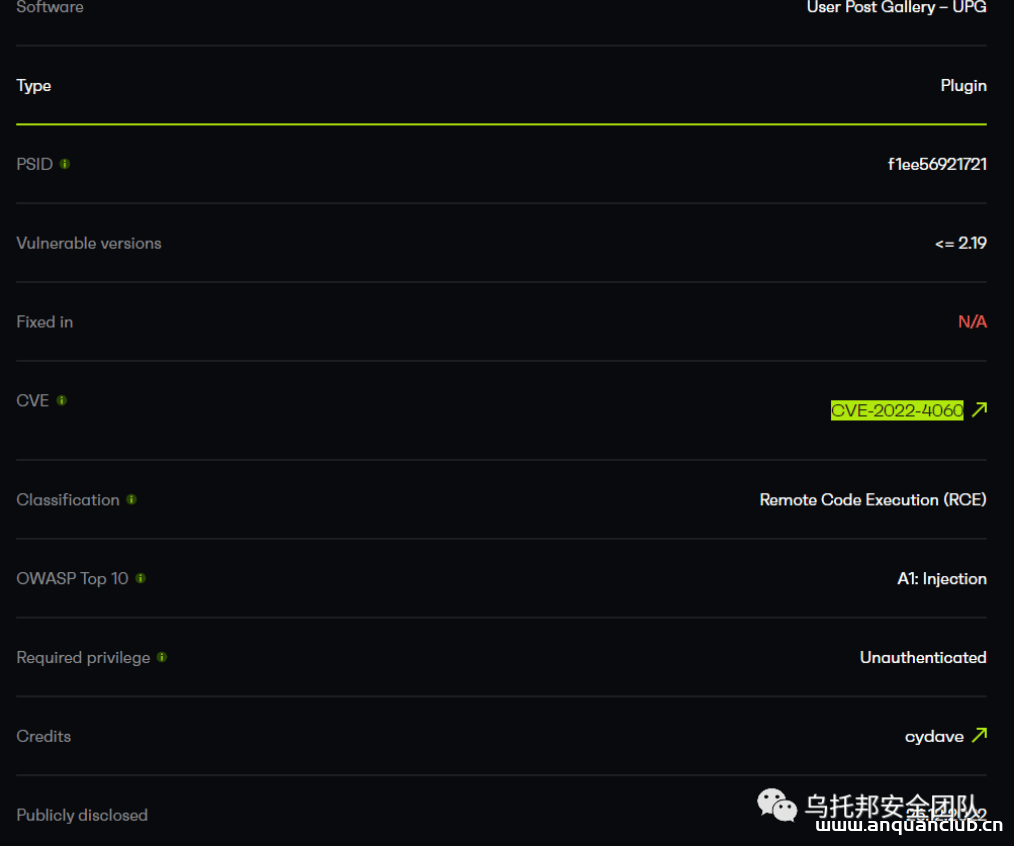
WordPress远程代码执行漏洞(CVE-2022-4060)
本文来自公众号:乌托邦安全团队原文地址:http://mp.weixin.qq.com/s/qfGzRS_8ZABYReqjmBG35g 0x00 概述 User Post Gallery – UPG是WordPress的插件,该插件存在远程命令执行漏洞,公开于2022...
2023年1月17日 21:06CVE-2023-49103: OwnCloud – Phpinfo Configuration
漏洞标题 CVE-2023-49103: OwnCloud - Phpinfo Configuration 漏洞描述 An issue was discovered in ownCloud owncloud/graphapi 0.2.x before 0.2.1 and 0.3.x before 0.3.1. The graphapi app...
2023年10月22日 13:01CVE-2015-9480: WordPress RobotCPA 5 – Directory Traversal
漏洞标题 CVE-2015-9480: WordPress RobotCPA 5 - Directory Traversal 漏洞描述 The RobotCPA plugin 5 for WordPress has directory traversal via the f.php l parameter. PoC代码
2015年1月18日 12:56CVE-2023-46455: GL.iNet <= 4.3.7 - Arbitrary File Write
漏洞标题 CVE-2023-46455: GL.iNet <= 4.3.7 - Arbitrary File Write 漏洞描述 GL.iNet <= 4.3.7 is vulnerable to an arbitrary file write exploit, allowing an attacker to overwrite...
2023年11月8日 17:37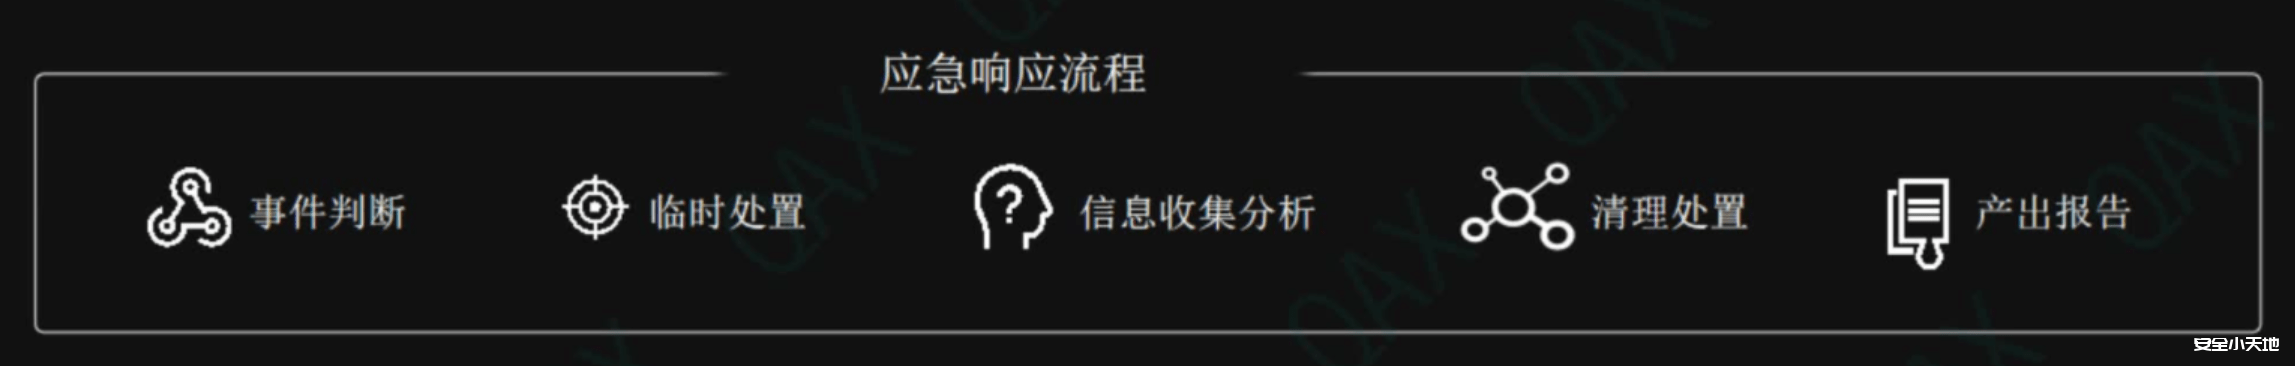
【网安面试】应急响应
应急响应是什么 随着信息化的高速发展,全球每年发生的网络安全事件不计其数,组织面临的安全威胁也逐年递增,当客户系统遭受病毒传播、网络攻击、黑客入侵,这类安全事件从而导致企业声誉受损...
2023年5月7日 20:53CVE-2023-27638: tshirtecommerce PrestaShop Module – SQL Injection
漏洞标题 CVE-2023-27638: tshirtecommerce PrestaShop Module - SQL Injection 漏洞描述 The tshirtecommerce module for PrestaShop is vulnerable to unauthenticated SQL injection via the...
2023年8月3日 01:15
深入理解linux执行文件提示No such file or directory的背后原因_Linux
这篇文章主要介绍了深入理解linux执行文件提示No such file or directory的背后原因,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编...
2026年5月16日 11:45CVE-2021-45811: osTicket 1.15.x – SQL Injection
漏洞标题 CVE-2021-45811: osTicket 1.15.x - SQL Injection 漏洞描述 A SQL injection vulnerability in the "Search" functionality of "tickets.php" page in osTicket ...
2021年10月11日 23:25
2026年10月16日 11:45
2026年10月15日 11:45
2026年10月14日 11:45
2026年10月13日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

