
最新发布第731页

CVE-2023-3578: DedeCMS 5.7.109 – Server-Side Request Forgery
漏洞标题 CVE-2023-3578: DedeCMS 5.7.109 - Server-Side Request Forgery 漏洞描述 Manipulation of the rssurl parameter in co_do.php leads to server-side request forgery in DedeCMS ver...
 2023年12月9日 00:45
CVE-2021-25003: WordPress WPCargo Track & Trace <6.9.0 - Remote Code Execution
漏洞标题 CVE-2021-25003: WordPress WPCargo Track & Trace <6.9.0 - Remote Code Execution 漏洞描述 WordPress WPCargo Track & Trace plugin before 6.9.0 is susceptible to re...
2021年11月16日 17:33CVE-2018-17431: Comodo Unified Threat Management Web Console – Remote Code Execution
漏洞标题 CVE-2018-17431: Comodo Unified Threat Management Web Console - Remote Code Execution 漏洞描述 Comodo Firewall & Central Manager (UTM) All Release before 2.7.0 & 1....
2018年8月28日 22:45CVE-2023-3990: Mingsoft MCMS < 5.3.1 - Cross-Site Scripting
漏洞标题 CVE-2023-3990: Mingsoft MCMS < 5.3.1 - Cross-Site Scripting 漏洞描述 A vulnerability classified as problematic has been found in Mingsoft MCMS up to 5.3.1. This affects...
2023年2月2日 09:48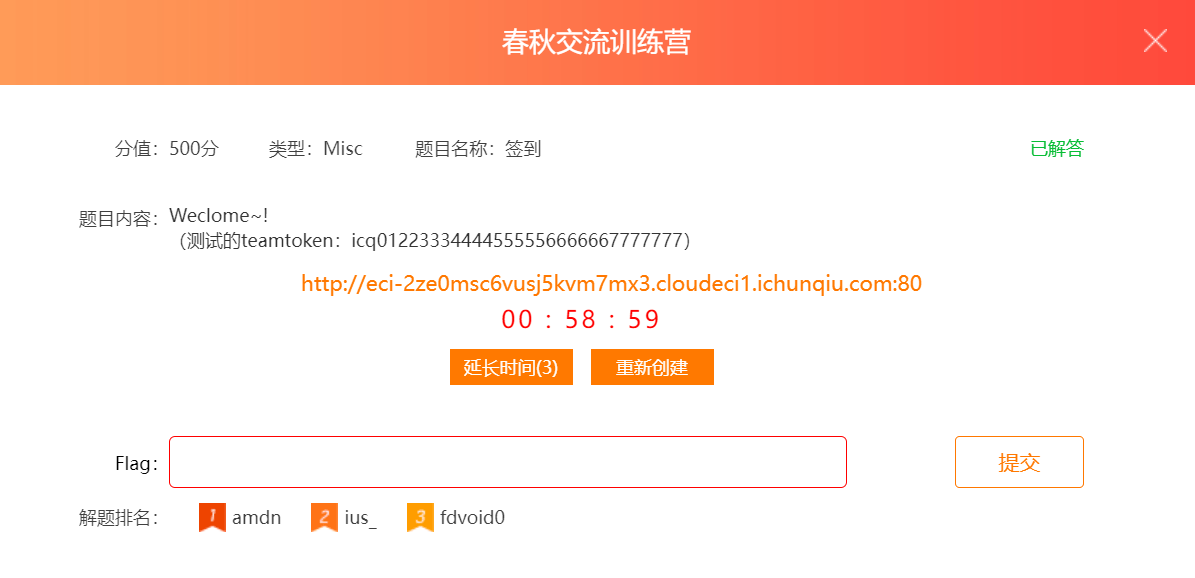
签到misc 漫漫求职路-合并相同“文字” 直到获得“P14” 春秋交流训练营
打开题目,有一个提示:测试的teamtoken:icq01223334444555556666667777777 网址打开,是一个游戏,2048类型的 因为是签到题,提示P14,玩了一下没有进行流量包发送,也就是直接是js处理 全局...

 2024年4月16日 22:49
CVE-2022-24990: TerraMaster TOS < 4.2.30 Server Information Disclosure
漏洞标题 CVE-2022-24990: TerraMaster TOS < 4.2.30 Server Information Disclosure 漏洞描述 TerraMaster NAS devices running TOS prior to version 4.2.30 are vulnerable to informatio...
2022年9月14日 22:12CVE-2025-34040: Zhiyuan OA Platform – Arbitrary File Upload
漏洞标题 CVE-2025-34040: Zhiyuan OA Platform - Arbitrary File Upload 漏洞描述 An arbitrary file upload vulnerability exists in the Zhiyuan OA platform 5.0, 5.1 - 5.6sp1, 6.0 - 6.1s...
2025年11月10日 10:10CVE-2020-9496: Apache OFBiz 17.12.03 – Cross-Site Scripting
漏洞标题 CVE-2020-9496: Apache OFBiz 17.12.03 - Cross-Site Scripting 漏洞描述 Apache OFBiz 17.12.03 contains cross-site scripting and unsafe deserialization vulnerabilities via an ...
2020年7月20日 17:13Citrix System SDWAN WAN-OP 权限绕过漏洞(CVE-2020-8193)
漏洞标题 Citrix System SDWAN WAN-OP 权限绕过漏洞(CVE-2020-8193) 漏洞描述 Citrix Systems Citrix System SDWAN WAN-OP是美国思杰系统(Citrix Systems)公司的一款SD-WAN(虚拟软件定义的...
2020年6月18日 15:22CVE-2023-23488: WordPress Paid Memberships Pro <2.9.8 - Blind SQL Injection
漏洞标题 CVE-2023-23488: WordPress Paid Memberships Pro <2.9.8 - Blind SQL Injection 漏洞描述 WordPress Paid Memberships Pro plugin before 2.9.8 contains a blind SQL injection v...
2023年8月19日 22:35CVE-2025-23061: Mongoose – NoSQL Injection
漏洞标题 CVE-2025-23061: Mongoose - NoSQL Injection 漏洞描述 NoSQL injection vulnerability in Mongoose < 8.9.5 affecting the populate() function's match option. This vulner...
2025年8月2日 03:07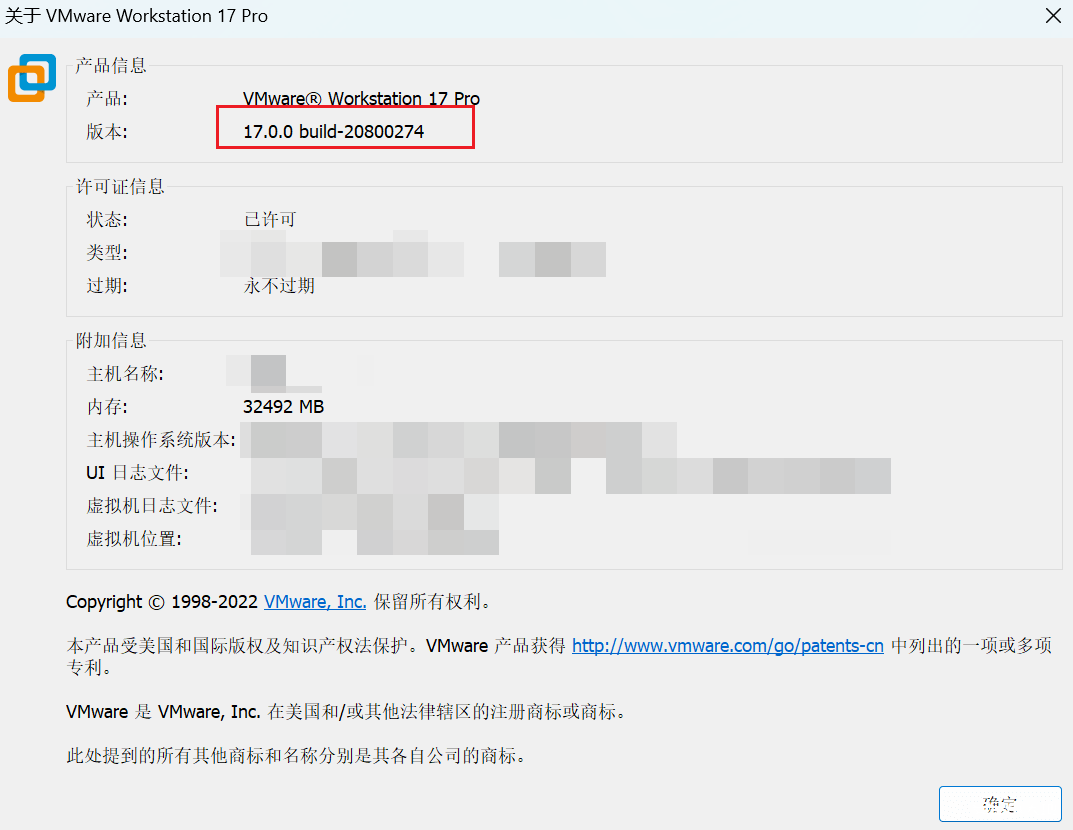
VMware虚拟机17.5版更新发布 附永久激活KEY
免责声明 安全小天地所发布的文章及工具只限交流学习,安全小天地不承担任何责任!如有侵权,请告知我们立即删除。 新版特性 性能提升:我们对VM虚拟机的性能进行了全面优化,使其在处理大型应...
2023年10月23日 22:51CVE-2017-9841: PHPUnit – Remote Code Execution
漏洞标题 CVE-2017-9841: PHPUnit - Remote Code Execution 漏洞描述 PHPUnit before 4.8.28 and 5.x before 5.6.3 allows remote attackers to execute arbitrary PHP code via HTTP POST data...
2017年12月25日 19:06CVE-2020-36731: Flexible Checkout Fields for WooCommerce <= 2.3.1 - Unauthenticated Arbitrary Plugin Settings Update
漏洞标题 CVE-2020-36731: Flexible Checkout Fields for WooCommerce <= 2.3.1 - Unauthenticated Arbitrary Plugin Settings Update 漏洞描述 The Flexible Checkout Fields for WooCommer...
2020年12月28日 04:14CVE-2023-30869: Easy Digital Downloads – Privilege Escalation
漏洞标题 CVE-2023-30869: Easy Digital Downloads - Privilege Escalation 漏洞描述 Improper Authentication vulnerability in Easy Digital Downloads plugin allows unauth. Privilege Esca...
2023年5月8日 01:45CVE-2019-19824: TOTOLINK Realtek SD Routers – Remote Command Injection
漏洞标题 CVE-2019-19824: TOTOLINK Realtek SD Routers - Remote Command Injection 漏洞描述 TOTOLINK Realtek SDK based routers may allow an authenticated attacker to execute arbitrary...
2019年5月24日 09:24
2026年10月21日 11:45
2026年10月20日 11:45
2026年10月19日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

