
最新发布第733页

Cisco RV132W RV134W 路由器信息泄露(CVE-2018-0127)
漏洞标题 Cisco RV132W RV134W 路由器信息泄露(CVE-2018-0127) 漏洞描述 Cisco RV132W ADSL2+Wireless-N VPN路由器和Cisco RV134W VDSL2 Wireless ACVPN路由器的web界面中存在漏洞,使得未经验...
 2018年8月23日 21:58
CVE-2019-14287: Sudo <= 1.8.27 - Security Bypass
漏洞标题 CVE-2019-14287: Sudo <= 1.8.27 - Security Bypass 漏洞描述 In Sudo before 1.8.28, an attacker with access to a Runas ALL sudoer account can bypass certain policy blackli...
2019年6月17日 21:07CVE-2023-26256: STAGIL Navigation for Jira Menu & Themes <2.0.52 - Local File Inclusion
漏洞标题 CVE-2023-26256: STAGIL Navigation for Jira Menu & Themes <2.0.52 - Local File Inclusion 漏洞描述 STAGIL Navigation for Jira Menu & Themes plugin before 2.0.52 i...
2023年11月3日 03:54CVE-2025-26319: FlowiseAI Flowise <= 2.2.6 - Arbitrary File Upload
漏洞标题 CVE-2025-26319: FlowiseAI Flowise <= 2.2.6 - Arbitrary File Upload 漏洞描述 FlowiseAI Flowise version 2.2.6 and below contains an arbitrary file upload vulnerability in...
2025年8月6日 23:12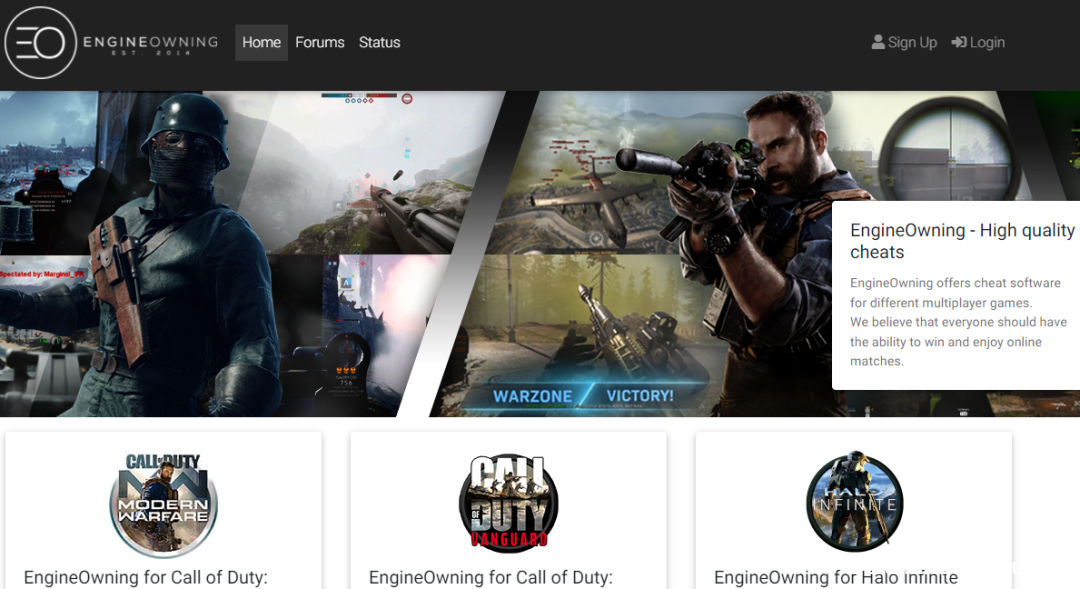
动视起诉外挂网站EngineOwning,且要求外挂开发者赔偿损失
针对外挂横行的环境,《使命召唤》制作发行商动视Activision外挂打击行动再次升级,于前不久起诉了最热门的外挂网站之一EngineOwning。动视的诉求除永久关闭该外挂网站外,还要求外挂开发人员、...
2022年3月10日 23:39CVE-2020-35476: OpenTSDB 2.4.0 Remote Code Execution
漏洞标题 CVE-2020-35476: OpenTSDB 2.4.0 Remote Code Execution 漏洞描述 A remote code execution vulnerability occurs in OpenTSDB through 2.4.0 via command injection in the yrange pa...
2020年6月8日 16:41CVE-2024-3032: WordPress Themify Builder < 7.5.8 - Open Redirect
漏洞标题 CVE-2024-3032: WordPress Themify Builder < 7.5.8 - Open Redirect 漏洞描述 The Themify Builder WordPress plugin before version 7.5.8 contains an open redirect vulnerabil...
2024年6月21日 16:47CVE-2017-14186: FortiGate FortiOS SSL VPN Web Portal – Cross-Site Scripting
漏洞标题 CVE-2017-14186: FortiGate FortiOS SSL VPN Web Portal - Cross-Site Scripting 漏洞描述 FortiGate FortiOS through SSL VPN Web Portal contains a cross-site scripting vulnerabi...
2017年7月13日 19:02CVE-2025-25291: GitLab – SAML Authentication Bypass
漏洞标题 CVE-2025-25291: GitLab - SAML Authentication Bypass 漏洞描述 ruby-saml provides security assertion markup language (SAML) single sign-on (SSO) for Ruby. An authentication ...
2025年4月9日 13:15CVE-2023-41109: SmartNode SN200 Analog Telephone Adapter (ATA) & VoIP Gateway – Command Injection
漏洞标题 CVE-2023-41109: SmartNode SN200 Analog Telephone Adapter (ATA) & VoIP Gateway - Command Injection 漏洞描述 The SmartNode SN200 Analog Telephone Adapter (ATA) & VoI...
2023年8月7日 10:14CVE-2023-5974: WordPress WPB Show Core <= 2.2 - Server-Side Request Forgery
漏洞标题 CVE-2023-5974: WordPress WPB Show Core <= 2.2 - Server-Side Request Forgery 漏洞描述 The WPB Show Core WordPress plugin through version 2.2 is vulnerable to Server-Side...
2023年7月8日 11:47CVE-2021-24370: WordPress Fancy Product Designer <4.6.9 - Arbitrary File Upload
漏洞标题 CVE-2021-24370: WordPress Fancy Product Designer <4.6.9 - Arbitrary File Upload 漏洞描述 WordPress Fancy Product Designer plugin before 4.6.9 is susceptible to an arbit...
2021年6月7日 17:05CVE-2014-9614: Netsweeper 4.0.5 – Default Weak Account
漏洞标题 CVE-2014-9614: Netsweeper 4.0.5 - Default Weak Account 漏洞描述 The Web Panel in Netsweeper before 4.0.5 has a default password of 'branding' for the branding ac...
2014年3月30日 01:57
Nginx 负载均衡是什么以及该如何配置_nginx
这篇文章主要介绍了Nginx 负载均衡是什么以及该如何配置,帮助大家更好的理解和使用Nginx服务器,感兴趣的朋友可以了解下 什么是负载均衡 负载均衡主要通过专门的硬件设备或者通过软件算法实现...
2022年10月7日 20:37CVE-2018-6184: Zeit Next.js < 4.2.3 - Local File Inclusion
漏洞标题 CVE-2018-6184: Zeit Next.js < 4.2.3 - Local File Inclusion 漏洞描述 Zeit Next.js before 4.2.3 is susceptible to local file inclusion under the /_next request namespace....
2018年2月17日 16:29CVE-2021-32819: Nodejs Squirrelly – Remote Code Execution
漏洞标题 CVE-2021-32819: Nodejs Squirrelly - Remote Code Execution 漏洞描述 Nodejs Squirrelly is susceptible to remote code execution. Squirrelly is a template engine implemented i...
2021年1月16日 12:11
2026年9月19日 11:45
2026年9月18日 11:46
2026年9月17日 18:46
2026年9月17日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月17日 18:19
2026年8月16日 20:18
2026年8月11日 13:39
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

