
最新发布第734页

CVE-2007-4556: OpenSymphony XWork/Apache Struts2 – Remote Code Execution S2-001
漏洞标题 CVE-2007-4556: OpenSymphony XWork/Apache Struts2 - Remote Code Execution S2-001 漏洞描述 Apache Struts support in OpenSymphony XWork before 1.2.3, and 2.x before 2.0.4, as...
 2007年5月6日 22:27
多地疫情再起,健康码的“健康大考”如何过关?
自疫情伊始,健康码就成为了出行必需品。健康码能保障疫情防控工作的高效开展,让技术应用更好地为社会“加码”护航。在关键时期,若健康码出现访问慢或者无法访问,有可能影响整个城市的生产生...

 2022年3月10日 16:02
CVE-2020-3952: VMware vCenter Server LDAP Broken Access Control
漏洞标题 CVE-2020-3952: VMware vCenter Server LDAP Broken Access Control 漏洞描述 Under certain conditions, vmdir that ships with VMware vCenter Server, as part of an embedded or e...
2020年2月15日 21:35CVE-2022-33901: WordPress MultiSafepay for WooCommerce <=4.13.1 - Arbitrary File Read
漏洞标题 CVE-2022-33901: WordPress MultiSafepay for WooCommerce <=4.13.1 - Arbitrary File Read 漏洞描述 WordPress MultiSafepay for WooCommerce plugin through 4.13.1 contains an ...
2022年11月2日 18:36CVE-2019-12314: Deltek Maconomy 2.2.5 – Local File Inclusion
漏洞标题 CVE-2019-12314: Deltek Maconomy 2.2.5 - Local File Inclusion 漏洞描述 Deltek Maconomy 2.2.5 is prone to local file inclusion via absolute path traversal in the WS.macx1.W_...
2019年2月24日 00:48CVE-2022-34048: Wavlink WN-533A8 – Cross-Site Scripting
漏洞标题 CVE-2022-34048: Wavlink WN-533A8 - Cross-Site Scripting 漏洞描述 Wavlink WN-533A8 M33A8.V5030.190716 contains a reflected cross-site scripting vulnerability via the login_...
2022年4月21日 10:54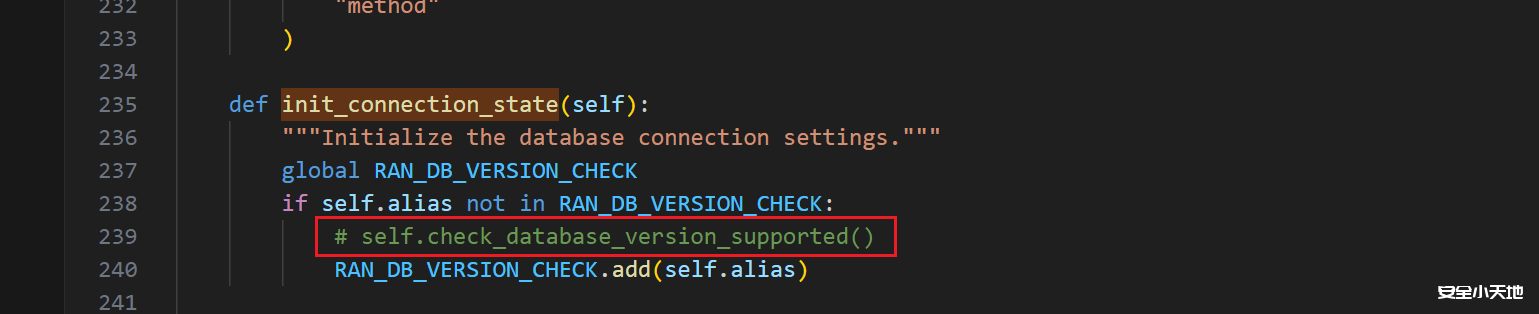
django报错数据库不支持低版本解决办法 django.db.utils.NotSupportedError: MySQL 8 or later is required (found 5.7.26)
Django提示mysq版本过低: django db. utils NotSuppotedError: MySQL 8 or later is required (found 5.7.26).因为mysql5.7及以下是免费的数据库,8.0之后是收费的。使用免费的数据库更放心,...
2024年3月22日 23:45CVE-2024-0200: Github Enterprise Authenticated Remote Code Execution
漏洞标题 CVE-2024-0200: Github Enterprise Authenticated Remote Code Execution 漏洞描述 An unsafe reflection vulnerability was identified in GitHub Enterprise Server that could lead...
2024年3月14日 02:04CVE-2022-3982: WordPress Booking Calendar <3.2.2 - Arbitrary File Upload
漏洞标题 CVE-2022-3982: WordPress Booking Calendar <3.2.2 - Arbitrary File Upload 漏洞描述 WordPress Booking Calendar plugin before 3.2.2 is susceptible to arbitrary file upload...
2022年6月12日 02:26CVE-2023-46574: TOTOLINK A3700R – Command Injection
漏洞标题 CVE-2023-46574: TOTOLINK A3700R - Command Injection 漏洞描述 An issue in TOTOLINK A3700R v.9.1.2u.6165_20211012 allows a remote attacker to execute arbitrary code via the ...
2023年1月4日 00:37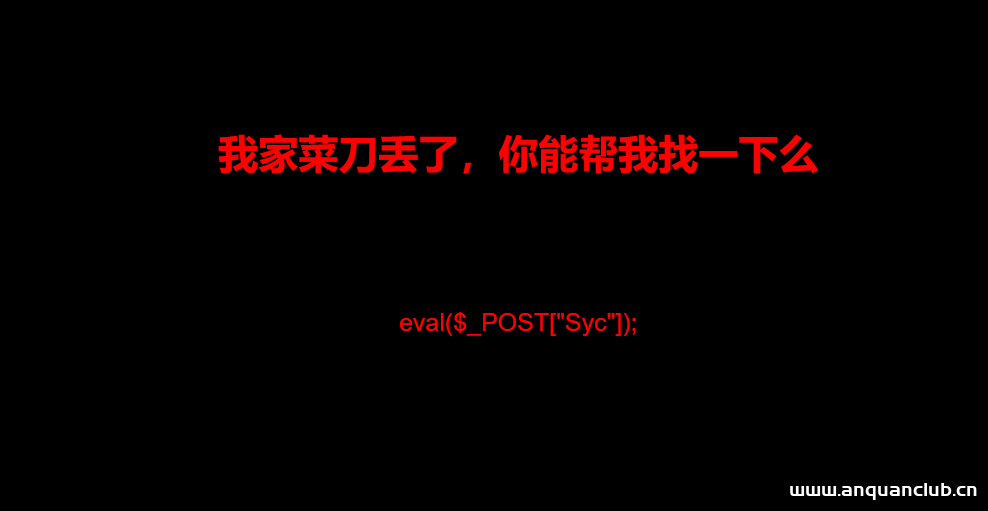
[极客大挑战 2019]Knife – buu刷题笔记
我家菜刀丢了,你能帮我找一下么 一句话木马也在这eval($_POST['Syc']); 现在的问题是木马有了,不知道文件名和路径,尝试目录扫描之后,居然只有一个index.php 按照ctf的尿性,玩的就是脑回路...
2022年4月14日 15:47CVE-2024-49757: Zitadel – User Registration Bypass
漏洞标题 CVE-2024-49757: Zitadel - User Registration Bypass 漏洞描述 The open-source identity infrastructure software Zitadel allows administrators to disable the user self-registr...
2024年2月5日 13:18CVE-2021-24214: WordPress OpenID Connect Generic Client 3.8.0-3.8.1 – Cross-Site Scripting
漏洞标题 CVE-2021-24214: WordPress OpenID Connect Generic Client 3.8.0-3.8.1 - Cross-Site Scripting 漏洞描述 WordPress OpenID Connect Generic Client plugin 3.8.0 and 3.8.1 contains...
2021年5月14日 09:23CVE-2023-7028: GitLab – Account Takeover via Password Reset
漏洞标题 CVE-2023-7028: GitLab - Account Takeover via Password Reset 漏洞描述 An issue has been discovered in GitLab CE/EE affecting all versions from 16.1 prior to 16.1.6, 16.2 pr...
2023年11月15日 11:20CVE-2022-29009: Cyber Cafe Management System 1.0 – SQL Injection
漏洞标题 CVE-2022-29009: Cyber Cafe Management System 1.0 - SQL Injection 漏洞描述 Cyber Cafe Management System 1.0 contains multiple SQL injection vulnerabilities via the username...
2022年9月20日 12:19CVE-2022-38295: Cuppa CMS v1.0 – Cross Site Scripting
漏洞标题 CVE-2022-38295: Cuppa CMS v1.0 - Cross Site Scripting 漏洞描述 Cuppa CMS v1.0 was discovered to contain a cross-site scripting vulnerability at /table_manager/view/cu_user...
2022年8月24日 00:45
2026年10月20日 11:45
2026年10月19日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

