
最新发布第737页
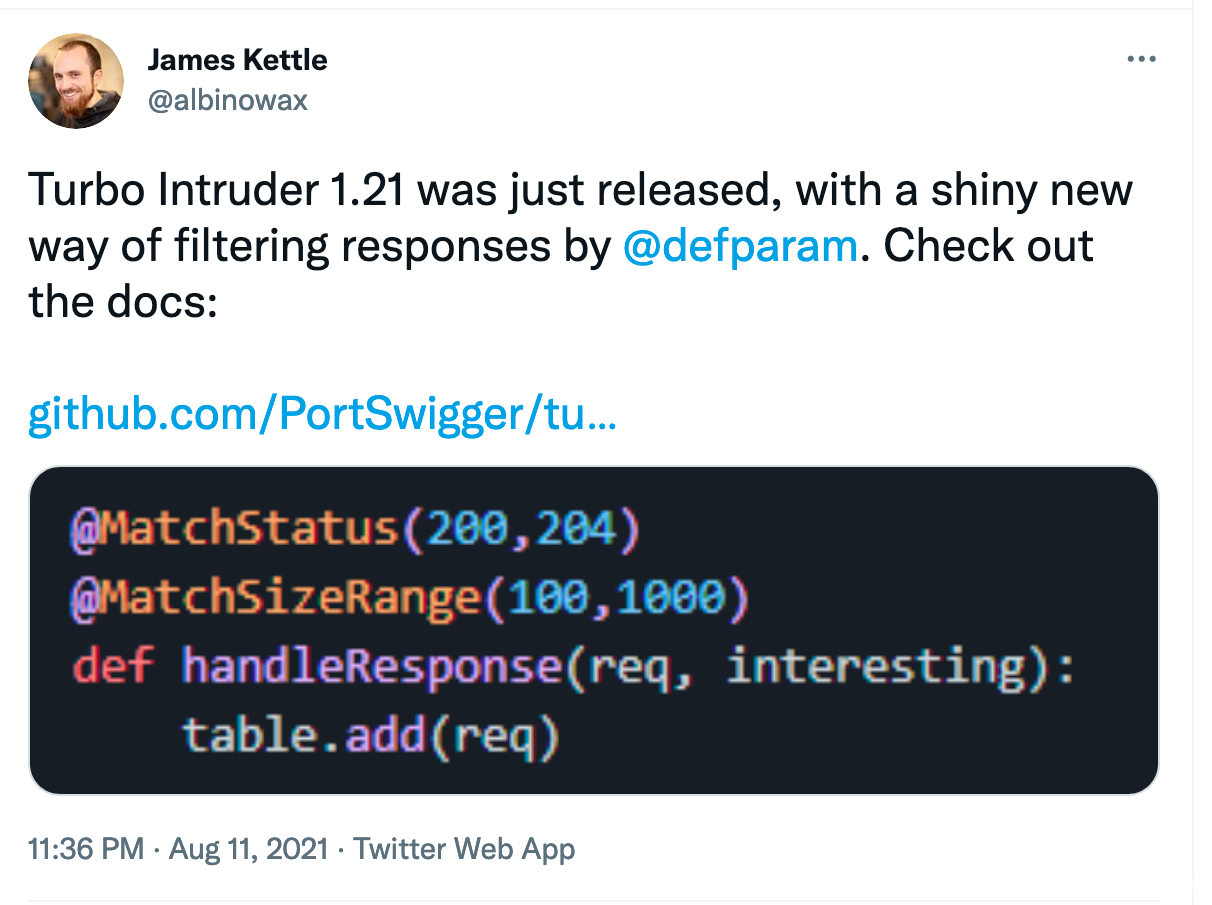
bugbounty技巧聚合20210812
漏洞报告 Acronis #1070533 Acronis True Image 2021 (windows) does not validate server hostname on a login TLS connection Elastic #1218680 Improper authorization on /api/as/v1/creden...
 2022年3月10日 23:35

解决Tomcat10 Catalina log乱码问题_Tomcat
这篇文章主要介绍了解决Tomcat10 Catalina log乱码问题,本文通过图文并茂的形式给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 运行环境,Idea2020版...
2023年2月27日 21:06
CVE-2020-35749: WordPress Simple Job Board <2.9.4 - Local File Inclusion
漏洞标题 CVE-2020-35749: WordPress Simple Job Board <2.9.4 - Local File Inclusion 漏洞描述 WordPress Simple Job Board prior to version 2.9.4 is vulnerable to arbitrary file retr...
2020年6月27日 06:42
详解Linux环境变量配置全攻略_Linux
这篇文章主要介绍了Linux环境变量配置全攻略,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编来一起学习学习吧 在自定义安装软件的时...
2024年6月20日 20:25CVE-2021-39350: FV Flowplayer Video Player WordPress plugin – Authenticated Cross-Site Scripting
漏洞标题 CVE-2021-39350: FV Flowplayer Video Player WordPress plugin - Authenticated Cross-Site Scripting 漏洞描述 The FV Flowplayer Video Player WordPress plugin is vulnerable to ...
2021年10月25日 11:32CVE-2025-5961: WordPress WPvivid Backup & Migration Plugin <= 0.9.116 - Authenticated Arbitrary File Upload
漏洞标题 CVE-2025-5961: WordPress WPvivid Backup & Migration Plugin <= 0.9.116 - Authenticated Arbitrary File Upload 漏洞描述 The Migration, Backup, Staging – WPvivid Backu...
2025年8月7日 17:22CVE-2023-4116: PHPJabbers Taxi Booking 2.0 – Cross Site Scripting
漏洞标题 CVE-2023-4116: PHPJabbers Taxi Booking 2.0 - Cross Site Scripting 漏洞描述 A vulnerability classified as problematic was found in PHP Jabbers Taxi Booking 2.0. Affected by...
2023年10月7日 07:21CVE-2024-4399: WordPress CAS Theme <= 1.0.0 - Server-Side Request Forgery
漏洞标题 CVE-2024-4399: WordPress CAS Theme <= 1.0.0 - Server-Side Request Forgery 漏洞描述 The CAS WordPress theme through version 1.0.0 is vulnerable to Server-Side Request Fo...
2024年10月21日 09:23CVE-2023-5561: WordPress Core – Post Author Email Disclosure
漏洞标题 CVE-2023-5561: WordPress Core - Post Author Email Disclosure 漏洞描述 WordPress Core is vulnerable to Sensitive Information Exposure in versions between 4.7.0 and 6.3.1 vi...
2023年6月19日 06:10
俄罗斯最大社交平台明年将强制实施双因素身份认证
VK,全称VKontakte,是俄罗斯及独联体国家最流行的社交媒体平台,拥有超过6.5亿用户。VK已决定在其服务中引入2FA(two-factor authentication,双因素身份认证)。从明年二月开始,所有订阅人数...
2022年3月10日 23:39CVE-2023-41621: Emlog Pro v2.1.14 – Cross-Site Scripting
漏洞标题 CVE-2023-41621: Emlog Pro v2.1.14 - Cross-Site Scripting 漏洞描述 Cross Site Scripting (XSS) vulnerability in Emlog Pro v2.1.14 via /admin/store.php. PoC代码
2023年6月11日 09:47CVE-2025-24752: Essential Addons for Elementor < 6.0.15 - Cross-Site Scripting
漏洞标题 CVE-2025-24752: Essential Addons for Elementor < 6.0.15 - Cross-Site Scripting 漏洞描述 A Cross-Site Scripting (XSS) vulnerability exists in Essential Addons for Elemen...
2025年12月7日 17:37CVE-2025-27112: Navidrome <=0.54.5 - Authentication Bypass in Subsonic API
漏洞标题 CVE-2025-27112: Navidrome <=0.54.5 - Authentication Bypass in Subsonic API 漏洞描述 Navidrome is an open source web-based music collection server and streamer. Starting...
2025年7月8日 23:30CVE-2013-2251: Apache Struts 2 – DefaultActionMapper Prefixes OGNL Code Execution (S2-016)
漏洞标题 CVE-2013-2251: Apache Struts 2 - DefaultActionMapper Prefixes OGNL Code Execution (S2-016) 漏洞描述 In Struts 2 before 2.3.15.1 the information following "action:&quo...
2013年12月21日 22:20CVE-2024-38653: Ivanti Avalanche SmartDeviceServer – XML External Entity
漏洞标题 CVE-2024-38653: Ivanti Avalanche SmartDeviceServer - XML External Entity 漏洞描述 XXE in SmartDeviceServer in Ivanti Avalanche 6.3.1 allows a remote unauthenticated attack...
2024年11月11日 03:15CVE-2023-30013: TOTOLink – Unauthenticated Command Injection
漏洞标题 CVE-2023-30013: TOTOLink - Unauthenticated Command Injection 漏洞描述 TOTOLINK X5000R V9.1.0u.6118_B20201102 and V9.1.0u.6369_B20230113 contain a command insertion vulnera...
2023年1月29日 23:17
2026年11月7日 11:45
2026年11月6日 11:45
2026年11月5日 11:45
2026年11月4日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

