
最新发布第740页

Linux 中的防火墙 ufw 简介_Linux
ufw(简单防火墙Uncomplicated FireWall)真正地简化了 iptables,它从出现的这几年,已经成为 Ubuntu 和 Debian 等系统上的默认防火墙。这篇文章主要介绍了Linux 防火墙 ufw 简介,需要的朋友可...
 2024年2月16日 20:34

CVE-2019-17231: WordPress OneTone theme <= 3.0.6 – Unauthenticated Stored XSS
漏洞标题 CVE-2019-17231: WordPress OneTone theme <= 3.0.6 – Unauthenticated Stored XSS 漏洞描述 includes/theme-functions.php in the OneTone theme through 3.0.6 for WordPress ha...
2019年1月21日 02:35CVE-2021-26812: Moodle Jitsi Meet 2.7-2.8.3 – Cross-Site Scripting
漏洞标题 CVE-2021-26812: Moodle Jitsi Meet 2.7-2.8.3 - Cross-Site Scripting 漏洞描述 Moodle Jitsi Meet 2.7 through 2.8.3 plugin contains a cross-site scripting vulnerability via th...
2021年10月27日 07:41CVE-2023-3849: mooDating 1.2 – Cross-site scripting
漏洞标题 CVE-2023-3849: mooDating 1.2 - Cross-site scripting 漏洞描述 A vulnerability, which was classified as problematic, was found in mooSocial mooDating 1.2. Affected is an unk...
2023年10月20日 14:27CVE-2023-47643: SuiteCRM Unauthenticated Graphql Introspection
漏洞标题 CVE-2023-47643: SuiteCRM Unauthenticated Graphql Introspection 漏洞描述 Graphql Introspection is enabled without authentication, exposing the scheme defining all object ty...
2023年6月25日 16:22CVE-2021-24442: WordPress Polls Widget < 1.5.3 - SQL Injection
漏洞标题 CVE-2021-24442: Wordpress Polls Widget < 1.5.3 - SQL Injection 漏洞描述 The Poll, Survey, Questionnaire and Voting system WordPress plugin before 1.5.3 did not sanitise...
2021年12月9日 05:10CVE-2021-46104: webp_server_go 0.4.0 – Path Traversal
漏洞标题 CVE-2021-46104: webp_server_go 0.4.0 - Path Traversal 漏洞描述 webp_server_go 0.4.0 contains a path traversal caused by insufficient sanitization in file handling, letting...
2021年7月24日 16:27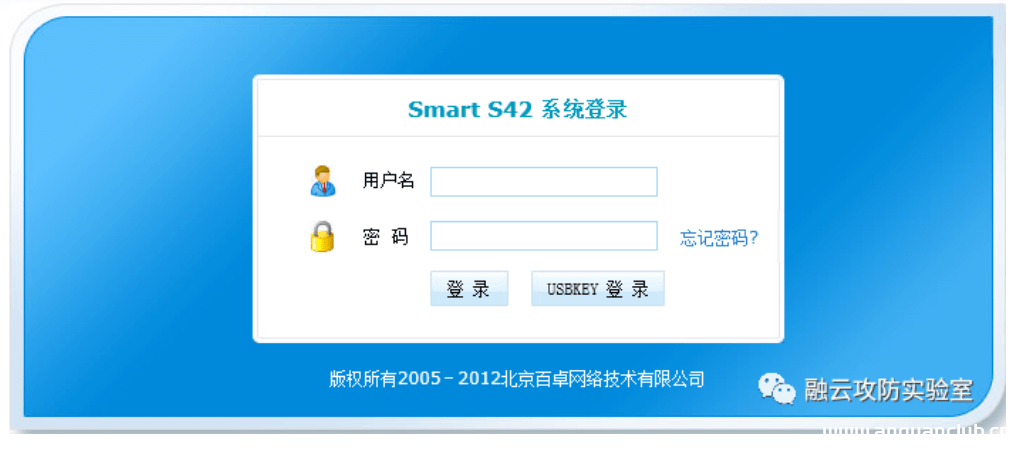
百卓 Smart importhtml.php 远程命令执行漏洞
本文转载于公众号:融云攻防实验室,原文地址: 漏洞复现 百卓 Smart importhtml.php 远程命令执行漏洞 百卓Smart S系列是强大的上网行为管理,设备内置实时更新的最全面的应用识别和URL分类库...
2026年2月13日 12:53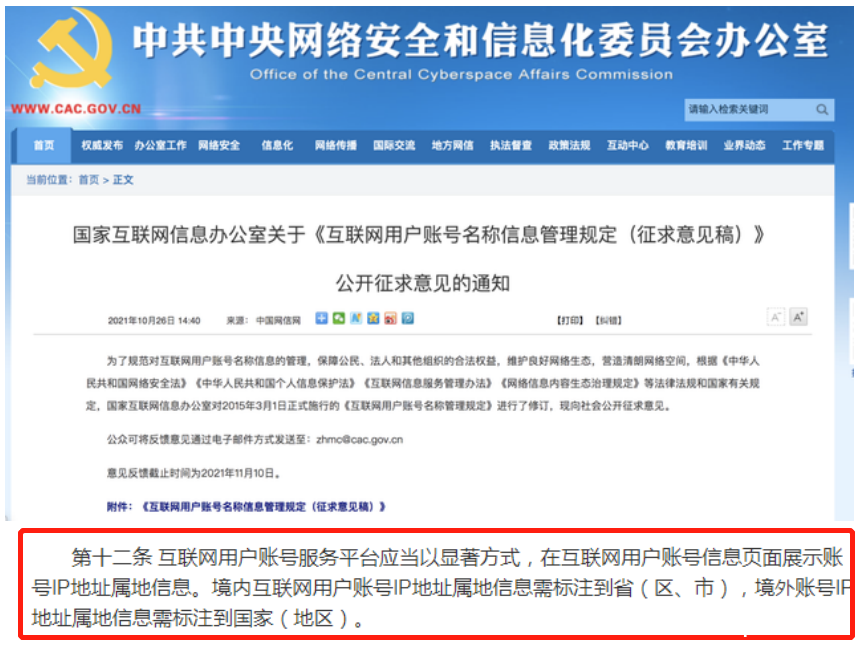
发现了吗?发表网络动态公开显示“IP属地”,会暴露我的行踪隐私吗?
自4月15日起,微博、抖音、今日头条、抖音、百家号、快手、知乎、小红书等各大平台宣布“公开账号IP属地”后,“国外”博主惊现国内IP,不少大V们都慌了,网络上出现了一个又一个翻车现场,因为...
2022年5月7日 18:07CVE-2020-12116: Zoho ManageEngine OpManger – Arbitrary File Read
漏洞标题 CVE-2020-12116: Zoho ManageEngine OpManger - Arbitrary File Read 漏洞描述 Zoho ManageEngine OpManager Stable build before 124196 and Released build before 125125 allows an...
2020年11月16日 21:00CVE-2018-13380: Fortinet FortiOS – Cross-Site Scripting
漏洞标题 CVE-2018-13380: Fortinet FortiOS - Cross-Site Scripting 漏洞描述 Fortinet FortiOS 6.0.0 to 6.0.4, 5.6.0 to 5.6.7, 5.4.0 to 5.4.12, 5.2 and below versions under SSL VPN web...
2018年8月6日 01:06CVE-2024-7339: TVT DVR Sensitive Device – Information Disclosure
漏洞标题 CVE-2024-7339: TVT DVR Sensitive Device - Information Disclosure 漏洞描述 A vulnerability has been found in TVT DVR TD-2104TS-CL, DVR TD-2108TS-HP, Provision-ISR DVR SH-40...
2024年8月9日 03:09CVE-2021-31602: Hitachi Vantara Pentaho/Business Intelligence Server – Authentication Bypass
漏洞标题 CVE-2021-31602: Hitachi Vantara Pentaho/Business Intelligence Server - Authentication Bypass 漏洞描述 Hitachi Vantara Pentaho through 9.1 and Pentaho Business Intelligence...
2021年6月2日 15:48CVE-2018-17207: WordPress Duplicator Plugin < 1.2.42 - Arbitrary Code Execution
漏洞标题 CVE-2018-17207: WordPress Duplicator Plugin < 1.2.42 - Arbitrary Code Execution 漏洞描述 An issue was discovered in Snap Creek Duplicator before 1.2.42. By accessing le...
2018年12月14日 23:11CVE-2021-36580: IceWarp Mail Server – Open Redirect
漏洞标题 CVE-2021-36580: IceWarp Mail Server - Open Redirect 漏洞描述 IceWarp Mail Server contains an open redirect via the referer parameter. This can lead to phishing attacks or ...
2021年10月31日 09:52CVE-2024-10783: WordPress Plugin MainWP Child – Authentication Bypass
漏洞标题 CVE-2024-10783: WordPress Plugin MainWP Child - Authentication Bypass 漏洞描述 The plugin is vulnerable to an authentication bypass that allows an unauthenticated user to ...
2024年6月24日 03:35
2026年9月20日 11:45
2026年9月19日 11:45
2026年9月18日 11:46
2026年9月17日 18:46
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

