
最新发布第748页

CVE-2025-2709: Yonyou UFIDA ERP-NC V5.0 – Cross-Site Scripting
漏洞标题 CVE-2025-2709: Yonyou UFIDA ERP-NC V5.0 - Cross-Site Scripting 漏洞描述 Yonyou UFIDA ERP-NC V5.0 is vulnerable to reflected cross-site scripting (XSS) via the key and redi...
 2025年2月6日 06:04
CVE-2025-30208: Vite – Arbitrary File Read
漏洞标题 CVE-2025-30208: Vite - Arbitrary File Read 漏洞描述 Vite, a provider of frontend development tooling, has a vulnerability in versions prior to 6.2.3, 6.1.2, 6.0.12, 5.4.15...
2025年6月4日 10:05CVE-2021-25114: WordPress Paid Memberships Pro <2.6.7 - Blind SQL Injection
漏洞标题 CVE-2021-25114: WordPress Paid Memberships Pro <2.6.7 - Blind SQL Injection 漏洞描述 WordPress Paid Memberships Pro plugin before 2.6.7 is susceptible to blind SQL inje...
2021年2月10日 23:59
bugbounty技巧聚合20211214
漏洞报告 【Sifchain】点击劫持漏洞 http://hackerone.com/reports/1199904 http://hackerone.com/reports/1212595 【Sifchain】时事通讯功能上的CSRF http://hackerone.com/reports/1190705 【...
2022年3月10日 23:32CVE-2021-24849: WCFM WooCommerce Multivendor Marketplace < 3.4.12 - SQL Injection
漏洞标题 CVE-2021-24849: WCFM WooCommerce Multivendor Marketplace < 3.4.12 - SQL Injection 漏洞描述 The wcfm_ajax_controller AJAX action of the WCFM Marketplace WordPress plugin...
2021年11月24日 23:19
空白页面第二种利用
这个页面也是src的,简单打个码,刚开始访问是这个样子滴 我记得我上一篇文章说了xray联动,那这篇就不说了,简单的探测一下,比如nmap,发现这个只有22跟80开放 那没办法,跑一手目录看看,看...
2022年3月10日 23:30CVE-2017-18556: Google Analytics by BestWebSoft < 1.7.1 - Cross-Site Scripting
漏洞标题 CVE-2017-18556: Google Analytics by BestWebSoft < 1.7.1 - Cross-Site Scripting 漏洞描述 The bws-google-analytics plugin before 1.7.1 for WordPress has multiple XSS issu...
2017年11月16日 16:26CVE-2020-21224: Inspur ClusterEngine V4.0 Remote Code Execution
漏洞标题 CVE-2020-21224: Inspur ClusterEngine V4.0 Remote Code Execution 漏洞描述 A Remote Code Execution vulnerability has been found in Inspur ClusterEngine V4.0. A remote attack...
2020年10月12日 20:10bugbounty技巧聚合20210810
漏洞报告 Mattermost #1216203 Mattermost Server OAuth Flow Cross-Site Scripting Kubernetes #1167773 Loading YAML in Java client can lead to command execution Nextcloud #1194606 Virt...
2022年3月10日 23:37CVE-2016-1000149: WordPress Simpel Reserveren <=3.5.2 - Cross-Site Scripting
漏洞标题 CVE-2016-1000149: WordPress Simpel Reserveren <=3.5.2 - Cross-Site Scripting 漏洞描述 WordPress plugin Simpel Reserveren 3.5.2 and before contains a reflected cross-sit...
2016年11月12日 10:27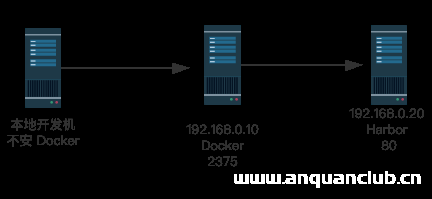
Spring Boot 2.4 新特性之一键构建Docker镜像的过程详解_docker
这篇文章主要介绍了Spring Boot 2.4 新特性之一键构建Docker镜像的过程详解,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 背景 在我们开发过程...
2022年12月21日 20:04CVE-2018-1271: Spring MVC Framework – Local File Inclusion
漏洞标题 CVE-2018-1271: Spring MVC Framework - Local File Inclusion 漏洞描述 Spring MVC Framework versions 5.0 prior to 5.0.5 and versions 4.3 prior to 4.3.15 and older unsupported...
2018年2月27日 20:30CVE-2017-5638: Apache Struts 2 – Remote Command Execution S2-045 S2-046
漏洞标题 CVE-2017-5638: Apache Struts 2 - Remote Command Execution S2-045 S2-046 漏洞描述 Apache Struts 2 2.3.x before 2.3.32 and 2.5.x before 2.5.10.1 is vulnerable to remote comm...
2017年10月21日 02:50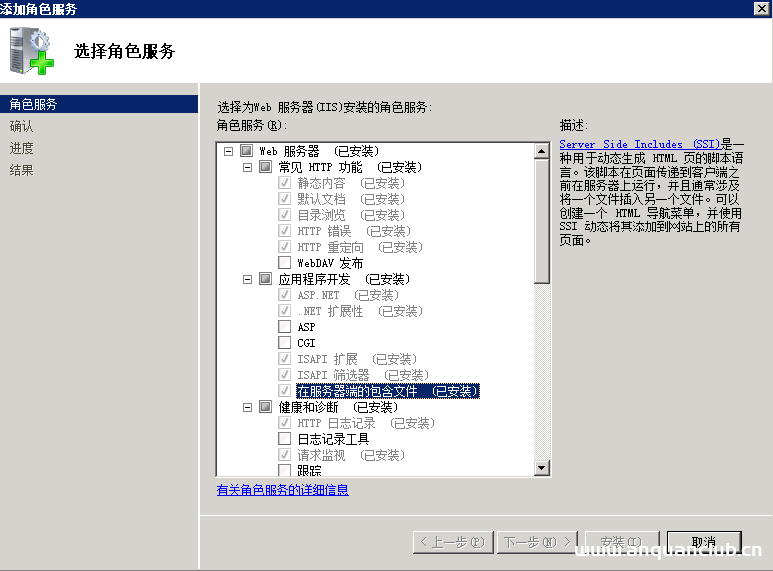
iis7.5中让html与shtml一样支持include功能(添加模块映射)_win服务器
因为客户经常需要修改文件,用不能每次都用js容易被屏蔽,文章已经生成了html或htm格式,不可能冒然再改为shtml扩展,下面就给大家分享一下如何让html也像shtml一样,需要的朋友可以参考下 刚开...
2024年4月6日 21:19CVE-2020-36731: Flexible Checkout Fields for WooCommerce <= 2.3.1 - Unauthenticated Arbitrary Plugin Settings Update
漏洞标题 CVE-2020-36731: Flexible Checkout Fields for WooCommerce <= 2.3.1 - Unauthenticated Arbitrary Plugin Settings Update 漏洞描述 The Flexible Checkout Fields for WooCommer...
2020年1月30日 11:33CVE-2023-27637: PrestaShop `tshirtecommerce` Module – SQL Injection
漏洞标题 CVE-2023-27637: PrestaShop `tshirtecommerce` Module - SQL Injection 漏洞描述 The tshirtecommerce module for PrestaShop is vulnerable to unauthenticated SQL injection via t...
2023年10月16日 00:22
2026年10月20日 11:45
2026年10月19日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

