
最新发布第755页

CVE-2010-1658: Joomla! Component NoticeBoard 1.3 – Local File Inclusion
漏洞标题 CVE-2010-1658: Joomla! Component NoticeBoard 1.3 - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the Code-Garage NoticeBoard (com_noticeboard) compo...
 2010年2月10日 16:32
CVE-2020-8194: Citrix ADC and Citrix NetScaler Gateway – Remote Code Injection
漏洞标题 CVE-2020-8194: Citrix ADC and Citrix NetScaler Gateway - Remote Code Injection 漏洞描述 Citrix ADC and NetScaler Gateway are susceptible to remote code injection. An attac...
2020年10月5日 20:32CVE-2023-4542: D-Link DAR-8000-10 – Command Injection
漏洞标题 CVE-2023-4542: D-Link DAR-8000-10 - Command Injection 漏洞描述 D-Link DAR-8000-10 version has an operating system command injection vulnerability. The vulnerability origin...
2023年7月19日 11:09CVE-2025-2747: Kentico Xperience 13 CMS – Staging Service Authentication Bypass (WT-2025-0006)
漏洞标题 CVE-2025-2747: Kentico Xperience 13 CMS - Staging Service Authentication Bypass (WT-2025-0006) 漏洞描述 An authentication bypass vulnerability in Kentico Xperience allows ...
2025年4月15日 13:50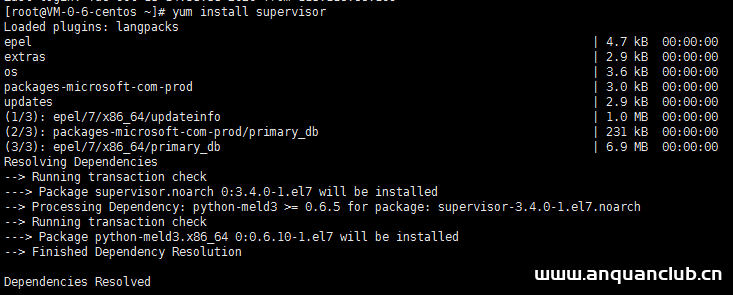
centos7下安装并配置supervisor守护程序的操作方法_Linux
这篇文章主要介绍了centos7下安装并配置supervisor守护程序的操作方法,本文通过图文并茂的形式给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 新手,...
2023年4月12日 21:09CVE-2023-2624: KiviCare WordPress Plugin – Cross-Site Scripting
漏洞标题 CVE-2023-2624: KiviCare WordPress Plugin - Cross-Site Scripting 漏洞描述 The KiviCare WordPress plugin before 3.2.1 does not sanitise and escape the 'filterType'...
2023年1月28日 07:34CVE-2018-17431: Comodo Unified Threat Management Web Console – Remote Code Execution
漏洞标题 CVE-2018-17431: Comodo Unified Threat Management Web Console - Remote Code Execution 漏洞描述 Comodo Firewall & Central Manager (UTM) All Release before 2.7.0 & 1....
2018年7月1日 03:00CVE-2020-23575: Kyocera Printer d-COPIA253MF – Directory Traversal
漏洞标题 CVE-2020-23575: Kyocera Printer d-COPIA253MF - Directory Traversal 漏洞描述 Kyocera Printer d-COPIA253MF plus is susceptible to a directory traversal vulnerability which c...
2020年3月18日 05:24CVE-2024-36837: CRMEB开源电商系统 /api/products SQL注入漏洞(CVE-2024-36837)
漏洞标题 CVE-2024-36837: CRMEB开源电商系统 /api/products SQL注入漏洞(CVE-2024-36837) 漏洞描述 该漏洞可以通过请求api的路径接口来进行SQL注入,进而可能导致敏感信息泄露,该注入可暴露后...
2024年12月28日 09:55
HBuilderX配置tomcat外部服务器查看编辑jsp界面的方法详解_Tomcat
这篇文章主要介绍了HBuilderX配置tomcat外部服务器查看编辑jsp界面的方法,本文通过实例图文相结合给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 一、...
2023年4月1日 20:29CVE-2024-36404: GeoServer and GeoTools – Remote Code Execution
漏洞标题 CVE-2024-36404: GeoServer and GeoTools - Remote Code Execution 漏洞描述 GeoTools is an open source Java library that provides tools for geospatial data. Prior to versions ...
2024年1月19日 23:50
斥资170亿美元,三星已决定于美国德州新建半导体厂
11月23日,韩国最大的跨国企业集团三星SAMSUNG在其官方网站上发布公告称,其将于美国德克萨斯州泰勒市斥资170亿美元新建一个半导体制造工厂。这是三星在美国有史以来的最大一次投资,至此,三星...
2022年3月10日 23:38CVE-2019-2767: Oracle Business Intelligence Publisher – XML External Entity Injection
漏洞标题 CVE-2019-2767: Oracle Business Intelligence Publisher - XML External Entity Injection 漏洞描述 Oracle Business Intelligence Publisher is vulnerable to an XML external enti...
2019年8月16日 14:20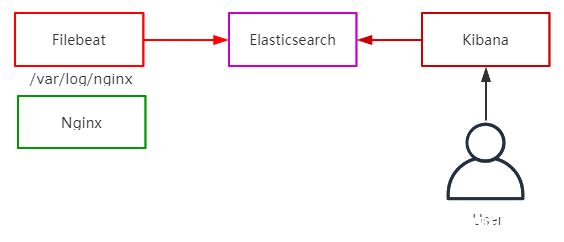
Filebeat 采集 Nginx 日志的方法_nginx
这篇文章主要介绍了Filebeat 采集 Nginx 日志的方法,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 Nginx 日志可用于分析用户地址位置,行为画像...
2023年3月26日 21:17CVE-2021-20123: Draytek VigorConnect 1.6.0-B – Local File Inclusion
漏洞标题 CVE-2021-20123: Draytek VigorConnect 1.6.0-B - Local File Inclusion 漏洞描述 Draytek VigorConnect 1.6.0-B3 is susceptible to local file inclusion in the file download func...
2021年1月31日 18:13CVE-2022-27228: Bitrix Site Manager – Remote Code Execution
漏洞标题 CVE-2022-27228: Bitrix Site Manager - Remote Code Execution 漏洞描述 In the vote (aka "Polls, Votes") module before 21.0.100 of Bitrix Site Manager, a remote una...
2022年8月12日 21:28
2026年11月7日 11:45
2026年11月6日 11:45
2026年11月5日 11:45
2026年11月4日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

