
最新发布第756页
【工具更新】EasyShell v1.7版本更新,修复诸多bug,同时新增诸多新功能
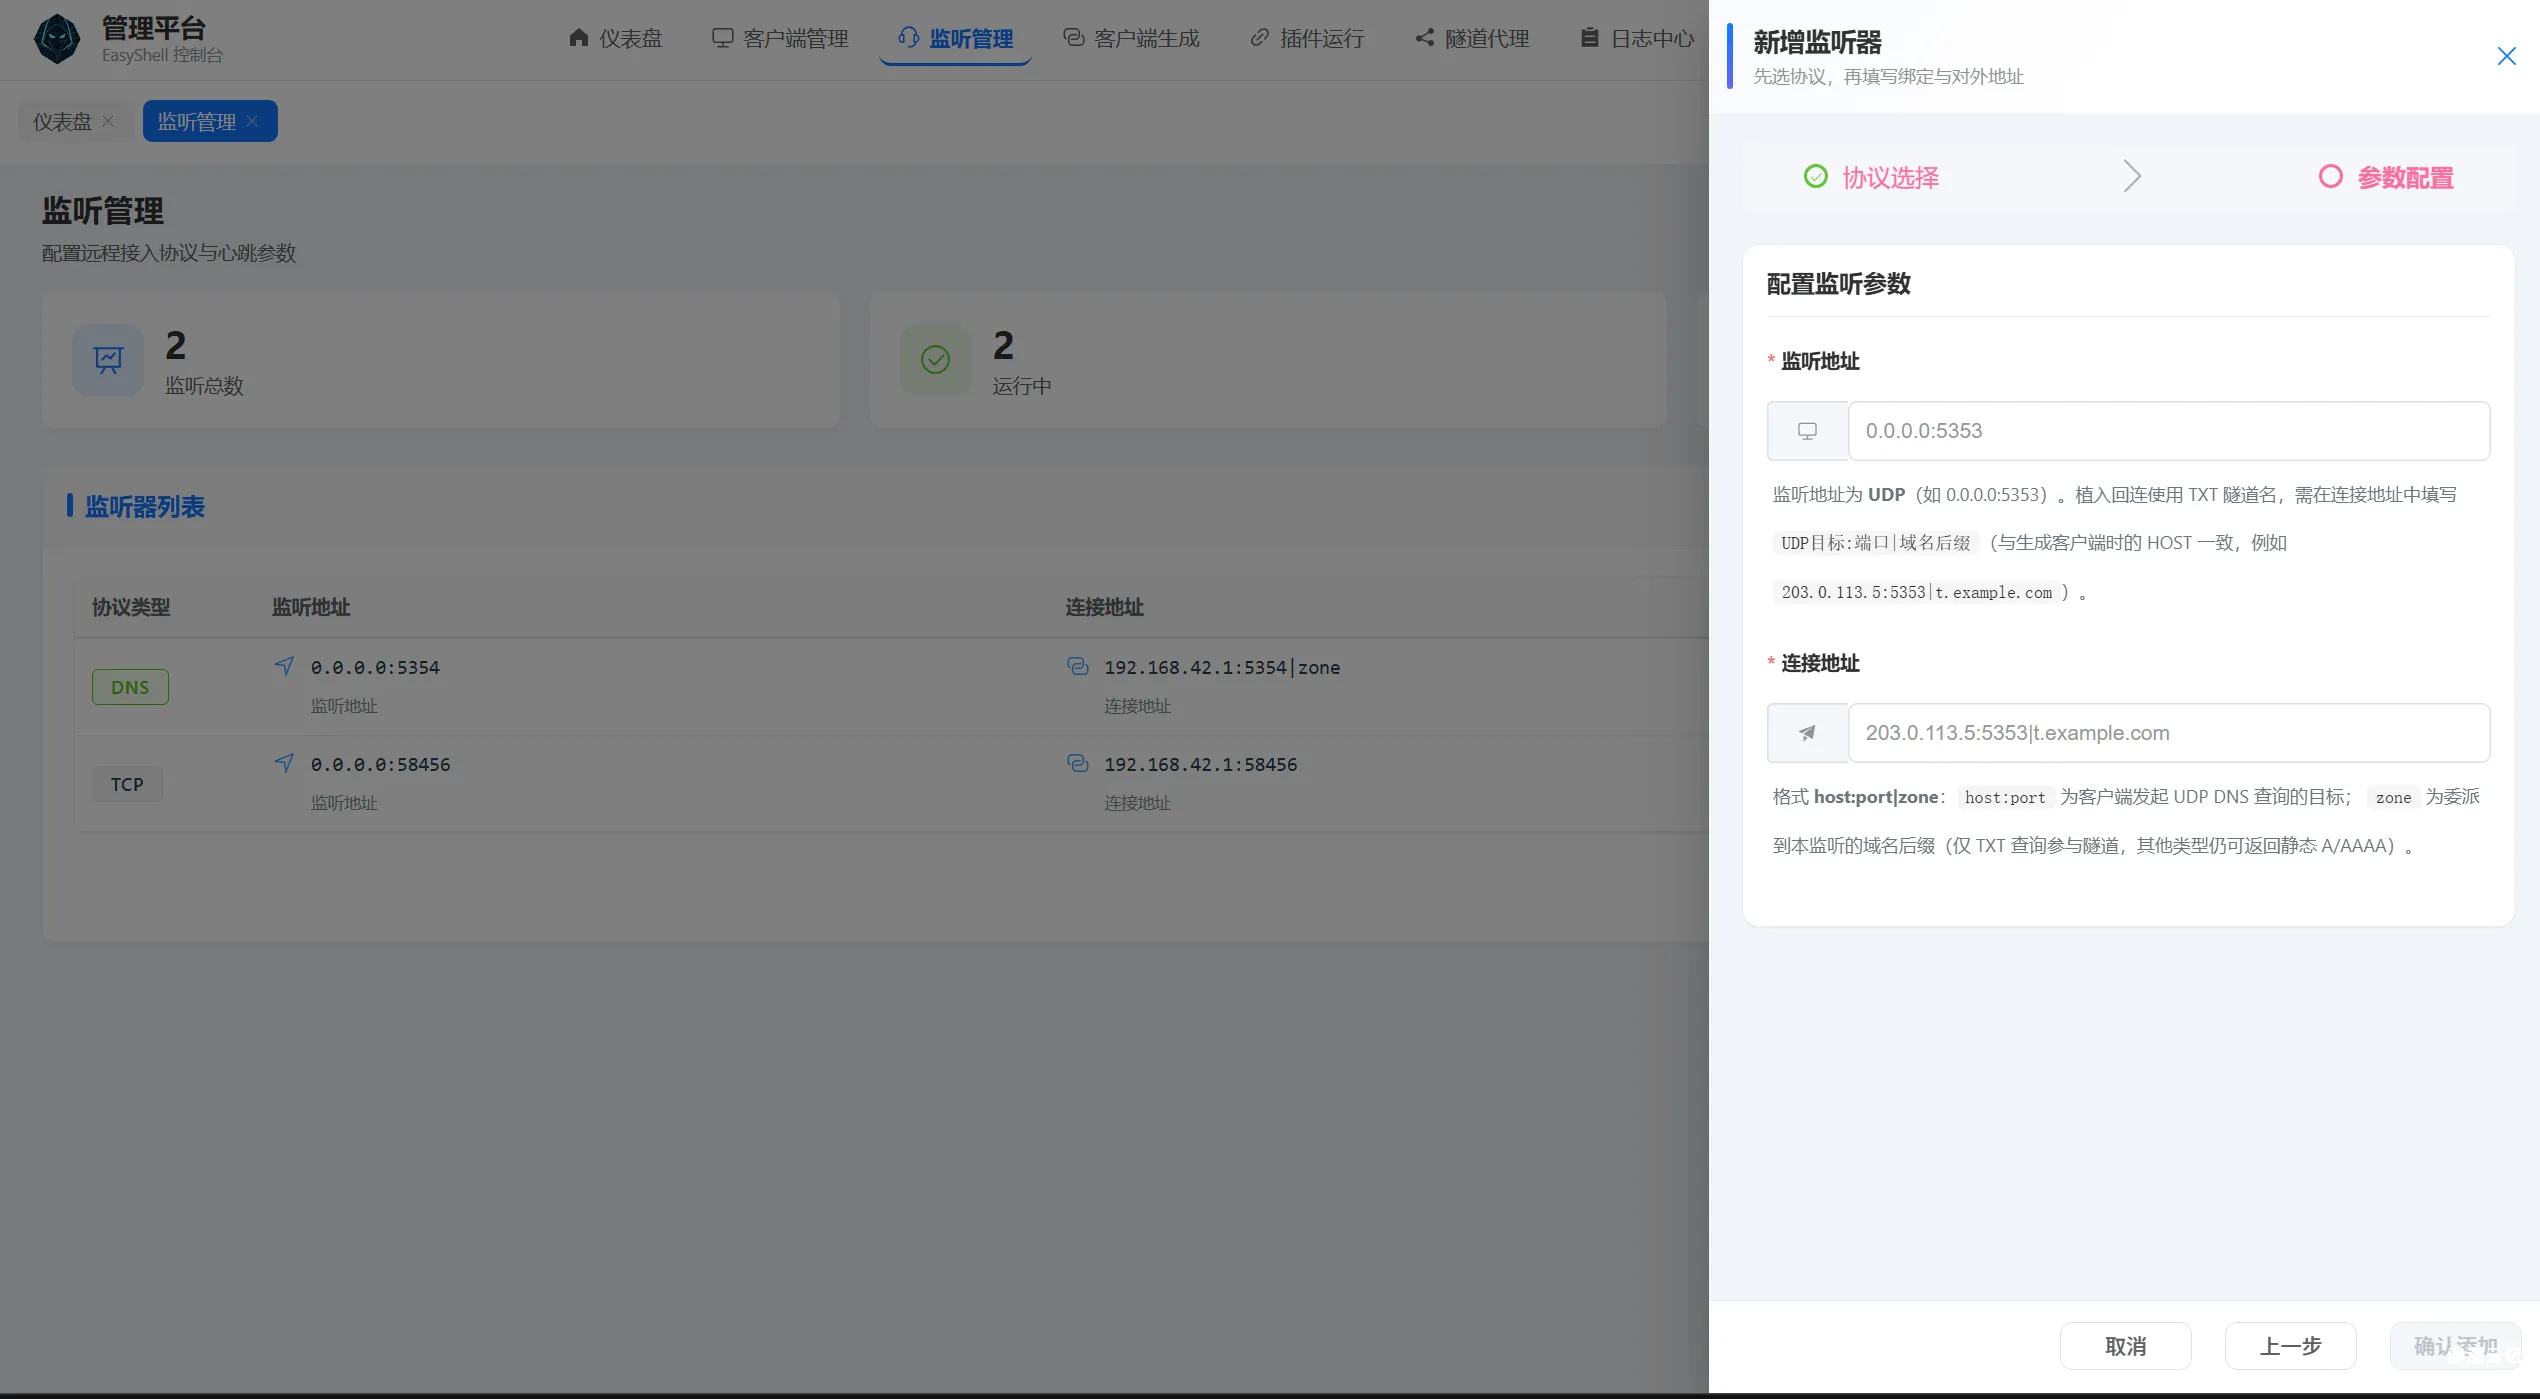
前言 听人劝,吃饱饭,师傅们说啥我加啥,经过一段时间的更新,新版本的EasyShell出来了,修复了诸多bug,同时也新增了诸多功能,在此进行一个更新说明。 新增DNS监听协议,支持DNS协议上线 优...

 2026年5月22日 18:36

CVE-2021-26855: Microsoft Exchange Server Remote Code Execution
漏洞标题 CVE-2021-26855: Microsoft Exchange Server Remote Code Execution 漏洞描述 Microsoft Exchange Server Remote Code Execution Vulnerability PoC代码
 2021年9月24日 23:05
Apache RocketMQ CVE-2023-33246 远程代码执行漏洞
漏洞标题 Apache RocketMQ CVE-2023-33246 远程代码执行漏洞 漏洞描述 Apache RocketMQ存在远程代码执行漏洞,此漏洞是由于对权限和用户输入校验不当导致的。 PoC代码 暂无
2023年7月7日 10:17CVE-2018-10738: Nagios XI before 5.4.13 SQL Inject
漏洞标题 CVE-2018-10738: Nagios XI before 5.4.13 SQL Inject 漏洞描述 Nagios XI before 5.4.13 SQL Inject PoC代码
2018年2月25日 09:38CVE-2017-12149: Java/Jboss Deserialization [RCE]
漏洞标题 CVE-2017-12149: Java/Jboss Deserialization [RCE] 漏洞描述 In Jboss Application Server as shipped with Red Hat Enterprise Application Platform 5.2, it was found that the do...
2017年6月28日 11:06CVE-2022-30525: Zyxel Firewall – OS Command Injection
漏洞标题 CVE-2022-30525: Zyxel Firewall - OS Command Injection 漏洞描述 An OS command injection vulnerability in the CGI program of Zyxel USG FLEX 100(W) firmware versions 5.00 thr...
2022年2月7日 17:47CVE-2023-43374: Hoteldruid v3.0.5 – SQL Injection
漏洞标题 CVE-2023-43374: Hoteldruid v3.0.5 - SQL Injection 漏洞描述 Hoteldruid v3.0.5 was discovered to contain a SQL injection vulnerability via the id_utente_log parameter at /ho...
2023年11月1日 17:34CVE-2022-0434: WordPress Page Views Count <2.4.15 - SQL Injection
漏洞标题 CVE-2022-0434: WordPress Page Views Count <2.4.15 - SQL Injection 漏洞描述 WordPress Page Views Count plugin prior to 2.4.15 contains an unauthenticated SQL injection v...
2022年1月10日 19:33CVE-2022-2756: Kavita <0.5.4.1 - Server-Side Request Forgery
漏洞标题 CVE-2022-2756: Kavita <0.5.4.1 - Server-Side Request Forgery 漏洞描述 Kavita before 0.5.4.1 is susceptible to server-side request forgery in GitHub repository kareadita...
2022年1月10日 22:08CVE-2017-11444: Subrion CMS <4.1.5.10 - SQL Injection
漏洞标题 CVE-2017-11444: Subrion CMS <4.1.5.10 - SQL Injection 漏洞描述 Subrion CMS before 4.1.5.10 has a SQL injection vulnerability in /front/search.php via the $_GET array. P...
2017年2月5日 04:55CVE-2018-3810: Oturia WordPress Smart Google Code Inserter <3.5 - Authentication Bypass
漏洞标题 CVE-2018-3810: Oturia WordPress Smart Google Code Inserter <3.5 - Authentication Bypass 漏洞描述 Oturia Smart Google Code Inserter plugin before 3.5 for WordPress allow...
2018年12月21日 08:41CVE-2018-7662: Couchcms 2.0 Dictionary Disclosure
漏洞标题 CVE-2018-7662: Couchcms 2.0 Dictionary Disclosure 漏洞描述 Couchcms 2.0 Dictionary Disclosure fofa: app="Couchcms" shodan: http.html:"Couchcms" PoC代码
2018年7月25日 13:36CVE-2023-32243: WordPress Elementor Lite 5.7.1 – Arbitrary Password Reset
漏洞标题 CVE-2023-32243: WordPress Elementor Lite 5.7.1 - Arbitrary Password Reset 漏洞描述 Improper Authentication vulnerability in WPDeveloper Essential Addons for Elementor allo...
2023年4月19日 12:13CVE-2018-11784: Apache Tomcat – Open Redirect
漏洞标题 CVE-2018-11784: Apache Tomcat - Open Redirect 漏洞描述 Apache Tomcat versions prior to 9.0.12, 8.5.34, and 7.0.91 are prone to an open-redirection vulnerability because it...
2018年10月31日 06:14
一个脚本让你的app自动吐出密钥信息
### 背景 安全小天地某个私密项目中涉及到一个app的测试,打开一看,证书校验--不让抓包,信息加密-无法篡改,遇到这种情况怎么,正常我这种小菜鸡都是直接放弃了,奈何厂家奖金给的高啊,我还...
2022年3月10日 23:36CVE-2020-25213: WordPress File Manager Plugin – Remote Code Execution
漏洞标题 CVE-2020-25213: WordPress File Manager Plugin - Remote Code Execution 漏洞描述 The WordPress File Manager plugin prior to version 6.9 is susceptible to remote code executi...
2020年11月30日 08:29
2026年9月20日 11:45
2026年9月19日 11:45
2026年9月18日 11:46
2026年9月17日 18:46
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

