
最新发布第757页

CVE-2023-46574: TOTOLINK A3700R – Command Injection
漏洞标题 CVE-2023-46574: TOTOLINK A3700R - Command Injection 漏洞描述 An issue in TOTOLINK A3700R v.9.1.2u.6165_20211012 allows a remote attacker to execute arbitrary code via the ...
 2023年12月21日 07:38
CVE-2018-9995: DVR Authentication Bypass
漏洞标题 CVE-2018-9995: DVR Authentication Bypass 漏洞描述 DVR,全称为Digital Video Recorder(硬盘录像机),即数字视频录像机。最初由阿根廷研究员发现,通过使用“Cookie: uid = admin”...
2018年3月22日 18:19CVE-2025-54309: CrushFTP – Authentication Bypass Race Condition
漏洞标题 CVE-2025-54309: CrushFTP - Authentication Bypass Race Condition 漏洞描述 CrushFTP 10 before 10.8.5 and 11 before 11.3.4_23, when the DMZ proxy feature is not used, mishand...
2025年4月24日 04:42spring4shell-CVE-2022-22965: Spring Framework RCE via Data Binding on JDK 9+
漏洞标题 spring4shell-CVE-2022-22965: Spring Framework RCE via Data Binding on JDK 9+ 漏洞描述 A Spring MVC or Spring WebFlux application running on JDK 9+ may be vulnerable to rem...
2022年12月7日 11:57CVE-2020-13820: Extreme Management Center 8.4.1.24 – Cross-Site Scripting
漏洞标题 CVE-2020-13820: Extreme Management Center 8.4.1.24 - Cross-Site Scripting 漏洞描述 Extreme Management Center 8.4.1.24 contains a cross-site scripting vulnerability via a p...
2020年11月25日 12:19CVE-2010-0219: Apache Axis2 Default Login
漏洞标题 CVE-2010-0219: Apache Axis2 Default Login 漏洞描述 Apache Axis2, as used in dswsbobje.war in SAP BusinessObjects Enterprise XI 3.2, CA ARCserve D2D r15, and other products...
2010年11月11日 04:38CVE-2016-10976: Safe Editor Plugin < 1.2 - CSS/JS-injection
漏洞标题 CVE-2016-10976: Safe Editor Plugin < 1.2 - CSS/JS-injection 漏洞描述 The safe-editor plugin before 1.2 for WordPress has no se_save authentication, with resultant XSS. ...
2016年12月10日 20:46
详解Linux服务器最多能开放多少个端口_Linux
本文主要介绍了Linux服务器最多能开放多少个端口,文中通过示例代码介绍的非常详细,具有一定的参考价值,感兴趣的小伙伴们可以参考一下 目录端口相关的概念:端口与服务的关系1:nmap工具检测...
2022年6月17日 10:04CVE-2022-22733: Apache ShardingSphere ElasticJob-UI privilege escalation
漏洞标题 CVE-2022-22733: Apache ShardingSphere ElasticJob-UI privilege escalation 漏洞描述 Exposure of Sensitive Information to an Unauthorized Actor vulnerability in Apache Shardi...
2022年8月20日 20:44CVE-2022-0250: Redirection for Contact Form 7 < 2.5.0 - Cross-Site Scripting
漏洞标题 CVE-2022-0250: Redirection for Contact Form 7 < 2.5.0 - Cross-Site Scripting 漏洞描述 The Redirection for Contact Form 7 WordPress plugin before 2.5.0 does not escape a...
2022年12月20日 09:07CVE-2022-28033: Atom.CMS 2.0 – SQL Injection
漏洞标题 CVE-2022-28033: Atom.CMS 2.0 - SQL Injection 漏洞描述 Atom.CMS 2.0 is vulnerable to SQL Injection via Atom.CMS_admin_uploads.php which allows an attacker to execute arbitr...
2022年12月1日 04:22CVE-2025-4009: Evertz SDVN 3080ipx-10G – Unauthenticated Arbitrary Command Injection
漏洞标题 CVE-2025-4009: Evertz SDVN 3080ipx-10G - Unauthenticated Arbitrary Command Injection 漏洞描述 The Evertz SDVN 3080ipx-10G is a High Bandwidth Ethernet Switching Fabric for...
2025年4月15日 05:15CVE-2014-4539: Movies <= 0.6 - Cross-Site Scripting
漏洞标题 CVE-2014-4539: Movies <= 0.6 - Cross-Site Scripting 漏洞描述 A cross-site scripting vulnerability in the Movies plugin 0.6 and earlier for WordPress allows remote attac...
2014年4月16日 09:34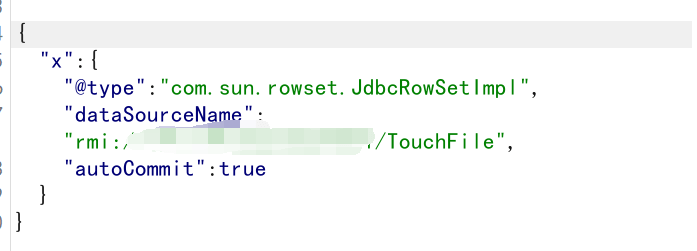
vulhub漏洞复现之fastjson1.2.47反弹shell
前言 现在java站越来越多啦,面试也基本上全部问的都是java呀,加油呀 什么是json? 借用人家的表达:“.json是用来存储简单的数据结构和对象的文件。json是一种轻量级的数据交换格式,基于ECMA...

 2023年8月18日 06:48
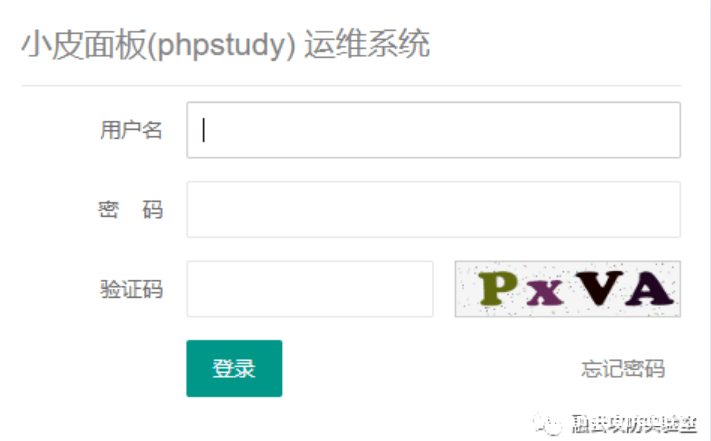
phpstudy面板XSS盲打_计划任务RCE漏洞
本文转载于公众号:融云攻防实验室,原文地址: 漏洞复现 phpstudy面板XSS盲打_计划任务RCE漏洞 PhpStudy国内12年老牌公益软件,集安全、高效、功能与一体,已获得全球用户认可安装,运维也高效...
2023年2月7日 17:21CVE-2021-31602: Hitachi Vantara Pentaho/Business Intelligence Server – Authentication Bypass
漏洞标题 CVE-2021-31602: Hitachi Vantara Pentaho/Business Intelligence Server - Authentication Bypass 漏洞描述 Hitachi Vantara Pentaho through 9.1 and Pentaho Business Intelligence...
2021年3月23日 16:28
2026年10月21日 11:45
2026年10月20日 11:45
2026年10月19日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

