
最新发布第763页
Windows 安装和配置 WSL的方法步骤_win服务器
这篇文章主要介绍了Windows 安装和配置 WSL的方法步骤,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编来一起学习学习吧 什么是 WSL ...
 2026年3月18日 11:45

CVE-2022-0288: WordPress Ad Inserter <2.7.10 - Cross-Site Scripting
漏洞标题 CVE-2022-0288: WordPress Ad Inserter <2.7.10 - Cross-Site Scripting 漏洞描述 WordPress Ad Inserter plugin before 2.7.10 contains a cross-site scripting vulnerability. I...
2022年10月31日 10:42CVE-2019-5129: YouPHPTube Encoder 2.3 – Command Injection
漏洞标题 CVE-2019-5129: YouPHPTube Encoder 2.3 - Command Injection 漏洞描述 Exploitable unauthenticated command injections exist in YouPHPTube Encoder 2.3 a plugin for providing en...
2019年12月5日 03:31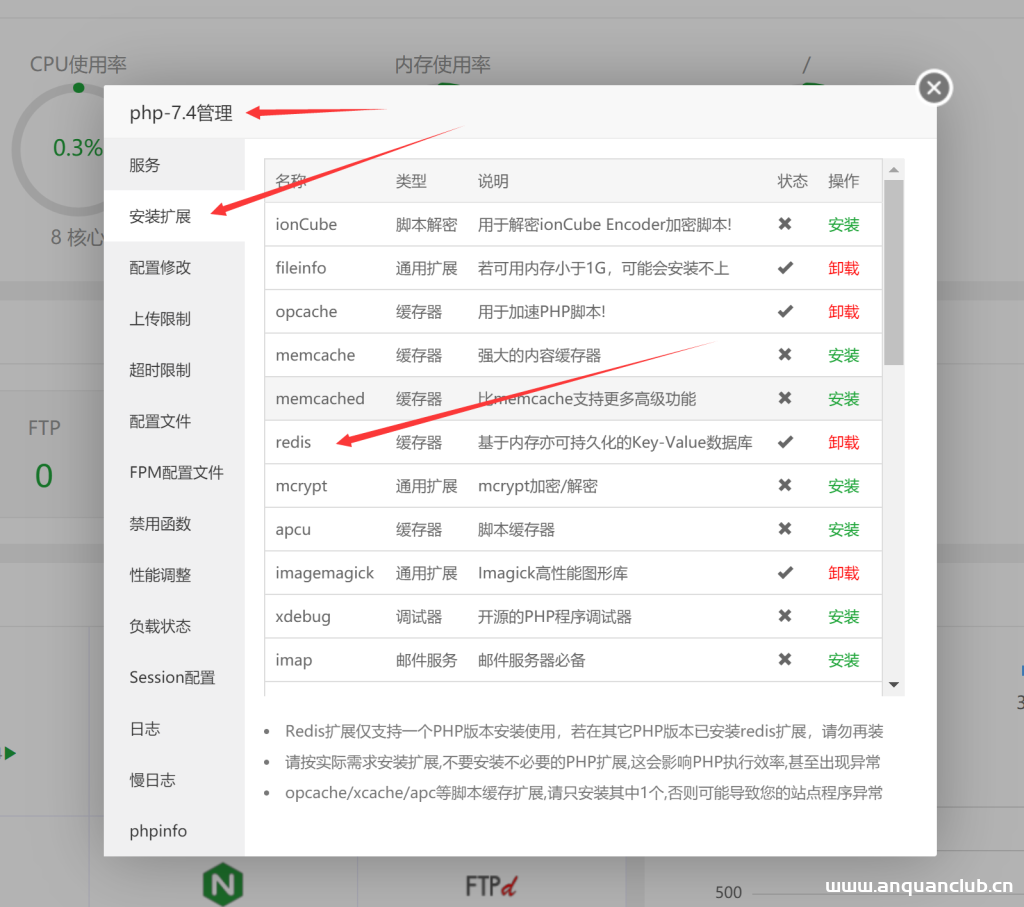
wordpress网站使用Redis缓存和PHP opcache为网站加速详细图文教程
相信建站的朋友都十分关心网站速度问题了,子比主题一直在强调极速优化这次词语,同时在之前的很多文章中我也简单的介绍了子比主题的关于速度优化的一些原理。理论上来讲使用子比主题搭配一个不...

 2022年5月20日 20:05
CVE-2023-4115: PHPJabbers Cleaning Business 1.0 – Cross-Site Scripting
漏洞标题 CVE-2023-4115: PHPJabbers Cleaning Business 1.0 - Cross-Site Scripting 漏洞描述 The attacker can send to victim a link containing a malicious URL in an email or instant me...
2023年6月5日 07:54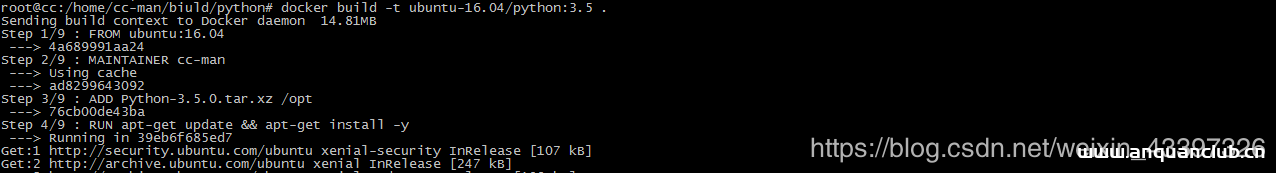
Docker制作Python运行环境基础镜像的方法步骤_docker
这篇文章主要介绍了Docker制作Python运行环境基础镜像的方法步骤,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编来一起学习学习吧 一...
2024年7月14日 20:14CVE-2020-35847: Agentejo Cockpit <0.11.2 - NoSQL Injection
漏洞标题 CVE-2020-35847: Agentejo Cockpit <0.11.2 - NoSQL Injection 漏洞描述 Agentejo Cockpit before 0.11.2 allows NoSQL injection via the Controller/Auth.php resetpassword func...
2020年3月24日 17:39CVE-2024-8852: All-in-One WP Migration < 7.87 - Unauthenticated Information Disclosure
漏洞标题 CVE-2024-8852: All-in-One WP Migration < 7.87 - Unauthenticated Information Disclosure 漏洞描述 The All-in-One WP Migration and Backup plugin for WordPress is vulnerabl...
2024年1月15日 01:20CVE-2025-64525: Astro – Broken Access Control
漏洞标题 CVE-2025-64525: Astro - Broken Access Control 漏洞描述 Astro 2.16.0 to 5.15.5 contains a broken access control caused by insecure use of unsanitized x-forwarded-proto and ...
2025年11月30日 11:54CVE-2021-29490: Jellyfin 10.7.2 – Server Side Request Forgery
漏洞标题 CVE-2021-29490: Jellyfin 10.7.2 - Server Side Request Forgery 漏洞描述 Jellyfin is a free software media system. Versions 10.7.2 and below are vulnerable to unauthenticate...
2021年6月14日 14:16CVE-2022-23131: Zabbix – SAML SSO Authentication Bypass
漏洞标题 CVE-2022-23131: Zabbix - SAML SSO Authentication Bypass 漏洞描述 When SAML SSO authentication is enabled (non-default), session data can be modified by a malicious actor b...
2022年10月18日 15:02
记一次修改前端时间导致的未授权
发现之前 在前段时间看到了好像是一个支付宝的漏洞那个人修改了电脑的时间然后可以提前秒杀抢购商品,于是这个洞在弟弟我的心里深深的记住了,于是就有了后面的发现 发现过程 在刚刚加入火线某...
2022年3月10日 23:29CVE-2019-17233: WordPress Ultimate FAQs <= 1.8.24 – Unauthenticated HTML Content Injection
漏洞标题 CVE-2019-17233: WordPress Ultimate FAQs <= 1.8.24 – Unauthenticated HTML Content Injection 漏洞描述 Functions/EWD_UFAQ_Import.php in the ultimate-faqs plugin through 1...
2019年11月4日 07:10CVE-2021-24214: WordPress OpenID Connect Generic Client 3.8.0-3.8.1 – Cross-Site Scripting
漏洞标题 CVE-2021-24214: WordPress OpenID Connect Generic Client 3.8.0-3.8.1 - Cross-Site Scripting 漏洞描述 WordPress OpenID Connect Generic Client plugin 3.8.0 and 3.8.1 contains...
2021年4月24日 17:27CVE-2016-1000141: WordPress Page Layout builder v1.9.3 – Cross-Site Scripting
漏洞标题 CVE-2016-1000141: WordPress Page Layout builder v1.9.3 - Cross-Site Scripting 漏洞描述 WordPress plugin Page-layout-builder v1.9.3 contains a cross-site scripting vulnerab...
2016年10月9日 11:21CVE-2025-52970: Fortinet FortiWeb – Authentication Bypass to Admin Privilege
漏洞标题 CVE-2025-52970: Fortinet FortiWeb - Authentication Bypass to Admin Privilege 漏洞描述 A improper handling of parameters in Fortinet FortiWeb versions 7.6.3 and below, vers...
2025年5月16日 19:57
2026年9月19日 11:45
2026年9月18日 11:46
2026年9月17日 18:46
2026年9月17日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月17日 18:19
2026年8月16日 20:18
2026年8月11日 13:39
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

