
最新发布第764页

CVE-2022-0968: Microweber <1.2.12 - Integer Overflow
漏洞标题 CVE-2022-0968: Microweber <1.2.12 - Integer Overflow 漏洞描述 Microweber before 1.2.12 is susceptible to integer overflow. The application allows large characters to in...
 2022年10月12日 02:25

CentOS7下安装yum源及上传下载命令rz、sz安装方法(图解)_Linux
这篇文章主要介绍了CentOS7下安装yum源及上传下载命令rz、sz安装方法,本文通过图文并茂的形式给大家介绍的非常详细,具有一定的参考借鉴价值,需要的朋友可以参考下 ** CentOS7下安装yum源及上...
2026年9月6日 11:45CVE-2018-13380: Fortinet FortiOS – Cross-Site Scripting
漏洞标题 CVE-2018-13380: Fortinet FortiOS - Cross-Site Scripting 漏洞描述 Fortinet FortiOS 6.0.0 to 6.0.4, 5.6.0 to 5.6.7, 5.4.0 to 5.4.12, 5.2 and below versions under SSL VPN web...
2018年1月28日 10:19
在VMware虚拟机中安装windowsserver2016步骤详解(附激活教程及激活码)
前言 去msdn上面找了一下这个资源,给了一个种子链接,明明记得以前百度网盘可以下载的,结果这次就是不行,无奈下载一个迅雷,结果告诉我没会员不能下载,我都去搜索资源了,怎么可能还去付费...

 2026年3月27日 14:57
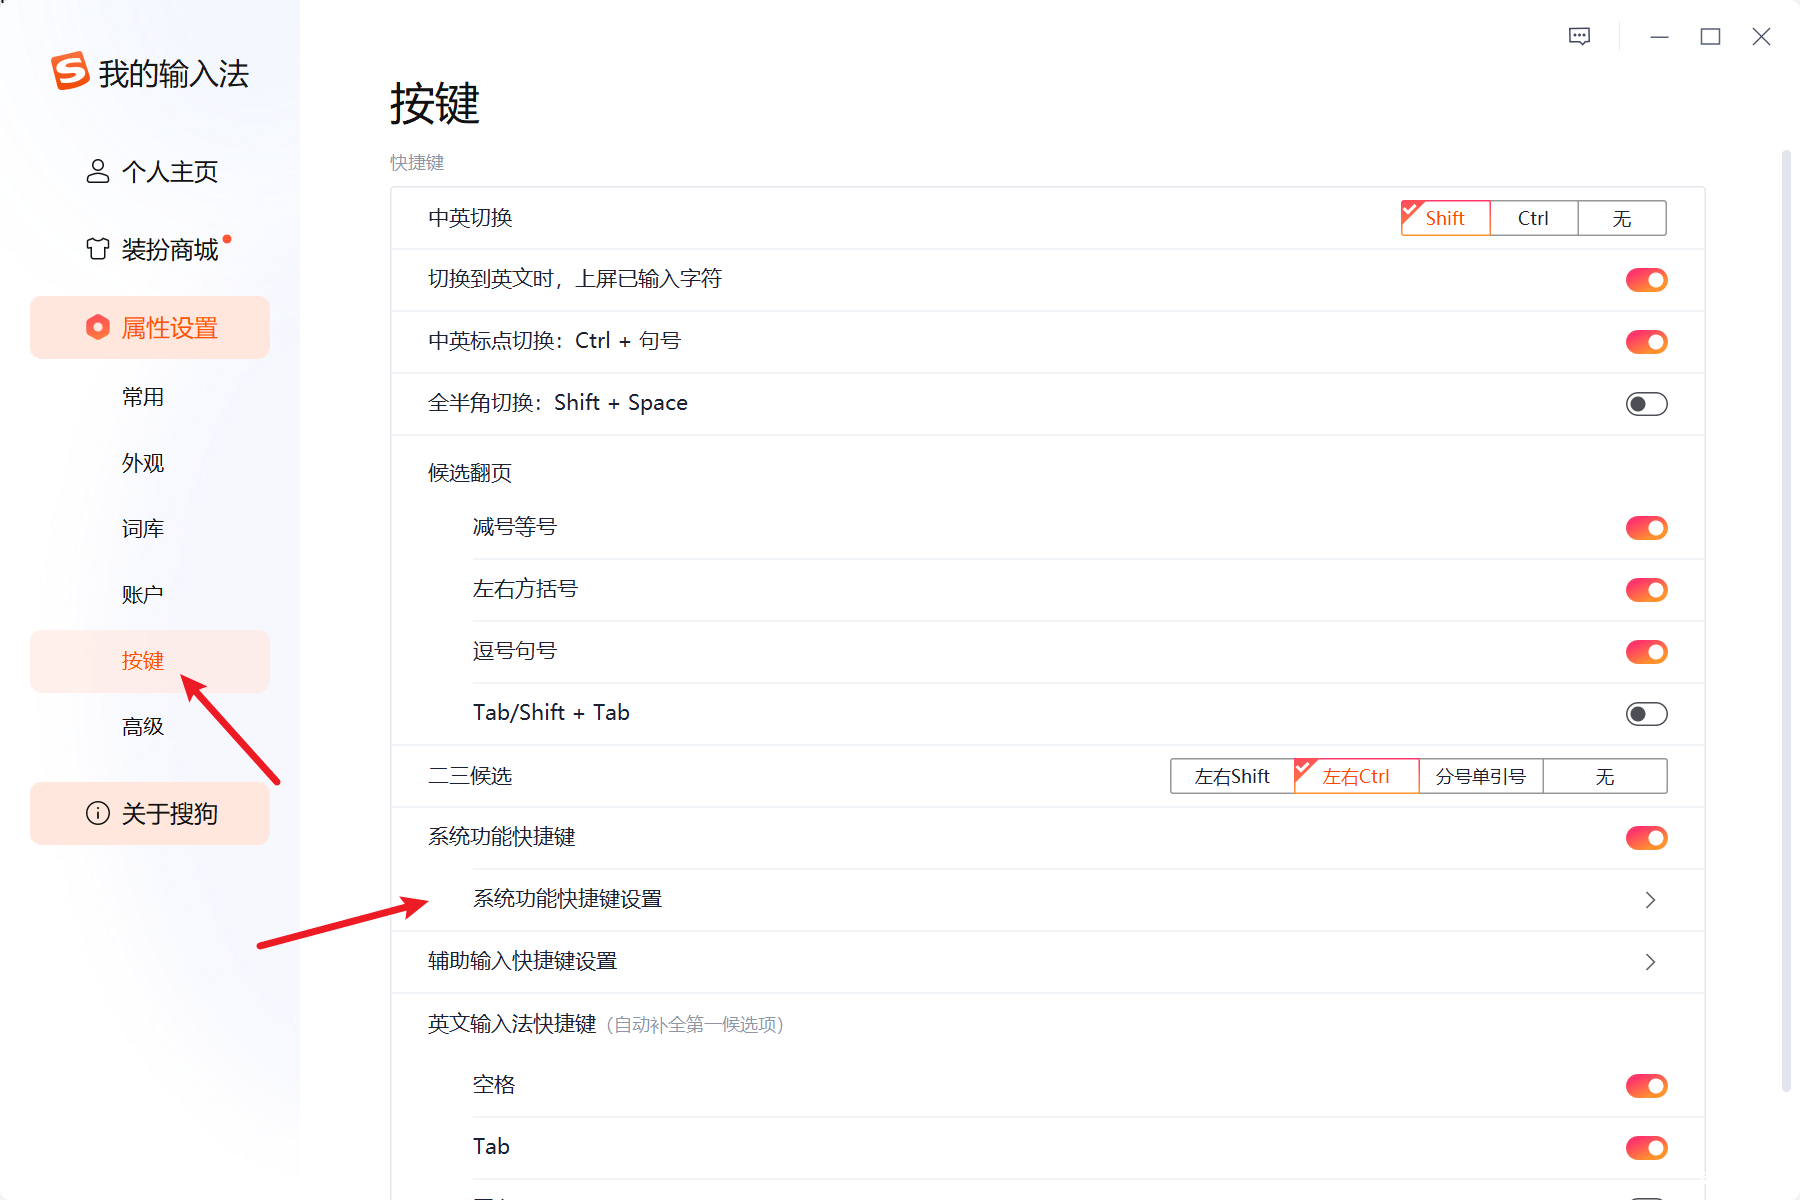
PhpStorm 快捷键Ctrl+Shift+F失效的解决办法
问题 在使用PhpStorm、idea等开发工具的时间,咱们想进行快速文件搜索通常会使用Ctrl+Shift+F 但是有些情况下怎么按都没有出现搜索界面,这个情况下通常是快捷键占用导致的 解决办法 方法一 首...
2024年2月8日 11:17CVE-2019-18393: Ignite Realtime Openfire <4.42 - Local File Inclusion
漏洞标题 CVE-2019-18393: Ignite Realtime Openfire <4.42 - Local File Inclusion 漏洞描述 Ignite Realtime Openfire through 4.4.2 is vulnerable to local file inclusion via PluginSe...
2019年6月12日 05:18CVE-2020-24312: WordPress Plugin File Manager (wp-file-manager) Backup Disclosure
漏洞标题 CVE-2020-24312: WordPress Plugin File Manager (wp-file-manager) Backup Disclosure 漏洞描述 mndpsingh287 WP File Manager v6.4 and lower fails to restrict external access to...
2020年7月8日 16:16CVE-2022-44290: WebTareas 2.4p5 – SQL Injection
漏洞标题 CVE-2022-44290: WebTareas 2.4p5 - SQL Injection 漏洞描述 webTareas 2.4p5 was discovered to contain a SQL injection vulnerability via the id parameter in deleteapprovalstag...
2022年3月20日 20:10CVE-2024-8877: Riello Netman 204 – SQL Injection
漏洞标题 CVE-2024-8877: Riello Netman 204 - SQL Injection 漏洞描述 The three endpoints /cgi-bin/db_datalog_w.cgi, /cgi-bin/db_eventlog_w.cgi, and /cgi-bin/db_multimetr_w.cgi are vu...
2024年4月20日 08:27CVE-2022-24681: ManageEngine ADSelfService Plus <6121 - Stored Cross-Site Scripting
漏洞标题 CVE-2022-24681: ManageEngine ADSelfService Plus <6121 - Stored Cross-Site Scripting 漏洞描述 ManageEngine ADSelfService Plus before 6121 contains a stored cross-site sc...
2022年2月13日 03:51
Linux read命令的使用_Linux
这篇文章主要介绍了Linux read命令的使用,帮助大家更好的理解和学习Linux,感兴趣的朋友可以了解下 1.命令简介 read命令是Shell内建命令,用于从标准输入或-u选项指定的文件描述符中读取单行,...
2023年7月27日 20:54Adobe Commerce CVE-2024-34102 XML外部实体注入漏洞
漏洞标题 Adobe Commerce CVE-2024-34102 XML外部实体注入漏洞 漏洞描述 Adobe Commerce 存在XML外部实体注入漏洞,此漏洞是由于程序未充分验证用户输入estimate-shipping-methods的数据所导致...
2024年1月21日 12:53CVE-2020-9376: DLink dir610 credentials dump
漏洞标题 CVE-2020-9376: DLink dir610 credentials dump 漏洞描述 D-Link DIR-610 devices allow Information Disclosure via SERVICES=DEVICE.ACCOUNT%0AAUTHORIZED_GROUP=1 to getcfg.php. N...
2020年5月19日 05:11CVE-2019-9082: ThinkPHP < 3.2.4 - Remote Code Execution
漏洞标题 CVE-2019-9082: ThinkPHP < 3.2.4 - Remote Code Execution 漏洞描述 ThinkPHP before 3.2.4, as used in Open Source BMS v1.1.1 and other products, allows Remote Command Exec...
2019年5月22日 22:23CVE-2018-5233: Grav CMS <1.3.0 - Cross-Site Scripting
漏洞标题 CVE-2018-5233: Grav CMS <1.3.0 - Cross-Site Scripting 漏洞描述 Grav CMS before 1.3.0 is vulnerable to cross-site scripting via system/src/Grav/Common/Twig/Twig.php and ...
2018年5月24日 16:40CVE-2021-20123: Draytek VigorConnect 1.6.0-B – Local File Inclusion
漏洞标题 CVE-2021-20123: Draytek VigorConnect 1.6.0-B - Local File Inclusion 漏洞描述 Draytek VigorConnect 1.6.0-B3 is susceptible to local file inclusion in the file download func...
2021年12月11日 13:28
2026年11月7日 11:45
2026年11月6日 11:45
2026年11月5日 11:45
2026年11月4日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

