
最新发布第767页

CVE-2025-2747: Kentico Xperience 13 CMS – Staging Service Authentication Bypass (WT-2025-0006)
漏洞标题 CVE-2025-2747: Kentico Xperience 13 CMS - Staging Service Authentication Bypass (WT-2025-0006) 漏洞描述 An authentication bypass vulnerability in Kentico Xperience allows ...
 2025年3月26日 01:12
CVE-2010-1533: Joomla! Component TweetLA 1.0.1 – Local File Inclusion
漏洞标题 CVE-2010-1533: Joomla! Component TweetLA 1.0.1 - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the TweetLA (com_tweetla) component 1.0.1 for Joomla!...
2010年1月13日 18:53Atlassian Jira 信息泄露(CVE-2019-3401)
漏洞标题 Atlassian Jira 信息泄露(CVE-2019-3401) 漏洞描述 Jira 7.13.3之前版本和8.1.1之前版本8.0.0中的ManageFilters.jspa资源允许远程攻击者通过不正确的授权检查枚举用户名。 PoC代码 暂...
2019年9月2日 12:42CVE-2020-11450: MicroStrategy Web 10.4 – Information Disclosure
漏洞标题 CVE-2020-11450: MicroStrategy Web 10.4 - Information Disclosure 漏洞描述 MicroStrategy Web 10.4 is susceptible to information disclosure. The JVM configuration, CPU archit...
2020年1月19日 04:10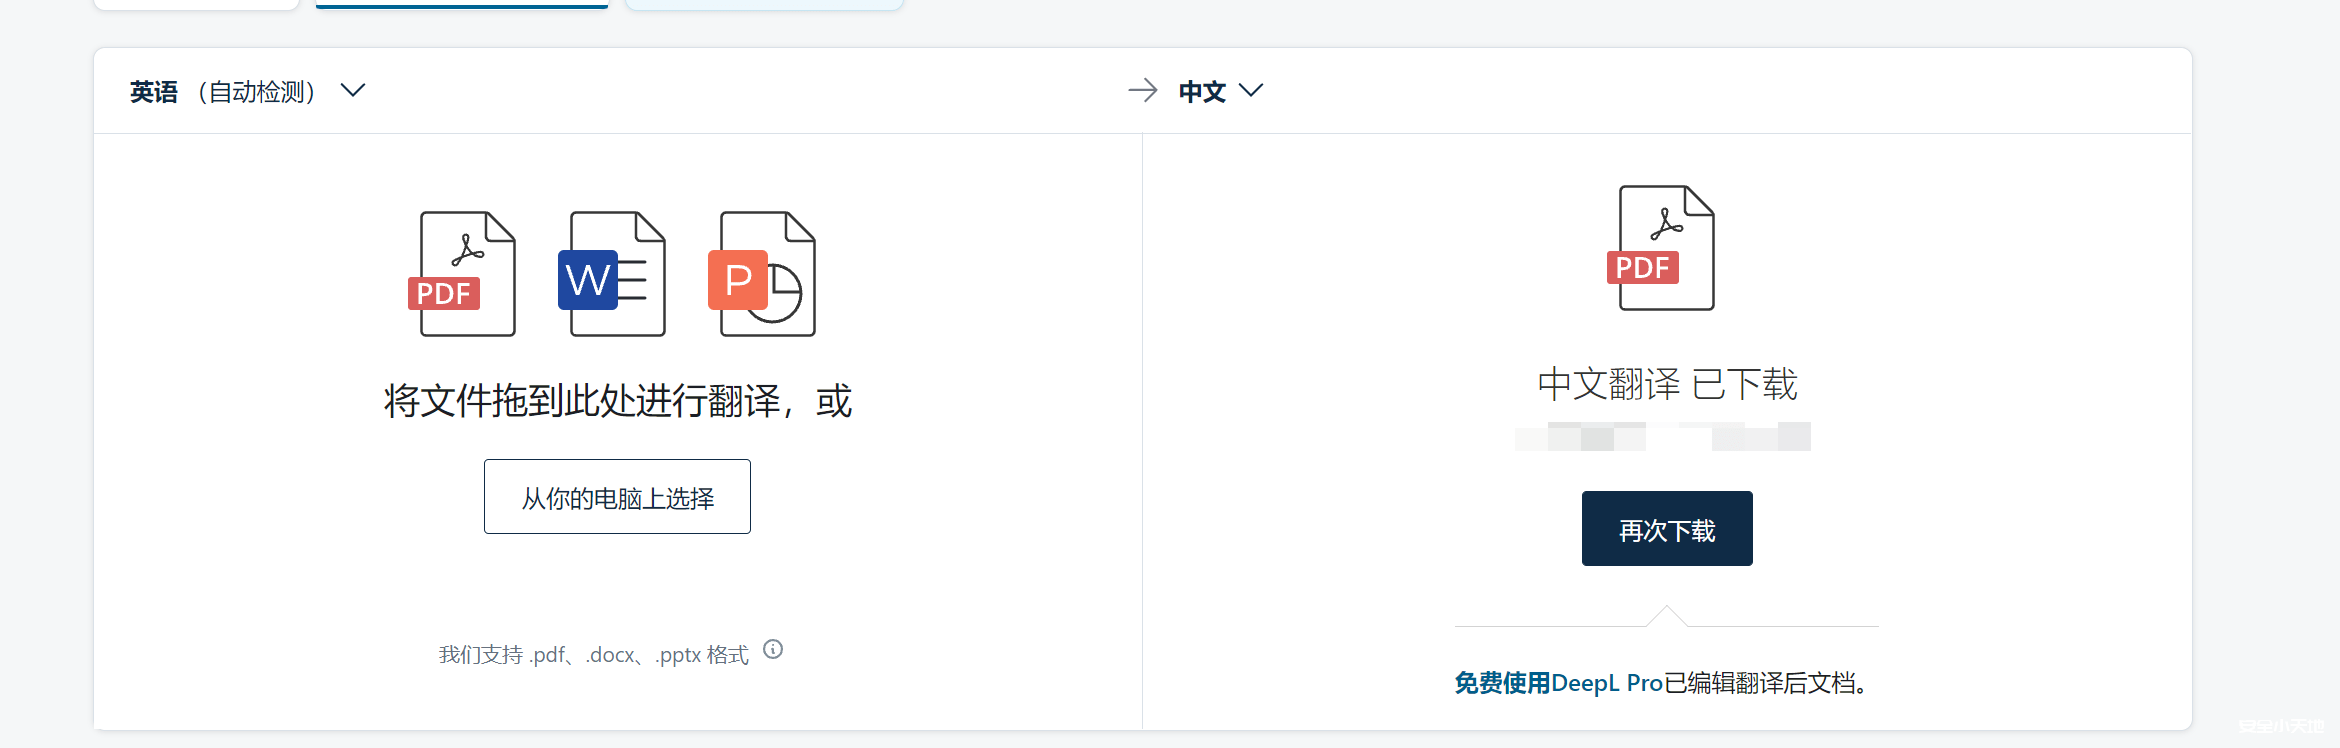
解决从DeepL翻译之后的pdf存在密码,无法复制编辑等问题
原文翻译 首先咱们使用deepl翻译对pdf进行转换翻译 下载翻译后的文件 打开咱可以发现 存在加密情况,没办法进行修改,复制等操作 解决办法 打开网址:http://www.ilovepdf.com/zh-cn 选择PDF解...

 2024年5月14日 11:47
CVE-2010-0985: Joomla! Component com_abbrev – Local File Inclusion
漏洞标题 CVE-2010-0985: Joomla! Component com_abbrev - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the Abbreviations Manager (com_abbrev) component 1.1 for...
2010年8月4日 04:34CVE-2019-7238: NEXUS < 3.14.0 Remote Code Execution
漏洞标题 CVE-2019-7238: NEXUS < 3.14.0 Remote Code Execution 漏洞描述 body="Nexus Repository Manager" app="Nexus-Repository-Manager" PoC代码
2019年5月20日 22:48CVE-2022-29303: SolarView Compact 6.00 – OS Command Injection
漏洞标题 CVE-2022-29303: SolarView Compact 6.00 - OS Command Injection 漏洞描述 SolarView Compact 6.00 was discovered to contain a command injection vulnerability via conf_mail.php...
2022年2月22日 02:01CVE-2023-34020: Uncanny Toolkit for LearnDash – Open Redirection
漏洞标题 CVE-2023-34020: Uncanny Toolkit for LearnDash - Open Redirection 漏洞描述 A vulnerability in the WordPress Uncanny Toolkit for LearnDash Plugin allowed malicious actors to...
2023年3月8日 18:16CVE-2022-45808: LearnPress Plugin < 4.2.0 - Unauthenticated Time-Based Blind SQLi
漏洞标题 CVE-2022-45808: LearnPress Plugin < 4.2.0 - Unauthenticated Time-Based Blind SQLi 漏洞描述 SQL Injection vulnerability in LearnPress – WordPress LMS Plugin <= 4.1.7...
2022年7月4日 02:00CVE-2025-34027: Versa Concerto API Path Based – Authentication Bypass
漏洞标题 CVE-2025-34027: Versa Concerto API Path Based - Authentication Bypass 漏洞描述 Authentication bypass in the Versa Concerto API, caused by URL decoding inconsistencies. It ...
2025年12月18日 23:15CVE-2020-35847: Agentejo Cockpit <0.11.2 - NoSQL Injection
漏洞标题 CVE-2020-35847: Agentejo Cockpit <0.11.2 - NoSQL Injection 漏洞描述 Agentejo Cockpit before 0.11.2 allows NoSQL injection via the Controller/Auth.php resetpassword func...
2020年1月23日 14:43
泛微OA 多个漏洞介绍
0x02 漏洞描述 本文转载于公众号:融云攻防实验室,原文地址: 漏洞复现 泛微OA E-Cology getdata.jsp SQL注入漏洞 本文转载于公众号:融云攻防实验室,原文地址: 漏洞复现 泛微OA E-Cology Lo...
2023年2月10日 14:03CVE-2023-6380: OpenCms 14 & 15 – Open Redirect
漏洞标题 CVE-2023-6380: OpenCms 14 & 15 - Open Redirect 漏洞描述 Open redirect vulnerability has been found in the Open CMS product affecting versions 14 and 15 of the 'Me...
2023年5月24日 22:41CVE-2018-1273 Spring Data Commons 远程命令执行
漏洞标题 CVE-2018-1273 Spring Data Commons 远程命令执行 漏洞描述 Pivotal Spring Data Commons和Spring Data REST都是美国Pivotal Software公司的产品。PivotalSpring Data Commons是一个为...
2018年7月8日 15:20CVE-2024-37728: OfficeWeb365 Indexs Interface – Arbitrary File Read
漏洞标题 CVE-2024-37728: OfficeWeb365 Indexs Interface - Arbitrary File Read 漏洞描述 There is any file reading in the officeWeb365 Indexs interface. PoC代码
2024年7月26日 21:53
2026年11月7日 11:45
2026年11月6日 11:45
2026年11月5日 11:45
2026年11月4日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

