
最新发布第768页

CVE-2025-24799: GLPI < 10.0.17 - Pre-Auth SQL Injection
漏洞标题 CVE-2025-24799: GLPI < 10.0.17 - Pre-Auth SQL Injection 漏洞描述 A pre-authentication SQL injection vulnerability exists in the Inventory feature of GLPI. The vulnerabi...
 2025年6月8日 17:01
CVE-2010-2122: Joomla! Component simpledownload <=0.9.5 - Arbitrary File Retrieval
漏洞标题 CVE-2010-2122: Joomla! Component simpledownload <=0.9.5 - Arbitrary File Retrieval 漏洞描述 A directory traversal vulnerability in the SimpleDownload (com_simpledownloa...
2010年10月15日 03:59
【技术分享】去除logo免费生成网站的水印 方法通用
声明 本文章仅供技术科普,对案例中涉及的网站并无恶意,如需原图,请前往官网下载!!! 请勿用作非法用途,如有违反,概不负责!如有侵权,联系站长! 相关阅读 案例 1、打开百度,搜索logo在...

 2023年1月13日 19:10
CVE-2021-25282: SaltStack Salt Unautherenticated Remote Command Execution
漏洞标题 CVE-2021-25282: SaltStack Salt Unautherenticated Remote Command Execution 漏洞描述 An issue was discovered in through SaltStack Salt before 3002.5. The salt.wheel.pillar_r...
2021年5月3日 13:26CVE-2022-23779: Zoho ManageEngine – Internal Hostname Disclosure
漏洞标题 CVE-2022-23779: Zoho ManageEngine - Internal Hostname Disclosure 漏洞描述 Zoho ManageEngine Desktop Central before 10.1.2137.8 exposes the installed server name to anyone....
2022年12月8日 21:46CVE-2023-27847: PrestaShop xipblog – SQL Injection
漏洞标题 CVE-2023-27847: PrestaShop xipblog - SQL Injection 漏洞描述 In the blog module (xipblog), an anonymous user can perform SQL injection. Even though the module has been patc...
2023年6月8日 14:04CVE-2022-47003: Mura CMS <10.0.580 - Authentication Bypass
漏洞标题 CVE-2022-47003: Mura CMS <10.0.580 - Authentication Bypass 漏洞描述 Mura CMS before 10.0.580 is susceptible to authentication bypass in the Remember Me function. An att...
2022年11月15日 20:23CVE-2022-23131: Zabbix – SAML SSO Authentication Bypass
漏洞标题 CVE-2022-23131: Zabbix - SAML SSO Authentication Bypass 漏洞描述 When SAML SSO authentication is enabled (non-default), session data can be modified by a malicious actor b...
2022年9月2日 16:24CVE-2021-24300: WordPress WooCommerce <1.13.22 - Cross-Site Scripting
漏洞标题 CVE-2021-24300: WordPress WooCommerce <1.13.22 - Cross-Site Scripting 漏洞描述 WordPress WooCommerce before 1.13.22 contains a reflected cross-site scripting vulnerabil...
2021年3月2日 18:24CVE-2010-1603: Joomla! Component ZiMBCore 0.1 – Local File Inclusion
漏洞标题 CVE-2010-1603: Joomla! Component ZiMBCore 0.1 - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the ZiMB Core (aka ZiMBCore or com_zimbcore) component...
2010年5月28日 06:12CVE-2021-31602: Hitachi Vantara Pentaho/Business Intelligence Server – Authentication Bypass
漏洞标题 CVE-2021-31602: Hitachi Vantara Pentaho/Business Intelligence Server - Authentication Bypass 漏洞描述 Hitachi Vantara Pentaho through 9.1 and Pentaho Business Intelligence...
2021年6月5日 17:59CVE-2023-2518: WordPress Easy Forms for Mailchimp Plugin < 6.8.9 - Cross-Site Scripting
漏洞标题 CVE-2023-2518: WordPress Easy Forms for Mailchimp Plugin < 6.8.9 - Cross-Site Scripting 漏洞描述 The Easy Forms for Mailchimp plugin before version 6.8.9 contains a ref...
2023年8月20日 19:07Atlassian Confluence Data Center and Server CVE-2024-21683 远程代码执行漏洞
漏洞标题 Atlassian Confluence Data Center and Server CVE-2024-21683 远程代码执行漏洞 漏洞描述 Atlassian Confluence Data Center and Server存在远程代码执行漏洞,此漏洞是程序对用户输...
2024年7月1日 20:46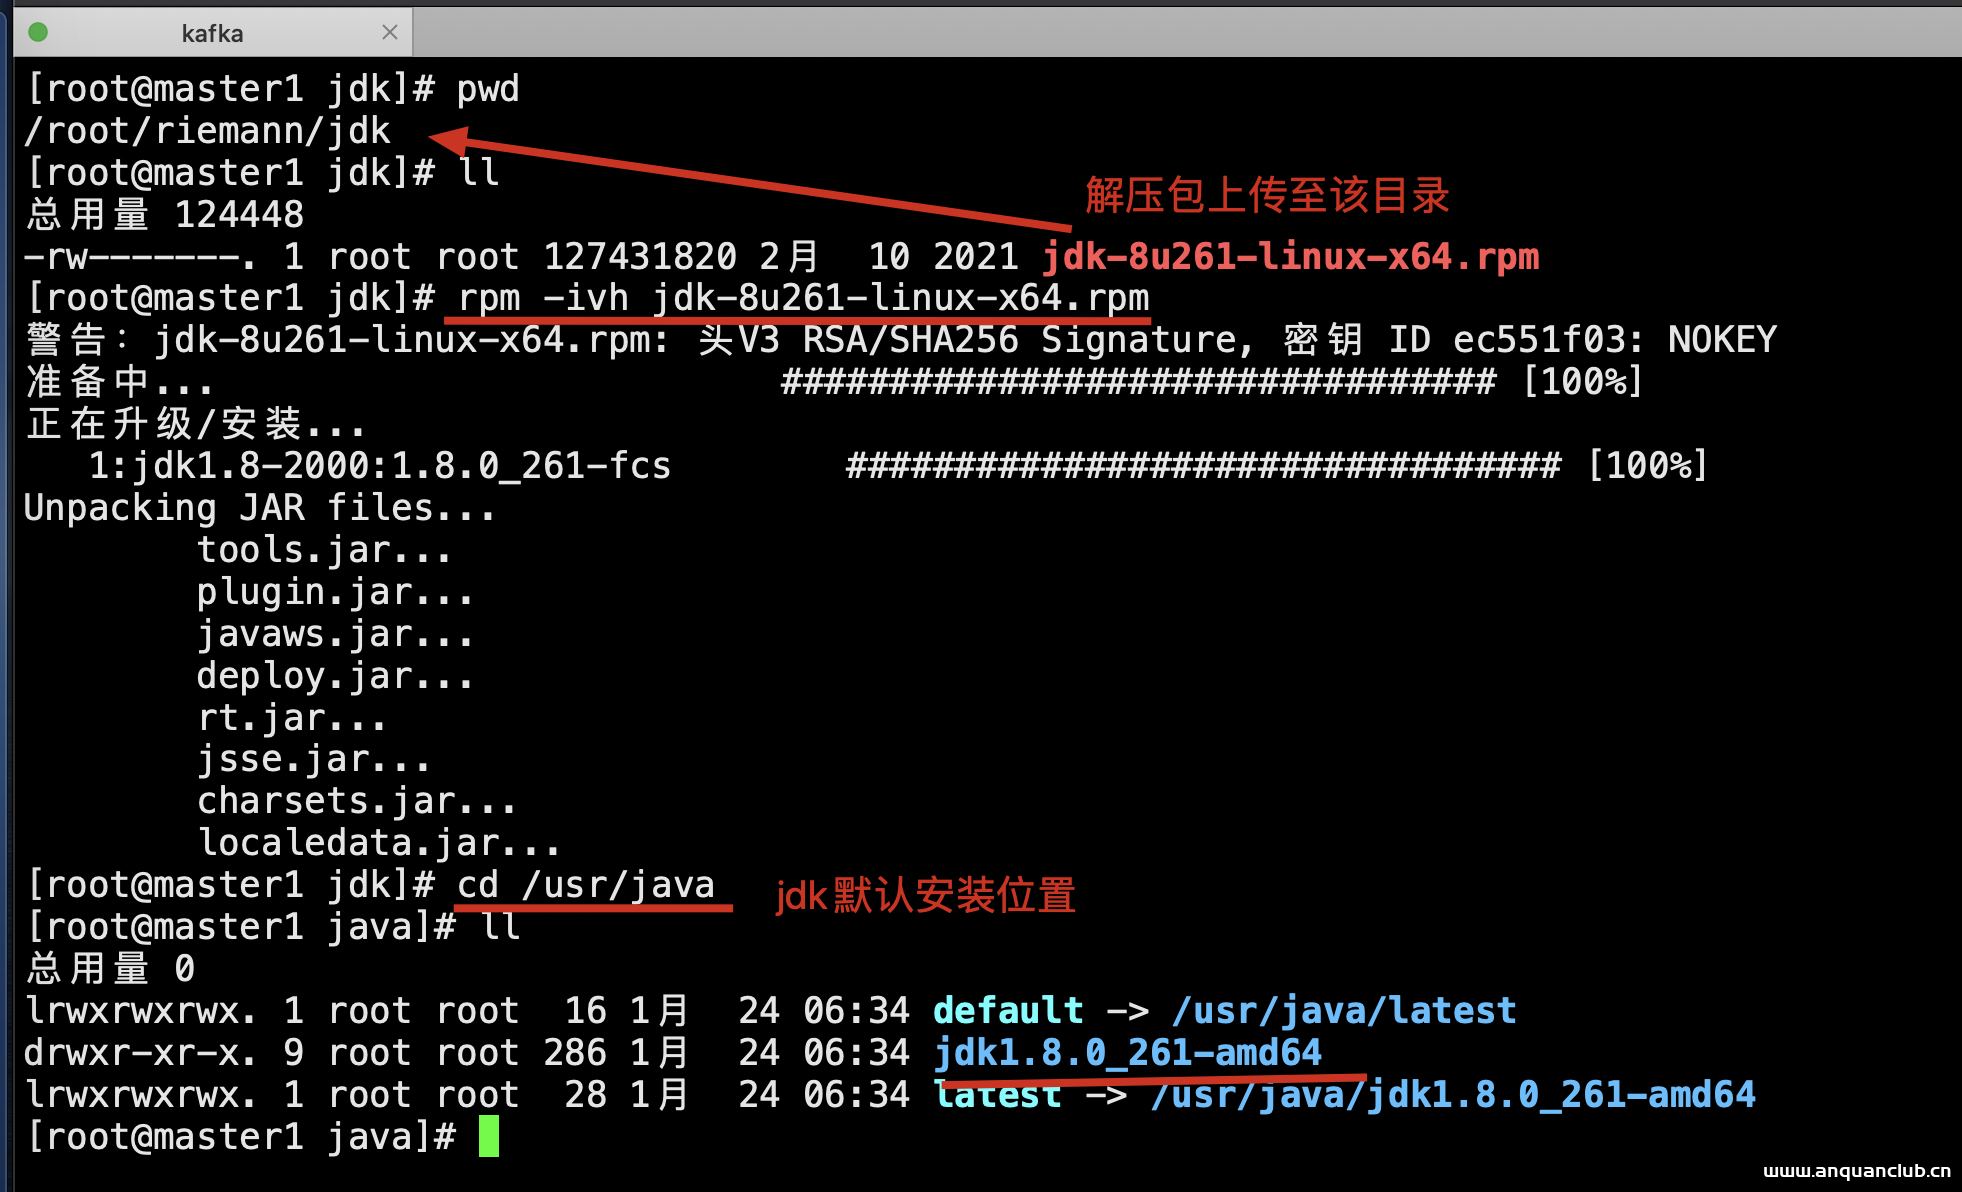
在Linux环境下安装Kafka_Linux
本文以安装Kafka的步骤做了图文详细介绍,Kafka是一种高吞吐量 的分布式发布订阅消息系统,对Kagka感兴趣的小伙伴可以参考参考本篇文章 目录1.1 Java环境为前提1.2 Zookeeper的安装配置1.3 Kafk...
2022年6月17日 10:04CVE-2022-40684: Fortinet FortiOS admin 远程命令执行漏洞
漏洞标题 CVE-2022-40684: Fortinet FortiOS admin 远程命令执行漏洞 漏洞描述 Fortinet 周一指出,上周修补的 CVE-2022-40684 身份验证绕过安全漏洞,正在野外被广泛利用。作为管理界面上的一...
2022年8月23日 06:24CVE-2022-1906: WordPress Copyright Proof <=4.16 - Cross-Site-Scripting
漏洞标题 CVE-2022-1906: WordPress Copyright Proof <=4.16 - Cross-Site-Scripting 漏洞描述 WordPress Copyright Proof plugin 4.16 and prior contains a cross-site scripting vulnerab...
2022年6月21日 21:27
2026年9月19日 11:45
2026年9月18日 11:46
2026年9月17日 18:46
2026年9月17日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月17日 18:19
2026年8月16日 20:18
2026年8月11日 13:39
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

