
最新发布第781页

CVE-2010-1954: Joomla! Component iNetLanka Multiple root 1.0 – Local File Inclusion
漏洞标题 CVE-2010-1954: Joomla! Component iNetLanka Multiple root 1.0 - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the iNetLanka Multiple root (com_multir...
 2010年3月2日 20:41
CVE-2001-0537: Cisco IOS HTTP Configuration – Authentication Bypass
漏洞标题 CVE-2001-0537: Cisco IOS HTTP Configuration - Authentication Bypass 漏洞描述 HTTP server for Cisco IOS 11.3 to 12.2 allows attackers to bypass authentication and execute a...
2001年9月19日 02:09CVE-2023-32563: Ivanti Avalanche – Remote Code Execution
漏洞标题 CVE-2023-32563: Ivanti Avalanche - Remote Code Execution 漏洞描述 An unauthenticated attacker could achieve the code execution through a RemoteControl server. PoC代码
2023年5月9日 14:03CVE-2024-9466: Palo Alto Expedition – Infomation Disclosure
漏洞标题 CVE-2024-9466: Palo Alto Expedition - Infomation Disclosure 漏洞描述 Palo Alto Networks Expedition的/API/convertCSVtoParquet.php接口存在信息泄露漏洞,从而导致PAN-OS防火墙...
2024年8月22日 06:03CVE-2021-3374: Rstudio Shiny Server <1.5.16 - Local File Inclusion
漏洞标题 CVE-2021-3374: Rstudio Shiny Server <1.5.16 - Local File Inclusion 漏洞描述 Rstudio Shiny Server prior to 1.5.16 is vulnerable to local file inclusion and source code l...
2021年5月26日 07:03CVE-2022-34094: Software Publico Brasileiro i3geo v7.0.5 – Cross-Site Scripting
漏洞标题 CVE-2022-34094: Software Publico Brasileiro i3geo v7.0.5 - Cross-Site Scripting 漏洞描述 Portal do Software Publico Brasileiro i3geo v7.0.5 was discovered to contain a cro...
2022年10月25日 16:50
Konga 任意用户登录 分析
原文链接: http://www.o2oxy.cn/3632.html 介绍: 首先呢,先了解下Konga是什么东东(有点多余,知道有漏洞就行了!),了解konga之前呢,先了解下Kong:Kong是一款基于OpenResty(Nginx + Lua模块...
2022年3月10日 23:32
linux编译内核的方法_Linux
在本篇文章里小编给各位整理的是关于linux编译内核的方法,有需要的朋友们可以跟着学习参考下。 1、下载需要的内核版本 2、上传到操作系统 3、解压到/usr/src目录下 比如:3.19内核 tar -xvf li...
2024年3月24日 20:28CVE-2021-44529: Ivanti EPM Cloud Services Appliance Code Injection
漏洞标题 CVE-2021-44529: Ivanti EPM Cloud Services Appliance Code Injection 漏洞描述 Ivanti EPM Cloud Services Appliance (CSA) before version 4.6.0-512 is susceptible to a code inj...
2021年7月18日 17:13CVE-2023-4114: PHP Jabbers Night Club Booking 1.0 – Cross Site Scripting
漏洞标题 CVE-2023-4114: PHP Jabbers Night Club Booking 1.0 - Cross Site Scripting 漏洞描述 A vulnerability was found in PHP Jabbers Night Club Booking Software 1.0. It has been rat...
2023年4月28日 08:50CVE-2005-0850: FileZilla Server < 0.9.6 - DoS via MS-DOS Device Names
漏洞标题 CVE-2005-0850: FileZilla Server < 0.9.6 - DoS via MS-DOS Device Names 漏洞描述 FileZilla Server versions prior to 0.9.6 are vulnerable to denial of service when process...
2005年6月7日 17:01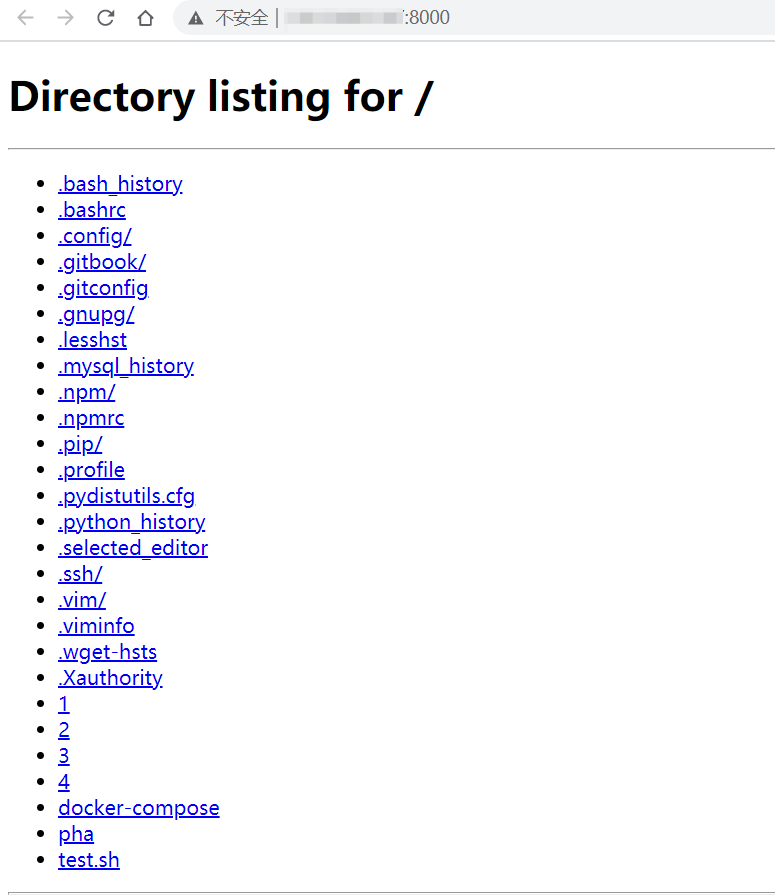
寻找python开启web服务中的宝藏
测试过程中,有时需要临时用python开启web服务,默认是允许目录浏览的,如果不及时关闭进程,可能会被窃取当前目录中的文件。 fofa(也可以尝试添加python2的服务器版本): ((server='SimpleHTTP/...
2022年3月10日 23:34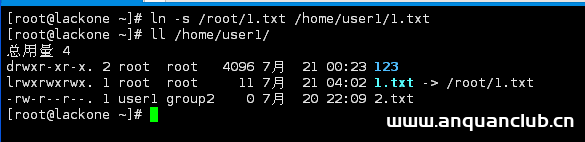
linux文件管理命令实例分析【显示、查看、统计等】_Linux
这篇文章主要介绍了linux文件管理命令,结合实例形式分析Linux文件管理的显示、查看、统计等相关操作命令使用技巧,需要的朋友可以参考下 本文实例讲述了linux文件管理命令。分享给大家供大家参考...
2024年3月10日 20:16CVE-2021-24210: WordPress PhastPress <1.111 - Open Redirect
漏洞标题 CVE-2021-24210: WordPress PhastPress <1.111 - Open Redirect 漏洞描述 WordPress PhastPress plugin before 1.111 contains an open redirect vulnerability. An attacker can r...
2021年3月20日 11:12CrushFTP /WebInterface/function/ 权限绕过漏洞(CVE-2025-31161)
漏洞标题 CrushFTP /WebInterface/function/ 权限绕过漏洞(CVE-2025-31161) 漏洞描述 CrushFTP 是一种流行的文件传输服务器软件,版本 10.0.0 至 10.8.3 和 11.0.0 至 11.3.0 存在身份验证绕...
2025年12月8日 14:01CVE-2024-36683: PrestaShop productsalert – SQL Injection
漏洞标题 CVE-2024-36683: PrestaShop productsalert - SQL Injection 漏洞描述 In the module 'Products Alert' (productsalert) up to version 1.7.4 from Smart Modules for Prest...
2024年1月10日 09:58
2026年9月20日 11:45
2026年9月19日 11:45
2026年9月18日 11:46
2026年9月17日 18:46
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

