
最新发布第798页

CVE-2018-1000861: Jenkins – Remote Command Injection
漏洞标题 CVE-2018-1000861: Jenkins - Remote Command Injection 漏洞描述 Jenkins 2.153 and earlier and LTS 2.138.3 and earlier are susceptible to a remote command injection via stapl...
 2018年1月17日 08:21

[GYCTF2020]Blacklist -堆叠查询- buu刷题笔记
启动挑战项目,发现前端界面显示Black list is so weak for you,isn’t it 随便输入几个关键词试试:select,他爆出来所有的黑名单关键词,本来还想fuzz跑一下的 return preg_match('/set|prepa...

 2022年4月27日 17:23
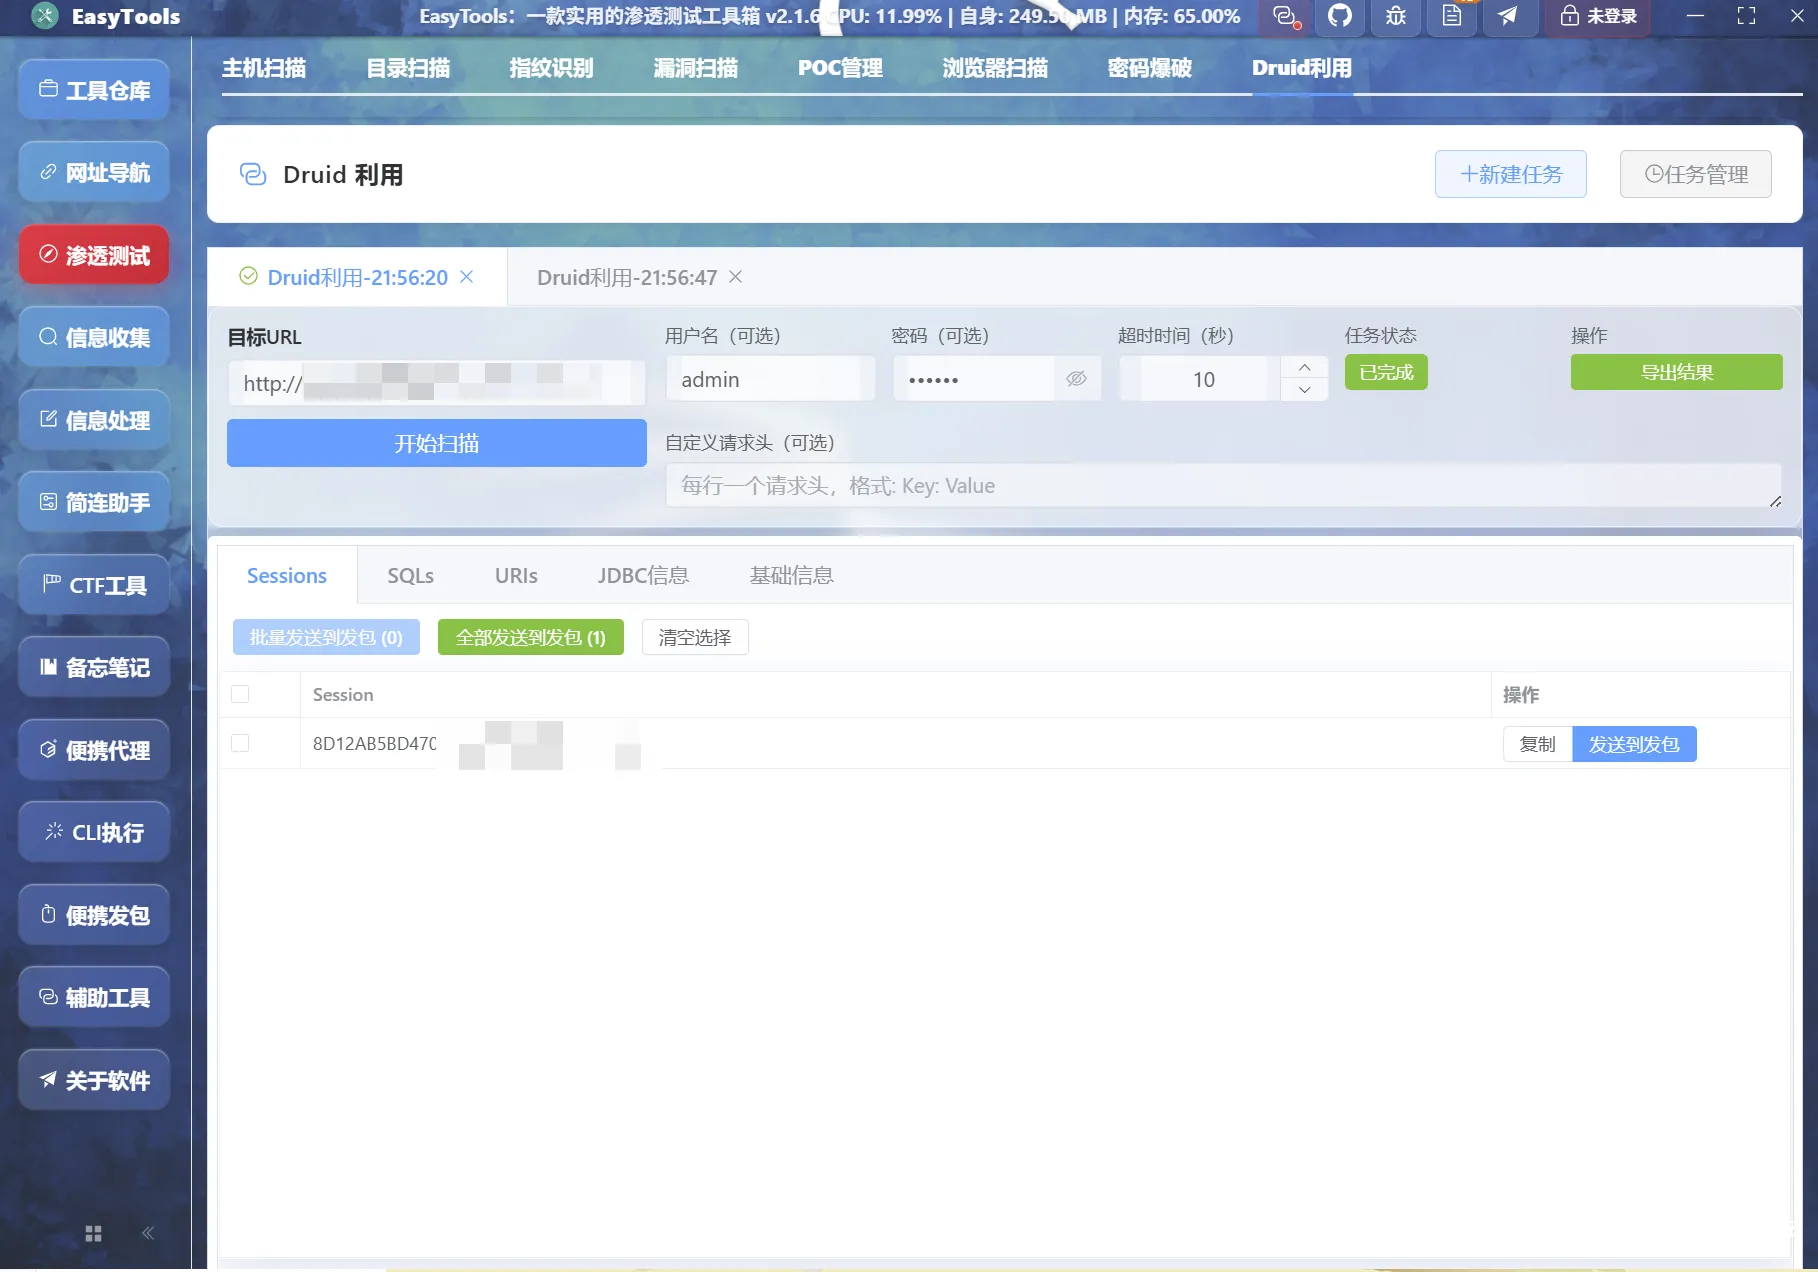
EasyTools渗透测试工具箱V2.1.6更新(1. 渗透测试模块新增druid利用功能; 2. 修复密码爆破模块部分协议无法直接执行命令的bug)
前言 开工第一更,在此汇报一下更新进度: 渗透测试模块新增druid利用功能,自动提取并支持一键发送到便携发包模块进行测试; 修复密码爆破模块部分协议无法直接执行命令的bug 新增功能 1. 渗透...
2026年3月15日 12:27CVE-2023-41621: Emlog Pro v2.1.14 – Cross-Site Scripting
漏洞标题 CVE-2023-41621: Emlog Pro v2.1.14 - Cross-Site Scripting 漏洞描述 Cross Site Scripting (XSS) vulnerability in Emlog Pro v2.1.14 via /admin/store.php. PoC代码
2023年3月4日 13:27CVE-2014-1843: Titan FTP Server < 10.40 - User Properties Traversal
漏洞标题 CVE-2014-1843: Titan FTP Server < 10.40 - User Properties Traversal 漏洞描述 Titan FTP Server versions prior to 10.40 build 1829 contain a directory traversal vulnerabi...
2014年2月2日 15:09
穿透静态检测:EDR对抗技术的分层实现
穿透静态检测:EDR对抗技术的分层实现作者:1571199704841171https://xz.aliyun.com/news/91978文章转载自 先知社区 穿透静态检测:EDR 对抗技术的分层拆解 本文仅用于安全研究与防御对抗学习。...
2026年4月24日 16:49CVE-2024-3656: Keycloak < 24.0.5 - Broken Access Control
漏洞标题 CVE-2024-3656: Keycloak < 24.0.5 - Broken Access Control 漏洞描述 A flaw was found in Keycloak. Certain endpoints in Keycloak's admin REST API allow low-privilege ...
2024年6月22日 14:06CVE-2015-1880: Fortinet FortiOS <=5.2.3 - Cross-Site Scripting
漏洞标题 CVE-2015-1880: Fortinet FortiOS <=5.2.3 - Cross-Site Scripting 漏洞描述 Fortinet FortiOS 5.2.x before 5.2.3 contains a cross-site scripting vulnerability in the SSL VPN...
2015年12月4日 02:45
-Struts2-053 远程命令执行漏洞
本文转载于公众号:融云攻防实验室,原文地址: 漏洞复现-Struts2-053 远程命令执行漏洞 Struts是Apache软件基金会(ASF)赞助的一个开源项目。它最初是Jakarta项目中的一个子项目,并在2004年3...
2023年2月6日 10:00CVE-2013-4625: WordPress Plugin Duplicator < 0.4.5 - Cross-Site Scripting
漏洞标题 CVE-2013-4625: WordPress Plugin Duplicator < 0.4.5 - Cross-Site Scripting 漏洞描述 A cross-site scripting vulnerability in files/installer.cleanup.php in the Duplicator...
2013年6月22日 05:03CVE-2013-2251: Apache Struts 2 – DefaultActionMapper Prefixes OGNL Code Execution (S2-016)
漏洞标题 CVE-2013-2251: Apache Struts 2 - DefaultActionMapper Prefixes OGNL Code Execution (S2-016) 漏洞描述 In Struts 2 before 2.3.15.1 the information following "action:&quo...
2013年4月10日 16:26CVE-2022-0968: Microweber <1.2.12 - Integer Overflow
漏洞标题 CVE-2022-0968: Microweber <1.2.12 - Integer Overflow 漏洞描述 Microweber before 1.2.12 is susceptible to integer overflow. The application allows large characters to in...
2022年10月12日 02:25
某彩票 任意代码执行漏洞(未公布)
0x01 漏洞描述 网络赌博是指通过互联网手段(非法赌博网站、博彩App、微信群等)进行的赌博活动。由于网络赌博不合法,资金不受法律保护,有很多“出老千”的行为,很多人被骗后往往不敢报...
2022年10月31日 11:27CVE-2022-43140: kkFileView 4.1.0 – Server-Side Request Forgery
漏洞标题 CVE-2022-43140: kkFileView 4.1.0 - Server-Side Request Forgery 漏洞描述 kkFileView 4.1.0 is susceptible to server-side request forgery via the component cn.keking.web.cont...
2022年11月12日 21:07CVE-2024-41955: Open Redirect in Login Redirect – MobSF
漏洞标题 CVE-2024-41955: Open Redirect in Login Redirect - MobSF 漏洞描述 Mobile Security Framework (MobSF) is a security research platform for mobile applications in Android, iOS ...
2024年8月9日 07:24CVE-2010-1714: Joomla! Component Arcade Games 1.0 – Local File Inclusion
漏洞标题 CVE-2010-1714: Joomla! Component Arcade Games 1.0 - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the Arcade Games (com_arcadegames) component 1.0 f...
2010年4月25日 11:34
2026年9月18日 11:46
2026年9月17日 18:46
2026年9月17日 11:45
2026年9月16日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53
2026年9月17日 18:19
2026年8月16日 20:18
2026年8月11日 13:39
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

