
最新发布第800页

CVE-2024-13126: WordPress Download Manager < 3.3.07 - Unauthenticated Data Exposure
漏洞标题 CVE-2024-13126: WordPress Download Manager < 3.3.07 - Unauthenticated Data Exposure 漏洞描述 The WordPress Download Manager plugin before version 3.3.07 does not preven...
 2024年11月5日 00:57
CVE-2023-35813: Sitecore – Remote Code Execution
漏洞标题 CVE-2023-35813: Sitecore - Remote Code Execution 漏洞描述 Multiple Sitecore products allow remote code execution. This affects Experience Manager, Experience Platform, and...
2023年8月19日 06:03CVE-2017-3506: Oracle Fusion Middleware Weblogic Server – Remote OS Command Execution
漏洞标题 CVE-2017-3506: Oracle Fusion Middleware Weblogic Server - Remote OS Command Execution 漏洞描述 The Oracle WebLogic Server component of Oracle Fusion Middleware (Web Servic...
2017年12月21日 04:13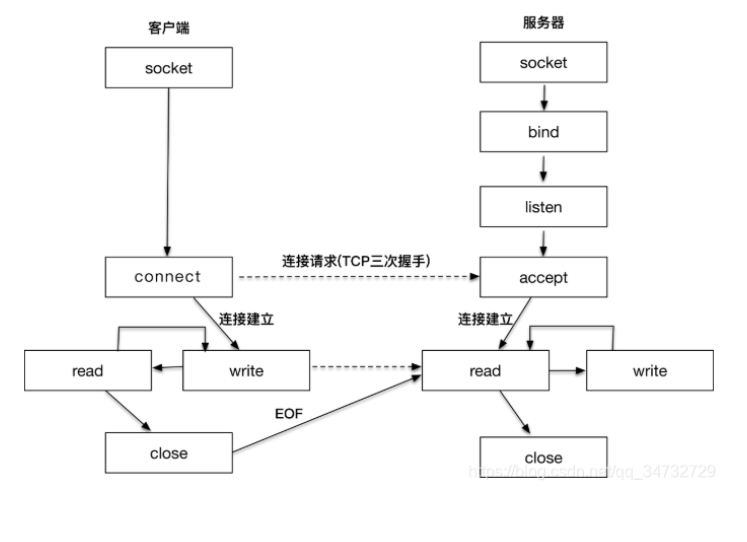
简析Linux网络编程函数_Linux
这篇文章主要介绍了Linux网络编程函数,利用这些基本函数,可以实现tcp协议通讯,可以实现通信。需要了解的小伙伴可以参考一下 目录1,创建套接字socket2,绑定套接字bind3,创建监听;listen4...
2022年6月15日 22:46CVE-2021-46417: Franklin Fueling Systems Colibri Controller Module 1.8.19.8580 – Local File Inclusion
漏洞标题 CVE-2021-46417: Franklin Fueling Systems Colibri Controller Module 1.8.19.8580 - Local File Inclusion 漏洞描述 Franklin Fueling Systems Colibri Controller Module 1.8.19.85...
2021年2月9日 08:15Apache Struts2(S2-062)远程代码执行漏洞(CVE-2021-31805)
漏洞标题 Apache Struts2(S2-062)远程代码执行漏洞(CVE-2021-31805) 漏洞描述 Apache Struts2框架是一个用于开发Java EE网络应用程序的Web框架。Apache Struts< 2.5.30存在OGNL表达式注入漏...
2021年9月23日 20:54CVE-2023-3845: MooDating 1.2 – Cross-Site Scripting
漏洞标题 CVE-2023-3845: MooDating 1.2 - Cross-Site Scripting 漏洞描述 A vulnerability was found in mooSocial mooDating 1.2. It has been rated as problematic. Affected by this issue...
2023年6月17日 15:19CVE-2024-1561: Gradio 4.3-4.12 – Local File Read
漏洞标题 CVE-2024-1561: Gradio 4.3-4.12 - Local File Read 漏洞描述 Local file read by calling arbitrary methods of Components class between Gradio versions 4.3-4.12 PoC代码
2024年8月14日 22:25CVE-2023-6018: Mlflow – Arbitrary File Write
漏洞标题 CVE-2023-6018: Mlflow - Arbitrary File Write 漏洞描述 An attacker can overwrite any file on the server hosting MLflow without any authentication. PoC代码
2023年2月5日 11:32CVE-2020-24312: WordPress Plugin File Manager (wp-file-manager) Backup Disclosure
漏洞标题 CVE-2020-24312: WordPress Plugin File Manager (wp-file-manager) Backup Disclosure 漏洞描述 mndpsingh287 WP File Manager v6.4 and lower fails to restrict external access to...
2020年2月18日 03:44Apache Struts2(S2-001)远程代码执行漏洞(CVE-2007-4556)
漏洞标题 Apache Struts2(S2-001)远程代码执行漏洞(CVE-2007-4556) 漏洞描述 在Struts2 WebWork 2.1+ 和 Struts 2 的“altSyntax”功能允许将 OGNL表达式插入到文本字符串中并进行递归处理。这...
2007年2月7日 13:15CVE-2022-46463: Harbor <=2.5.3 - Unauthorized Access
漏洞标题 CVE-2022-46463: Harbor <=2.5.3 - Unauthorized Access 漏洞描述 An access control issue in Harbor v1.X.X to v2.5.3 allows attackers to access public and private image rep...
2022年5月15日 00:42(CVE-2025-54123) Hoverfly 中间件API命令注入漏洞
漏洞标题 (CVE-2025-54123) Hoverfly 中间件API命令注入漏洞 漏洞描述 (CVE-2025-54123) Hoverfly 中间件API命令注入漏洞 PoC代码 暂无
2025年1月4日 10:17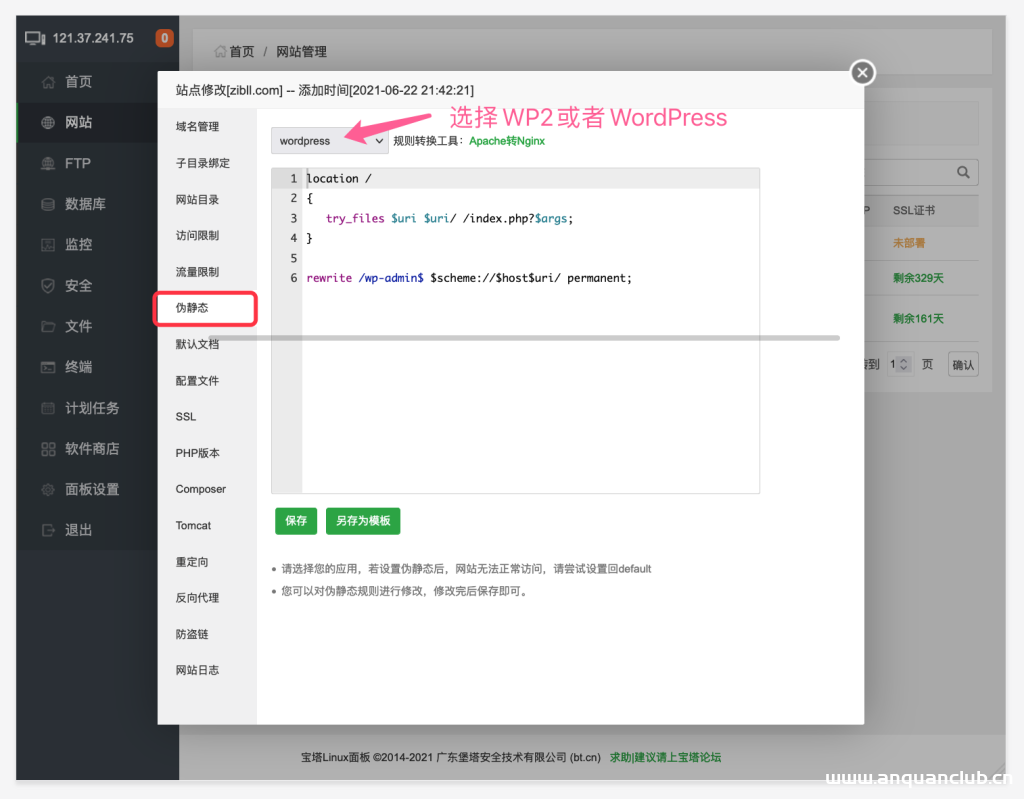
WordPress网站伪静态设置及固定链接设置教程-解决404错误问题-WordPress主题模板
搭建好WordPress网站之后我个人建议首先要做的就是设置好固定链接,WordPress的固定链接也就是网站各个页面的链接格式,默认的方式不太符合现代化网站,推荐使用自定义的方案。 既然涉及到网站...

 2022年5月20日 20:06
CVE-2021-24300: WordPress WooCommerce <1.13.22 - Cross-Site Scripting
漏洞标题 CVE-2021-24300: WordPress WooCommerce <1.13.22 - Cross-Site Scripting 漏洞描述 WordPress WooCommerce before 1.13.22 contains a reflected cross-site scripting vulnerabil...
2021年8月12日 04:27
bugbounty技巧聚合20220114
漏洞报告 【 Lark Technologies】[IDOR] 通过reminderId参数修改其他团队的提醒 http://hackerone.com/reports/946323 【Adobe】在配置文件中泄露 github 访问令牌 http://hackerone.com/report...
2022年3月10日 23:38
2026年11月5日 11:45
2026年11月4日 11:45
2026年11月3日 11:46
2026年11月2日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

