
最新发布第813页

CVE-2020-35848: Agentejo Cockpit <0.12.0 - NoSQL Injection
漏洞标题 CVE-2020-35848: Agentejo Cockpit <0.12.0 - NoSQL Injection 漏洞描述 Agentejo Cockpit prior to 0.12.0 is vulnerable to NoSQL Injection via the newpassword method of the ...
 2020年1月17日 08:42
CVE-2025-27817: Apache Kafka 客户端任意文件读取
漏洞标题 CVE-2025-27817: Apache Kafka 客户端任意文件读取 漏洞描述 允许未经身份验证的攻击者利用该漏洞实现任意文件读取,大多数据处理中间件或流式处理框架,如:Apache Spark Structured ...
2025年4月28日 00:39CVE-2025-46817: Redis < 8.2.1 lua script - Integer Overflow
漏洞标题 CVE-2025-46817: Redis < 8.2.1 lua script - Integer Overflow 漏洞描述 Redis is an open source, in-memory database that persists on disk. Versions 8.2.1 and below allow a...
2025年12月7日 22:02CVE-2024-48307: JeecgBoot v3.7.1 – SQL Injection
漏洞标题 CVE-2024-48307: JeecgBoot v3.7.1 - SQL Injection 漏洞描述 The JeecgBoot application is vulnerable to SQL Injection via the `getTotalData` endpoint. An attacker can exploit...
2024年12月16日 17:19CVE-2023-35078: Ivanti Endpoint Manager Mobile (EPMM) – Authentication Bypass
漏洞标题 CVE-2023-35078: Ivanti Endpoint Manager Mobile (EPMM) - Authentication Bypass 漏洞描述 Ivanti Endpoint Manager Mobile (EPMM), formerly MobileIron Core, through 11.10 allow...
2023年1月3日 03:23CVE-2021-43574: Atmail 6.5.0 – Cross-Site Scripting
漏洞标题 CVE-2021-43574: Atmail 6.5.0 - Cross-Site Scripting 漏洞描述 Atmail 6.5.0 contains a cross-site scripting vulnerability in WebAdmin Control Pane via the format parameter t...
2021年10月20日 12:06CVE-2025-46822: Java-springboot-codebase 1.1 – Arbitrary File Read
漏洞标题 CVE-2025-46822: Java-springboot-codebase 1.1 - Arbitrary File Read 漏洞描述 OsamaTaher/Java-springboot-codebase is a collection of Java and Spring Boot code snippets, appl...
2025年6月2日 12:32
微软称发现针对乌克兰的破坏性恶意软件
2022年1月15日,微软安全团队发布了一份报告,称在乌克兰政府机构及与乌克兰密切合作的组织系统中观察到破坏性恶意软件。该恶意软件一旦被攻击者激活,受感染的计算机系统将无法运行。微软威胁...
2022年3月10日 23:34CVE-2018-20470: Tyto Sahi pro 7.x/8.x – Local File Inclusion
漏洞标题 CVE-2018-20470: Tyto Sahi pro 7.x/8.x - Local File Inclusion 漏洞描述 Tyto Sahi Pro versions through 7.x.x and 8.0.0 are susceptible to a local file inclusion vulnerabilit...
2018年7月24日 22:59CVE-2022-28033: Atom.CMS 2.0 – SQL Injection
漏洞标题 CVE-2022-28033: Atom.CMS 2.0 - SQL Injection 漏洞描述 Atom.CMS 2.0 is vulnerable to SQL Injection via Atom.CMS_admin_uploads.php which allows an attacker to execute arbitr...
2022年11月15日 22:32CVE-2010-2918: Joomla! Component Visites 1.1 – MosConfig_absolute_path Remote File Inclusion
漏洞标题 CVE-2010-2918: Joomla! Component Visites 1.1 - MosConfig_absolute_path Remote File Inclusion 漏洞描述 A PHP remote file inclusion vulnerability in core/include/myMailer.cl...
2010年10月20日 01:40CVE-2023-32243: WordPress Elementor Lite 5.7.1 – Arbitrary Password Reset
漏洞标题 CVE-2023-32243: WordPress Elementor Lite 5.7.1 - Arbitrary Password Reset 漏洞描述 Improper Authentication vulnerability in WPDeveloper Essential Addons for Elementor allo...
2023年7月30日 00:29CVE-2023-27032: PrestaShop AdvancedPopupCreator – SQL Injection
漏洞标题 CVE-2023-27032: PrestaShop AdvancedPopupCreator - SQL Injection 漏洞描述 In the module “Advanced Popup Creator” (advancedpopupcreator) from Idnovate for PrestaShop, a gu...
2023年10月29日 12:02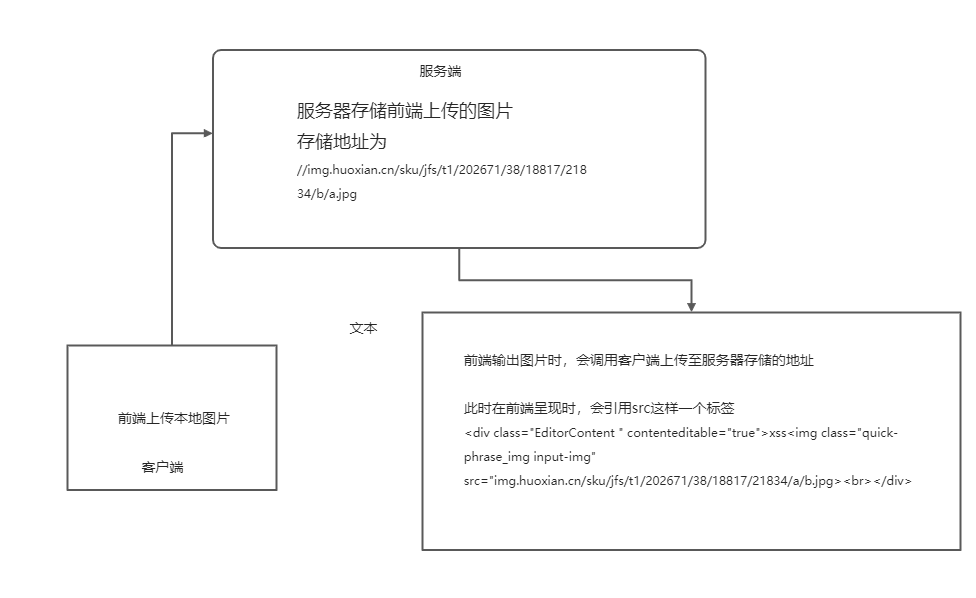
挖掘存储Xss时发现的小Tips
前言:一直以来在挖掘xss时总是被各种过滤,各种实体化转义。是真滴很难受,敢想连着几天兴冲冲奔着表单去,看着被过滤,转义的payload,用尽办法都过不去的心情。最后似乎有个声音在跟我说,能...
2022年3月10日 23:30CVE-2024-45388: Hoverfly < 1.10.3 - Arbitrary File Read
漏洞标题 CVE-2024-45388: Hoverfly < 1.10.3 - Arbitrary File Read 漏洞描述 Hoverfly is a lightweight service virtualization/ API simulation / API mocking tool for developers and ...
2024年4月17日 18:36CVE-2025-9196: Trinity Audio <= 5.21.0 - Information Exposure
漏洞标题 CVE-2025-9196: Trinity Audio <= 5.21.0 - Information Exposure 漏洞描述 The Trinity Audio Text to Speech AI audio player to convert content into audio plugin for WordPre...
2025年9月11日 08:46
2026年11月6日 11:45
2026年11月5日 11:45
2026年11月4日 11:45
2026年11月3日 11:46
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

