
最新发布第814页

CVE-2025-4427: Ivanti Endpoint Manager Mobile – Unauthenticated Remote Code Execution
漏洞标题 CVE-2025-4427: Ivanti Endpoint Manager Mobile - Unauthenticated Remote Code Execution 漏洞描述 An authentication bypass in Ivanti Endpoint Manager Mobile allowing attacker...
 2025年6月21日 02:50
(CVE-2021-21975) vRealize Operations Manager API 请求伪造漏洞
漏洞标题 (CVE-2021-21975) vRealize Operations Manager API 请求伪造漏洞 漏洞描述 (CVE-2021-21975) vRealize Operations Manager API 请求伪造漏洞 PoC代码 暂无
2021年6月25日 01:13CVE-2023-6266: WordPress Backup Migration <= 1.3.6 - Path Traversal
漏洞标题 CVE-2023-6266: WordPress Backup Migration <= 1.3.6 - Path Traversal 漏洞描述 WordPress Backup Migration plugin versions up to 1.3.6 contain a path traversal and file va...
2023年10月31日 17:17CVE-2021-24970: WordPress All-In-One Video Gallery <2.5.0 - Local File Inclusion
漏洞标题 CVE-2021-24970: WordPress All-In-One Video Gallery <2.5.0 - Local File Inclusion 漏洞描述 WordPress All-in-One Video Gallery plugin before 2.5.0 is susceptible to local...
2021年12月21日 21:06CVE-2011-5106: WordPress Plugin Flexible Custom Post Type < 0.1.7 - Cross-Site Scripting
漏洞标题 CVE-2011-5106: WordPress Plugin Flexible Custom Post Type < 0.1.7 - Cross-Site Scripting 漏洞描述 A cross-site scripting vulnerability in edit-post.php in the Flexible ...
2011年1月23日 21:24CVE-2024-1380: Relevanssi (A Better Search) <= 4.22.0 - Query Log Export
漏洞标题 CVE-2024-1380: Relevanssi (A Better Search) <= 4.22.0 - Query Log Export 漏洞描述 The Relevanssi Search plugin for WordPress is vulnerable to unauthorized access of dat...
2024年2月25日 00:29(CVE-2021-21975) vRealize Operations Manager API 请求伪造漏洞
漏洞标题 (CVE-2021-21975) vRealize Operations Manager API 请求伪造漏洞 漏洞描述 (CVE-2021-21975) vRealize Operations Manager API 请求伪造漏洞 PoC代码 暂无
2021年1月1日 13:06
bugbounty技巧聚合20210818
漏洞报告 MTN Grou #1060518 No rate limit in otp code sending Mail.ru #1255676 Blind XSS Stored and CORS misconfiguration в отчете 'События' сервиса top.mail.ru...
2022年3月10日 23:32CVE-2020-29583: ZyXel USG – Hardcoded Credentials
漏洞标题 CVE-2020-29583: ZyXel USG - Hardcoded Credentials 漏洞描述 A hardcoded credential vulnerability was identified in the 'zyfwp' user account in some Zyxel firewall...
2020年12月5日 13:14CVE-2023-26255: STAGIL Navigation for Jira Menu & Themes <2.0.52 - Local File Inclusion
漏洞标题 CVE-2023-26255: STAGIL Navigation for Jira Menu & Themes <2.0.52 - Local File Inclusion 漏洞描述 STAGIL Navigation for Jira Menu & Themes plugin before 2.0.52 i...
2023年1月27日 06:00CVE-2010-1718: Joomla! Component Archery Scores 1.0.6 – Local File Inclusion
漏洞标题 CVE-2010-1718: Joomla! Component Archery Scores 1.0.6 - Local File Inclusion 漏洞描述 A directory traversal vulnerability in archeryscores.php in the Archery Scores (com_a...
2010年1月13日 04:13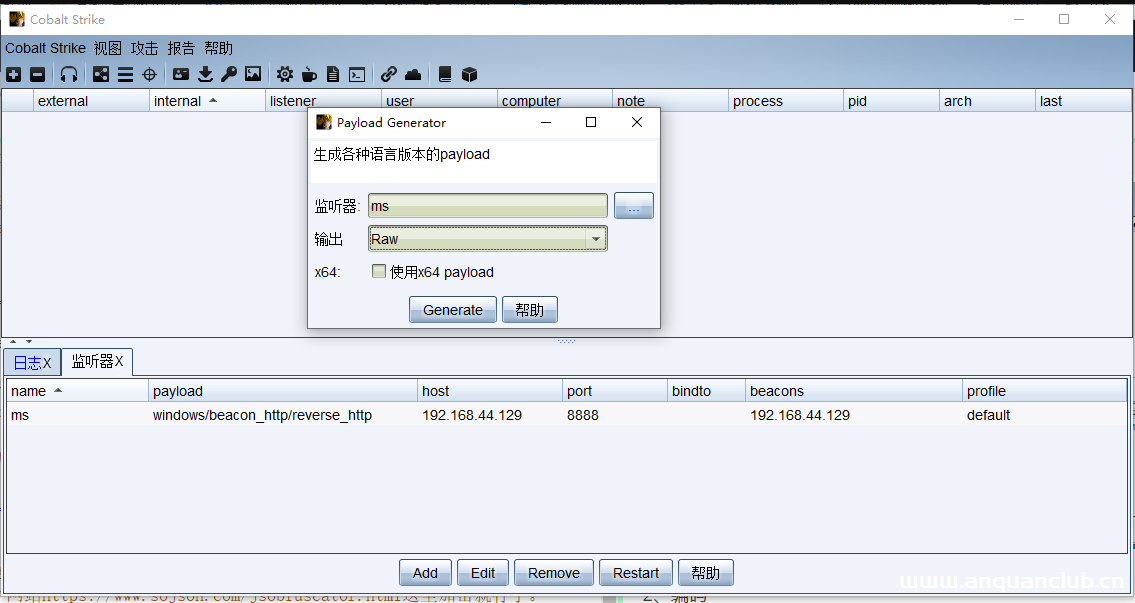
cobaltstrike免杀过360和火绒
在免杀之前需要自己处理一下cobaltstrike的相关特征,和更新一下证书。不然虽然文件免杀了,可是上线的时候会有特征,会被火绒拦截。 具体参考以下文章 http://www.wangan.com/articles/1144 ht...
2022年3月16日 09:16CVE-2018-7422: WordPress Site Editor <=1.1.1 - Local File Inclusion
漏洞标题 CVE-2018-7422: WordPress Site Editor <=1.1.1 - Local File Inclusion 漏洞描述 WordPress Site Editor through 1.1.1 allows remote attackers to retrieve arbitrary files via...
2018年7月28日 05:38CVE-2025-24963: Vitest Browser Mode – Local File Read
漏洞标题 CVE-2025-24963: Vitest Browser Mode - Local File Read 漏洞描述 Vitest is a testing framework powered by Vite. The `__screenshot-error` handler on the browser mode HTTP ser...
2025年10月30日 11:08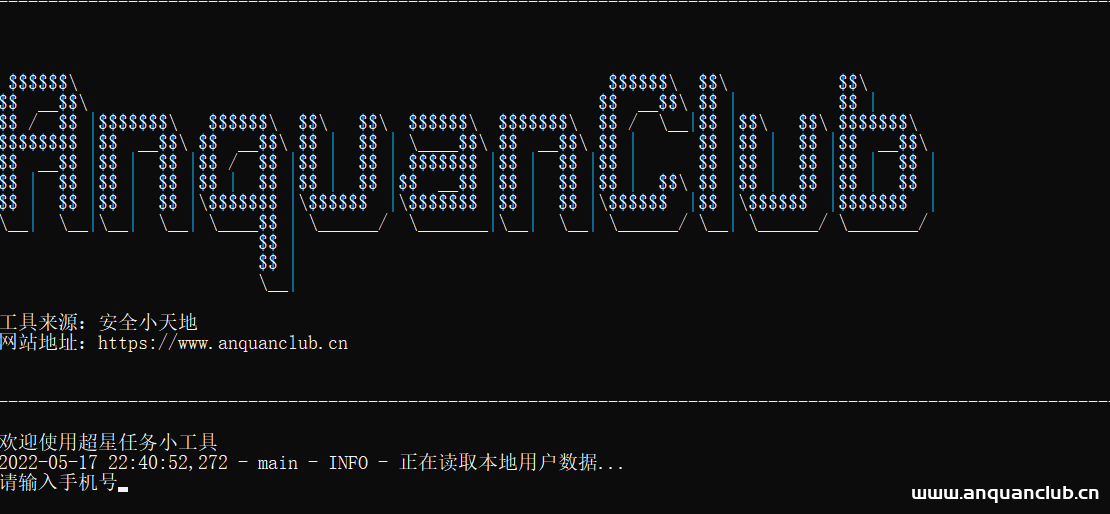
bat脚本案例:实现炫酷的文字logo
需求 我们在日常运行第三方的脚本的时候经常看到非常炫酷的启动logo,比如下图: 不仅美观,而且可以展示品牌和团队标志,提高曝光度。下面详细介绍一下如何用纯batch脚本实现上述效果(powersh...

 2023年3月31日 20:28
CVE-2011-5106: WordPress Plugin Flexible Custom Post Type < 0.1.7 - Cross-Site Scripting
漏洞标题 CVE-2011-5106: WordPress Plugin Flexible Custom Post Type < 0.1.7 - Cross-Site Scripting 漏洞描述 A cross-site scripting vulnerability in edit-post.php in the Flexible ...
2011年12月4日 02:21
2026年11月7日 11:45
2026年11月6日 11:45
2026年11月5日 11:45
2026年11月4日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

